We're delighted to announce our partnership with @our__trace, the female-founded, Australian tech company focused on making carbon neutrality accessible to everyone.
Find out more about trace's projects at https://t.co/0bGxyRYW4T
#positivetrace#climatepositive#carbonemissions
Register to join Issam and me this Wednesday to discuss DMARC. We will help clarify what DMARC is, how to implement it and debunk a lot of the misunderstanding around DMARC. Also highlighting the security benefits of getting to a policy of enforcement. #DMARC#cybersecurity#BEC
Looking to block #domainimpersonation attacks on your domain? Or increase email #deliverability? Deploying #DMARC can help solve both of these issues.
Register for our upcoming webinar to find out more:
https://t.co/sysjT0Au84
📅 Wednesday 16th March
⏰ 3PM (CST) / 8PM (GMT)
Register for our live webinar! We will be discussing BEC attacks and solutions that will help bridge the gap in your email security. Our focus is on helping organizations protect themselves against these never-ending phishing attacks. #BEC#emailsecurity#Redsift
OnDOMAIN enables security teams to shut down phishing sites and discover legitimate but unsecured domains while defending their brands 🎣
Learn more: https://t.co/oHrLypJyPT
#impersonation#cybersecurity#newproduct
Join me on 3/16/22 to discuss DMARC! There is a knowledge gap around DMARC. What it is, and why does it matter? Knowledge is power, so join us to understand DMARC. Register here. #DMARC#knowledgeshare#cybersecurity
https://t.co/dgHpM6lQIb
A recent @IDTheftCenter report identified a 40% increase in the number of U.S. breaches that traced to #phishing, #smishing or #businessemailcompromise in 2021 🇺🇸
Find out how Red Sift's suite of products can help protect against these cyberthreats - https://t.co/1YYAQ539Zt
Great news, we have secured our Series B Funding! Happy to be working with such a great company that is further set up to assist even more organizations in protecting themselves from BEC attacks. #cybersecurity#BEC#RedSift
We’ve secured $54 million in Series B funding! 🍾 🎉 A huge thank you to everyone who’s been a part of Red Sift's journey so far. We’re excited about what’s to come! 🚀
Read more: https://t.co/QYgQRxvwtI
@HighlandCapital Sands Capital @MMC_Ventures@Oxford_Capital#thankyou
We have been named 'Best Cybersecurity Company' and are Gold winners in 'Fastest Growing Cybersecurity Company - EUROPE'! It feels great working for a great company! #awards#cybersecurity#redsift
We have been named 'Best Cybersecurity Company' and are Gold winners in 'Fastest Growing Cybersecurity Company - EUROPE'! It feels great working for a great company! #awards#cybersecurity#redsift
We've been named 'Best Cybersecurity Company' and are Gold winners in the 'Fastest Growing Cybersecurity Company - EUROPE' category at the Cybersecurity Excellence Awards 2022! 🏆
https://t.co/bBxexf1xxj
#Awards#cybersecurity#innovation
A recent study shows the impact most organizations are facing with phishing attacks. Implement DMARC to protect your organization. #phishing#emailsecurity#cybersecurity
A recent survey revealed that 3⃣1⃣% of respondents who suffered an external attack in the last year reported #phishing as the primary attack vector.
https://t.co/3OG2kJda8L
Protect end users, customers, and your brand by implementing #DMARC.
Join our webinar next week with @netcore_cloud and @Entrust_Corp to find out:
✅ How to identify your current #emailsecurity setup
✅ How to configure SPF, DKIM, #DMARC, and #BIMI
✅ What these deciphered reports can provide for your organization
https://t.co/n9gEkhp87B
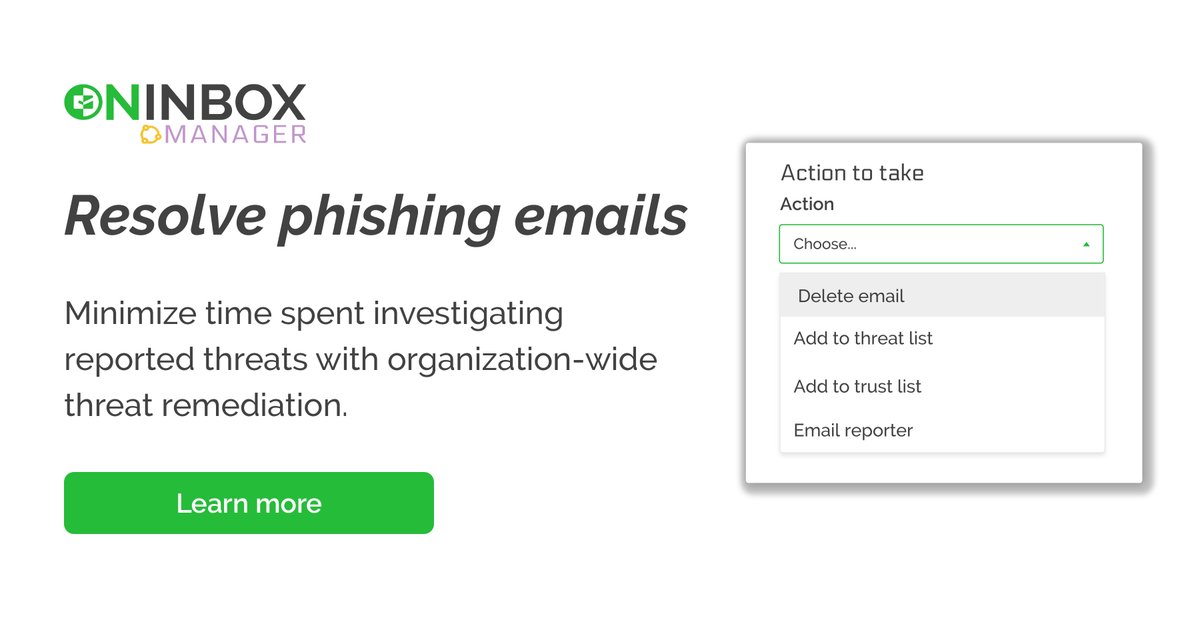
We’re delighted to announce the launch of OnINBOX Remediation, the tool that empowers organizations to resolve #phishingemails fast while minimizing detective work and saving time.🛡⏳
Full story here: https://t.co/MqqfIdRBxc
The continued evolution of email compromise, spear phishing, brand impersonation scams, & other email threats is far from linear. Download this report presented in partnership with @AgariInc for a look at the trends that dominated the past quarter: https://t.co/2RTRaqT5o5