Building an AI agent is the easy part. Knowing it actually works in production - that’s the hard part. 💪
Our Chief Architect Shlomi featured in @N12 as one of 12 leaders reshaping software development in the AI era. 🔗https://t.co/8QWImYWzFy
#CloudSecurity#AISecurity
⚠️ Think HTTP2Shell only affects http://Node.js and C? Think again.
If you’re running Traefik, Fiber, Iris, or fasthttp, it’s worth checking your exposure.
Here's wwe found, what it means, and what to do: https://t.co/6U0s2Mn09Z
#HTTP2Shell#VirtualPatching#CloudSecurity
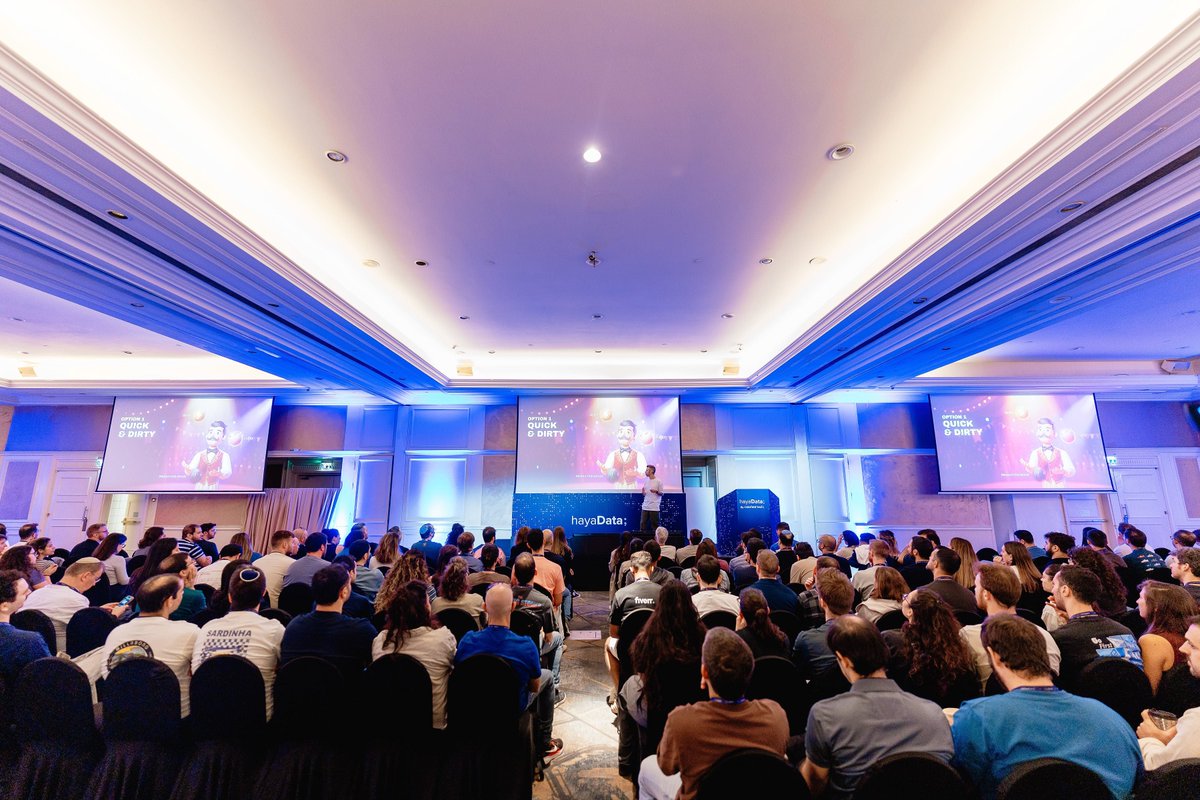
Omer Ginosar showed a packed room data pros at #hayaData 2026 how it works: data products shipped as backend services on the platform R&D already runs, updates delivered in Slack, and an LLM that decides only whether something deserves someone's attention today.
𝐌𝐨𝐬𝐭 𝐚𝐝𝐯𝐚𝐧𝐜𝐞𝐝 𝐀𝐈 𝐦𝐨𝐝𝐞𝐥 + 𝐫𝐞𝐝 𝐭𝐞𝐚𝐦 = 𝐦𝐨𝐫𝐞 𝐬𝐞𝐜𝐮𝐫𝐞 ?
Not necessarily. Turns out that a better model helps. But without the right context, it’s still guessing.
#AISecurity#CloudSecurity#RuntimeSecurity
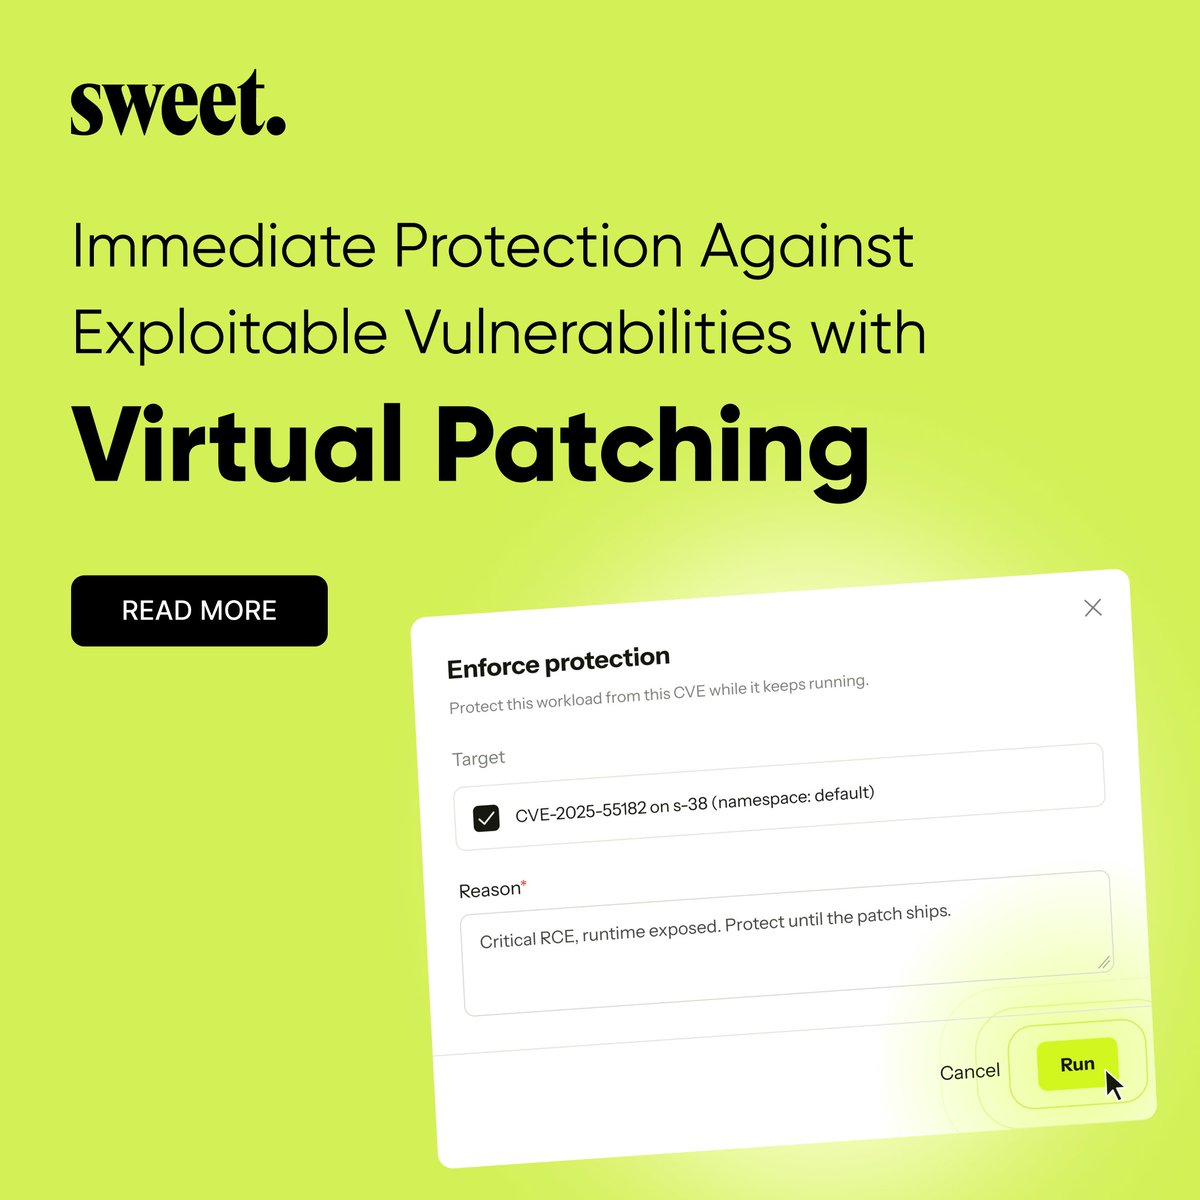
🎊 Virtual Patching is live.
🐝 Now you can protect a running applications from a specific vulnerability in one click - while engineering takes the time it needs to fix it.
Read → https://t.co/ENeMW3V54T
#RuntimeSecurity#VirtualPatching#AISecurity#CloudSecurity
Attackers have AI. Defenders have home advantage. 🐝
Our CEO Dror Kashti writes in @Calcalistech about turning deep runtime context into an advantage: proving real attack paths, fixing exposure and stopping harmful behavior as it happens. Read the piece: https://t.co/g9phTiYRxB
Cloud security’s math is changing. 🍬 Sweet’s Chief AI Officer, Yigael Berger, is taking the stage at Toronto’s AI x Cloud Security Summit to unpack how AI changes the cost and speed of finding, exploiting and fixing vulnerabilities. At #SECTOR26? Come say hi!
Black Hat's a grind.
This is the good kind. ☕
Watch reality change in real time, get caught in the act, and walk out with the shirt in one hand and a coffee in the other.
👉 Come see what we’ve been brewing https://t.co/4EbMnJMvTM #BlackHat#BHUS
We're bringing The Sweet Stop to Black Hat ☕
Aug 5–6 🍭 Mandalay Bay 🍭 Booth 5721
Barista-made coffee, live runtime demos & a first look at how Sweet stops bad behavior in runtime.
👉 Coffee's on us - reserve your 20-min session: https://t.co/uz1xWlNoJ1
🇺🇸 Happy 4th of July - 250 years of American independence!
To our US team, customers, partners, and the security community: thank you for being part of our journey. Wishing you a safe and joyful holiday from all of us at Sweet! 🎆
#America250#FourthOfJuly
🎙️ Our CEO & co-founder Dror Kashti joined @avivfrenkel podcast @calcalist. It's in Hebrew, but the themes translate 👇
30+ years in Israel's cyber establishment, why "agentic" isn't a dirty word & why he's happy to spend on AI tokens.
🎧 https://t.co/Si0F6qeGTU
The gap between granted access and used access is where most identity risk hides.
Introducing Sweet Entitlements: runtime-powered visibility into permissions, identities, and access paths.
Read more: https://t.co/hqAEYdvXFJ
Big milestone for Sweet Security: we're expanding into the U.S. federal market and pursuing FedRAMP Moderate authorization, with @Coalfire supporting our journey.
Learn more: https://t.co/YqsNFnVE7w
#FedRAMP#CloudSecurity
@ShipStation Global's Birat Niraula on going from vulnerability management to breach prevention. With Sweet Attack, his team targets the attack paths that actually matter - fixing real risks before they're exploited. https://t.co/up7zcFVHKD #AISecurity#AIRedTeam#SweetAttack
Another read on Sweet Attack. 📰
TechDay US gets to the core of why we built it: fewer theoretical findings, more proof of which attack paths work.
Sweet Attack exposes attack chains with evidence and remediation paths.
Read more: https://t.co/6tPHL1WrN5
#AISecurity
@TechstrongGroup looks at Sweet Attack 🔎
As AI changes offense, red teaming needs to evolve too.
Sweet Attack uses runtime intelligence to validate exploitable attack chains and show what made each path work.
Take a closer look: https://t.co/qn9xrtx69z
#AISecurity
Sweet Attack is already making headlines. 🗞️
SecurityWeek covers the shift behind our launch: AI red teaming only works when the agent understands the real environment.
Sweet Attack validates the paths attackers would actually take.
Read the coverage: https://t.co/TPCREYILgu
Attackers rarely move one finding at a time.
They chain vulnerabilities, identities, APIs, permissions, and runtime behavior into usable paths.
Sweet Attack validates exploitable attack paths, so teams know what to fix first.
See how: https://t.co/MruD4sGRY5
#RedTeam#Mythos