The Part 2 article is now up (link below). It shows using the exploit we examined in Part 1 to target Chrome and other adjacent processes to pull interesting artifacts out of memory.
https://t.co/E1H2IV8oJY
watchTowr Intel has observed exploitation attempts against N-able N-central honeypots overnight following the “Able2Shell” zero-days being dropped.
Audit for signs of compromise, restrict access, and follow vendor guidance on mitigation steps.
If you need help, reach out via our website.
https://t.co/dcZjy3Rsdv
Only just started my day and this was in the news feed on my phone...its going to be a good week.
It sends and email everyday with details of how much spare ram you have.
‼️ A default "admin:admin" password helped researchers unlock and start connected cars remotely.
Two car brands' identity systems were vulnerable to account takeover. Researchers demonstrated the full attack chain on authorized U.S. vehicles.
Read ↓ https://t.co/1xCBkexLhP
‼️ A default "admin:admin" password helped researchers unlock and start connected cars remotely.
Two car brands' identity systems were vulnerable to account takeover. Researchers demonstrated the full attack chain on authorized U.S. vehicles.
Read ↓ https://t.co/1xCBkexLhP
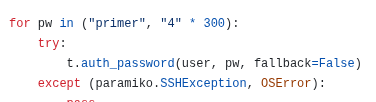
Euuuughhhhhh all the sshhole scripts that are like 400+ lines longggggggggggg
Made a smaller one...or you could...you know...just type a bunch of A's into a box I guess.
https://t.co/39kfl47ABv
I'm winding down my time in the Apple Security Bounty program — so I'm open-sourcing the research. 100+ PoCs, real CVEs, and the fuzzers that found them. Public repo 👇 https://t.co/fKuaWiLUHA