🚨 New Blog Published!
From a simple Contact Us form to full server compromise — a practical case study on Server-Side Template Injection (SSTI) leading to RCE.
Read the full write-up 👇
https://t.co/Ao4YMbiVvc
🔐 Client-side encryption ��� confidentiality
During a recent AI chatbot security assessment, I found that encrypted responses could be decrypted in the browser because the required key material was already exposed to the client.
yo. anyone else tired of the murky UX of GNU screen and other terminal multiplexers I won't call out here!? so were me and my boy Claudio!
so we sat down for a week and reward-hacked and dogfed a new terminal multiplexer into existence: slosh
I am standing on the shoulders of giants of course; massive shoutout to @mitchellh and the rest of the contributors of libghostty-vt!
below you will find a small preview teaser for slosh I recorded the other day. slosh makes the mouse a first-class citizen again and introduces the concept of terminal "shaders". these shaders can be applied to the chrome or the contents of a terminal pane. and you can (ab)use them for all sorts of useful things: dimming inactive panes, drawing attention to panes that got a BEL, visualizing scrollback with fades, and many other interesting things.
I have battle-tested it a fair bit, and the full development/clank seshes were streamed on sl0p dot foo. if there's enough interest, I will carry on, start properly packaging it, and try to be a good maintainer for this new toy.
so just to be clear; everything you see in the video is rendered inside of a single "native" (somewhat modern) terminal. you can `ssh` into a box, `slosh` to attach/spawn and get this experience.
there's more cool stuff not demo'd in the video! random example: responsive layouts. if your terminal window becomes too narrow it'll start rendering the pane grids as a single "stack" instead. so managing your slosh working env from an iPhone (example) becomes chill. (also expands to original grid layout again once terminal grows again, etc.)
RT for reach would be welcome! 🙏
P.S. soundtrack has been composed by `tristan` from Kakiarts, and is featured in their 64KiB demo "Vortex 2" :)
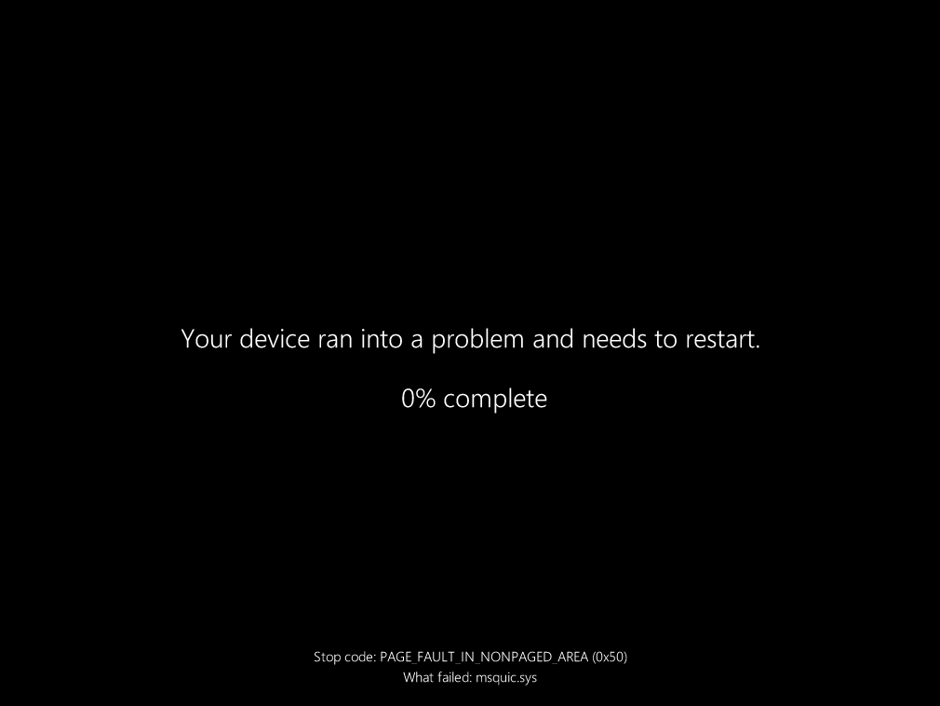
Microsoft's QUIC had a UAF (CVE-2026-62815), which can cause a BSoD on IIS with http/3 configured or SMB over QUIC. PoC included.
Both non-default, but internet-exposed assets are more than I expected.
Read more https://t.co/IrCWbIuQ0M
@prakashraaj@mkstalin gaaru would go as one of the greatest politician in history of TN-
In the era of dirty political games, this man stood for MORALS & ETHICS-
Thalaivaar @mkstalin 🫡🫂❤️
Credential Guard was supposed to end credential dumping. It didn't.
@bytewreck just dropped a new blog post detailing techniques for extracting credentials on fully patched Windows 11 & Server 2025 with modern protections enabled.
Read for more ⤵️ https://t.co/mYPHg1mTKj
The watchTowr Labs team is back, providing our full analysis of the Oracle E-Business Suite Pre-Auth RCE exploit chain (CVE-2025-61882).
Enjoy with us (or cry, your choice..)
https://t.co/ffDKb723N6
@rana__khalil This course looks amazing! 🚀 Excited to dive deeper into OAuth 2.0 vulnerabilities and hands-on labs 🙌 Thanks for creating such valuable content @RanaKhalilAcad 🔒
🎉 New Course Alert + Giveaway! 🎉
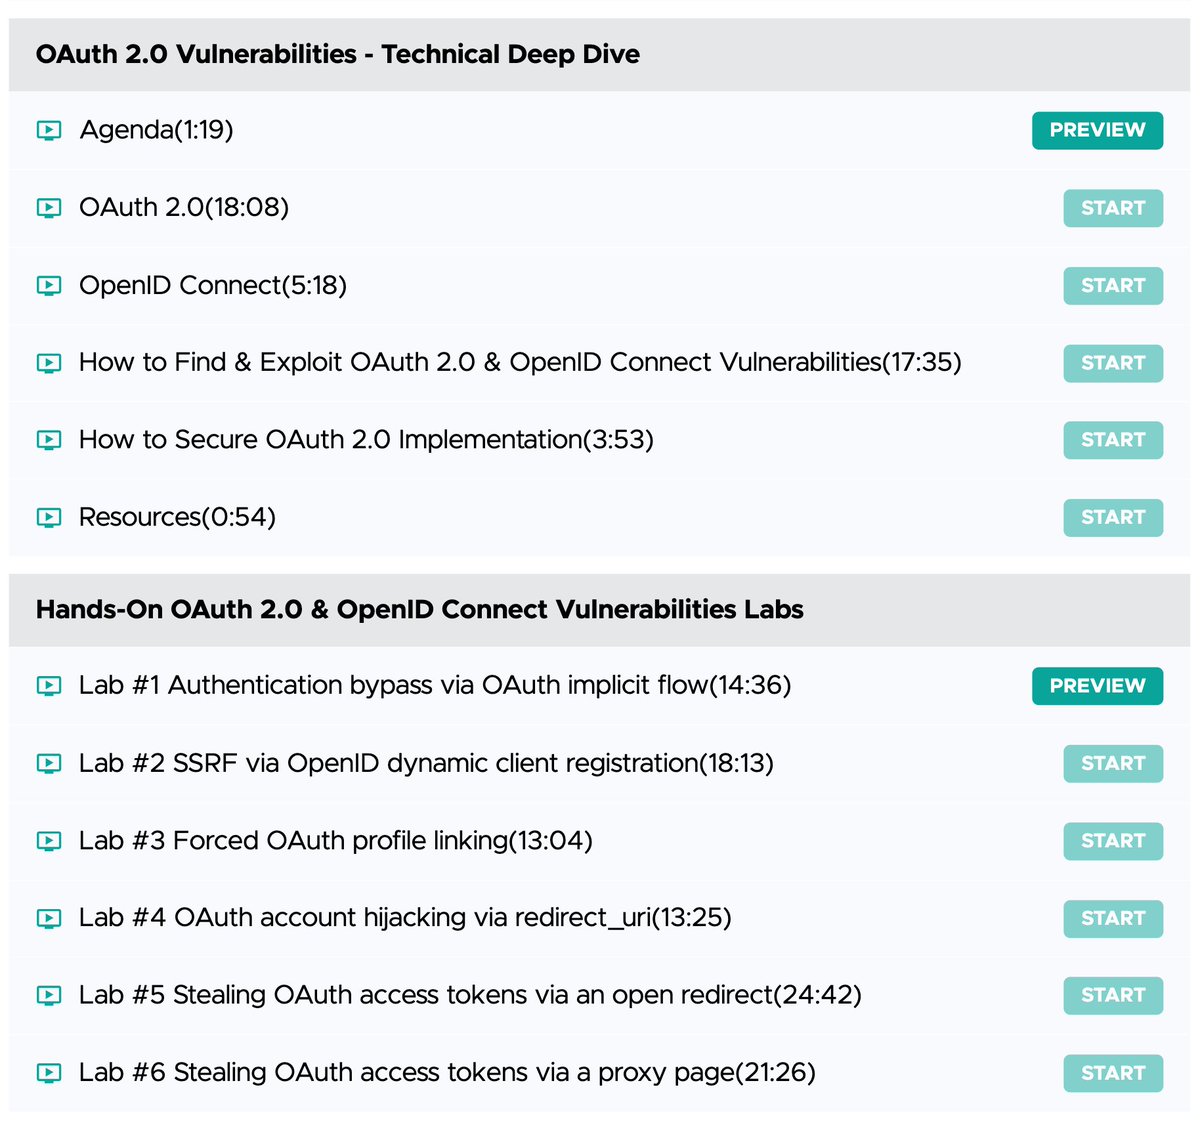
I'm excited to announce a brand-new course on Rana Khalil's Academy - OAuth 2.0 Vulnerabilities.
This course includes:
📚 A technical deep dive into OAuth 2.0 and OpenID Connect: what they are, how they work, the common pitfalls in implementation, the vulnerabilities that can arise, and best practices to keep your applications secure.
🧪 6 hands-on labs
📃 Subtitles in 6 languages for all the videos in this course
👉 Course Link: https://t.co/R3YzBnyCqQ
🎁 To celebrate the launch, I’m giving away 5 FREE 30-day All-Access Memberships to the Academy. To enter the giveaway:
1️⃣ Follow @RanaKhalilAcad.
2️⃣ Comment on and retweet this tweet.
Winners will be announced on the 13th of September. Good luck! 🧡
@rana__khalil This course looks amazing! 🚀 Excited to dive deeper into OAuth 2.0 vulnerabilities and hands-on labs 🙌 Thanks for creating such valuable content @RanaKhalilAcad 🔒