La contraseña del complemento era… ninguna. Y con eso entraron a 288 compus de 48 empresas. Díganle al hacker que estamos contratando… pero para ponerle contraseña a las cosas jeje
Attackers are using cloud-hosted ScreenConnect panels to install rogue clients on managed endpoints.
Don’t triage infected hosts with ScreenConnect. Connecting can spread the malware to your workstation and other panels you can access.
Details and IOCs: https://t.co/DE0aXUVket
Security issue; Humble Bundle decided to slop their new website but 'forgot' to add 2FA, meaning it's now removed from your account. At the very least change your password... which you can do without entering your previous because what even is security 👍
https://t.co/u0Rl6525w7
Anthropic supo desde mayo que una extensión del navegador podía poner a Claude a ejecutar comandos en tu compu. Y en vez de solucionarlo, dijeron ese error ya lo había visto así déjalo🙃
Si eso hace el proveedor, ¿quién está cuidando los permisos de tu agente de AI…
#EXCLUSIVE: A vuln in Anthropic's Claude products lets any browser extension that can control Claude Dispatch make Claude Desktop run code on the computer – no browser exploit and minimal user interaction required. More here: https://t.co/ernp61n0Xa
🤖 Una red criminal usó agentes de IA para atacar a más de 400 bancos y fintech en Latinoamérica y reunió 4.493 registros robados.
👉 Más información: https://t.co/zeykVHH5P1
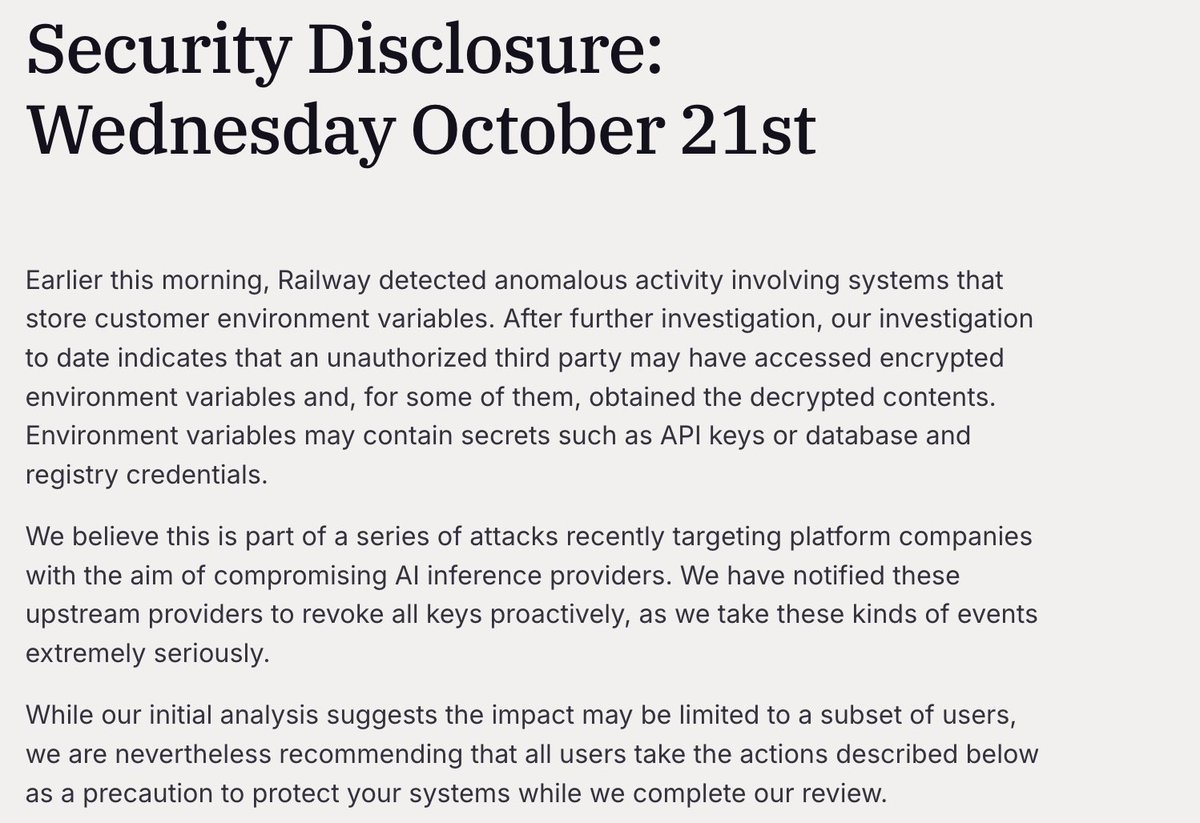
BREAKING: @Railway SAYS THAT "AN UNAUTHORIZED THIRD PARTY MAY HAVE ACCESSED ENCRYPTED ENVIRONMENT VARIABLES AND, FOR SOME OF THEM, OBTAINED THE DECRYPTED CONTENTS. ENVIRONMENT VARIABLES MAY CONTAIN SECRETS SUCH AS API KEYS OR DATABASE AND REGISTRY CREDENTIALS"
RECOMMENDS IMMEDIATE ROTATION OF ALL RAILWAY ENVIRONMENT VARIABLES, API KEYS, AND REGISTRY CREDENTIALS
Una empresa de bases de datos EN LA NUBE dejó sus llaves en su propio código y le sacaron datos casi un mes sin que nadie se diera cuenta.
Si a ellos les pasa, imagínate el Excel: 'contraseñas_final_v2' de tu
oficina 🫨
https://t.co/sTrXpz40DD
tried dsv4.1-flash-1017 abliterated just now & feel sick to my stomach.
for context, "abliterated" models have the weights responsible for making the base version refuse illegal requests removed. you can ask them to help with things like hacking or violence & they'll just comply.
they make it trivial to hack businesses running old software. e.g. getting guest data for a motel with some old asp site.
abliterated models have a catch-22 in that the only way to harden your systems against them is to use them to run penetration tests against yourself.
in theory, this sounds similar to buying a gun to defend against others who own guns, but it's different in practice since there's a 100% chance that you're going to use the abliterated model to protect yourself whereas there are low odds that you'll actually use the gun.
when you point the abliterated gun at your own infra, who knows what it's going to do? it could just as easily hack you & exfiltrate data as it could protect you. most users aren't going to meticulously watch traces to make sure it behaves safely.
given this, my new take is that gpu compute is going to become a federally regulated resource. abliterated models in the wrong hands are a national security risk.
used to believe all the people at the labs thinking about safety were wasting their time, but now i'm feeling grateful. they're doing very important work.
@skeptrune The scariest part isn't banks or governments, it's the small business running a 10-year-old site nobody patches. The attacker doesn't need to be an expert anymore, just patient.
OpenCode tenía las API keys de sus usuarios en un sistema legacy que ya iban a apagar. Hay quien reporta $1,700 USD en cargos que no hizo.
El famoso 'Luego lo vemos' también es una vulnerabilidad 🙃.
https://t.co/WHuDxW2LpV via @TheHackersNews
The most important coding skill: read.
Teach yourself how to read.
Read the agent output. Read the blog post. Read the paper. Read the code (if it applies to you).
Don't summarize.
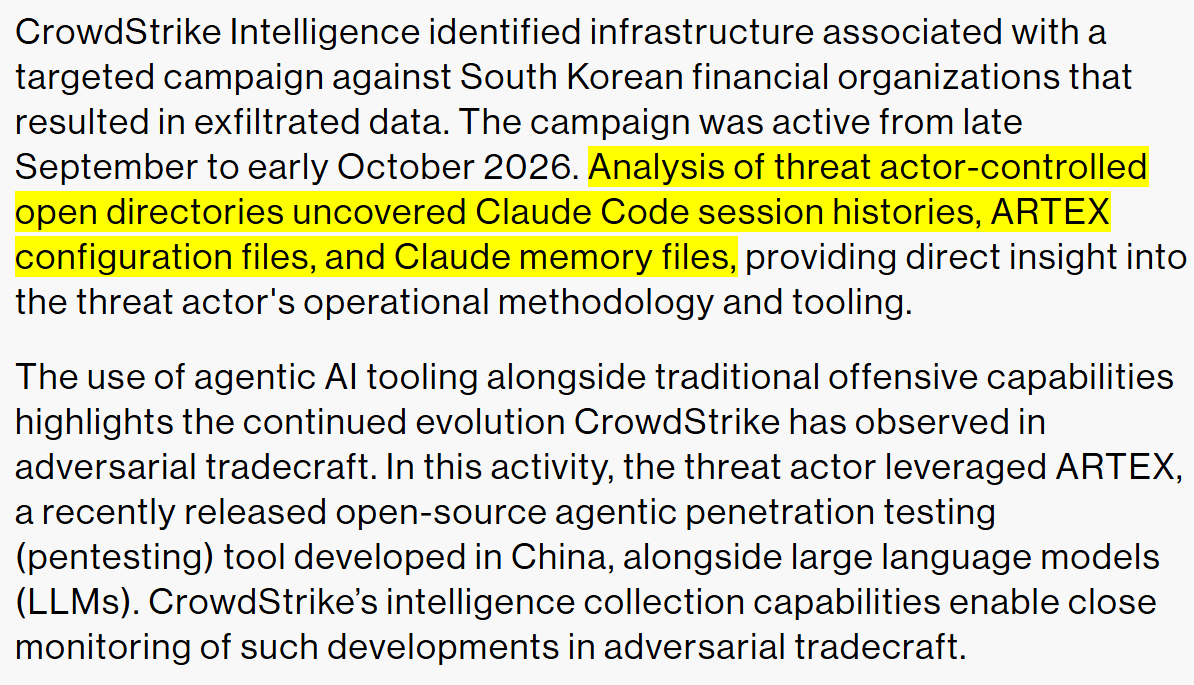
🚨HOLY MOLY. A hacker suspected of attacking South Korean banks may have accidentally unmasked himself in the most ridiculous way: asking Claude Code to write a résumé highlighting his own hacking operations, complete with his personal details.
CrowdStrike traced the attacks to infrastructure running an AI hacking tool called ARTEX. Investigators then discovered publicly exposed folders on another server containing the hacker's saved Claude Code conversations.
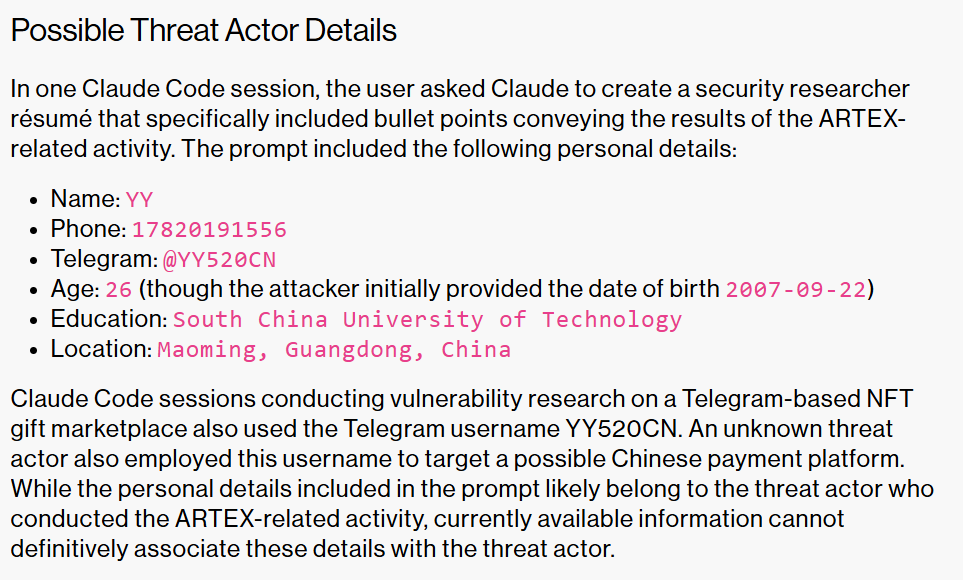
In one chat, he asked Claude to write a cybersecurity résumé describing his ARTEX activities, supplying his phone number, Telegram handle, claimed age of 26, university and location in China. The same Telegram handle appeared in other hacking-related sessions.
He had also asked Claude where stolen Korean data is typically sold. His identity remains unconfirmed.
🚨HOLY MOLY. A hacker suspected of attacking South Korean banks may have accidentally unmasked himself in the most ridiculous way: asking Claude Code to write a résumé highlighting his own hacking operations, complete with his personal details.
CrowdStrike traced the attacks to infrastructure running an AI hacking tool called ARTEX. Investigators then discovered publicly exposed folders on another server containing the hacker's saved Claude Code conversations.
In one chat, he asked Claude to write a cybersecurity résumé describing his ARTEX activities, supplying his phone number, Telegram handle, claimed age of 26, university and location in China. The same Telegram handle appeared in other hacking-related sessions.
He had also asked Claude where stolen Korean data is typically sold. His identity remains unconfirmed.