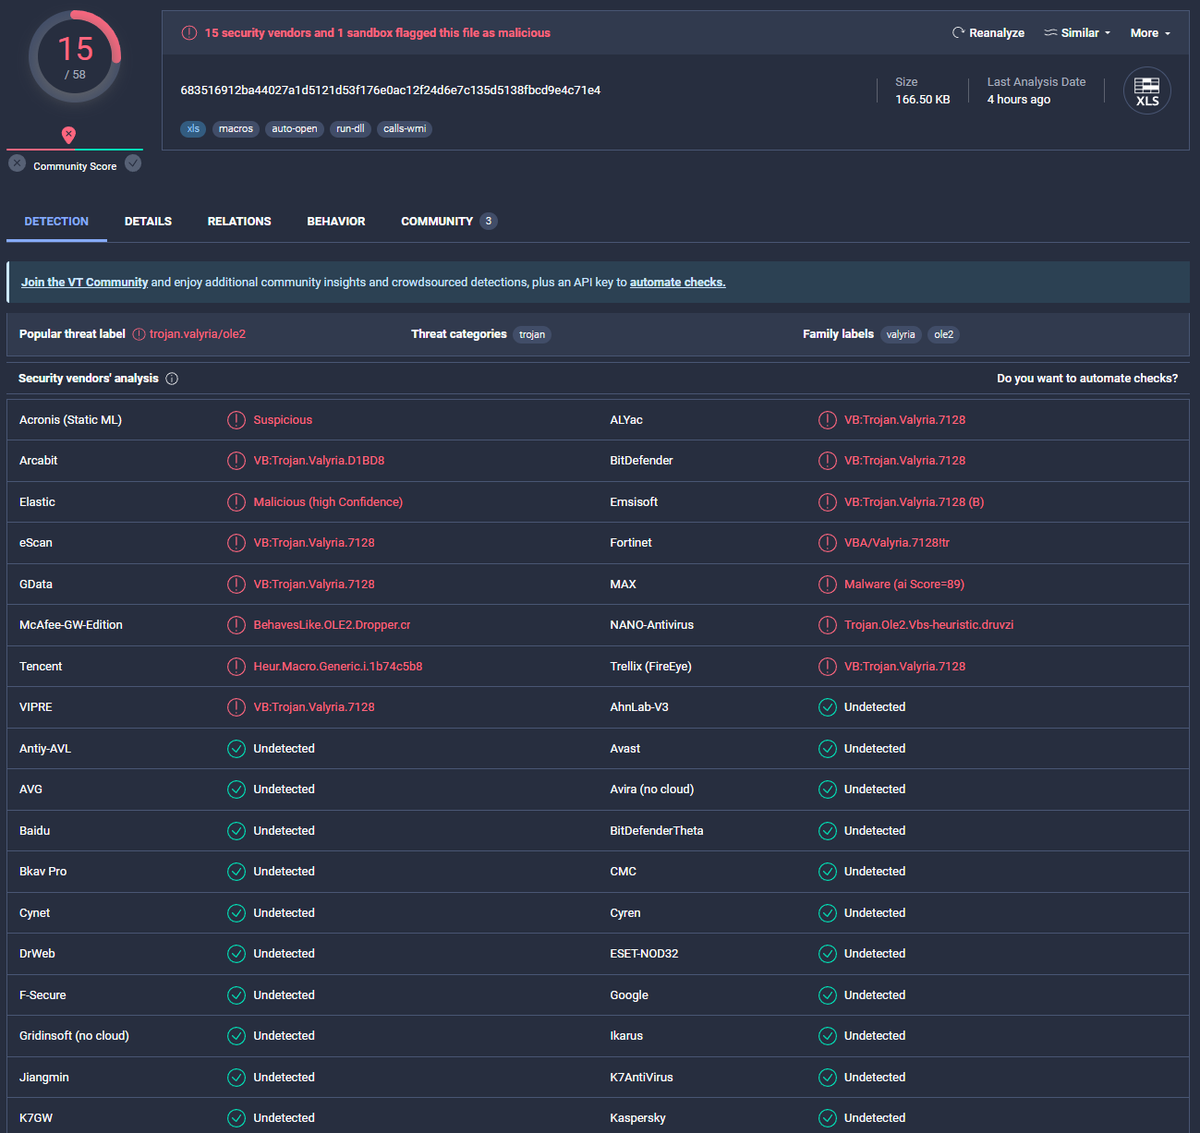
MISTPEN 2ff5f461ae6b94b7cae8114c94d55fe3f4f40fc30db82446a62758e532557de7 uploaded from Romania. Can be decrypted by b68a90b703750beaff2869b686c4adddcd47702d6a06b591ee7ac22b67d331b0
#Lazarus#Dreamjob
@GroupIB_TI#CobaltStrike beacon was deployed via a webshell that was planted by exploiting the #ProxyShell vulnerability. This #HsHarada campaign targets healthcare and healthcare-adjacent organizations, and relies on https://t.co/6KNZHf99qe
While 66% of businesses suspect insider attacks, reality proves different. A recent incident our Responsemen handled had a surprising twist. Watch our comic book and read the full story on our blog: https://t.co/Hbz0GXwmCG
#IncidentResponse#FightCyberCrime#CyberSecurity
Our DFIR team launched their channel and started with perfect case which shows collaboration between @GroupIB_TI and @GroupIB_DFIR . Subscribe to know spicy details of our real life IR cases.
Last Christmas, Group-IB flagged a C&C server tied to SystemBC backdoor. Quick alerts led to rapid response, safeguarding a European firm from looming #ransomware. Distinct tactics pointed to two threat actors: an access broker and a ransomware assailant.
🔍 Further analysis has unearthed 🕳️ more potential infrastructure linked to the same adversary 😈 using a simple pivot from the CobaltStrike IP and SSH Key.
What's even more intriguing is that the same SSH key is being used by #Truebot.
🔹88.214.25.242 0/88 VT
🔹5.188.87.37 11/89 VT
🔹45.227.255.34 1/89 VT
🔹45.182.189.118 9/89 VT
🛡️ Stay on your toes and remain vigilant! 🚨 #CyberSecurity #Pikabot 🤖
In the spirit of "this talk could've been a tweet", I just pushed a button:
#BinDiff is now open source.
- Snapshot release, no major new functionality
- Release binaries later today or tomorrow
- This is my 20% and I won't we able to act on PRs until end of Q4 (OOO traveling)
#Silence gang started a new campaign and deployed few #CobaltStrike servers:
tsvsnjv[.]com
rokllofrold29[.]com
rokllold279[.]com
Attribution is based on CS watermarks and the unique domain names template. Final stage is a ransomware, possible types: #CL0P, #bl00dy.
Group-IB has made a key contribution to the #INTERPOL-led Africa Cyber Surge II operation that spanned 25 countries. Group-IB shared more than 1,000 indicators related to malicious infrastructure across Africa. This successful initiative led to arrests of 14 suspects. More details: https://t.co/P88ORhgrQP
@INTERPOL_Cyber #FightAgainsCybercrime
#Gigabud#RAT is out there expanding its capabilities and targets. Our team recently dissected the fraudulent techniques employed by Gigabud’s operators, using the Group-IB Fraud Matrix. The detailed investigation uncovered more than 400 separate Gigabud.RAT samples, and we outline how the #trojan operates, its previously unknown variants, and the potential risks to organizations, particularly across the Asia-Pacific region. Dive into the full investigation here: https://t.co/FoDWVoIj5O
#FightAgainstCybercrime
Group-IB provided key intelligence that contributed to an INTERPOL-led operation aimed at disrupting the activities of 16shop, a notorious phishing-as-a-service platform, that led to the arrests of three suspects in Asia-Pacific region. More details: https://t.co/DR5Yu6Rl5h
@INTERPOL_HQ@INTERPOL_Cyber
#FightAgainsCybercrime
Global geopolitical conflicts frequently serve as catalysts for #hacktivist activities. In a comprehensive overview, @GroupIB specialists have traced Mysterious Team Bangladesh’s attacks, uncovering their timeline and distribution. Check out or new blog: https://t.co/DYaotuO1nE
Many thanks to everyone who contributed into the investigation and worked with us together (especially @OrangeCertCC and @c_APT_ure) in making the cyberspace safier.
🤝 Group-IB has assisted in the INTERPOL-led Operation Nervone, aimed at successfully disrupting the operations of the cybercriminal syndicate #OPERA1ER in French-speaking Africa. More details: https://t.co/aZ2DmzIboX
@INTERPOL_HQ@INTERPOL_Cyber