Tanto Security is a leading provider of advanced offensive cyber security services to leading organisations across Australia, New Zealand and North America.
Our website was getting a bit stale, so we gave it a glow up 💅
Check it out, peep our blog posts and sign up for our newsletter if you need more Tanto Security in your life – https://t.co/sJCW7LN7tS
🚨🚨🚨
From Arbitrary File Read to Shell: Yet Another RCE in Telerik
In that post, we exploit an arbitrary file read via RadImageEditor's image cache to leak web[.]config and, if it contains the right secrets, turn it into RCE!
Update now to 2026.3.812.
https://t.co/YrCH4Zd3Gv
We are beyond giddy to be releasing tturl, the HTTP/2 CLI for finding tiny timing differences and winning request races. Our Director of Research @justinsteven can't wait to tell you all about it at @BSidesCbr today, 3:15PM on the main stage 😎
https://t.co/yAIieTPNiW
The entire Tanto Security team will be at @BSidesCbr this wk. We look forward to catching up with friends and supporting our colleagues who are getting up on stage... and we'll have lots of them! With SEVEN talks. Plus we got swaggggg to give away.
Four years running!
@TantoSecurity has sponsored BSides Canberra every year since 2023 and they contribute some pretty amazing talks along the way.
Thanks for continuing to support BSides both on and off the stage! ❤️
https://t.co/gkjnHOcFKc
🚨 A public Telerik UI PoC chains a padding oracle into unauthenticated RCE.
TantoSec’s exploit for RadAsyncUpload forges encrypted state and loads a DLL, but only on specific non-default configurations.
Inside the chain → https://t.co/tmvIIbR3Ns
🚨🚨🚨🚨🚨🚨
From Padding Oracle to Shell: Unauthenticated RCE in Telerik UI for ASP[.]NET AJAX
https://t.co/H0ZBJ4R05d
The vulnerabilities described in this post were discovered, analysed, and exploited with some AI assistance, and a lot of old-fashioned human persistence.
Our brilliant and talented Sam picked up a 4G industrial router from a second hand store, and as they say in the biz, what he found will shock you.
Check out the blow-by-blow as he wound up logged in to a "fake" root account. Full dets over on the blog: https://t.co/nENmrqb1C9
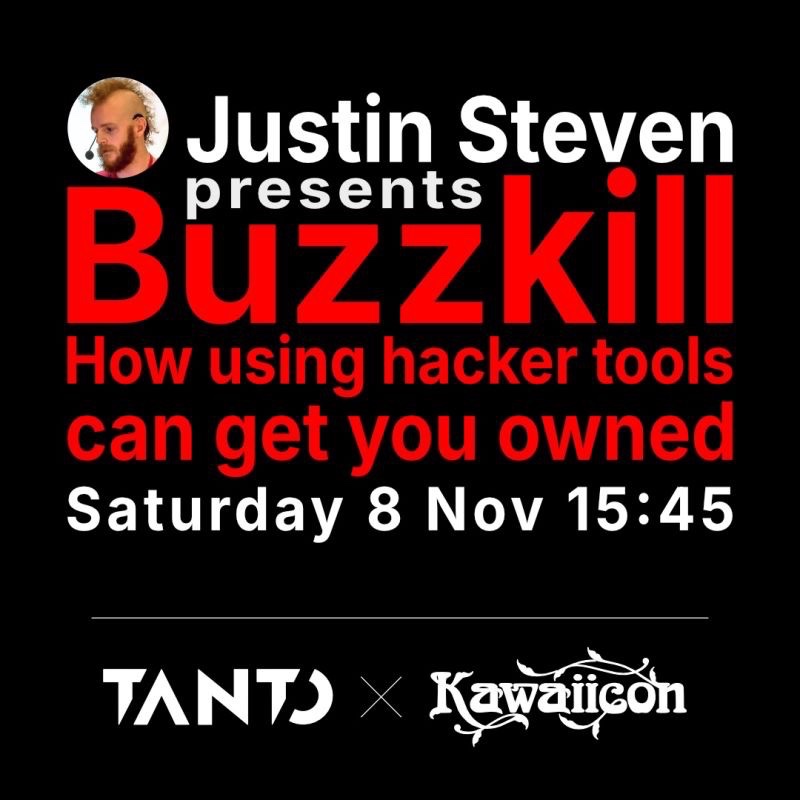
@justinsteven
hits the main stage today at Kawaiicon. If you can’t be in Wellington the live stream is here: https://t.co/TFD8Upmgol. It’s going to be a lot of fun 🤩
Congratulations to Noah and Jesse for their awesome talk yesterday!
🔥ℝ𝕖𝕒𝕕𝕪 𝕥𝕠 𝕓𝕣𝕖𝕒𝕜 𝕥𝕙𝕖 𝕤𝕥𝕒𝕔𝕜 𝕒𝕟𝕕 𝕡𝕨𝕟 𝕥𝕙𝕖 𝕙𝕖𝕒𝕡?
Corelan Stack (Feb 3-6) + Heap (Feb 9-12) in Melbourne 🇦🇺 — the ultimate exploit dev combo, back to back 💥
Do both = earn your shot at CCED 😈
Seats 👉 https://t.co/DckcMarpVW
💛 Sharing = caring
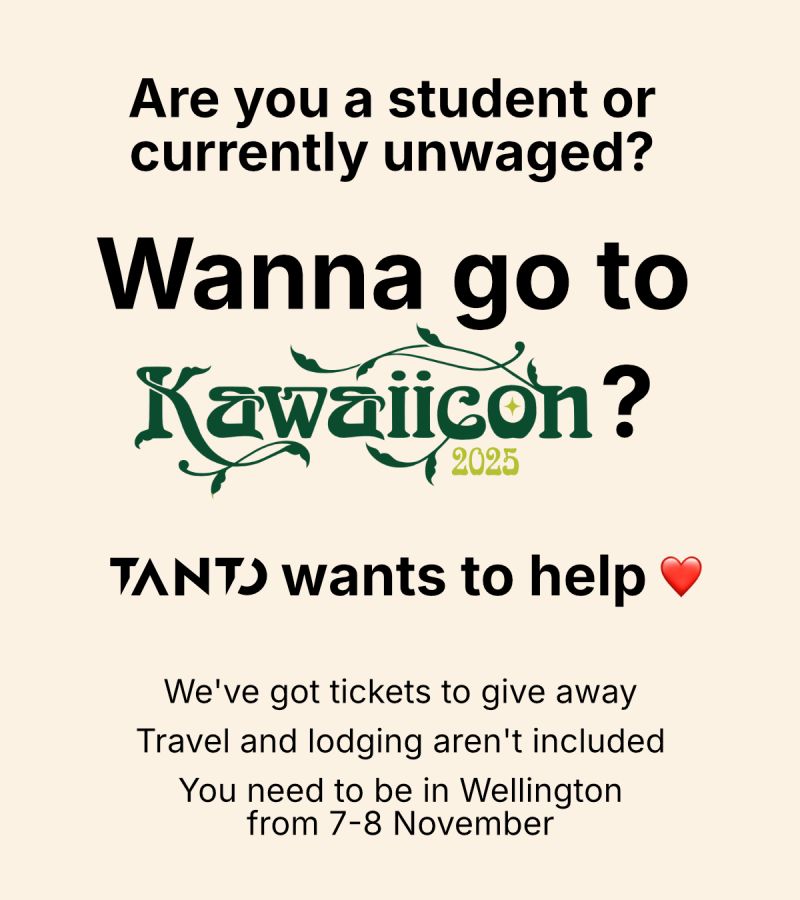
Are you going to be in or around Wellington on the 7th-8th November? Are you a student or currently unwaged? TantoSec wants to get you to Kawaiicon❤️
We have tickets to give away. They cover entry to the con only. Travel & accom aren't included. Send us a DM if you can make it😎
🚨BBOT Security Advisory🚨
4 fresh CVEs (2 CRITICAL RCE) can give a clever defender RCE on your attack box if you’re on BBOT <2.7.0.
Hat tip to @justinsteven of @TantoSecurity for the catch. 🙌
Details 👉BLS Blog https://t.co/mo9BO00gyB
#infosec#CVE
@BSidesCbr is just around the corner and we've got six talks booked in. Starting tomorrow with CrestCon then 5 spots at BSides from Thursday to Saturday. If you are coming along come say hi and we'll have stickers and t-shirts to give away!
We think @DownUnderCTF does incredible work, and Tanto Security is proud to have been a sponsor since 2023. Thank you friends for letting us pentest your new scoreboard, and we'll see you for DownUnderCTF 7 in 2026 🫡
Tanto Security ❤️ @DownUnderCTF - and when they asked us if we could do a pentest of their new brand new CTF scoreboard we knew we had to say yes.
With their permission we are proud to release the full pentest report today! 👇
@DownUnderCTF have published their annual infra writeup at https://t.co/LEmHDa7Kc6 and today's an extra special day, because they're open sourcing their scoreboard, noCTF! 🎉 we think it's pretty dang good (and probably pretty secure)
🚆🚄🚅🚉🛤️🚃🚂
Training Alert!
We are partnering with @corelanc0d3r to bring his amazing exploit dev workshop to Melbourne for the first time. Want to take your exploit dev to the next level? Check out https://t.co/MUYhX0W98C Early Bird Discounts if you get in before October 1