🚨 Hackers are exploiting a WinRAR flaw to plant malware in government systems.
Silent Lynx used CVE-2025-8088 to drop PickleShell, a custom reverse shell, into the Windows Startup folder for execution at the next login.
Full story: https://t.co/OMiwURtjxX
‼️ Breaking: First-ever Zero-Click Mercenary Spyware Delivered via Targeted Ads
Details: https://t.co/OWlUptCmGp
Simply viewing an online advertisement can be enough to infect a device with powerful spyware, without the user clicking, downloading a file, or seeing any warning.
Citizen Lab researchers documented what they call the first public technical proof of zero-click mercenary spyware delivered through targeted ads.
The method, named “AdFection,” infected devices at international news network Al Jazeera with spyware linked to Israeli vendor Candiru, which now operates as Integrity Labs. For users and organizations, the case shows that careful clicking alone cannot stop every infection.
#cybersecuritynews
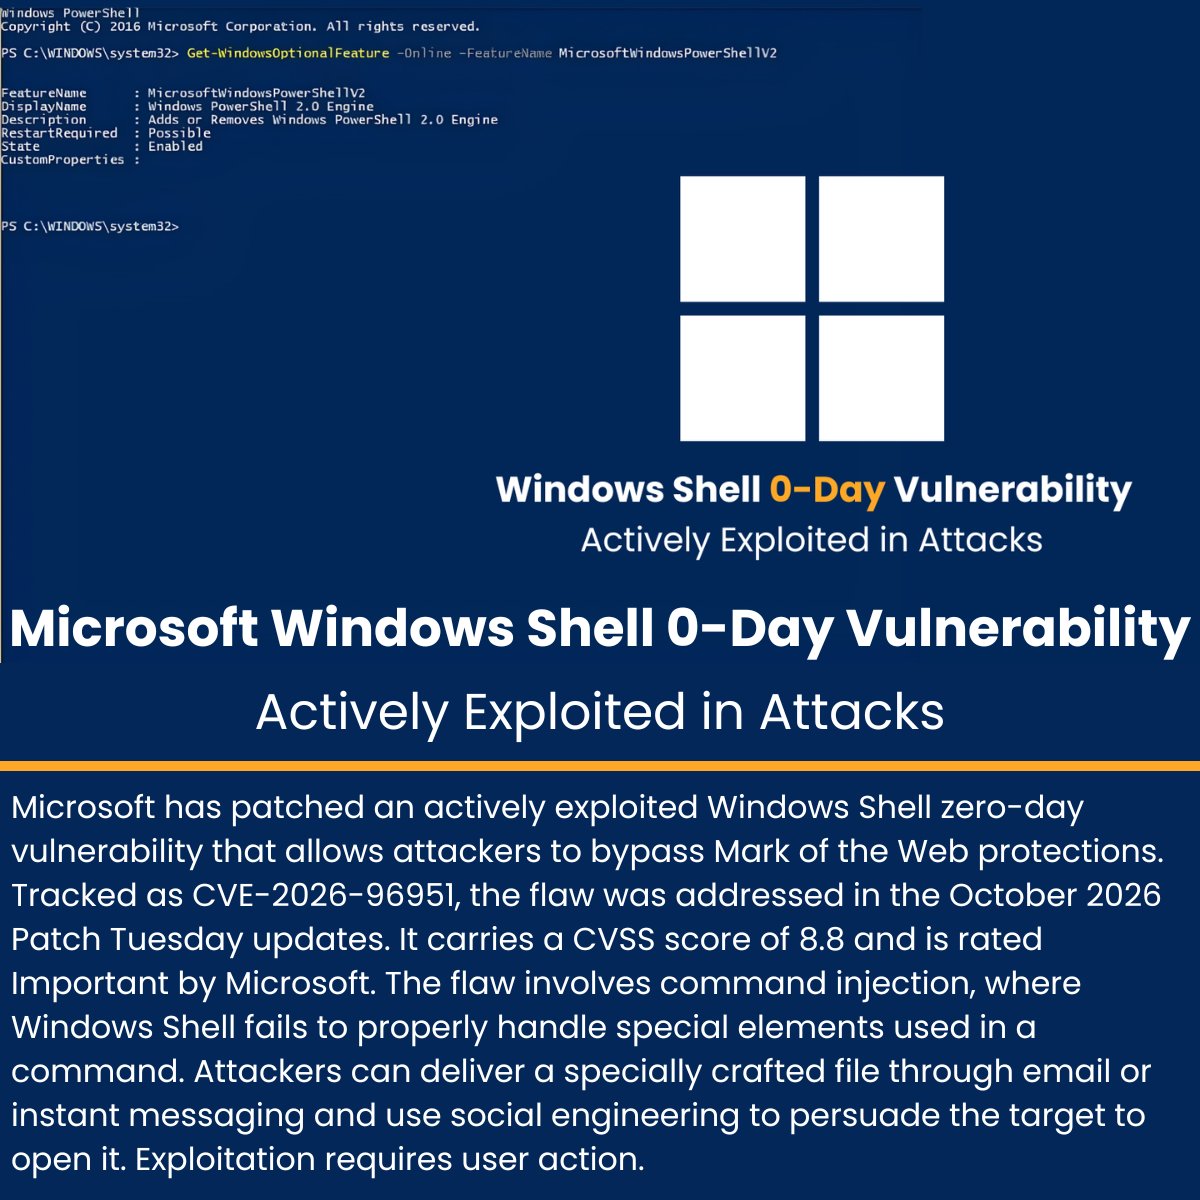
‼️ Microsoft Windows Shell 0-Day Vulnerability Actively Exploited in Attacks
Details: https://t.co/Uv2Ip8fDnI
Microsoft has patched an actively exploited Windows Shell zero-day vulnerability that allows attackers to bypass Mark of the Web protections. Tracked as CVE-2026-96951, the flaw was addressed in the October 2026 Patch Tuesday updates. It carries a CVSS score of 8.8 and is rated Important by Microsoft.
The flaw involves command injection, where Windows Shell fails to properly handle special elements used in a command. Attackers can deliver a specially crafted file through email or instant messaging and use social engineering to persuade the target to open it. Exploitation requires user action.
#cybersecuritynews #Microsoft
‼️ Attackers Reportedly Hack Supermarket Fridges and Raise Temperatures to 50°C
Details: https://t.co/fQd0VMaNpf
French supermarket chains are dealing with a major cybersecurity incident after attackers reportedly changed refrigeration settings remotely, causing some chilled cabinets and freezers to heat up instead of cool down.
The incident began overnight between October 11 and October 12 and affected stores linked to Intermarché, E. Leclerc, and Système U, according to early reports. The cyberattack is believed to have targeted refrigeration-control systems made by Danish industrial technology company Danfoss.
In the affected stores, attackers reportedly changed the settings to trigger continuous defrosting and set temperatures as high as 50°C.
#cybersecuritynews
‼️ Admin Password “123456” Led to 8.8 Million Danish CPR Data Breach
Details: https://t.co/vnQPZvyTNq
A weak administrator password is linked to a major Danish data breach that exposed information tied to about 8.8 million national identification numbers. At least three accounts at Pays, an IT company on the island of Funen, reportedly used “123456”, including an administrator account.
The case shows how poor security at a company with trusted access can place a national database at risk. Pays had permission to search Denmark’s Central Person Register, known as CPR.
#cybersecuritynews
‼️ Hackers Abuse Microsoft Defender Exclusions to Hide Malware From Antivirus Scans
Read more: https://t.co/8Sahm5DVoN
Hackers are abusing Microsoft Defender Antivirus exclusions to keep malicious files outside routine security scans. Rather than switching protection off completely, attackers can leave antivirus running while creating gaps around malware staging folders and selected file types.
This is an established evasion technique, not a new malware family. It requires administrator privileges or higher, making it a step after attackers gain sufficient control. Defender supports exclusions for paths, file extensions, processes, and IP addresses.
#cybersecuritynews