@Sverrevh I've stopped using it for a while now, and the last code I used is what's currently in my repository. I do have plans to setup again and update to the latest official version (20.06.2~) but there is no definite schedule. DM is welcome if you need further discussion.
#ESETresearch unveils another APT group, #FamousSparrow, that exploited the #ProxyLogon vulnerability in March 2021 and carried out cyberespionage activities against hotels, governments and private companies worldwide https://t.co/3RSbX5xO7I @matthieu_faou Tahseen Bin Taj 1/6
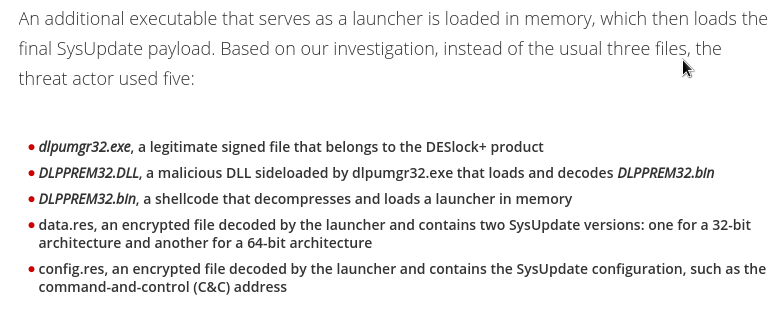
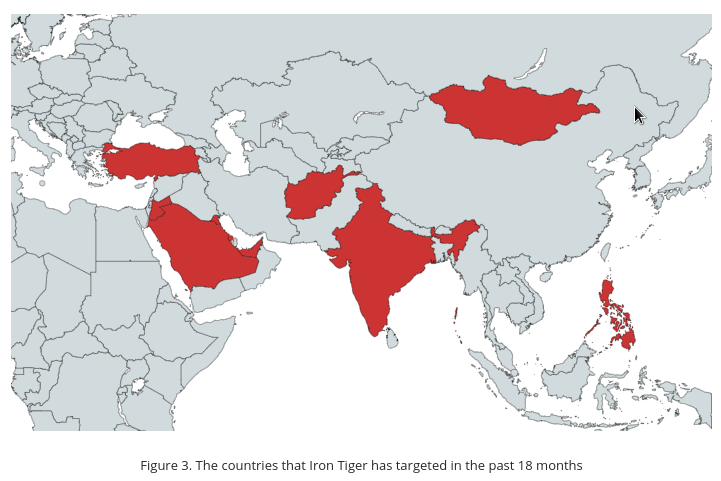
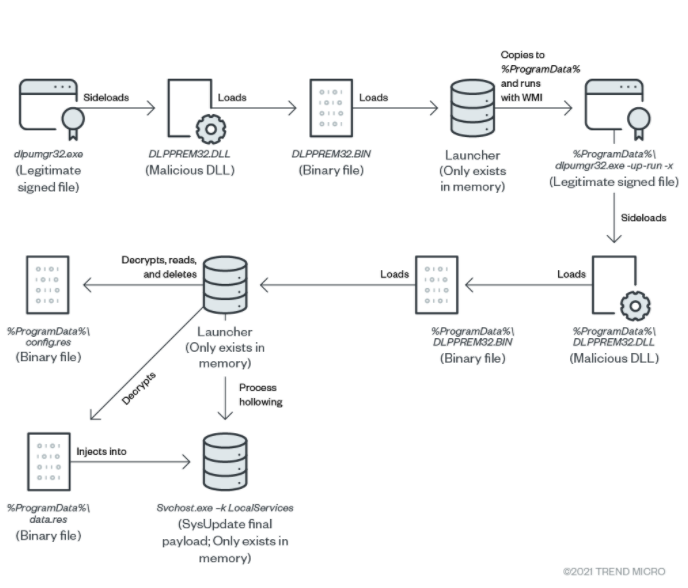
Our latest research on #IronTiger (APT27) is out ! We disclose a new method for dropping the SysUpdate malware that uses 5 files instead of the typical triad, as well as a rootkit that hides other threat actor's backdoors that we discuss in the blog https://t.co/c7vZZBW3rI
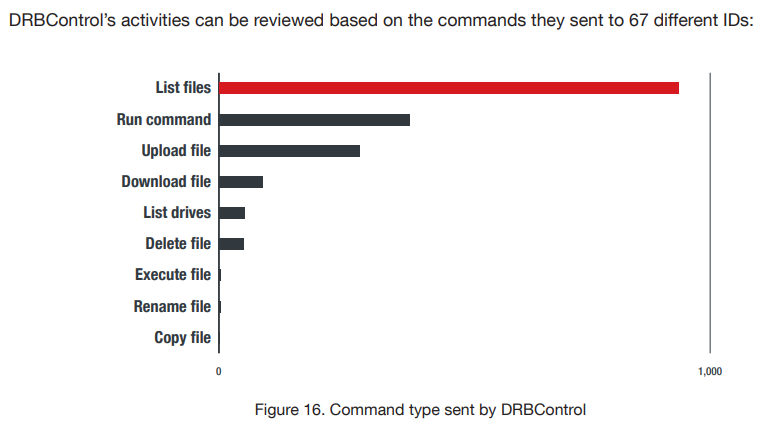
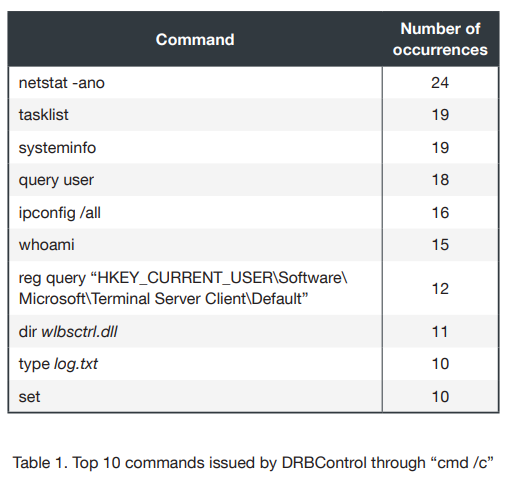
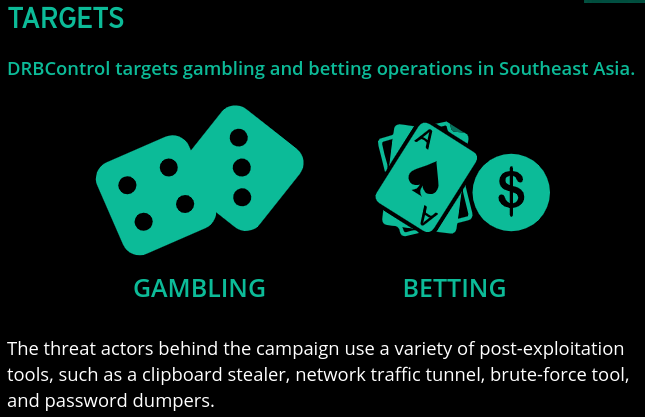
For those who enjoy #APT attribution nightmares, here goes another one. During our #DRBControl investigation, we found some links to #Winnti and #EmissaryPanda. I recently stumbled upon the Secureworks' report about #MustangPanda https://t.co/rtcpy0gAwI and found yet another link
Threat actor linked to #Winnti and #EmissaryPanda/#LuckyMouse#APT groups targets gambling companies in South-East Asia with a new backdoor using Dropbox as C2. TTPs, post-exploitation tools and different malware families discussed in our report https://t.co/TWFyaGjoG9