AI Raises the Stakes for Cyber Resilience: An organization's ability to quickly recover from a business disruption will be a competitive advantage in an era of AI-driven threats and business enablement. www.darkreading.com/cyber-risk/ai-raises-stakes-cyber-resilience
eMudhra revokes 8 more CA certificates after private key mishap: Certificate authority eMudhra has revoked eight additional intermediate CA certificates after an… www.bleepingcomputer.com/news/security/emudhra-revokes-8-more-ca-certificates-after-private-key-mishap/ #Security
Notion says Fireworks breach exposed customer AI chat transcripts: Notion, the digital workspace platform, disclosed that a security… www.bleepingcomputer.com/news/security/notion-says-fireworks-breach-exposed-customer-ai-chat-transcripts/ #Security#ArtificialIntelligence
Attackers Say 'Hello' to a Different Scale of Cloud Attack: Researchers dubbed an attack chain "Greeter" after discovering that attackers deliberately covered their trail by leaving "hello" messages in logs. www.darkreading.com/cloud-security/attackers-hello-scale-cloud-attack
N-able Takes N-central Platform Offline After Discovery of 33 Flaws: The RMM provider also released a hotfix as one of recommended mitigations to address public exploits for the alleged zero-days that… www.darkreading.com/endpoint-security/n-able-n-central-offline-33-flaws
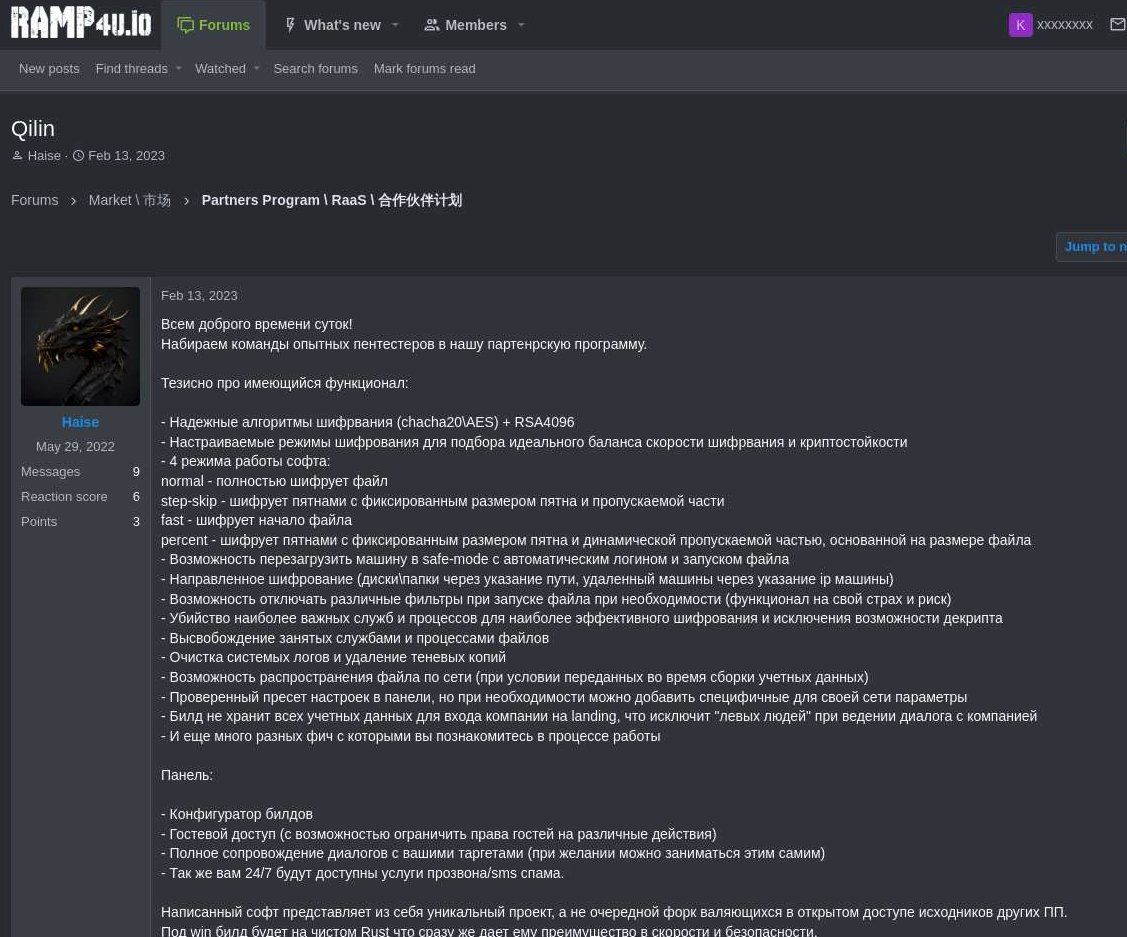
Who Runs the Ransomware Group Qilin?: The cybercrime group Qilin has emerged as the world's most active ransomware affiliate program, claiming at least 365 victim organizations in the past three months alone. But… krebsonsecurity.com/2026/11/who-runs-the-ransomware-group-qilin/
N-able Rushes Out N-central Fixes After 33 Zero-Days Go Public: N-able fixes seven N-central CVEs after 33 alleged zero-days are published www.infosecurity-magazine.com/news/n-able-n-central-able2shell-0day/ #cybersecurity#infosec#hacking
Critical Zoom Workplace Flaw Could Allow Unauthenticated Remote Privilege Escalation: Zoom has released software updates to address two security flaws impacting Zoom Workplace for Windows, including a critical… thehackernews.com/2026/11/critical-zoom-workplace-flaw-could.html
Anthropic's Glasswing Finds Many Vulnerabilities Yet Delivers Few Fixes, Researcher Says: VulnCheck’s Patrick Garrity has found that seven months on, Project Glasswing resulted in only… www.infosecurity-magazine.com/news/anthropic-glasswing/ #cybersecurity#infosec#hacking
Maersk confirms data breach as WhiteArmor ransomware demands $5 million: Maersk announced that a threat actor gained unauthorized access to a local legacy… www.bleepingcomputer.com/news/security/maersk-confirms-data-breach-as-whitearmor-ransomware-demands-5-million/ #Security
AntiFox AI Pentesting Platform Linked to Attacks That Accessed AWS Production Secrets: Cybersecurity researchers have disclosed details of a campaign in which an emerging agentic penetration testing platform… thehackernews.com/2026/11/antifox-ai-pentesting-platform-linked.html
Suspected Chinese Malware Supplier Tied to Three Hacking Campaigns: Check Point links three China-nexus clusters through a shared Sparrow malware framework www.infosecurity-magazine.com/news/chinese-malware-tied-three-hacking/ #cybersecurity#infosec#hacking
Thousands of schools in Italy, Scotland and Ireland receive bomb threats: Incidents appear to be latest co-ordinated attack aimed at disrupting life in Europe www.ft.com/content/7bbc0a5e-b7e2-4a3f-874f-a63de94e922d?syn-25a6b1a6=1
Hackers use AntiFox AI agents in AWS credential-theft attacks: Attackers are using Alibaba Cloud to host self-managed instances of AntiFox,… www.bleepingcomputer.com/news/security/hackers-use-antifox-ai-agents-in-aws-credential-theft-attacks/ #Security#ArtificialIntelligence
eBPF Rootkits: Why Underground Actors Are Taking Notice: Linux eBPF rootkits can hide malicious activity and evade traditional detection methods without loading kernel… www.bleepingcomputer.com/news/security/ebpf-rootkits-why-underground-actors-are-taking-notice/ #Security
Hackers Target Qlik Sense Servers With Reverse Shells, Stage ActiveMQ and Veeam Exploits: Threat actors have been observed targeting Qlik Sense servers to unsuccessfully deliver PowerShell reverse shell… thehackernews.com/2026/11/hackers-target-qlik-sense-servers-with.html
Over 35,000 Grok-Built Apps Exposed Online, Some Leaking Confidential Data and Passwords: Of the 37,571 Grok-built apps that security company Claroc found online, 35,578 were open to anyone without a sign-in,… thehackernews.com/2026/11/over-35000-grok-built-apps-exposed.html