Supply chain attacks, AI as a malware vector, MDM exploits, fintech trojans, and a massive education breach — all in 24 hours. Which of these is the most concerning? 👇 #CyberSecurity#InfoSec#ThreatIntel#AI#ZeroDay
🟠 5/5 Canvas breach. ShinyHunters claims data from 275M students and faculty across 9,000 institutions. Education is no longer a soft target — the data volume makes it prime real estate for extortion groups. (via @KrebsOnSecurity) https://t.co/MxjcmuUGBO
🟠 4/5 TCLBANKER targets 59 banking, fintech, and crypto platforms with worm capabilities spreading via WhatsApp and Outlook. A banking trojan that hijacks your corporate comms channels is a serious tactical evolution. (via @TheHackersNews) https://t.co/iOJD6lwmea
🔴 3/5 CISA gives federal agencies 4 days to patch an actively exploited Ivanti EPMM zero-day. The flaw grants unauthorized access to MDM platforms managing thousands of corporate devices. Patch now — no exceptions. (via @BleepingComputer) https://t.co/jI9AACQGqv
🔴 2/5 Fake OpenAI repo on Hugging Face hit trending while quietly pushing an infostealer to Windows users. Trusted AI platforms are the new malware distribution vector — verify every repo before you run it. (via @BleepingComputer) https://t.co/fdKUtK0pWF
🔴 1/5 JDownloader site compromised. The official website was hacked to replace legitimate installers with a Python RAT targeting both Windows and Linux. If you downloaded it this week, scan your system immediately. (via @BleepingComputer) https://t.co/1CBi8sTxUw
🟠 5/5 Canvas breach. ShinyHunters reclama 275M de estudiantes y docentes comprometidos en 9,000 instituciones. Educación ya no es un sector de bajo riesgo — el tamaño de la base de datos lo hace un blanco prioritario. (vía @KrebsOnSecurity) https://t.co/MxjcmuUGBO
🟠 4/5 TCLBANKER apunta a 59 plataformas bancarias, fintech y crypto con capacidades de gusano vía WhatsApp y Outlook. Un troyano que usa tus canales corporativos para propagarse es una señal de madurez táctica preocupante. (vía @TheHackersNews) https://t.co/iOJD6lwmea
🔴 3/5 CISA: 4 días para parchear zero-day activo en Ivanti EPMM. La falla permite acceso no autorizado a plataformas MDM con miles de dispositivos corporativos. Si lo usas, actúa antes de que venza el plazo. (vía @BleepingComputer) https://t.co/jI9AACQGqv
2/5 Repo falso de OpenAI en Hugging Face. Llegó a trending mientras distribuía un infostealer a usuarios de Windows. Las plataformas de IA de confianza son el nuevo vector de distribución de malware. (vía @BleepingComputer) https://t.co/fdKUtK0pWF
🔴 1/5 JDownloader hackeado. El sitio oficial fue comprometido para reemplazar instaladores legítimos con un Python RAT para Windows y Linux. Si lo descargaste esta semana, analiza tu sistema ya. (vía @BleepingComputer) https://t.co/1CBi8sTxUw
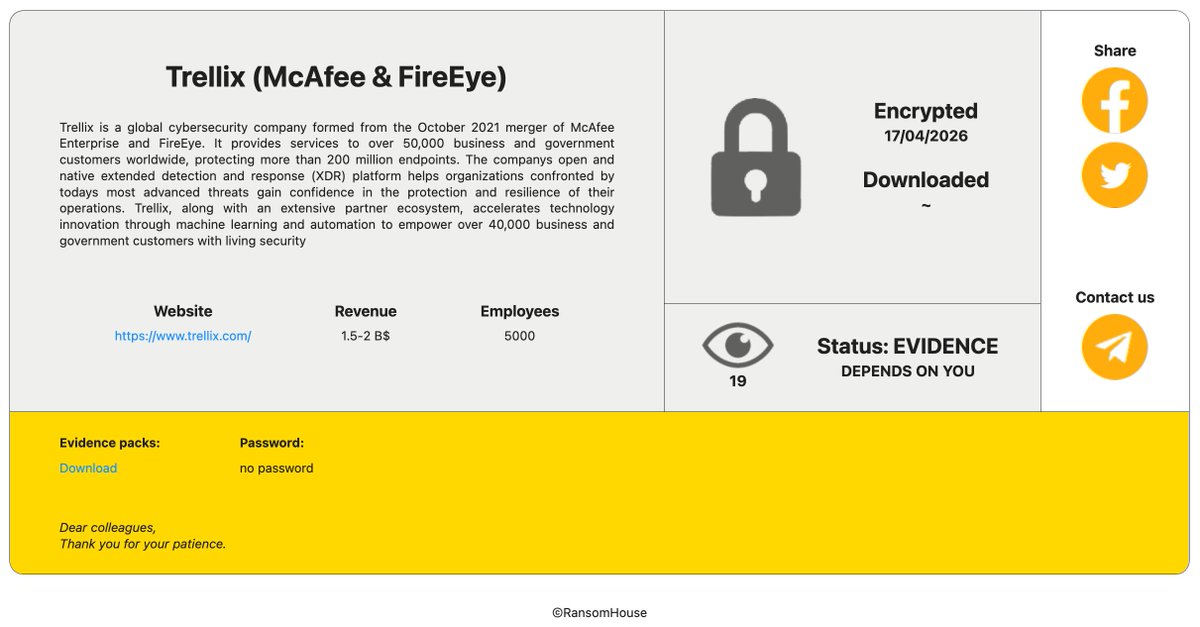
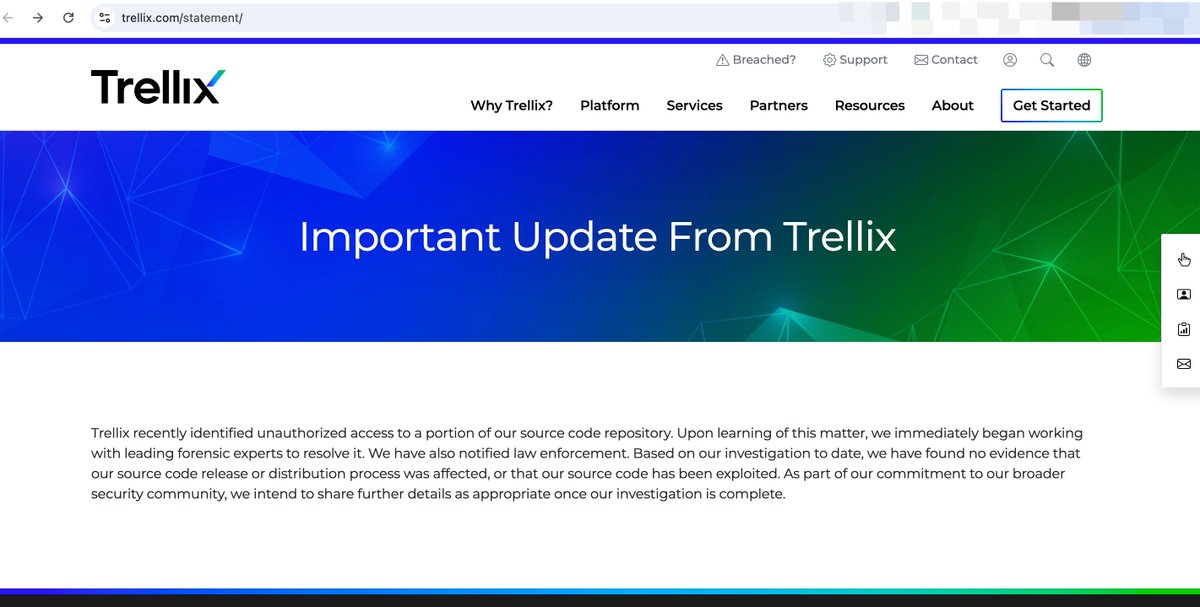
El grupo #hacker#RansomHouse ha publicado en su blog a #Trellix 🇺🇲 (@Trellix) como posible víctima de un #ciberataque#ransomware.
#Trellix 🇺🇲 es una empresa de #ciberseguridad especializada en #software y servicios para la detección y la respuesta a amenazas.
Monitorea este incidente en VenariX, Inc. ➡️ https://t.co/OW9Te2XdwS
#CyberAttack #CyberSecurity #Threats #DarkWeb #InfoSec #USA #McAfee #FireEye #CyberSec
🚨 CYBER THREAT INTELLIGENCE ALERT: SALE OF ACCESSES AND BACKDOORS ON MULTIPLE CHILEAN DOMAINS (.cl) 🇨🇱💻🚪🔓 [STATUS: ACTIVE THREAT]
Threat intelligence collection engines have detected malicious activity within the "Pharaoh's Team" Telegram channel. The threat actor has published a sales catalog exposing the compromise of over a dozen websites in Chile, ranging from civil infrastructure to educational institutions.
📍 Affected Country: Chile (.cl) and Chilean organizations (.org).
👤 Threat Actor: Pharaoh's Team
🛠️ Compromised Asset: Web access (presumably Web Shells, Backdoors, or CMS credentials).
📅 Report Date: May 7, 2026.
🏢 List of Compromised Domains and Sectors
The Pharaoh's Team catalog impacts various critical and commercial sectors:
Civil and Corporate Infrastructure:
https://t.co/C9rhGr61OS (Road infrastructure/concessionaire).
https://t.co/gVybyTlwUQ (Water management/dams).
Education and NGOs:
https://t.co/QeP2sJqjXY (School).
https://t.co/cEvH2QXVHV (Educational initiative).
https://t.co/Lf7R6vwV7h (Presumed NGO).
Commerce, Retail, and Entertainment:
https://t.co/C1ZIBJ01Ni, https://t.co/miemJ08okc, https://t.co/rnk6p1pZRv, https://t.co/eTe4xwGhJe, https://t.co/aDnOZF6Dvj, https://t.co/5rSIV6XrEF, https://t.co/lLBNxBFLyh, https://t.co/dqv76tiVfa, https://t.co/hszveaNxVN.
The presence of backdoors on portals such as https://t.co/C9rhGr61OS poses a serious risk to the supply chain. Cybercriminals can utilize these legitimate domains to send highly convincing spear-phishing emails to Chilean government entities, construction suppliers, or citizens, facilitating the deployment of ransomware under the guise of Official Communications
🛡️ Remediation Recommendations
🔒 Threat Hunting: IT administrators for the listed domains must immediately isolate their web servers and conduct a forensic scan to search for anomalous PHP/ASP files (Web Shells) hidden within public directories (e.g., /wp-content/uploads/).
🔑 Access Revocation: Enforce password resets for all CMS administrator accounts (e.g., WordPress, Joomla), FTP/SFTP accounts, and database access credentials.
Monitor: https://t.co/wk9bZJ2Nli
#CyberSecurity #Chile #WebShell #Backdoor #DataBreach #PharaohsTeam #ThreatIntelligence #VECERT #CyberAlert 🇨🇱🛡️⚠️🚨💻