🚨 Google Chrome Sandbox Breakout (CVE-2026-126872)
Flaw in FileSystem authorization lets remote attackers break out of the browser sandbox to execute arbitrary code on the host OS.
⚡ Action: Update Chrome to >= 157.0.8103.78 now.
https://t.co/L2f24FAskj
#Chrome#AppSec
🚨 Critical RCE in ManageEngine AssetExplorer & ServiceDesk (CVE-2026-12507, CVSS 9.1)
Reports module flaw allows authenticated users with report creation rights to execute OS commands on servers.
⚡ Action: Update immediately.
https://t.co/JvMaF1kPFO
#ManageEngine#AppSec
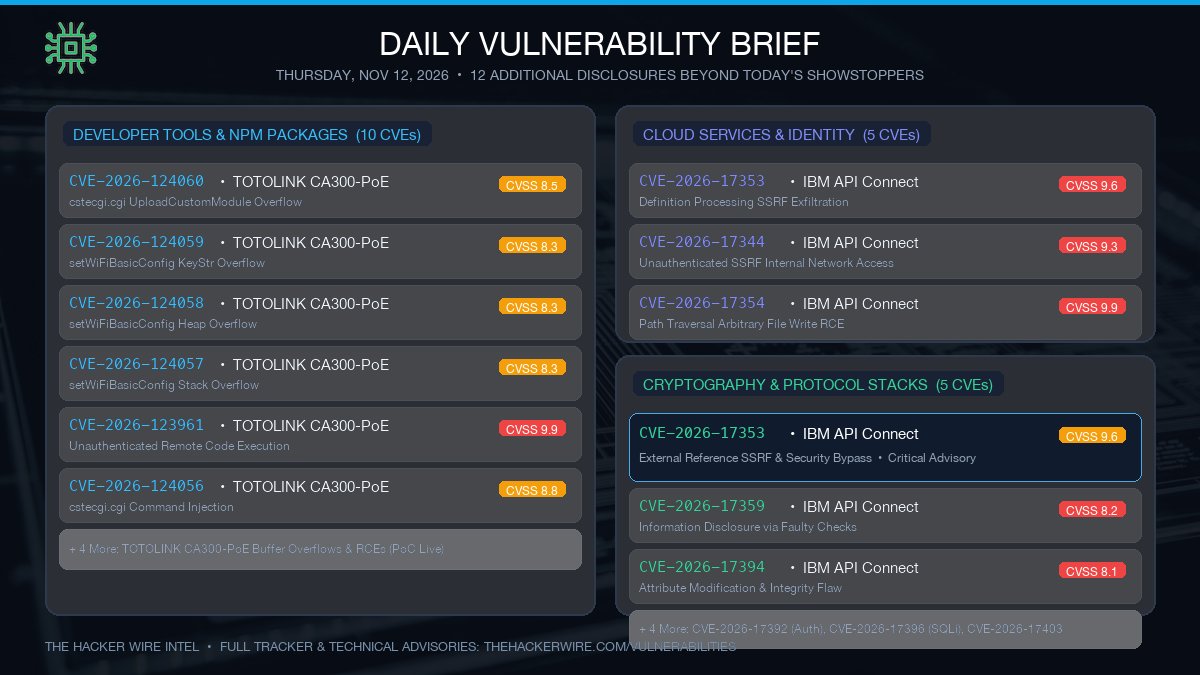
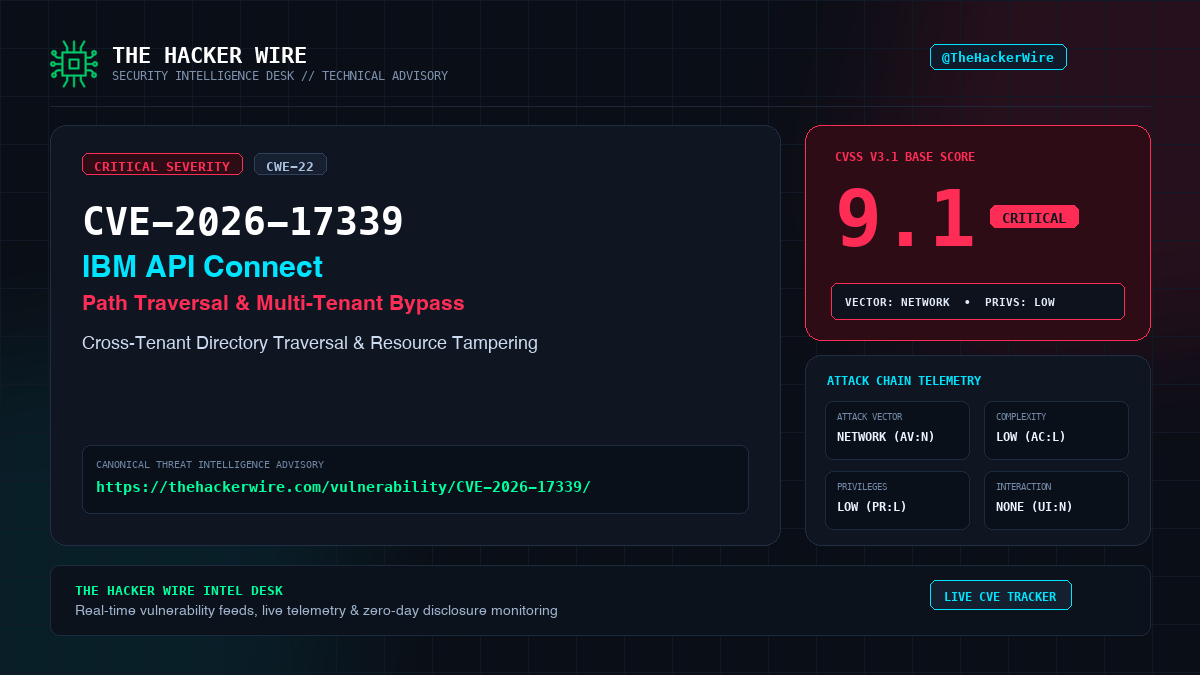
🚨 Multi-Tenant Isolation Bypass in IBM API Connect (CVE-2026-17339, CVSS 9.1)
Path traversal lets attackers cross tenant boundaries to access, overwrite, or delete restricted API contracts!
⚡ Action: Update to 12.1.1.3.
https://t.co/NM9HgcTAVI
#IBM#CloudSecurity
🚨 Critical Auth Flaw in Synology DSM (CVE-2026-76954, CVSS 9.8)
SQL injection in the Auth API allows unauthenticated attackers to read/write arbitrary files & hijack Synology NAS arrays.
⚡ Action: Update DSM via Control Panel.
https://t.co/0VZ8J714Ab
#Synology#NAS
🚨 Critical RCE in Apache HTTP Server (CVE-2026-119618)
Race condition in mod_http2 causes heap corruption & unauthenticated RCE on Apache 2.4.55–2.4.70. Flagged by Anthropic & Google.
⚡ Action: Update to 2.4.71 or disable mod_http2.
https://t.co/hXLPAoFyRa
#Apache#AppSec
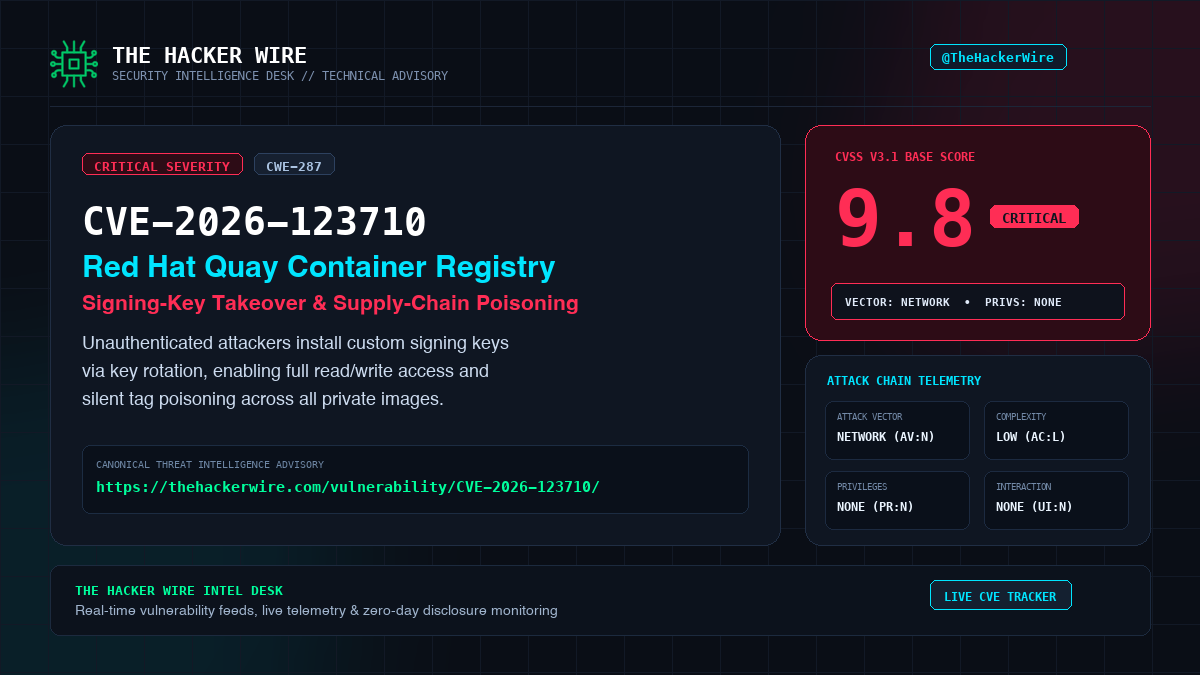
🚨 Supply-Chain Flaw in Red Hat Quay (CVE-2026-123710, CVSS 9.8)
Unauthenticated attackers can install arbitrary signing keys, gaining full read/write & tag poisoning across private container images.
⚡ Action: Update Quay now.
https://t.co/UpUGZ7oDs5
#DevSecOps#AppSec
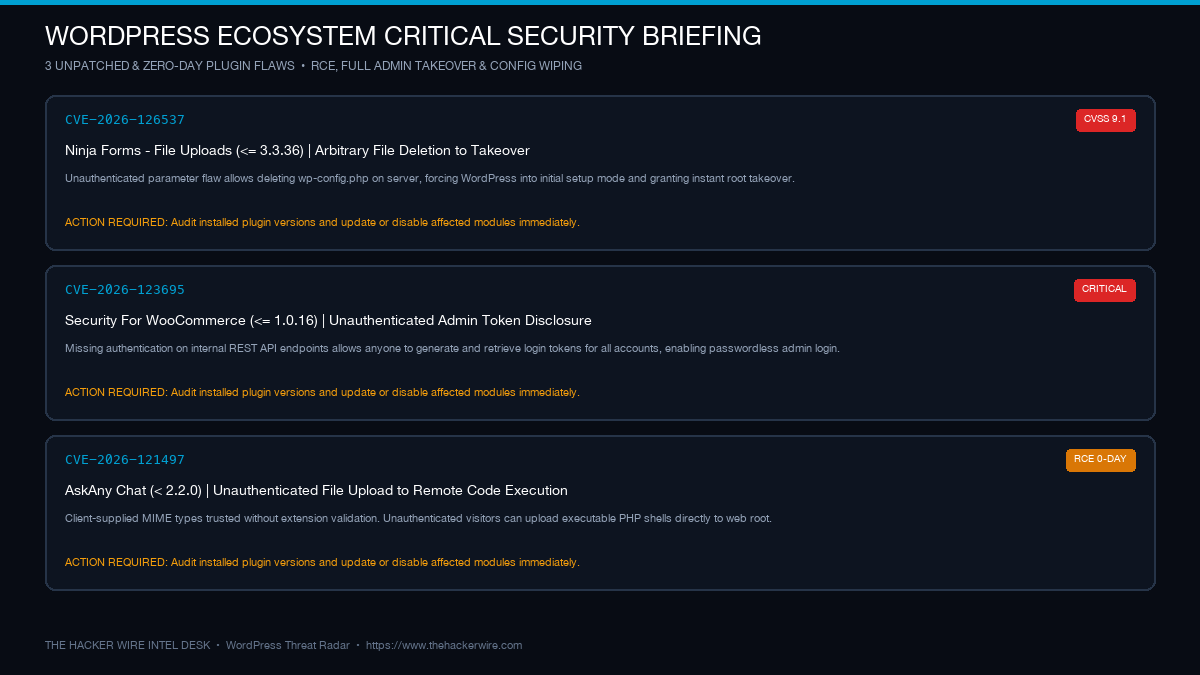
🚨 File Deletion to Site Takeover in Tournamatch (CVE-2026-121379, CVSS 8.8)
Subscriber+ users can delete wp-config.php during avatar reset to trigger re-install and seize the site!
⚡ Action: Update to >= 4.7.1.
https://t.co/CU5R3mJ3V1
#WordPress#BugBounty