From 11 September 2026, manufacturers selling digital products in the EU have 24 hours to report actively exploited vulnerabilities. ⏱️ Andreas Brombach explains what is reportable, and how to actually make those deadlines: https://t.co/uCBc0LifGT
#CRA#ProductSecurity
Pentesting passkeys? Security analyst @emanuelduss shows two JS snippets for tampering with the WebAuthn APIs. Handy for checking if you can login using a security key without knowing the PIN.
Check out the technical details and how he got there: https://t.co/yxTY6WaI5M
Pipeleek 1.0 is out 💧 Secret scanning across 7 CI/CD platforms, plus runner and Renovate bot exploitation.
Want to see one leaked job log turn into repo takeover? Try our deliberately vulnerable GitLab Attack Lab. Happy leeking!
https://t.co/dvyVsT1biO
#DevSecOps#CICD
Your team evaluated that automation platform as a productivity tool. Attackers see a jump host with SSH access, stored credentials, and a path around your network segmentation.
Read our latest blog post before deploying any automation platform: https://t.co/UDMxc3iie8
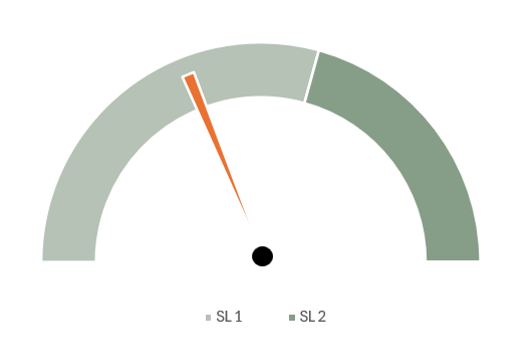
How do you translate the Cyber Resilience Act into technical testing? Part II of our #CRA series follows a cheap IP camera, from STRIDE threat modelling and firmware analysis to compliance with IEC 62443-4-2.
https://t.co/ezuDPCS1hm
#CyberSecurity#CyberResilienceAct#IEC62443
How do you prepare a product for the Cyber Resilience Act? Our latest article covers #CRA scope, product classification, threat modelling, technical security testing, and why we use IEC 62443 as an assessment framework. Part I of a two part series: https://t.co/u4aKX7MagQ
AI agents in your Entra ID tenant? They come with new identities, permissions, fresh attack paths.
Chrigi @ZH938472 breaks down Entra Agent ID security, their capabilities, control paths, abuse scenarios, and how to review your exposure with EntraFalcon.
https://t.co/vtR3Wat3gc
The monkey is still curious 🐒 Teleboy has topped up its bug bounty program with another CHF 10'000 in rewards. Explore a platform serving 400'000+ users across TV, internet, and telephony. Ready for another hunt? #bugbounty#ethicalhacking#cybersecurity
https://t.co/oXuB0Xld85
🦖 Meet RAPTR: our new open source platform for red and purple team collaboration. Plan engagements, document attacks and detections, evaluate results, and generate reports, all API-driven. Beta is live, feedback welcome! #PurpleTeam
https://t.co/GyXw40nN2p
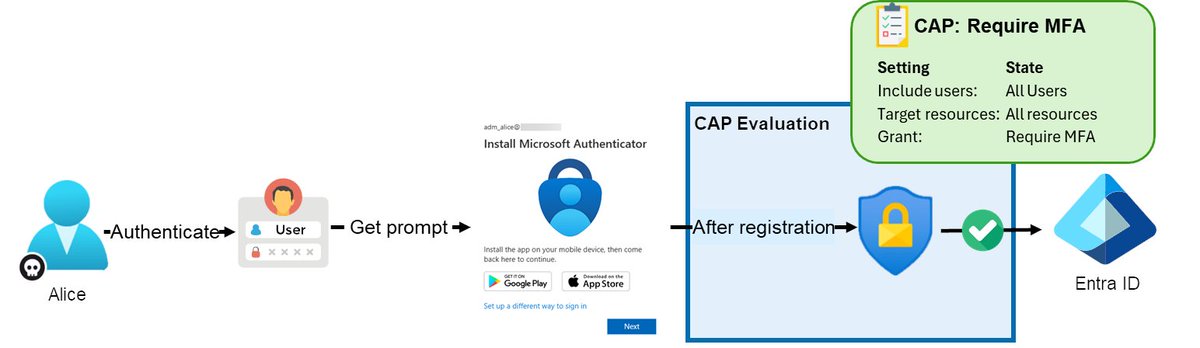
The final part of our Entra ID blog series looks at common Conditional Access weaknesses, practical attack scenarios, and how to identify such issues with EntraFalcon.
https://t.co/vx43hX6mDj
🏃♂️Time for a security workout. Sanitas is launching its #bugbounty program and inviting ethical hackers to help keep its digital healthcare services in peak condition.
Hunt vulnerabilities and help protect critical healthcare systems: https://t.co/6qUcSQJd9J
Foreign enterprise apps can expose your Entra ID tenant. Today, we release part 1 of our 4-part weekly series on common Entra ID pitfalls and how to detect them with EntraFalcon. Learn how external apps can lead to data access or worse: https://t.co/kwMWrC4tKA
Unprotected groups in Entra ID can lead to privilege escalation.
Part 2 of our 4-part series shows how weakly protected groups can be abused to bypass controls, gain privileged access, and lead to full compromise—and how to detect this with EntraFalcon: https://t.co/gnAgcDzoEQ
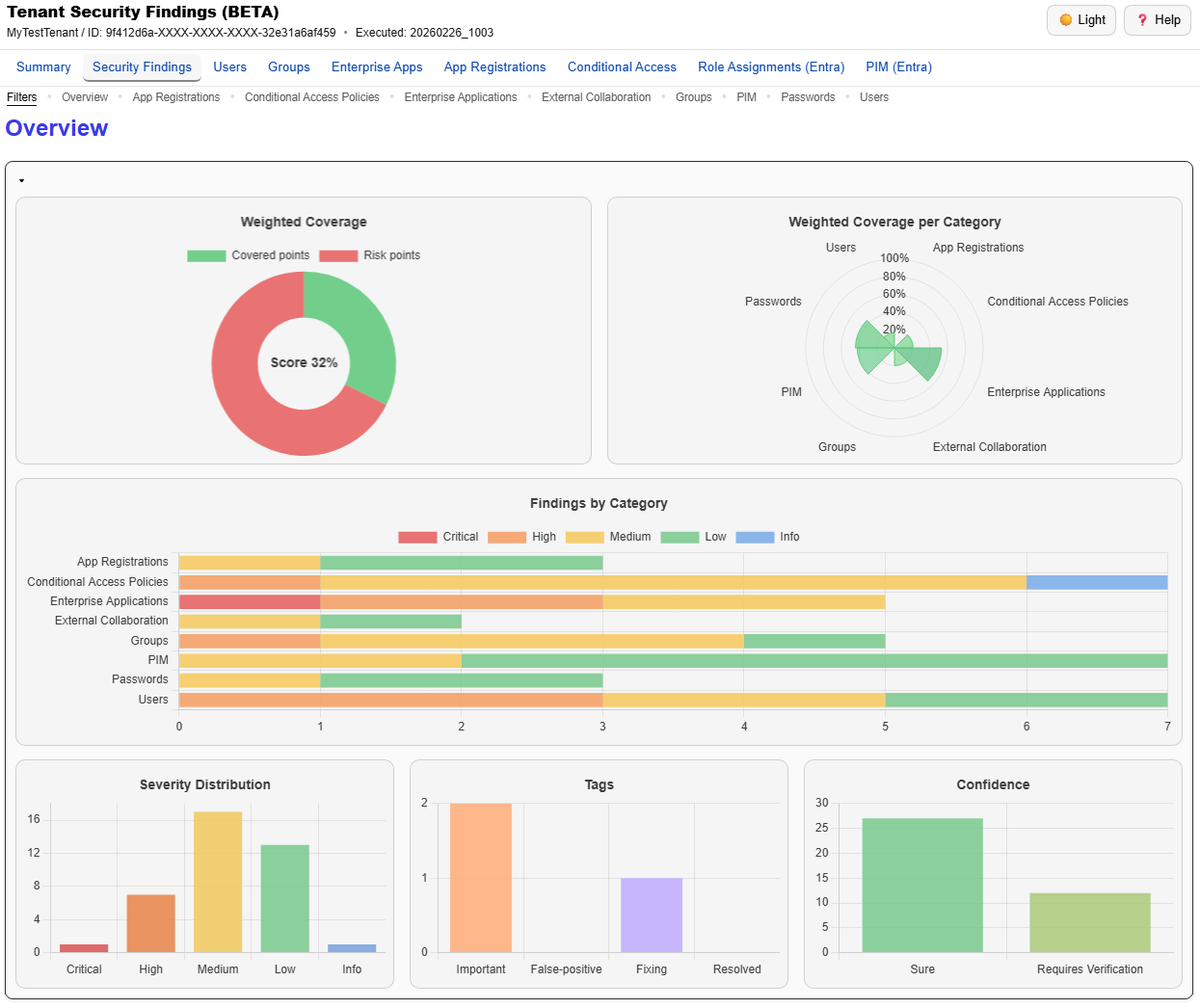
EntraFalcon update 🚀 The new Security Findings Report turns Entra ID enumeration into actionable findings with 60+ checks and color charts. Read the blog post of Chrigi @ZH938472 and try the tool now on your tenant! https://t.co/07gzDox92b
#EntraID#CloudSecurity#EntraFalcon
WinGet can be more than a package manager. We show how .winget configs + a self-referencing LNK become a viable initial access payload when Microsoft Store is enabled. Includes detection queries & mitigation tips.
https://t.co/1MLtOjzfaU
#RedTeam#Windows#LOLBins#InitialAccess
John Ostrowski (Compass Security) and Manuel Kiesel (Cyllective AG) worked together on CVE-2025-13154, a Lenovo Vantage LPE. Even after Microsoft closed a known primitive, collaboration led to a working PoC.
https://t.co/vunXyr408d
#Windows#CVE#SecurityResearch#PrivEsc
In a new video, Nicolò Fornari walks through how to fuzz with AFL++, how to pick targets, avoid common pitfalls, and boost effectiveness. Find performance tips, fuzzing theory, and AFL++ internals. https://t.co/S21LcYIUJZ
#security#fuzzing#AFLplusplus#appsec
NTLM relay works against HTTPS if channel binding is missing. Our new blog post explains why, shows how tooling evolved, and highlights defensive measures.
https://t.co/gXcsZZ01oP
Learn about a FortiProxy Domain Fronting Protection bypass discovered by our analyst @emanuelduss . Details in the advisory: https://t.co/aO2913oKxj
Curious how web filters are evaded? Read his blog series: https://t.co/4DcLNl7BBq
#cve#pentest#bypass
The leaked LockBit chats give a rare inside look at ransomware ops.
Read our blog for an analysis and lessons for defenders: https://t.co/5BmoOSvfyn
#CyberSecurity#Ransomware#LockBit