Fawzy Alkhawaja, Palestinese, mostra come un tempo gli arabi poveri estraevano l'olio da consumare a casa, senza ricorrere al frantoio (gli arabi migliorarono notevolmente l'intera filiera rispetto ai romani)→
In Italia c’è un’azienda in grado di sviluppare il Sacro Graal delle cyber armi: codici informatici che sfruttano le vulnerabilità di computer e smartphone per spiare un bersaglio. Questa azienda si chiama Dataflow Security.
Inchiesta firmata da @RositaRijtano per @IrpiMedia
🔗 https://t.co/3kYUIovJLV
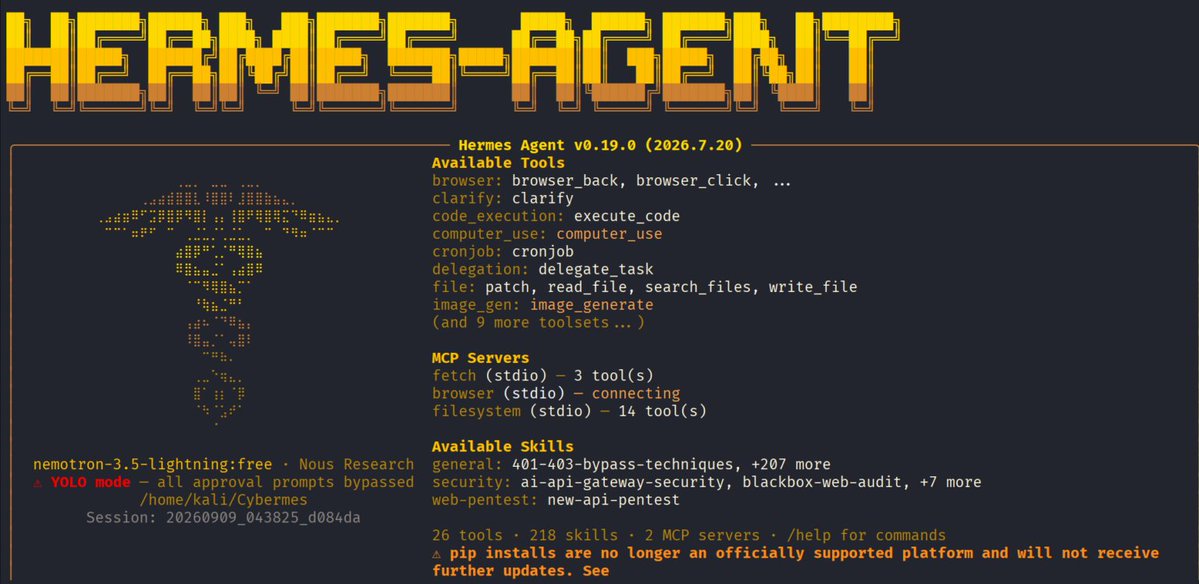
Cybermes - Web Pentest and Bug Bounty
In a recent article we covered the use of Cybermes. It's an interesting framework that can be used for pentests and web app hacking. It can generate good reports, which I think is an advantage.
Cybermes comes with built in skills, which are good enough to work with
https://t.co/YCe0rAwubi
Off-grid messages, file, and photos with VaraAC and an HF radio. No internet and no infrastructure. This is available to everyone if you want it bad enough.
🚨🚨 La CIA admite oficialmente que el cáncer es biológicamente idéntico a los parásitos…
La Universidad Johns Hopkins ha ocultado medicamentos antiparasitarios baratos que curan el cáncer en semanas...
Saudi Arabia already recorded a budget deficit of 125.7 billion riyals, roughly $33.5 billion, in the first quarter of 2026 alone.
That was nearly as large as the $44 billion deficit the government had projected for the entire year. Spending increased 20% while oil revenue declined 3%. Riyadh approved financing needs of roughly 217 billion riyals, or nearly $58 billion, for 2026, including money required to finance the deficit and refinance maturing debt.
Now imagine what happens when the volume of oil available to sell suddenly collapses to levels not seen since the Gulf War.
All these hacks of sensitive personal information are designed to highlight the vulnerability of the current system...
It's a big problem but don't worry they already have a solution...
Digital IDs will happen like it or not for national security reasons...
AI/crypto need DIDs
⚠️ ALERT: Revolut falls for a FAKE government request, exposing sensitive personal information of customers in a disturbing data breach.
Revolut disclosed that it complied with a fraudulent government request using a spoofed official email and valid credentials, exposing PII belonging to a group of customers.
The leaked data reportedly includes passports/driving licences, verification selfies, names, DOBs, occupations, home addresses, emails, phone numbers, IBANs, account statements and full transaction histories, including Bitcoin activity.
No customer funds were reportedly lost and Revolut says its systems were not hacked.
The company has notified affected users and regulators and blocked the source.
Social-engineering attacks are on the rise, with attackers increasingly exploiting human trust and weak verification processes rather than technical vulnerabilities.
Umberto Eco, qui possédait 50 000 livres, disait ceci à propos des bibliothèques personnelles :
"Il est insensé de penser qu'il faut lire tous les livres qu'on achète, tout comme il est insensé de critiquer ceux qui achètent plus de livres qu'ils ne pourront jamais en lire. Ce serait comme dire qu'il faut utiliser tous les couverts ou les lunettes, les tournevis ou les forets que vous avez achetés avant d'en acheter de nouveaux.
Il y a des choses dans la vie pour lesquelles nous avons besoin de toujours avoir suffisamment de provisions, même si nous n'en utilisons qu'une petite partie.
Si, par exemple, nous considérons les livres comme des médicaments, nous comprenons qu'il est bon d'en avoir plusieurs à la maison plutôt que quelques-uns : quand on veut se sentir mieux, alors on va au « placard à pharmacie » et on choisit un livre. un livre aléatoire, mais le bon livre pour le moment. C'est pourquoi vous devriez toujours avoir un choix nutritionnel !
Ceux qui n'achètent qu'un seul livre, ne lisent que celui-là et s'en débarrassent ensuite. Ils appliquent simplement la mentalité de consommateur aux livres, c'est-à-dire qu'ils les considèrent comme un produit de consommation, un bien. Ceux qui aiment les livres savent qu'un livre est tout sauf une marchandise."
Emma Bonino
Di Andrea Zhok
ha promosso il referendum per l’abolizione dell’art. 18 dello Statuto dei Lavoratori (perché irrigidiva il mercato del lavoro).
Ha promosso referendum per la piena liberalizzazione del collocamento privato abolendo ogni vincolo e responsabilità del datore di lavoro.
Ha sostenuto la piena libertà di contratto individuale (quali che siano i rapporti di potere contrattuale) e l’abolizione dei contratti collettivi.
Ha sostenuto l’abolizione dell’obbligo di stipulare assicurazioni contro gli infortuni sul lavoro con l’INAIL aprendo alle assicurazioni private.
Ha sostenuto l’abolizione del Servizio Sanitario Nazionale, da sostituire con assicurazioni private.
Ha sostenuto costantemente l’innalzamento dell’età minima per accedere alla pensione.
Lei, la libertaria, era favorevolissima al Green Pass, che riteneva essere un grande contributo civile.
Si è sempre definita un'amica sincera di Israele e ha sostenuto tutte le iniziative del sionismo.
Ha supportato dal primo minuto e fino alla fine l’invio di aiuti militari a Kiev e la necessità di dare una lezione alla Russia.
È sempre stata ferocemente atlantista e filoamericana.
Non si può dire che non sia stata una vita coronata di successi, magari indiretti.
In vista dei coccodrilli che pioveranno in questi giorni, credo sia corretto dire che Emma Bonino, dal punto di vista della gente che vive del proprio lavoro e che ama l’Italia, è stata politicamente il Male.
Niente di personale, se la vedrà lei dall’altra parte.
Ma per quanto riguarda questa valle di lacrime, se avesse fatto la cassiera invece della parlamentare l'intero paese ne avrebbe tratto beneficio.
THIS IS F**CKING DANGEROUS
7 AI cybersecurity tools every builder should know before shipping their next product.
→ PentestGPT — autonomous pentesting
→ BurpGPT — AI-powered Burp Suite analysis
→ Security Copilot — blue-team investigation
→ Snyk DeepCode AI — code scanning + autofix
→ HexStrike AI — 150+ security tools + AI agents
→ Garak — LLM vulnerability testing
→ Lakera Guard — prompt injection + jailbreak protection
The interesting part?
AI is now showing up across the entire security stack.
-Offensive security.
-Defensive security.
-Code security.
-LLM red teaming.
-Runtime protection.
Some are fully open source and self hostable, while others are commercial platforms.
If you’re building AI systems, cybersecurity is becoming impossible to ignore.
BOOKMARK this before someone take it down
LINKS BELOW