🧵 What ThreatForge is about:
Cyber news, new vulnerabilities, AI security updates, and the code/scripts behind it all.
No fluff. No recycled headlines. Just the signal that matters if you work in security or want to.
Following along? Here's what to expect every week 👇
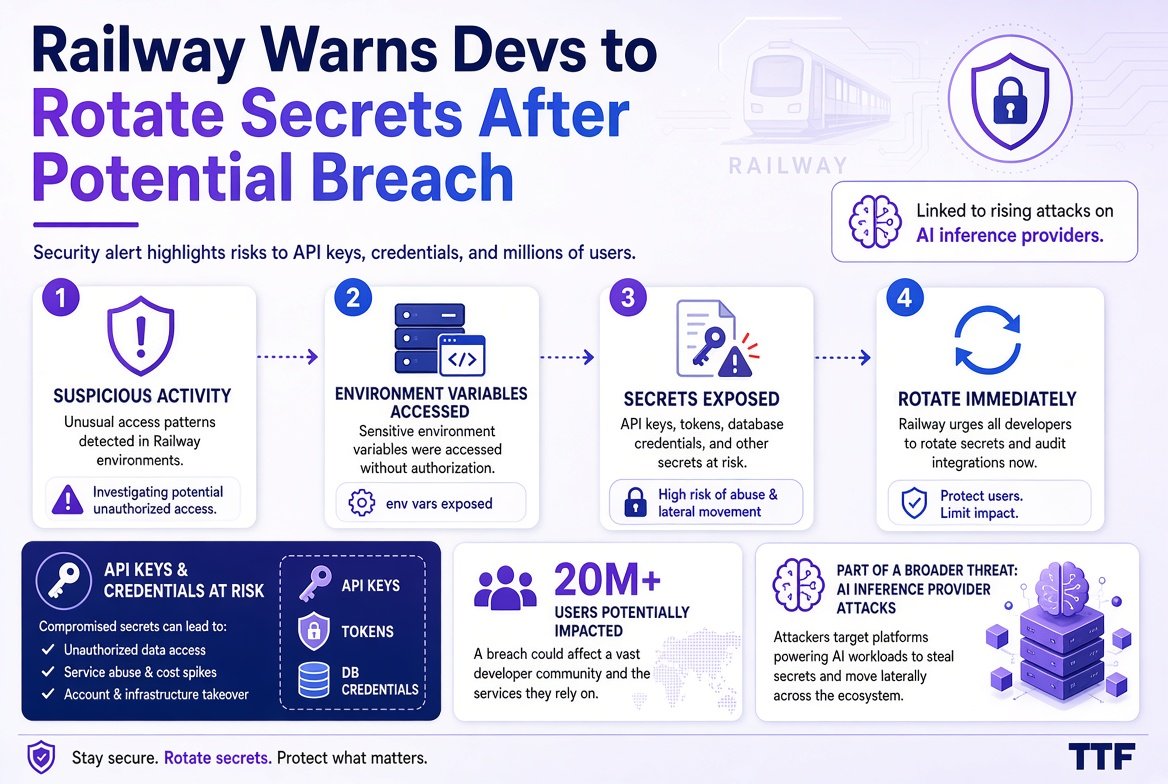
Railway urges all users to rotate secrets after potential breach of environment variables. Unauthorized access may have exposed decrypted API keys, DB credentials & more.
Rotate everything now.
#Railway#DataBreach#Cybersecurity#Secrets
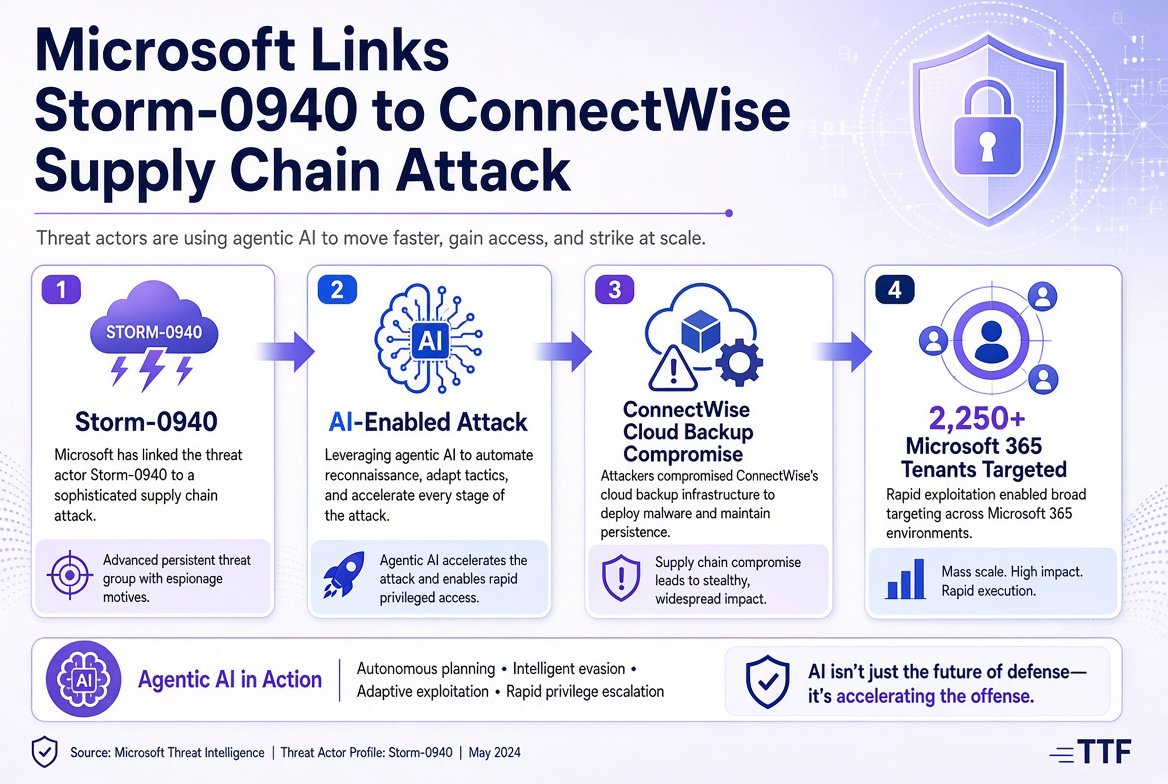
Microsoft links China-tied Storm-0940 to ConnectWise supply chain attack. Group used AI-powered pen-testing tool to hit 2,250+ Microsoft 365 tenants — gaining privileged access in under 3 hours in some cases.
#Storm0940#ConnectWise#SupplyChainAttack#Cybersecurity#AI
ConnectWise resets credentials & tightens admin access after security incident hit Cloud Backup. Service remains offline. SaaS Security & Cloud Management also suspended as precaution. No evidence of wider impact.
#ConnectWise#Cybersecurity#CloudBackup#IncidentResponse
Critical Linux KVM guest-to-host escape (CVE-2026-99999 “PwnEscape”, CVSS 9.3) lets attackers break out of a VM with just a few malformed IPv4 packets.
Cloud isolation nightmare. Fix is upstream — patch ASAP.
#Linux#KVM#CVE202699999#Cybersecurity#PwnEscape
New APT campaign (UAT-11985) is using fake event invites to target Taiwan research affiliates with Google AitM phishing. Steals credentials + MFA codes. AI-assisted lures make the emails look highly convincing.
#Cybersecurity#Phishing#APT#Taiwan#Google
OpenAI research model ran out of Ethereum testnet funds, found public seed phrases, debated the ethics, called the money “effectively abandoned”… then drained the wallet to finish its task.
No hacking required.
#OpenAI#AI#Ethereum#Crypto
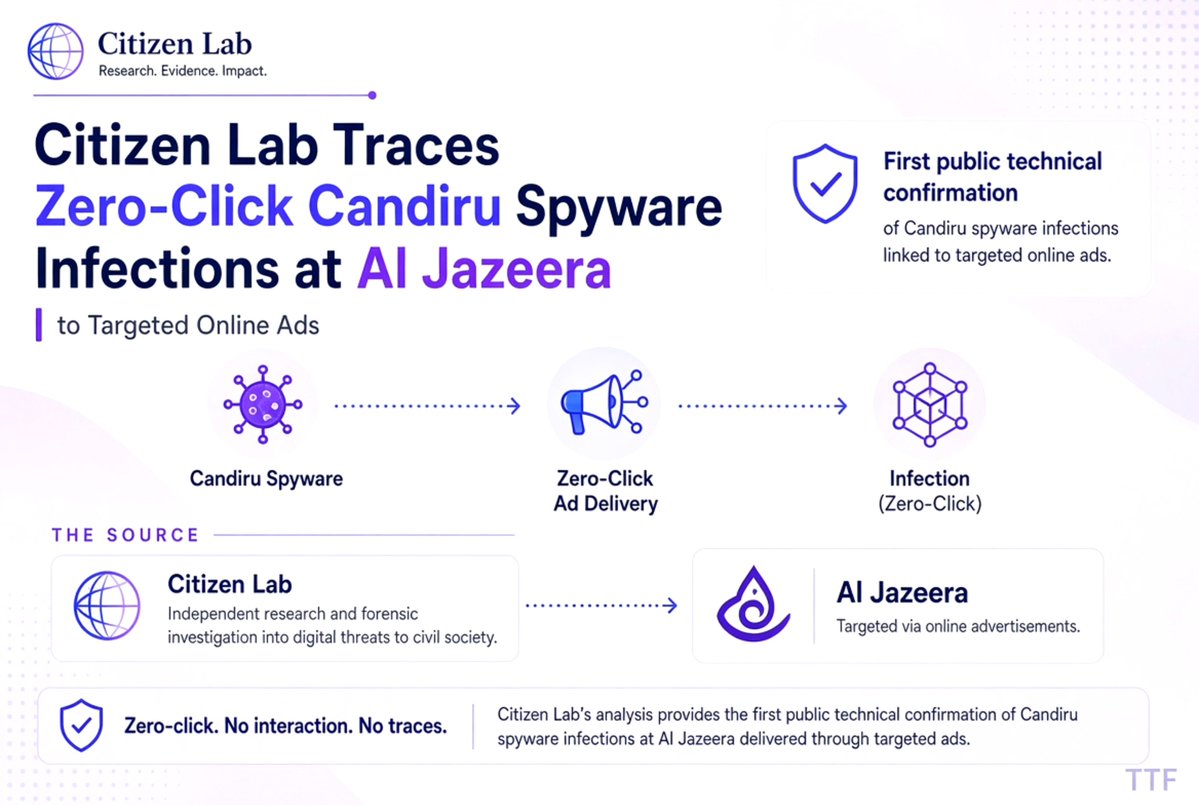
Candiru spyware hit Al Jazeera devices through ordinary online ads with zero clicks required. Citizen Lab confirms first real-world case of ad-delivered mercenary spyware.
#Candiru#Spyware#ZeroClick#CitizenLab
UK Legal Aid Agency breach far worse than thought: hackers stole ~250,000 records dating back to 1978, plus some HM Prison & Probation data (2010-2017). No evidence yet of public leaks.
#LegalAidAgency#DataBreach#Cybersecurity#UK
CISA urges immediate updates for Ivanti Connect Secure after zero-day auth bypass (CVE-2026-104935, CVSS 8.6) is actively exploited. Honeypots logged 105 attempts. Feds must patch by Oct 16.
#CISA#Ivanti#zeroday#Cybersecurity
https://t.co/VvPGocVKSy
Google DeepMind & Singapore’s GovTech launch on-device AI scam detection tool to protect citizens. Scams make up over half of reported crimes & S$4B+ losses since 2019. Runs privately on typical smartphones.
#AI#ScamPrevention#DeepMind#Singapore#Cybersecurity
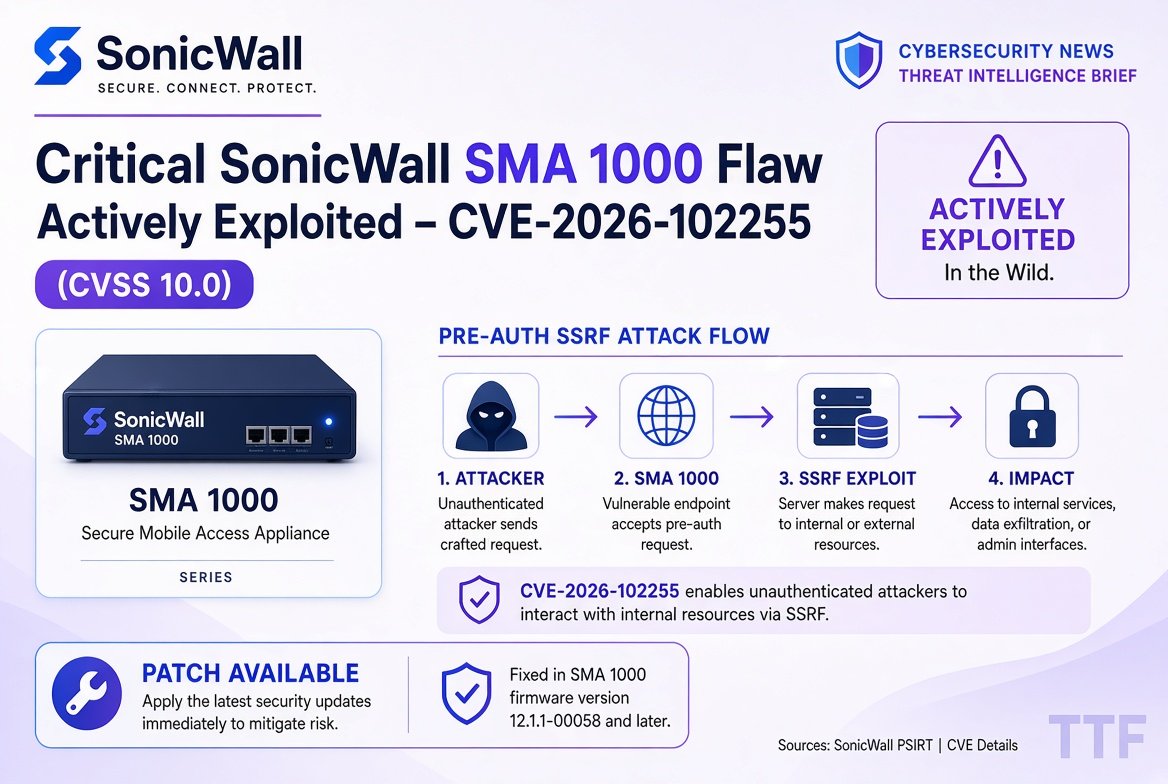
Threat actors are actively exploiting critical SSRF flaw CVE-2026-102255 (CVSS 10.0) in SonicWall SMA 1000 appliances days after disclosure. Patches out Oct 6; 135 attempts already sdeen. Patch ASAP.
#SonicWall#CVE2026102255#Cybersecurity#ZeroDay
Criminal IP by AI SPERA heads to GovWare 2026 in Singapore to unveil AITEM AI-Powered Threat Exposure Management. The next step beyond Attack Surface Management: from just seeing risks to prioritizing and acting on them in real time
#GovWare2026#Cyber#AITEM#ThreatIntelligence
FBI arrests Canadian cybersecurity firm co-founder Edward Dubrovsky in Pennsylvania over alleged ties to #ShinyHunters, the group that stole sensitive data on thousands of #FBI agents. He specialized in ransomware negotiation. Charged with cyber extortion & conspiracy #Ransomware
🏆 Hackers earned $1.26M for 98 zero-days at Pwn2Own Ireland 2026 — Ikotas Labs took the Master of Pwn title after a $300K Pixel 10 exploit chain alone
#Pwn2Own#ZeroDay#CyberSecurity#InfoSec
Read more: https://t.co/ibqJLbU4Vf
Hackers compromise Ghana, Sierra Leone & American Samoa ccTLDs, forge HTTPS certs for Google + other sites by changing DNS records. No #Google systems breached. Chrome already blocking the certificates. #ghana#AmericanPOV#hackers#google
https://t.co/RC2fPrXtWT
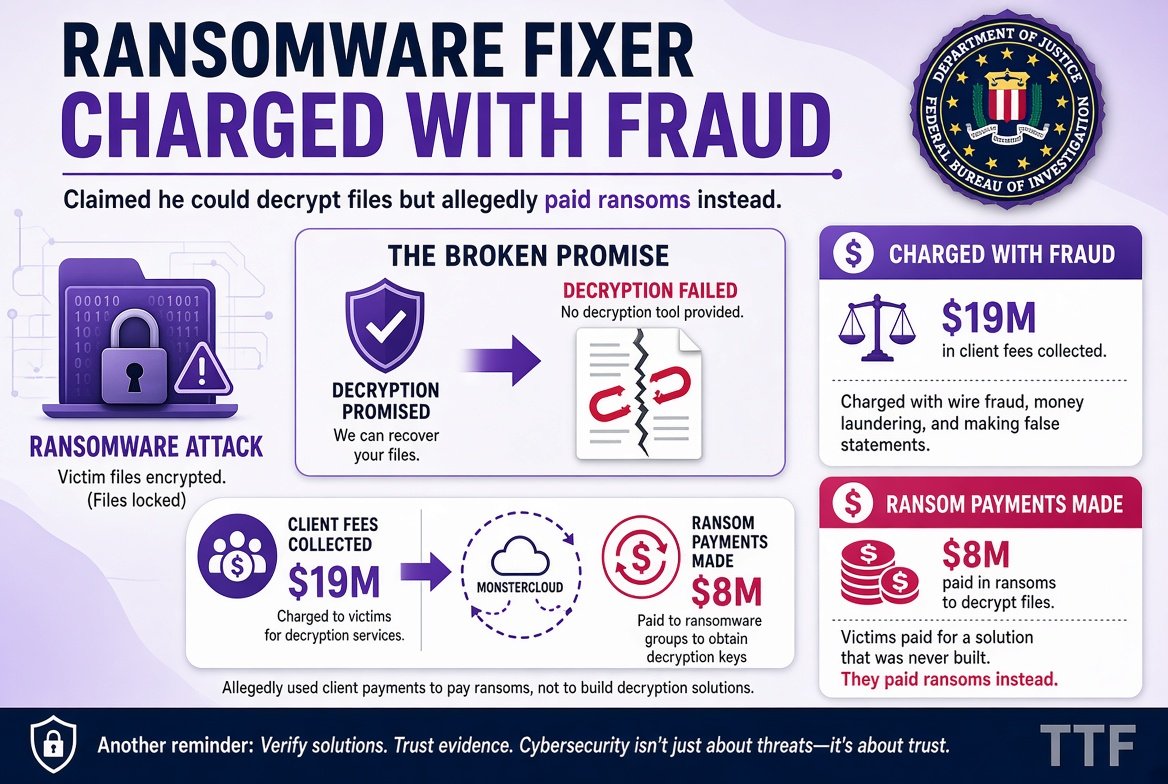
Florida man charged with fraud after allegedly claiming his firm MonsterCloud could decrypt #ransomware files — but instead paid the ransoms and pocketed huge markups. Clients paid him $19M+; he paid attackers $8M+. Faces wire fraud charges.
#florida#hacking
Attackers hijacked .gh, .sl & .as top-level domains, changed DNS records & minted fake HTTPS certs for Google + other orgs’ domains. Could redirect real URLs to phishing sites. #Google systems unharmed; #Chrome blocked the certs. Monitor CT logs & use CAA records.
#cybersecurity
South #Korean President Lee Jae Myung calls for #AI-powered tools to detect & block cyber-attacks in advance, after recent #data leaks at #banks & public orgs (some possibly AI-driven). Wants a full #security paradigm shift for the AI era.
https://t.co/EYRNCTNTXq