Kaspersky researchers uncovered BlackX, a UEFI bootkit exploiting the Baton Drop vulnerability (CVE-2022-21894) to bypass Windows Secure Boot.
Fully patched systems can remain exposed when Microsoft’s additional certificate-revocation protections have not been applied. https://t.co/TP9WqRxTTt
Microsoft has confirmed a Windows 11 regression affecting Universal Print printers originally installed on Windows 10.
Systems running KB5083769 or later may encounter configuration errors that disable printing, while upgrading to Windows 11 26H2 does not resolve the issue. https://t.co/kxTQxksnzW
Denmark’s Ministry of Digitalisation has ended a pilot testing Collabora as an open-source alternative to Microsoft Office.
The trial involving 38 employees reportedly encountered document-formatting problems, blank pages and issues with tracked changes.
The project will not resume, and no formal comparative evaluation was completed.
https://t.co/0TUtNmdJ7o
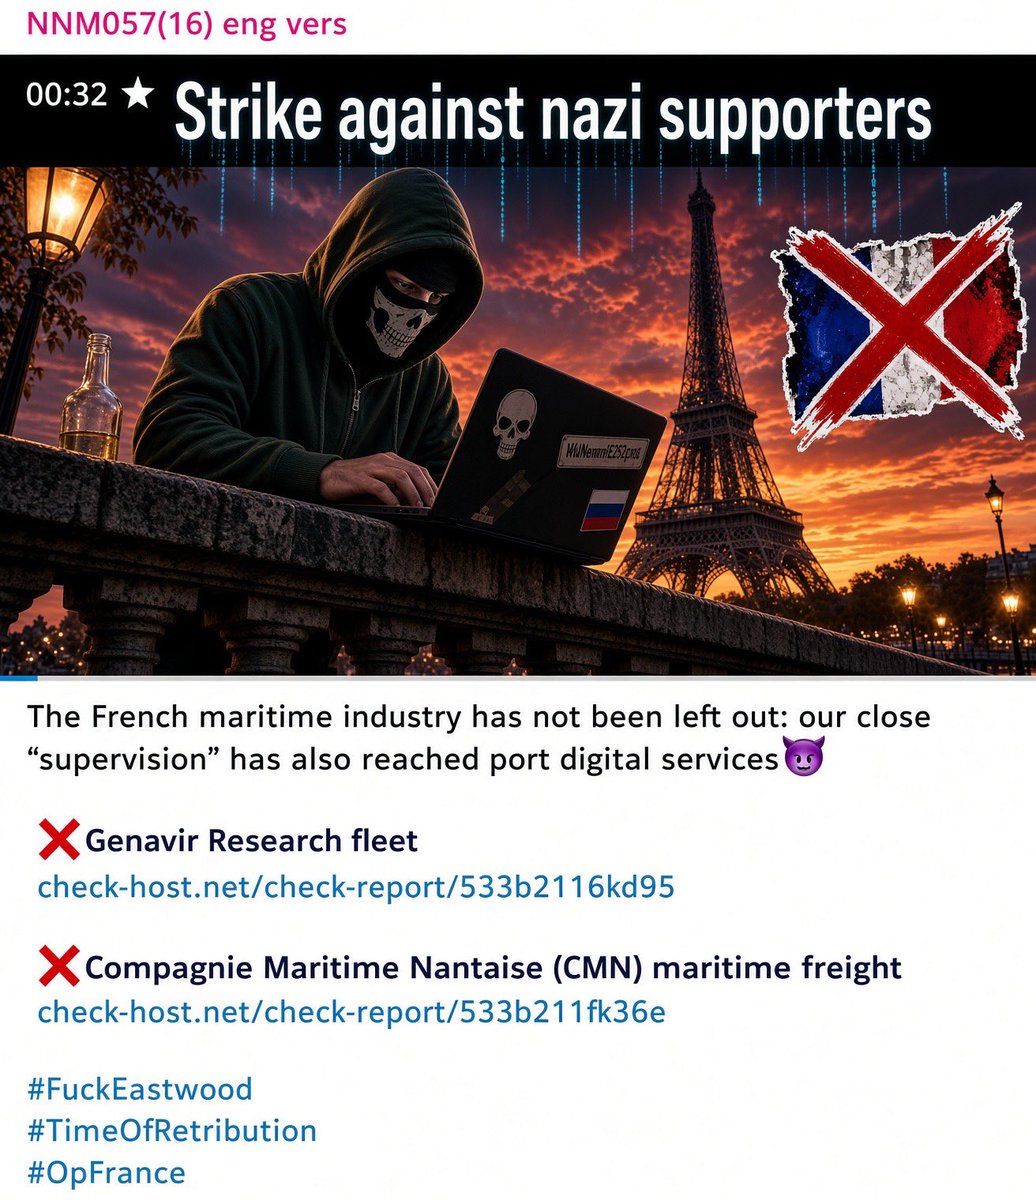
French Maritime Organizations Targeted in Alleged Cyberattacks
A threat actor associated with the #OpFrance campaign claims to have targeted French maritime organizations, including research-fleet operator Genavir and Compagnie Maritime Nantaise (CMN). Check-Host reports were shared as purported evidence of service disruption affecting their online infrastructure.
Country: France
Sector: Maritime / Transportation
Targets: Genavir / Compagnie Maritime Nantaise
Campaign: OpFrance
Attack Type: Alleged DDoS
Status: Unverified Claim
#CyberSecurity #DDoS #France #Maritime #OpFrance #ThreatIntel
Phishing Alert #35
Url: hxxps://ipko-pl.1wp.site/yh/pl/index.php
Country: Poland
Organization: PKO Bank Polski S.A.
Industry: Banking / Financial Services
Main services: Retail and business banking, iPKO internet banking, IKO mobile banking, bank accounts, domestic and international transfers, payment cards, loans and mortgages, savings and deposits, investments, currency exchange, insurance, online government services and other digital financial services.
French https://t.co/lC3LKDf0G6 User Database Allegedly Breached
Threat actor Opek0xx claims to have compromised https://t.co/lC3LKDf0G6 and extracted 99 user records. The allegedly exposed information includes names, contact and location data, employment profiles, availability schedules, work experience, transportation preferences and CV-related information.
Organization: https://t.co/lC3LKDf0G6
Country: France
Sector: Employment / Cleaning Services
Threat Actor: Opek0xx
Incident: Alleged Database Breach
Status: Unverified Claim
Source: PwnForums
#CyberSecurity #DataBreach #France #DataLeak #Privacy #ThreatIntel
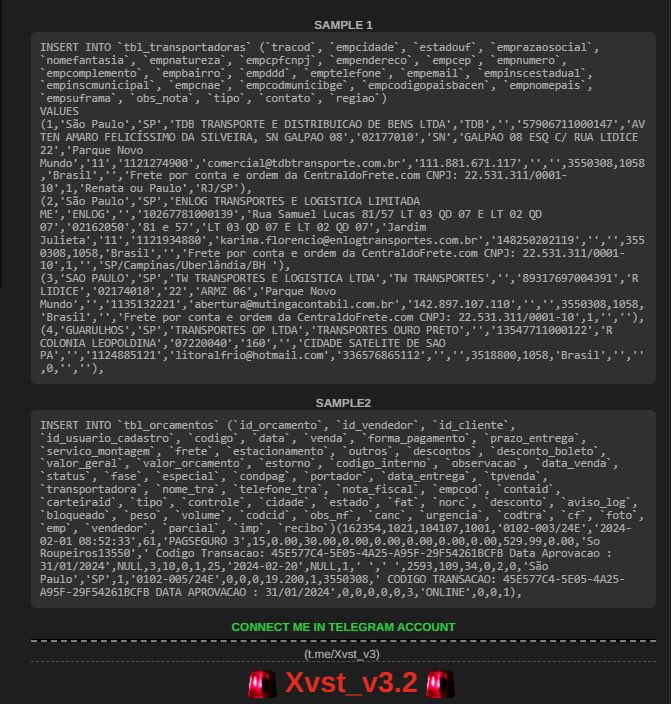
Brazilian PlaceIn Platform Database Allegedly Offered for Sale
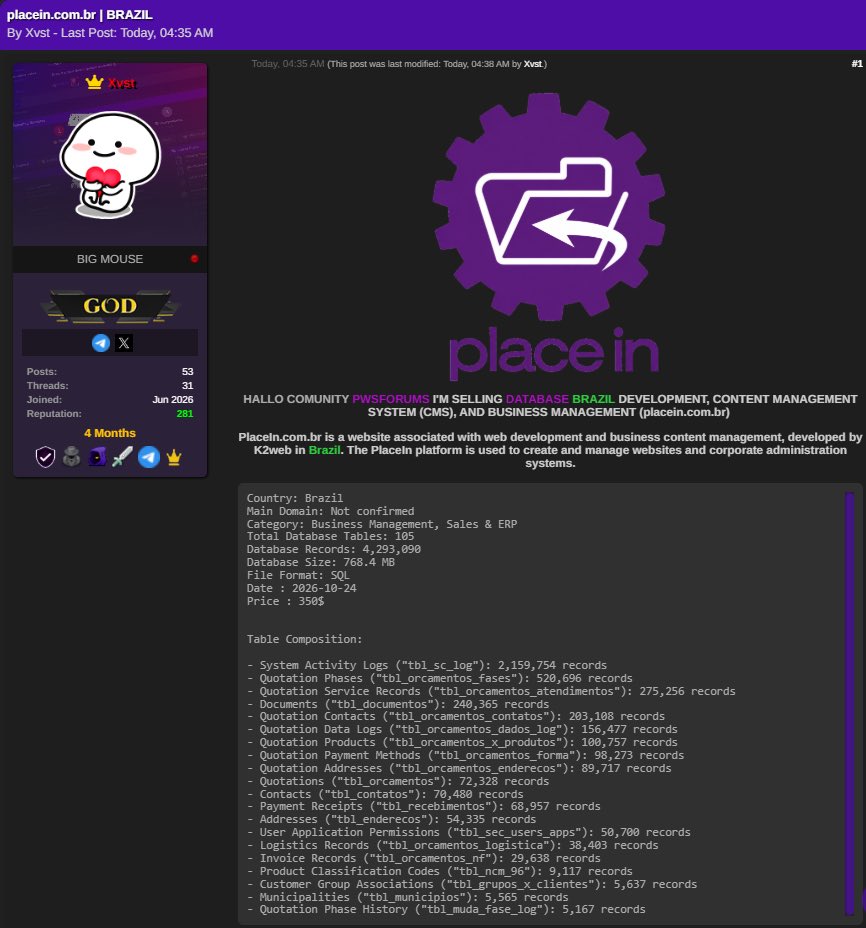
Threat actor Xvst claims to be selling a database allegedly associated with PlaceIn, a Brazilian business and content management platform. The 768MB SQL database reportedly contains more than 4.29 million records across 105 tables, including system logs, quotations, documents, contacts, addresses, payment records, invoices and logistics data.
Organization: PlaceIn
Country: Brazil
Sector: Business Management / CMS / ERP
Threat Actor: Xvst
Incident: Alleged Database Sale
Status: Unverified Claim
Source: PwnForums
#CyberSecurity #DataBreach #Brazil #DataLeak #ERP #ThreatIntel
Argentina’s Diagnóstico Tesla Patient Database Allegedly Leaked
Threat actor Synq1xxss claims to have released four databases allegedly associated with Diagnóstico Tesla, a medical imaging provider in Argentina, totaling approximately 2 million records. The exposed information reportedly includes patient names, dates of birth, study dates, gender and medical imaging-related metadata.
Organization: Diagnóstico Tesla
Country: Argentina
Sector: Healthcare / Medical Imaging
Threat Actor: Synq1xxss
Incident: Alleged Patient Data Leak
Status: Unverified Claim
Source: DarkForums
#CyberSecurity #DataBreach #Argentina #Healthcare #PatientData #ThreatIntel #DataLeak
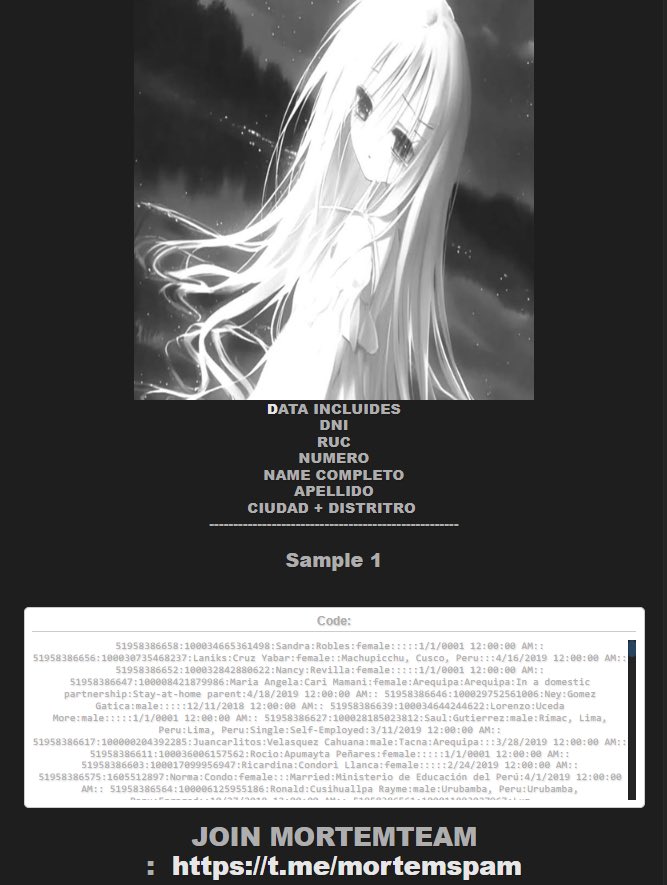
Peruvian Government Citizen Data Allegedly Leaked
MORTEMTEAM members Returner$ and KerberusCrow claim to have released government-related data from Peru covering records dated between 2017 and 2026. The dataset reportedly exposes citizen identity and location information, including DNI and RUC identifiers, names, phone numbers, cities and districts.
Country: Peru
Sector: Government
Threat Actor: MORTEMTEAM
Incident: Alleged Citizen Data Leak
Status: Unverified Claim
Source: DarkForums
#CyberSecurity #DataBreach #Peru #Government #DataLeak #ThreatIntel
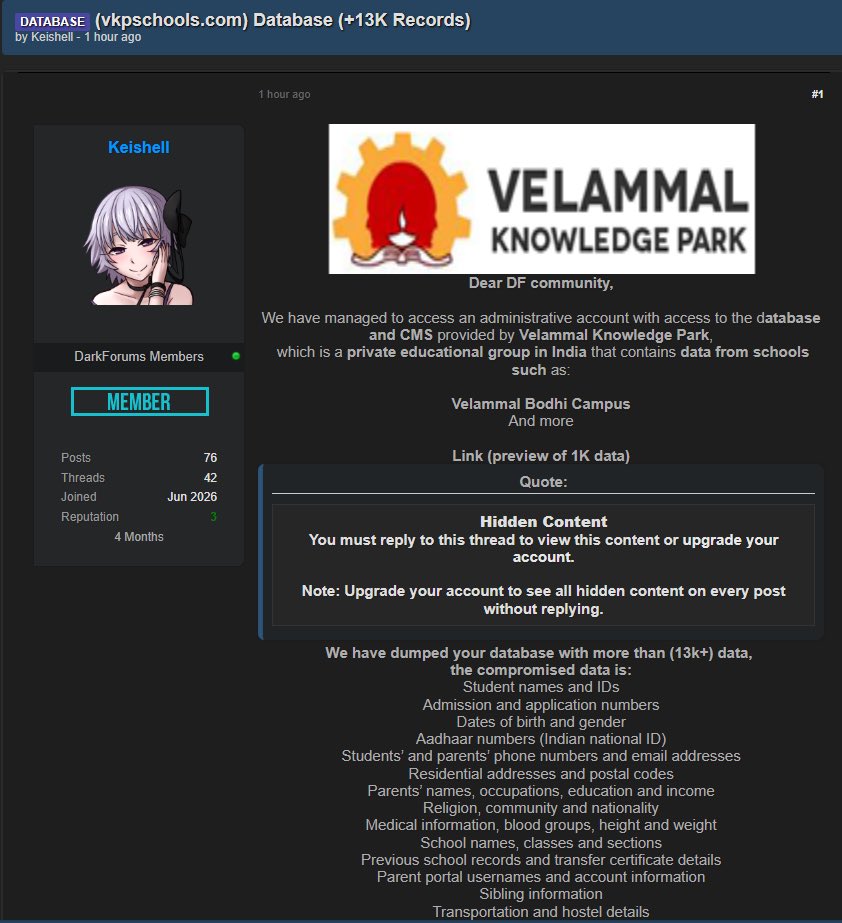
Velammal Knowledge Park Student Database Allegedly Breached
Threat actor Keishell claims to have compromised an administrative account associated with Velammal Knowledge Park in India and extracted more than 13,000 records. The allegedly exposed data includes student and parent identity and contact information, Aadhaar numbers, academic records, medical information, household details and parent portal account data.
Organization: Velammal Knowledge Park
Country: India
Sector: Education
Threat Actor: Keishell
Incident: Alleged Database Breach
Status: Unverified Claim
Source: DarkForums
#CyberSecurity #DataBreach #India #Education #StudentData #ThreatIntel #DataLeak
Bangka Belitung Manufacturing Polytechnic Alumni Database Allegedly Offered for Sale
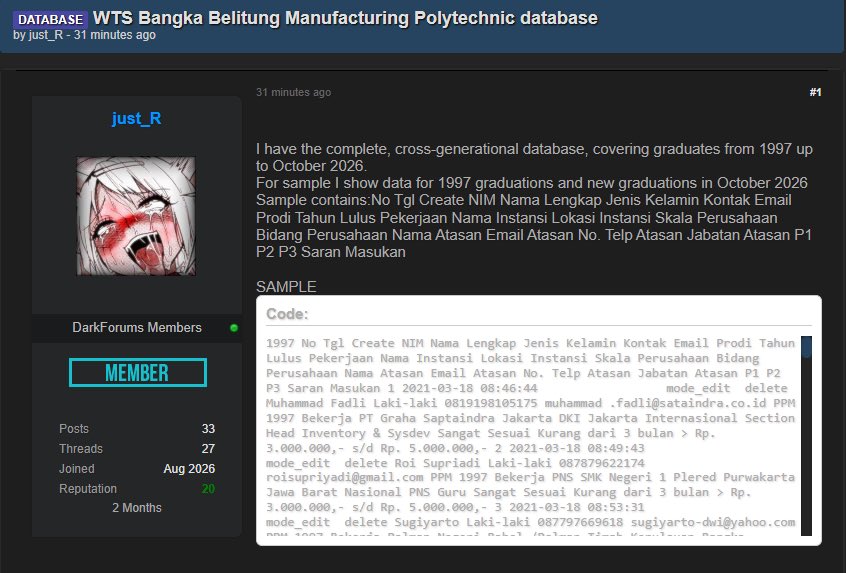
Threat actor just_R claims to possess a complete alumni database associated with Bangka Belitung Manufacturing Polytechnic in Indonesia, covering graduates from 1997 through October 2026. The dataset reportedly contains graduate identity and contact information, academic details, employment histories, employer information and workplace-related records.
Organization: Bangka Belitung Manufacturing Polytechnic
Country: Indonesia
Sector: Education
Threat Actor: just_R
Incident: Alleged Database Sale
Status: Unverified Claim
Source: DarkForums
#CyberSecurity #DataBreach #Indonesia #Education #DataLeak #ThreatIntel
Spanish Football Federation RFFM Targeted in Extortion Claim
Threat actor injecteur claims to have identified a critical vulnerability affecting the Royal Madrid Football Federation (RFFM) and is demanding $30,000 in cryptocurrency within 48 hours. The actor threatens to leak or sell data allegedly accessible through the vulnerability, including player and staff identity, contact and residential information.
Organization: Royal Madrid Football Federation (RFFM)
Country: Spain
Sector: Sports / Football
Threat Actor: injecteur
Incident: Alleged Vulnerability Exploitation / Extortion
Status: Unverified Claim
Source: DarkForums
#CyberSecurity #Extortion #Spain #RFFM #DataBreach #ThreatIntel
Argentina’s Marandu Comunicaciones HR Data Allegedly Leaked
Threat actor road2eldorado claims to have leaked an HR database and more than 1,200 files allegedly obtained from Marandu Comunicaciones, a telecommunications provider in Misiones, Argentina. The exposed material reportedly includes payroll information, employee-related data and internal PDF documents.
Organization: Marandu Comunicaciones
Country: Argentina
Industry: Telecommunications
Threat Actor: road2eldorado
Incident: Alleged HR Data Leak
Status: Unverified Claim
#CyberSecurity #DataBreach #Argentina #Telecom #DataLeak #ThreatIntel
Phishing Alert #34
Url: hxxp://digilocker.governement.info/
Country: India
Organization: DigiLocker — National e-Governance Division (NeGD), Ministry of Electronics & Information Technology (MeitY), Government of India
Industry: Government / Digital Public Services / e-Governance
Main services: Secure digital storage, access, issuance, sharing and verification of official documents and certificates, including identity documents, driving licences, vehicle registrations, academic certificates and other government-issued records.
Norway Citizen PII Dataset Allegedly Leaked
Threat actor xexa claims to have released a combined dataset containing personal and financial information associated with Norwegian citizens. The compilation reportedly includes names, phone numbers, residential addresses, postal information, family-related records and banking data gathered from multiple datasets.
Country: Norway
Sector: Financial / Consumer Data
Threat Actor: xexa
Incident: Alleged Data Leak
Status: Unverified Claim
Source: PwnForums
#CyberSecurity #DataLeak #Norway #Privacy #ThreatIntel #DataBreach
Kuwait Blizzard Computer Store Database Allegedly Offered for Sale
Threat actor Lenken claims to be selling data allegedly obtained from Blizzard Computer Store in Kuwait. The dataset reportedly contains more than 5,700 customer records alongside thousands of invoices, orders and transaction records, exposing contact information, payment-related details, purchase histories and transaction metadata.
Organization: Blizzard Computer Store
Country: Kuwait
Industry: Electronics / Retail
Threat Actor: Lenten
Incident: Alleged Data Sale
Status: Unverified Claim
#CyberSecurity #DataBreach #Kuwait #DataLeak #Retail #ThreatIntel