🔥 TIKUS IS RELEASED 🔥. DOWNLOAD FROM https://t.co/B2gsEwuBt4 ⚡OR GOOGLE PLAY
Android: https://t.co/NzdRHNydIm
iOS: Soon
First users will have a lot of advantages! Tikus is here to transform the landscape!!! 🔥
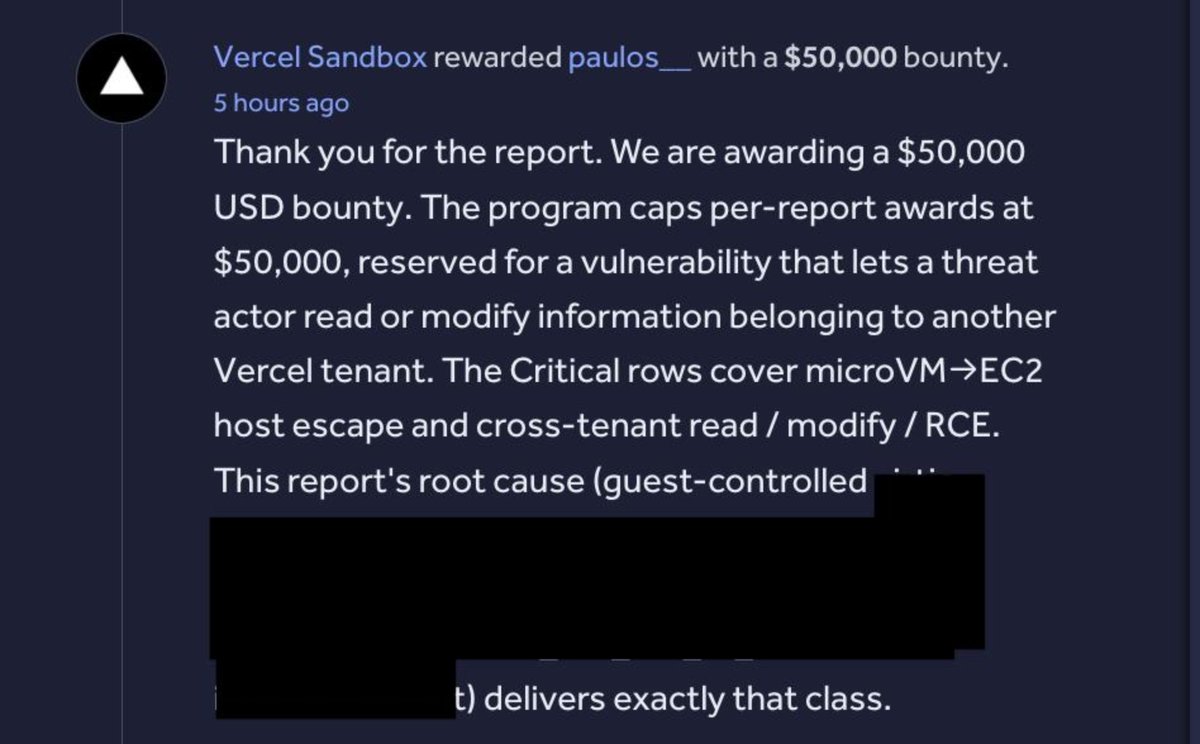
We’ve confirmed a KVM 0day through our Vercel Sandbox bounty program. Affecting the industry’s gold standard solution for Linux virtualization.
2026 is wild! Thankful to Paulos and other researchers helping us make the most secure sandbox for agents. Full writeup coming.
How pwn agents escaped the hardest-known sandbox setup: Google’s KVM (kvmCTF).
https://t.co/EWImJMfCFe
To celebrate 10K followers 🥳, we’re launching Stories from Inside the Sandbox, our new sandbox escape series.
‼️ WARNING - New WordPress "Click2Shell" vulnerability can force a silent theme install from a crafted link.
Researchers chained the flaw with a separate theme bug to execute code on the server.
Read details here → https://t.co/WXmhAp42Iq
So... we decided to hack WordPress Core, AGAIN! 🔥 ⛓️ Click2Shell is a one-click unauthenticated remote command execution chain (Preauth RCE) affecting every WordPress website. Wordpress rolled out a fix yesterday! The story about how one preview link made WordPress click Install, load an inactive theme's PHP, and hand us RCE is below. Happy Friday!
https://t.co/91D2F2lSdb
Muse Spark 1.3 is rolling out today with frontier performance almost too cheap to meter. This is the biggest jump we've made so far on coding and agentic work. Try it in Muse Code and our API.
Next up 🍉 and Muse Spark open weights releases coming soon.
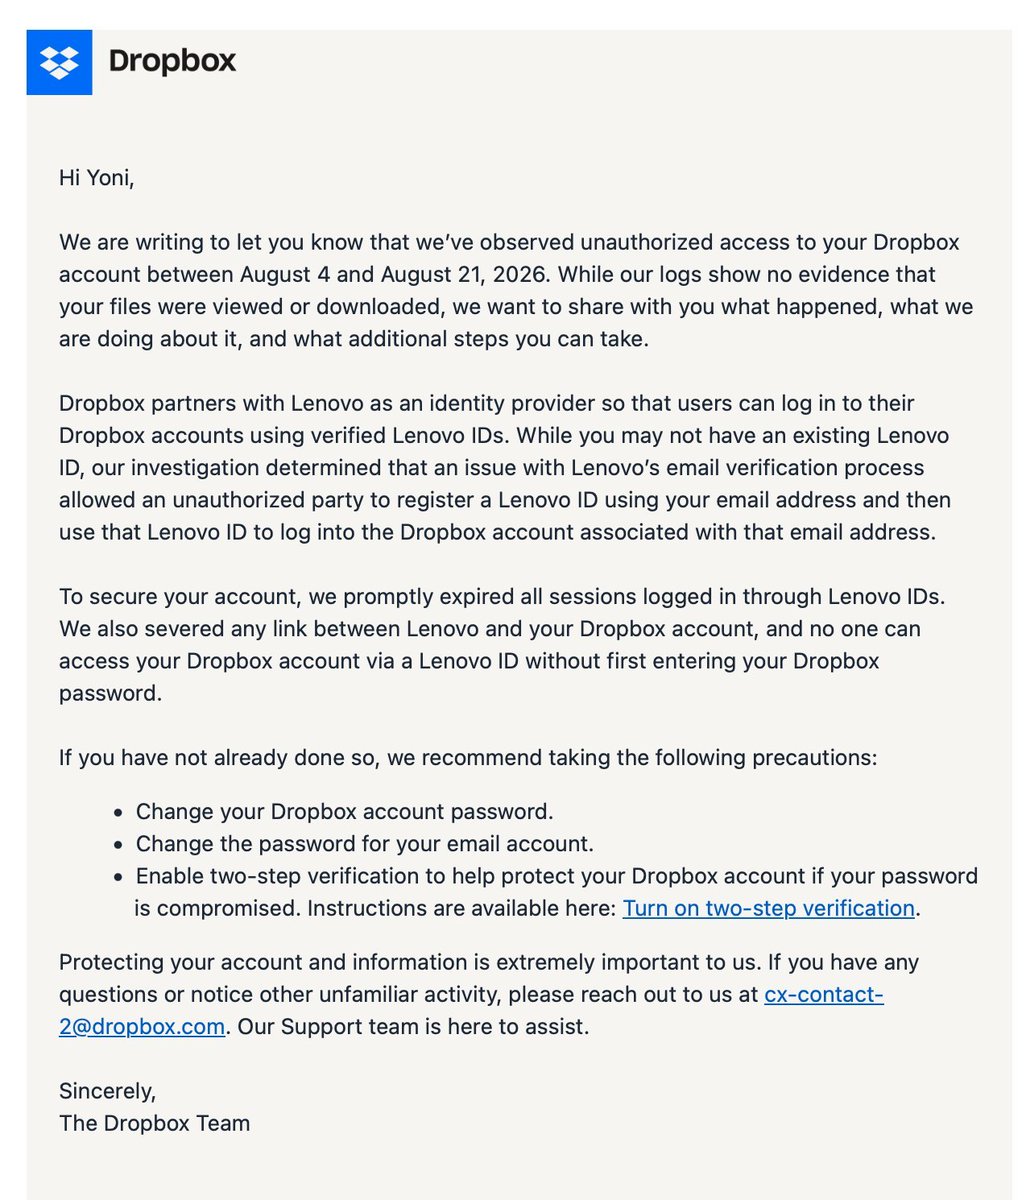
‼️ BREAKING: Dropbox says around 5,000 accounts were accessed without authorisation between 4 and 21 August, with files viewed or downloaded in fewer than a third of them.
Registering a Lenovo ID with someone else's email address was enough. Dropbox trusted Lenovo's verification and handed over a session.
Dropbox has terminated every Lenovo ID session and notified regulators.
@fouadmatin It didn't work. I tried to reverify many times and after few tries it says contact support where support doesn't seem to have any clue. It was working fine for months so this is cruel to force me to abandon my old account. And for what reason
@lorenzofb It's a weird mistake. A lot of people who were asked to reverify, when they tried to - it kept saying try again until after 30+ attempts and it then would say "contact support" where support is completely unhelpful saying they don't have access to TAC related stuff.
@cyb3rops Does being a "defender" mean you have to be retarded? Do u not know any one click RCE criticals ? 🤣
Giving all defenders bad names. Delete this lmao
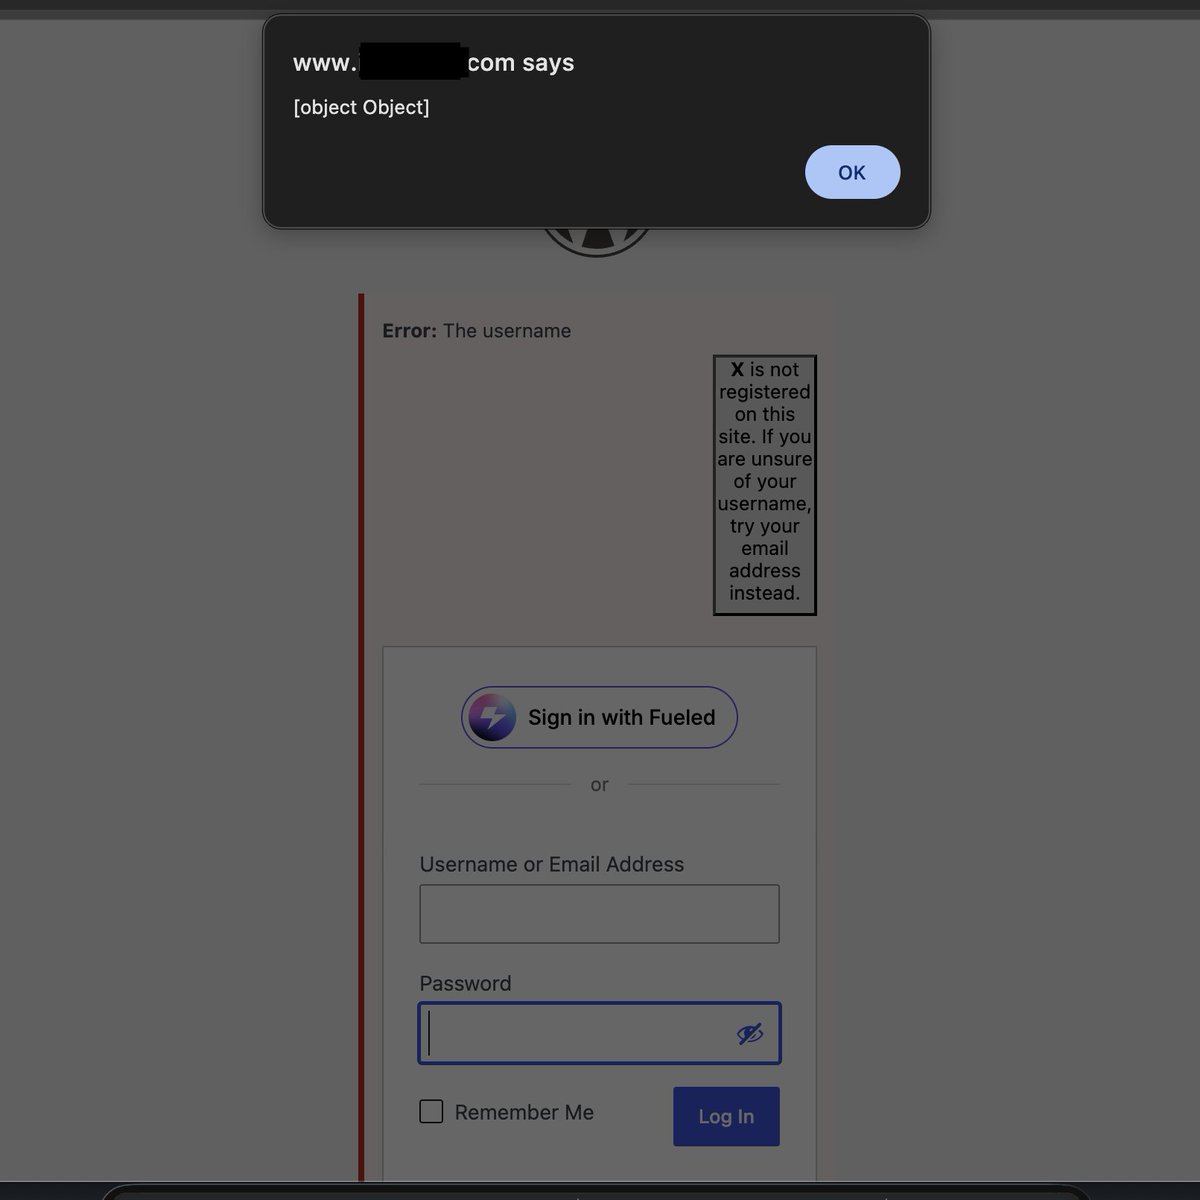
‼️ BREAKING: A critical WordPress Core vulnerability, which was found with open-weight LLMs, has been patched. It's a pre-auth XSS to remote code execution chain affecting every version of WordPress ever shipped.
Type a fake username, and WordPress prints it back in the error message. Add one space in the right place and WordPress prints it back as working code instead of text, no account needed.
pwn ai rode it to PHP execution on the server. CVE-2026-64638. Patched in WordPress 7.0.3.