Just posted part 2 for PwnEscape, this time targeting Firecracker and included the process of porting it from host memory leak to controlled write to root:
Good morning, we escaped the famous Firecracker VM and got root execution on the host.
Full firecracker escape technical writeup and Proof of Concept code attached below.
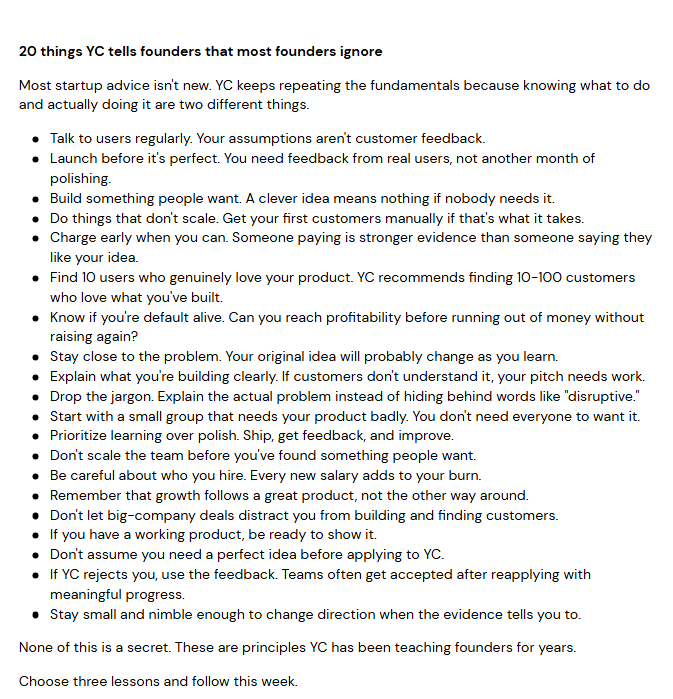
One of the most unexpected things about YC is how long we continue helping the founders. Even though we're generally the first investors, we're the ones still advising them 10 years later. I think it's because we're the investing analogue of old friends.
One question founders always ask when we speak at YC is: How much of the standard startup advice still applies in the age of AI? At this point, nearly all of it. I can't promise that will be true in 10 years, but at this moment, starting a startup is much the same as always.
Introducing CVE-2026-106378: Chrome GPU Sandbox Escape to full Remote Command Execution using synthetic keyboard injection
By combining it with common GPU bugs, it becomes a full chain. Binance DevOps was most likely pwnd with a zeroday chain affecting the browser 😬
The best part of Tikus is what people bring to it: their interests, their humor, their everyday lives. You have your own perspective to add. Share a little of your world with your first post.
https://t.co/0XvFMuiQMV
there's a real risk that a single PHP server will be exploited to infiltrate a guest OS somewhere, & from there, CVE-2026-99999 could be exploited to breach the host OS, leading to all other guest servers. So even if you don't run php, if some random customer of your host does, you are still going to be affected. This is esp concerning knowing most vps/compute providers still aren't patched.
The details of the long awaited KVM Escape are published. PwnEscape leads to VM escapes across multiple hypervisors due to a super cool Linux networking bug.
CVE-2026-99999 is a 9.3 CVSS critical rated KVM escape ⛓️
https://t.co/CXLvvjLxyF
Armadin researcher @mhskai2017 has uncovered an authenticated RCE vulnerability in Skype for Business Server (CVE-2026-70297, CVSS 8.8).
An attacker can exploit a path traversal vulnerability to write arbitrary files to the server while holding a valid token that can access any chat room with file-upload feature supported. No user interaction required. Patch immediately.
Updates are available for Skype for Business Server 2019 CU8, 2015 CU13, and Subscription Edition CU1.
Microsoft advisory: https://t.co/AtDO2Tkg9L
Introducing PwnEscape 🦉: a full KVM guest-to-host escape via a Linux kernel networking flaw affecting industry standard hypervisors.
CVE-2026-99999 went from untrusted VM code to host-kernel memory reads, controlled writes, and root command execution. More below:
A friend is trying to report a valid security vulnerability to @Meta (which I've reviewed), but the AI triager keeps closing it for incorrect reasons.
Could someone from Meta's security team reach out to me by any chance?
This is one of the most exhilarating times in technology, and this challenge was yet another jaw-dropping moment.
When the details of OpenAI’s agent escape and Hugging Face hack started to emerge, it became clear that agent containment would be one of the most important priorities for any AI infra company.
There are two classes of escapes: ① "escape the network" and ② “escape the matrix” 😁, as in, break the spell of virtualization. OpenAI was the former, where an agent not supposed to have internet access… gained it by hacking another system. Genuinely astonishing and worrisome.
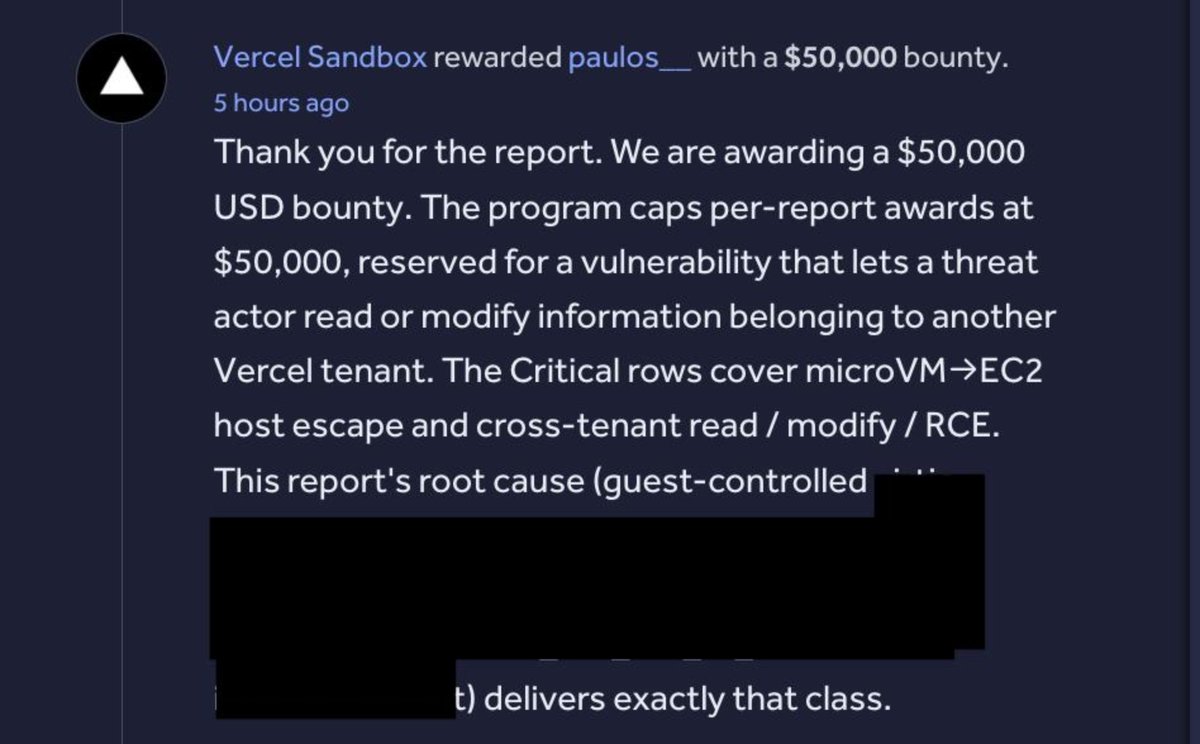
Through this challenge, however, we discovered something even more groundbreaking. A talented white-hat researcher, armed with a swarm of AI agents, expertise and perseverance, "pierced through" the Linux virtualization boundary that nearly every cloud sandbox provider in the world banks on today.
I'm very thankful we got the report, were able to quickly move to protect our customers, found no evidence of customer data compromise, and collaborated with many industry partners to protect the wider internet.
Our confidence and conviction in Vercel Sandbox are even greater now, after some of the smartest, most motivated researchers in the world, and their agents, gave it their best shot.
Tomorrow the vulnerability details for the coolest (imo) KVM escape will drop. The Vercel team was amazing to work with and has been an incredible partner throughout this journey!