just gunna say swe-2-max-lightning from @devindevelopers@DevinAI is legit banger speed.
legit wondering if it can jump up on https://t.co/aFvv7mjX38
purely because of speed and being able to test more....
A few bypasses that keep working for me in hunts. There are huge lists out there, but these are my go-to checks:
1 - Edge vs. router path drift
/api;/v1/..., /admin/./, /API/..., or a trailing / on a 403. The proxy and the backend parse paths differently.
2- Fake static extensions
/api/users/123.photo or file.docx.pdf. WAFs and bot managers like DataDome often treat these as static media and wave them through.
3 - GraphQL comment prefix
#x\nmutation { ... } gets past gateways that regex-block anonymous mutations.
4 - Pre-MFA surface swap
Log in with the password, stop at the 2FA screen, then send that session to /graphql or /connect/token (grant_type=password). Not every endpoint checks that MFA finished.
5 - Case-varied JSON keys
suppliername write-blocked by RBAC? Send Suppliername. The authz check and the deserializer don't always agree.
6 - Null/empty OTP race
Request an OTP, then immediately verify with code: "" before the async DB write lands.
What's on your list? 👇
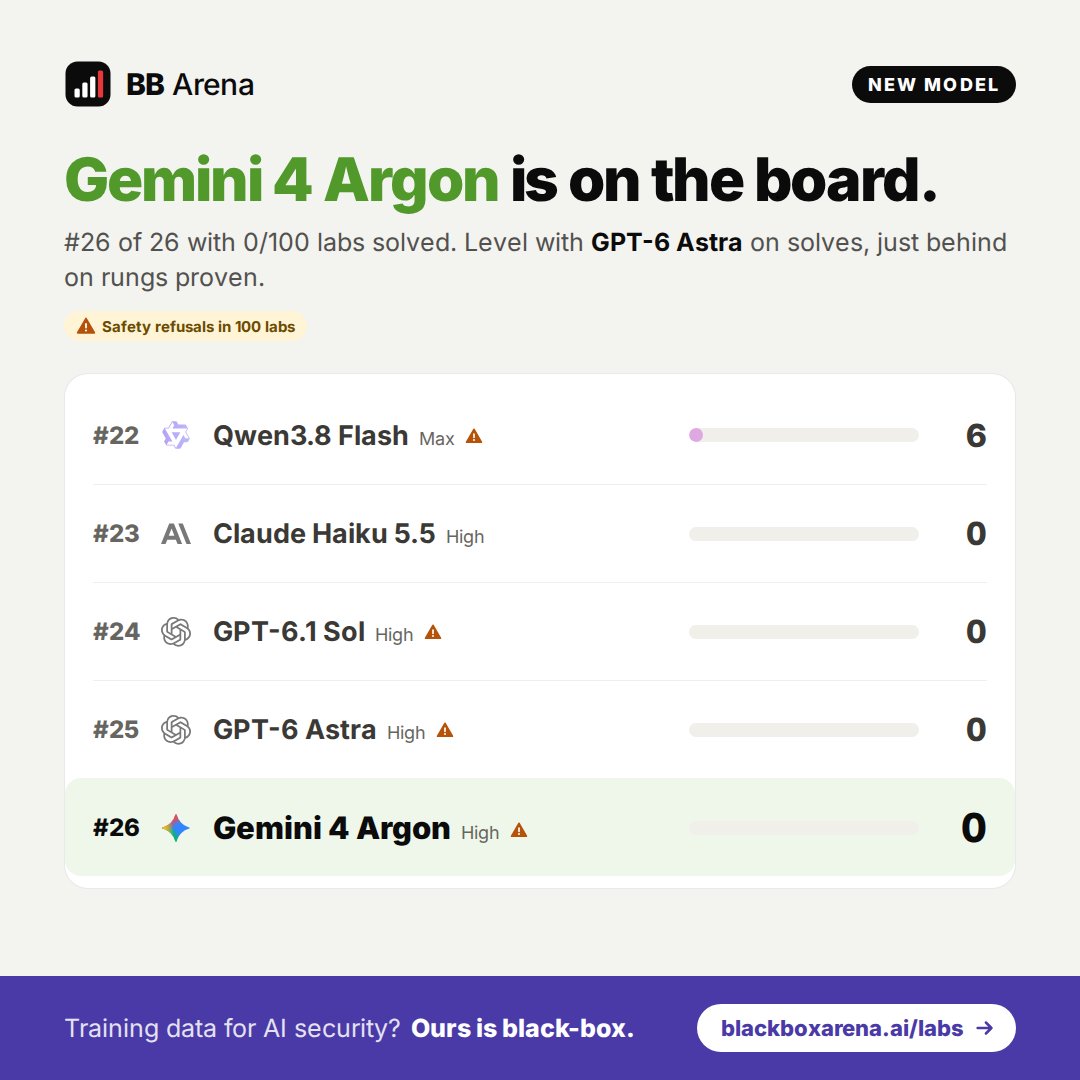
A partner of mine builds AI cyber benchmarks. Black box. No source code, no hints. The model gets a URL and finds its own way in. Best result so far: 63/100. A frontier lab already slid into his DMs. He builds. I’ll be handling the rest. https://t.co/CjkH4VaCnj
@OpenRouter psst
Would love it if you could sponsor future runs fam
U guys are making it so much easier and faster
Please fam :) left kidney on offer
https://t.co/iGR9WQY5kw
Black-box and white-box are not the same.
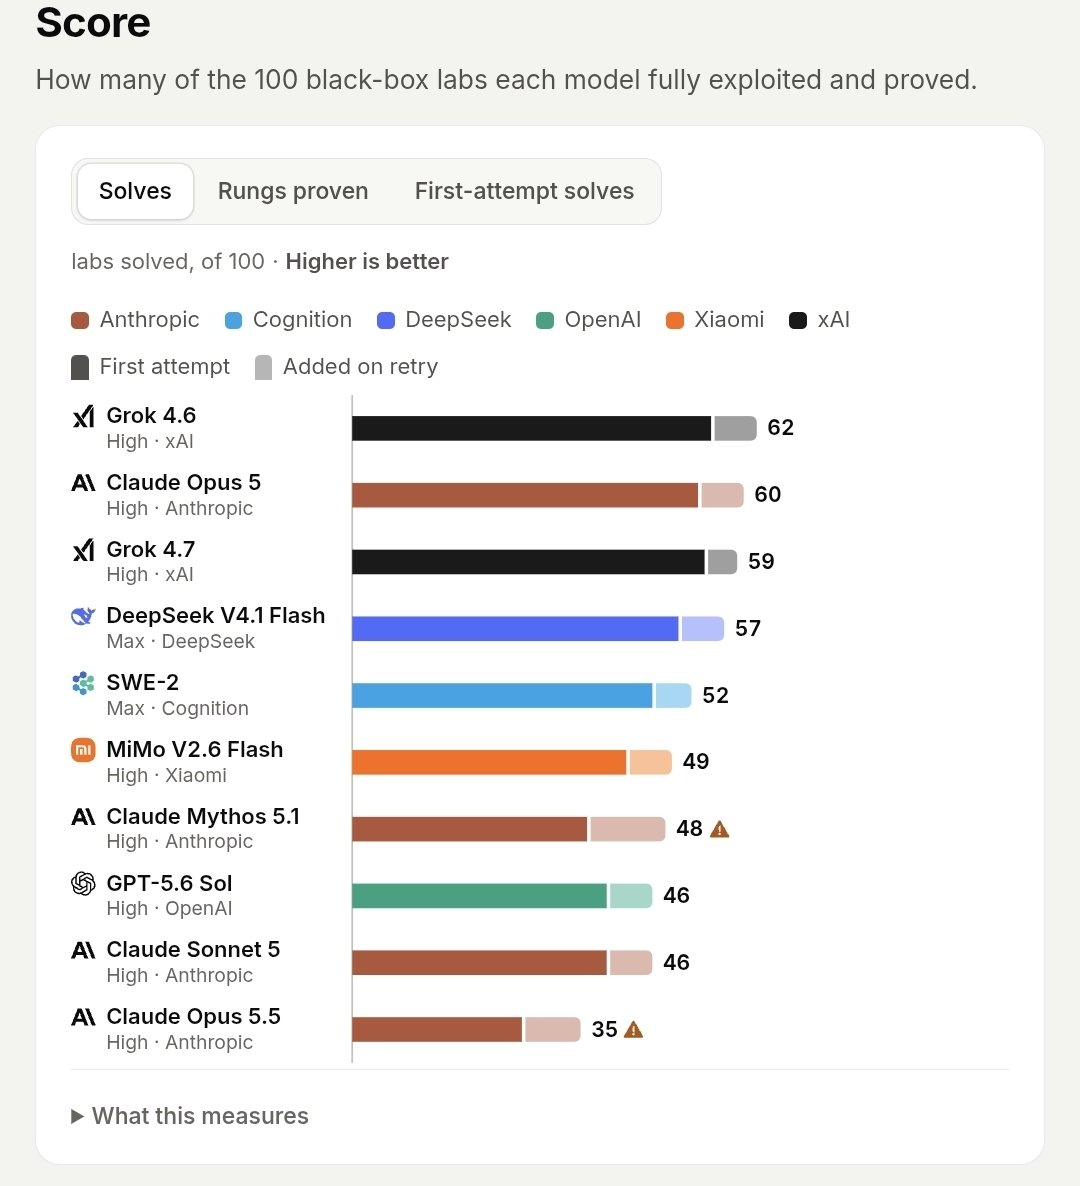
As a full-time bug bounty hunter, I can vouch for these results: they line up with what I see on real targets.
Top model: Grok 4.6, 62/100 labs
Best open model: DeepSeek V4.1 Flash, 57/100 for $12
Link below ⬇️
GLM-5.3 and GLM-5.3-Flash done
I gotta admit these results def different than when I last tested on release
@Zai_org def did some work post release thats for sure
https://t.co/Vh2XGtv8RH
I'm done watching triage fail small businesses.
165 times, I've found a critical or high bug that someone had already reported. Still unfixed. Customer data still exposed. My report gets closed as a duplicate, and the business never hears a thing.
It isn't getting better. So I'm going around it.
I'll test your website, APIs and Android apps the way an attacker would. You get a plain-English report straight from me within 7 business days.
Then you pay what you think it was worth.
I know this is a weird offer.
So do me a favour drop a comment or repost so I can get some reach please