Roots&Grind is more than just a clothing brand — it’s a movement.
It represents ambition, resilience, and identity. Every piece is designed to remind you1
WE RESCUE DOGS. BUT TODAY, WE’RE CELEBRATING A DIFFERENT KIND OF RESCUE!
BIG NEWS: LimeWire (@limewire ) has officially taken over Cookie3 (@cookiedotfun ) and Cookie Pro!
Just like rescued dogs, great projects deserve a lives to grow, evolve and thrive. 🐾
@playTrenches Let the player feel the game is real mission based
Bring streets out, get the knives as part of armoury, let the game have a story line every fight or use to kill weapon people will buy those tools to commit a kill you earn dollar 💵
@playTrenches and interacting naturally.
Objects: Real-world appearance, proportions, materials and physics.
Camera: Cinematic third-person or first-person perspective.
Animation: Natural human movements rather than cartoon-style animation.
@playTrenches Work on this bro The visual direction would include:
Human characters: Realistic faces, skin textures, body proportions, clothing and movements.
Environment: Realistic buildings, roads, trees, landscapes, weather and lighting.
Human interactions: Walking, talking, working,driving
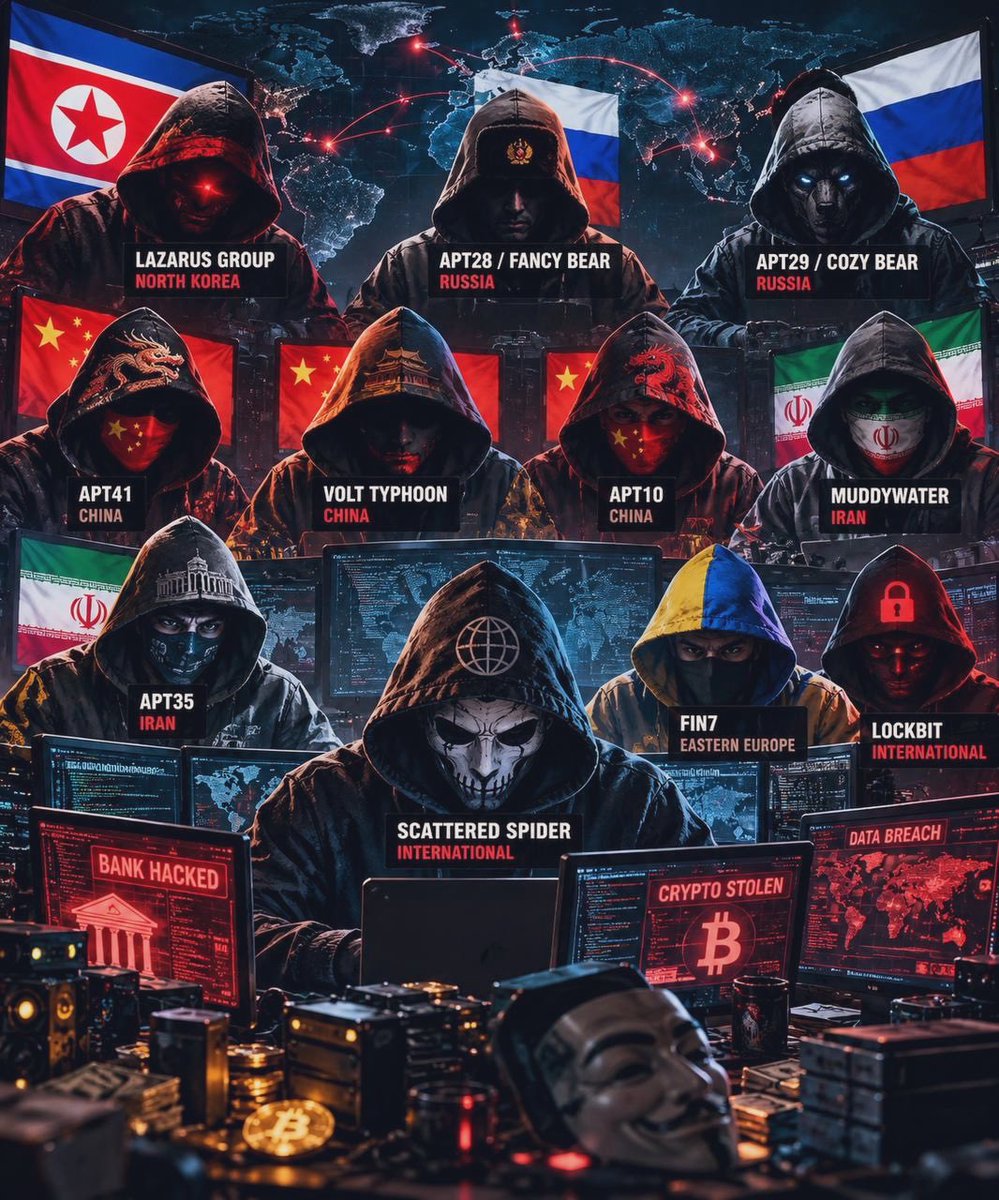
TOP 15 MOST NOTORIOUS HACKER GROUPS IN THE WORLD.
A breakdown of some of the world’s most sophisticated and dangerous cyber threat groups, their countries of origin, and their primary targets.
🇰🇵 NORTH KOREA
Lazarus Group
Targets: Cryptocurrency exchanges, banks, financial institutions, and government agencies.
Known for: Major crypto thefts, the Sony Pictures attack, and international cyber espionage.
APT38 (BeagleBoyz)
Targets: Banks, financial networks, and payment systems.
Known for: Large-scale financial theft and attacks on international banking systems.
Andariel
Targets: Defense contractors, financial institutions, and government organizations.
Known for: Financial cybercrime and espionage operations.
🇷🇺 RUSSIA
APT28 (Fancy Bear)
Targets: Governments, military organizations, NATO, and political institutions.
Known for: Cyber espionage and intelligence operations.
APT29 (Cozy Bear)
Targets: Government agencies, technology companies, and research institutions.
Known for: The SolarWinds supply chain attack.
Sandworm
Targets: Energy infrastructure, power grids, telecommunications, and government networks.
Known for: Destructive cyberattacks and attacks on Ukraine’s power infrastructure.
🇨🇳 CHINA
APT41
Targets: Technology companies, healthcare, telecommunications, and financial institutions.
Known for: Cyber espionage and financially motivated attacks.
Volt Typhoon
Targets: Critical infrastructure, telecommunications, and government networks.
Known for: Long term infiltration of strategic infrastructure.
APT10 (Stone Panda)
Targets: Corporations, technology companies, and government organizations.
Known for: Intellectual property theft and cyber espionage.
Mustang Panda
Targets: Governments, political organizations, and diplomatic institutions.
Known for: Advanced cyber espionage campaigns.
🇮🇷 IRAN
MuddyWater
Targets: Government agencies, telecommunications, and critical infrastructure.
Known for: Cyber espionage and credential theft.
APT35 (Charming Kitten)
Targets: Government officials, academics, journalists, and organizations.
Known for: Phishing, credential theft, and intelligence gathering.
🌍 INTERNATIONAL/EASTERN EUROPE
Scattered Spider
Origins: International network, primarily English speaking operators.
Targets: Telecommunications, technology companies, and financial institutions.
Known for: Social engineering, SIM swapping, and corporate network intrusions.
FIN7
Origins: Eastern Europe, with members associated with Ukraine and Russia.
Targets: Retailers, hospitality companies, payment systems, and financial institutions.
Known for: Payment card theft and corporate cybercrime.
LockBit
Origins: International ransomware operation with strong Russian connections.
Targets: Businesses, hospitals, government agencies, and corporations.
Known for: Ransomware attacks and large scale data extortion.
THE FIVE GROUPS TO WATCH CLOSELY IN CRYPTO AND FINANCIAL SECURITY:
🇰🇵 Lazarus Group - Cryptocurrency theft and financial attacks.
🇰🇵 APT38 - Banking and financial system attacks.
🇨🇳 APT41 - Financially motivated cybercrime and espionage.
🇷🇺 Sandworm - Critical infrastructure attacks.
🌍 Scattered Spider - Corporate and financial system intrusions.
🚨 IMPORTANT: Country associations do not automatically prove direct government control or responsibility for every attack. Cyber attribution requires forensic evidence and independent verification.
Hey there, i need some little clarification about ward migration should swap my coins or shouldn't that hold on @Gate and i want to understand this please cause am almost liquidated since the price went completely down I dont want to loose any of coins again.
@wardenprotocol
Find this book in the link below its contains all the necessary information for you to master forex trading #ebook
book #fx#tradingstrategy https://t.co/cC2MDUwKb1
🚨Leave Netflix tonight.
Watch this 2 h 34 min Stanford class.
It's the clearest, most complete, and brutally honest explanation out there on how ChatGPT and Claude are really built.
From Tokenization and BPE to the Transformer architecture, the training pipeline, and the next-token decoder. No fluff. No marketing. Just the truth.
Doesn't matter if you've never touched a line of AI code or if you spend your days launching Agents: by the end, you'll suddenly connect a ton of pieces you've been trying to fit together for years.
The real core boils down to this:
How text turns into numbers the model can "eat" (BPE tokenization)
The sole mission of a language model: predict the next token
How the Transformer uses Attention so tokens can pass messages to each other
In training, the NLL loss pushes the probability of the entire sequence
In generation, the decoder builds the response token by token
The big-picture view that takes most people years to form… this class delivers it to you complete in one sitting.
Free up your time.
This could be, no exaggeration, the most valuable class you watch this month.