The funds from the $3.8M NEAR Intents exploit have been returned, just one day later, and the investigation is closed.
Thanks to SHIELD, the AI security layer on Intents, along with some aggressive detective work, the Intents team identified the party responsible less than 24h after the hack, established communication, and got the funds back in full at 14:30 UTC today.
Thank you to @alexauroradev and the whole @near_intents team for this fast and clean resolution – as well as the broader @NEARProtocol ecosystem and SHIELD partners for the support and help. There’s been relentless work over the past 24 hours by so many people to make this right and it is a great testament to this community’s values and determination.
To echo Alex: for security researchers looking for exploits, we encourage you to use bug bounties. They exist for a reason.
At NEAR, we believe that privacy is a right, but not as a way to facilitate crime. Our technology is built to expand human agency and opportunity, not to facilitate criminal activity. The events of the last week have shown the value of SHIELD to find suspicious activity before things escalate too far, as well as to accelerate resolution so the vast majority of legitimate users are not affected. Confidentiality cannot come at the expense of lawfulness and I strongly believe it doesn’t have to.
We’ve learned a great deal from this incident and work is already underway to harden our security systems and further adapt to the changing cybersecurity landscape. AI may be accelerating exploits, but it can also help us defend against them. I hope our entire industry responds with vigilance and feels the same sense of urgency to work together.
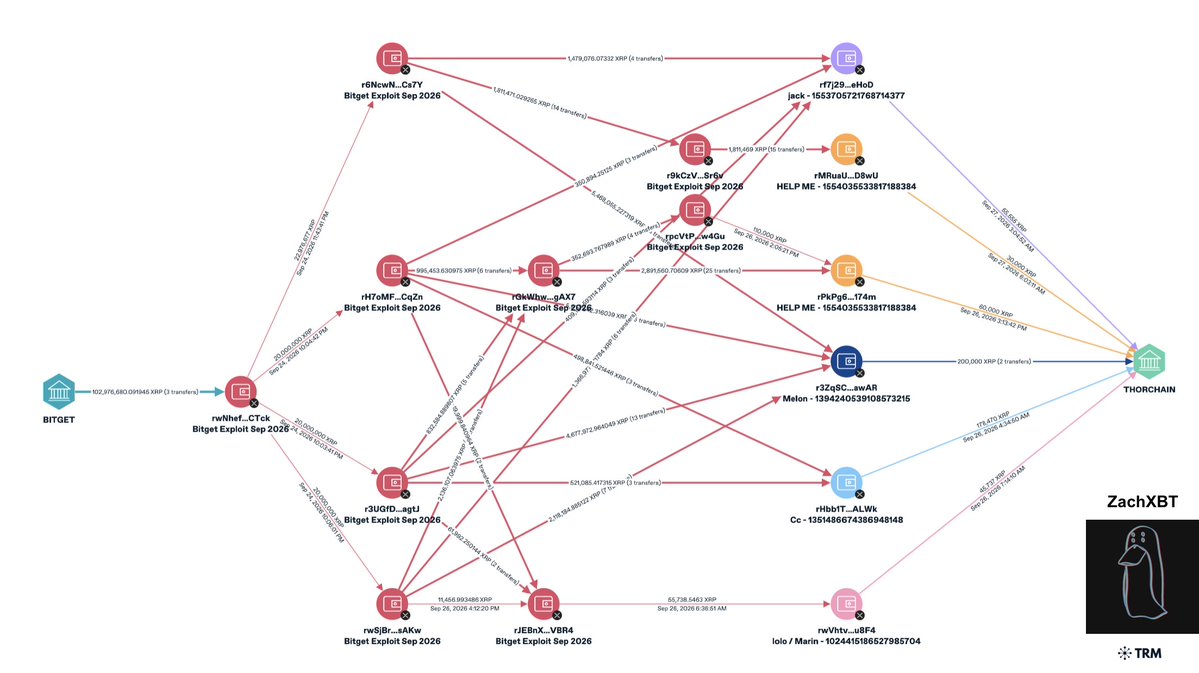
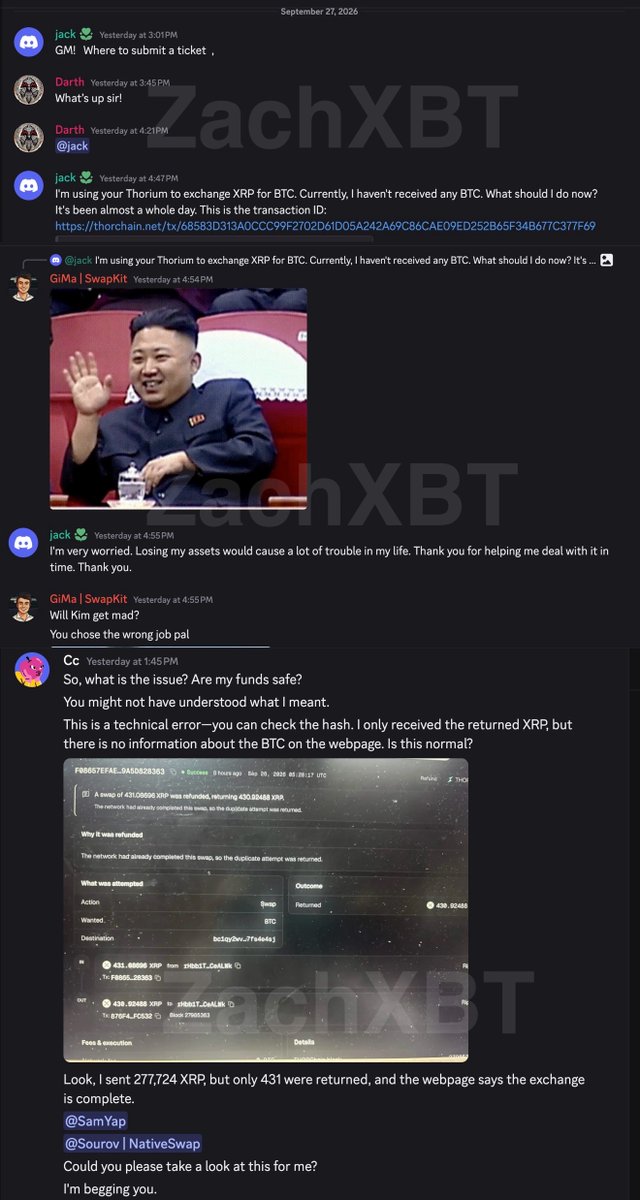
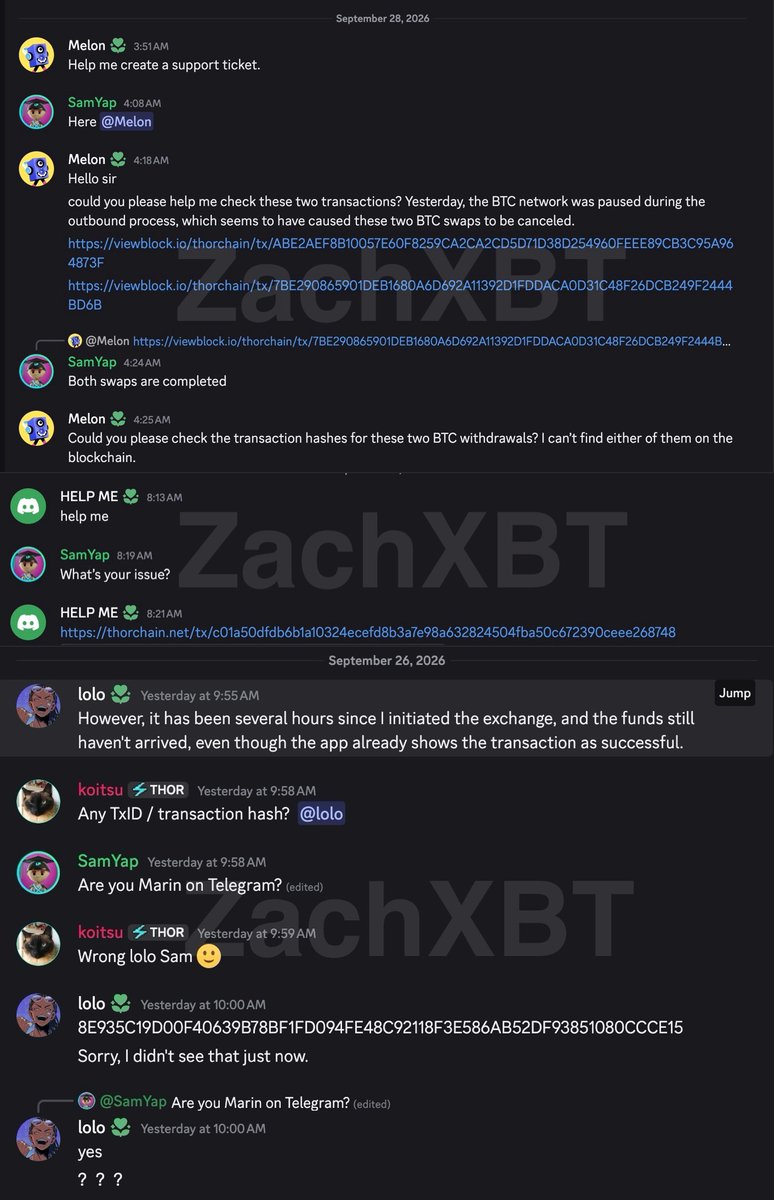
BREAKING: Chinese illicit actors laundering funds from the $387M Bitget exploit on behalf of the alleged DPRK attackers are openly asking for support with orders in public Discord servers and Telegram channels of services they use.
Notably, Alias 4 (below) was also seen laundering funds from the Kelp DAO $292M exploit earlier this year.
I've observed the same pattern after multiple TraderTraitor attributed exploits, and I've closely tracked these groups. I plan to share more of my data on them in coming weeks.
Currently, funds are being chain-hopped via bridges and being deposited into mixing services such as Wasabi.
Alias 1 - Cc
Discord: cc02006
Discord ID: 1351486674386948148
Txn: F08657EFAEAE7B58217CD17A22BF4779582E5D080C2E92E173BC239A5D828363
Alias 2 - jack
Discord: jack_34808
Discord ID: 1553705721768714377
Txn: 68583D313A0CCC99F2702D61D05A242A69C86CAE09ED252B65F34B677C377F69
Alias 3 - Melon
Discord: under0346
Discord ID: 1394240539108573215
Txn 1: ABE2AEF8B10057E60F8259CA2CA2CD5D71D38D254960FEEE89CB3C95A964873F
Txn 2: 7BE290865901DEB1680A6D692A11392D1FDDACA0D31C48F26DCB249F2444BD6B
Alias 4 - lolo / Marin
TG: pvpcz
TGID: 6223514198
Discord: losern
Discord ID: 1024415186527985704
Txn: 8E935C19D00F40639B78BF1FD094FE48C92118F3E586AB52DF93851080CCCE15
Alias 5 - HELP ME
Discord: helpme031897
Discord ID: 1554035533817188384
Txn: 7C58CAD760EBBED54F2CA4D2146D056910B7B6688B4F524396DC8807353C2379