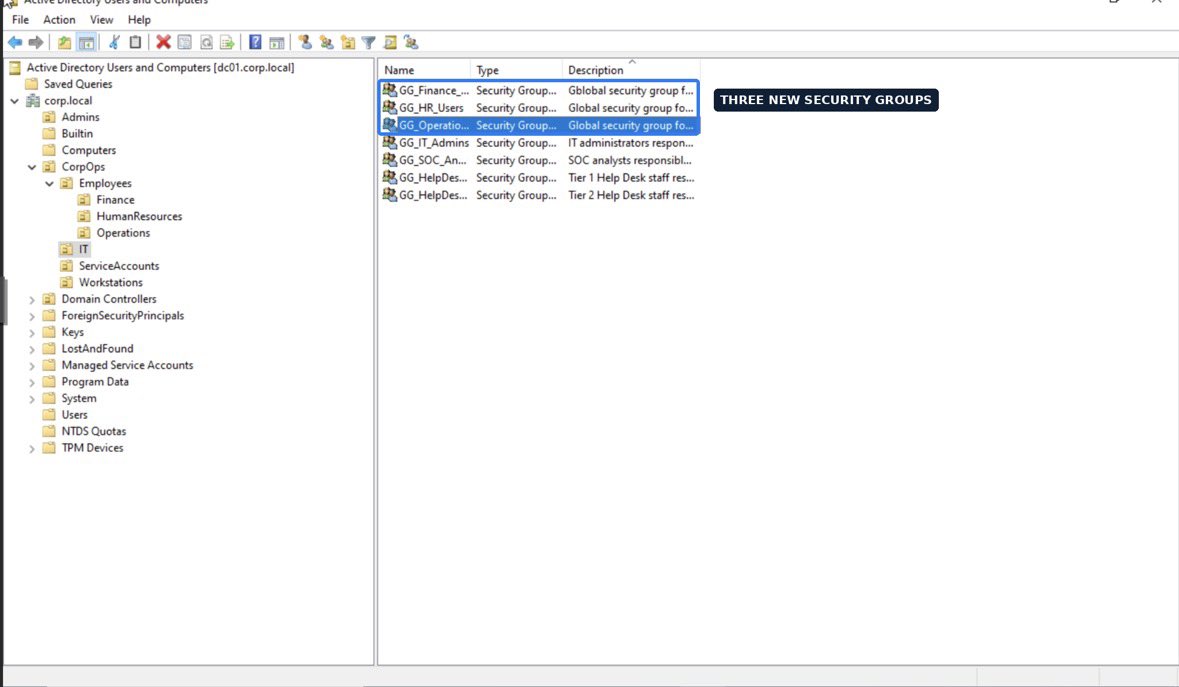
What if Active Directory shows a user in a security group, but the group's member list appears empty?
𝗗𝗔𝗬 𝟬𝟴/𝟵𝟬 | 𝗔𝗗 𝗨𝗦𝗘𝗥 𝗣𝗥𝗢𝗩𝗜𝗦𝗜𝗢𝗡𝗜𝗡𝗚
That was one discrepancy I encountered while testing three employee accounts.
The name was right. The Active Directory object type was WRONG.
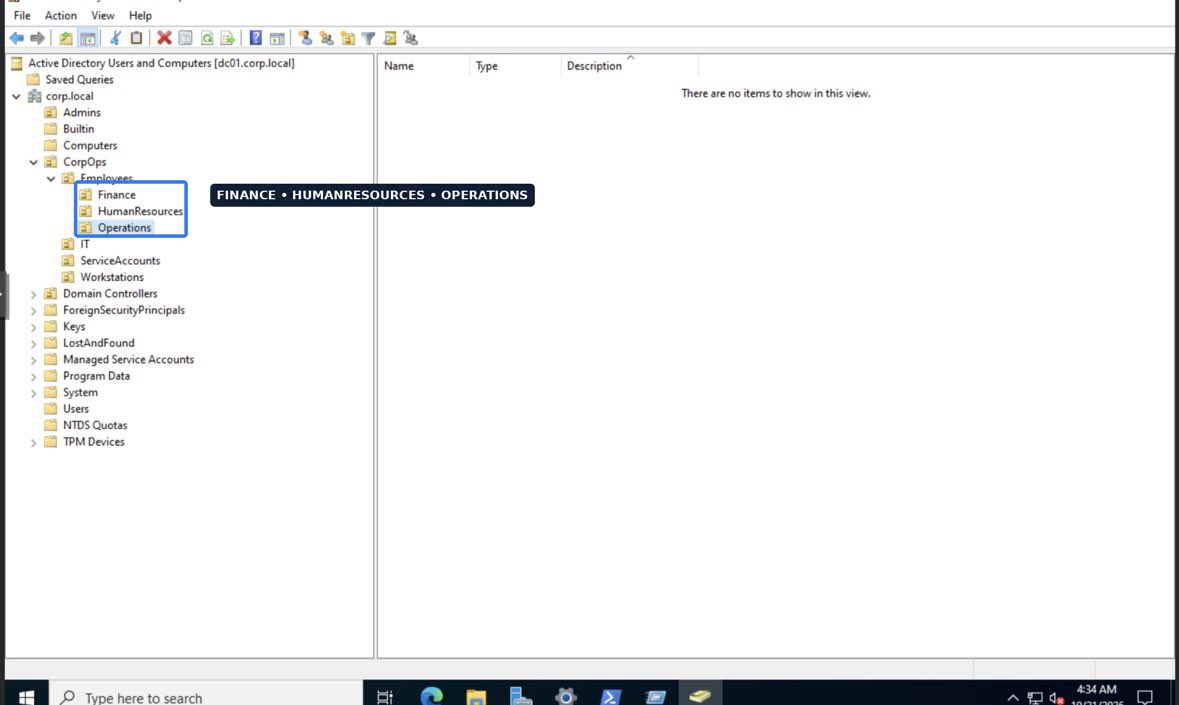
𝗗𝗔𝗬 𝟬𝟳/𝟵𝟬 | 𝗢𝗨𝘀 & 𝗦𝗘𝗖𝗨𝗥𝗜𝗧𝗬 𝗚𝗥𝗢𝗨𝗣𝗦
I initially created GG_HR_Users as an OU instead of a security group.
I caught it, corrected it, and verified the actual group.
@techspence
Nobody warned me about the emotional damage of building a home lab 😭
My Proxmox server just stopped working.
Now I have to migrate my entire lab to another laptop.
Glad I made a backup! That decision just saved me a bigger headache.
I signed up to learn cybersecurity, not to become a full-time infrastructure engineer 😂
Home lab life is not for the weak!
Want to learn something new without paying?
5 websites worth bookmarking:
1. https://t.co/jUuLAjClEm
2. https://t.co/OeT496Cayj
3. https://t.co/s9KA6gWOlQ
4. https://t.co/3IQv2zAsjS
5. https://t.co/Tvqgg3DEvs
Free learning resources in one place.
Save this for later.
A CV says you know security. A portfolio proves it.
7 ways to build one:
1. Lab and CTF writeups
2. A small tool on GitHub
3. A home lab
4. Open source contributions
5. A responsibly reported bug
6. A technical blog
7. Teaching what you learn
Start with one this week.
3 HOURS.
That's how quickly some attackers have moved from targeting an organization to privileged access.
The FBI's warning about AI-powered cyberattacks caught my attention.
Not because AI is involved, but because of what this speed means for defenders.
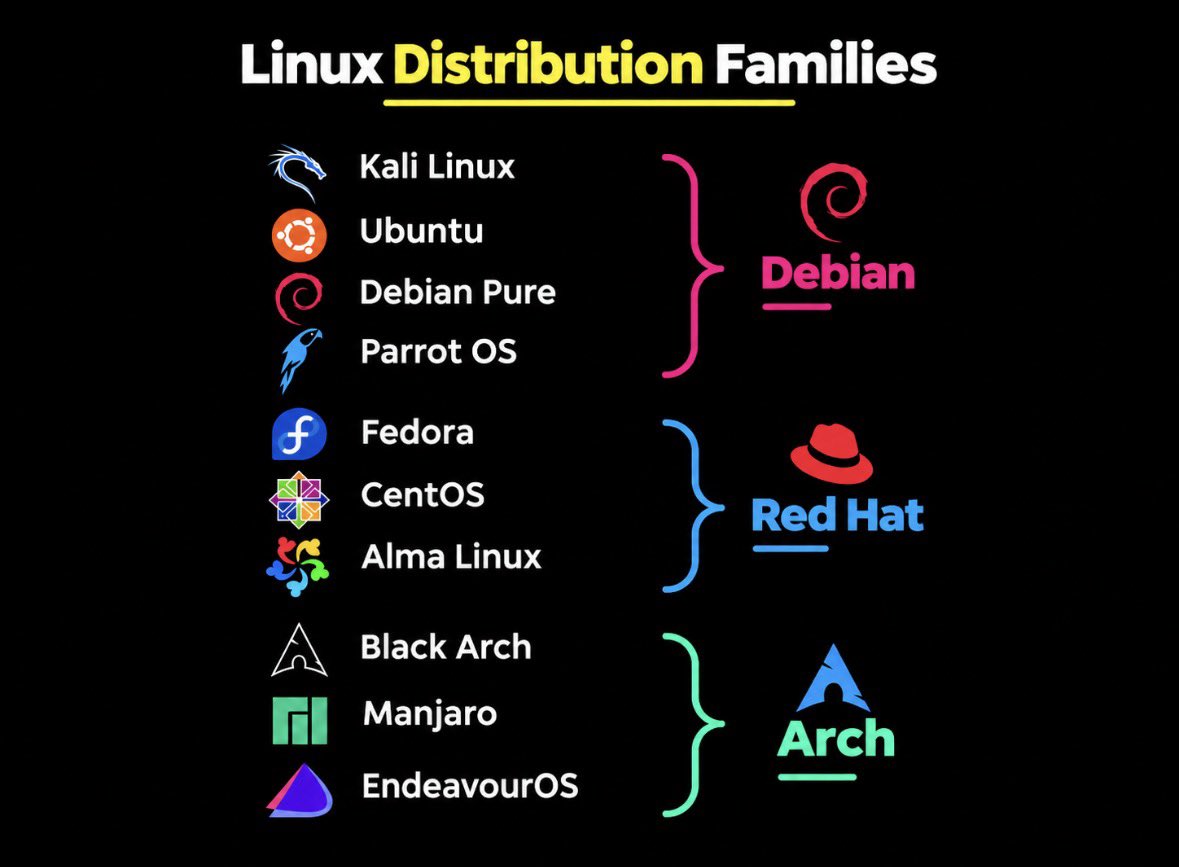
Different Linux distributions. Different security environments.
Debian, Red Hat, and Arch families differ in package management and system administration.
For SOC analysts, knowing the distribution helps identify the right logs, commands, and investigation approach.
What if Active Directory shows a user in a security group, but the group's member list appears empty?
𝗗𝗔𝗬 𝟬𝟴/𝟵𝟬 | 𝗔𝗗 𝗨𝗦𝗘𝗥 𝗣𝗥𝗢𝗩𝗜𝗦𝗜𝗢𝗡𝗜𝗡𝗚
That was one discrepancy I encountered while testing three employee accounts.
Hi, I’m Blessing Chidiebube.
I’m an Ethical Hacker, Penetration Tester, and Cybersecurity Specialist.
I work with organisations, developers, and founders to secure their systems, applications, and data against cyber threats.
I’m also a technical writer and Operations Manager.
File integrity monitoring tells you what changed. Not always who.
syscheck → Reports the change
Hash before and after → Proves content changed
who-data → Adds user and process
auditd → Needed behind it on Linux
Without who-data, you know the file changed. Not who changed it.
Different Linux distributions. Different security environments.
Debian, Red Hat, and Arch families differ in package management and system administration.
For SOC analysts, knowing the distribution helps identify the right logs, commands, and investigation approach.
Networking makes more sense when you can actually see how it works.
Found Protocol Explorer, a free interactive tool that visualizes DNS, TCP, HTTP and packet flows step by step.
Great for connecting networking theory to SOC traffic analysis.
https://t.co/mksNZu6Sr1
A proxy log shows a request to a suspicious URL. Was a file downloaded?
URL → Resource requested
Status code → Server response
Bytes received → Data transferred
Content type → Type of response
A successful request doesn't prove a file was saved.
Correlate with endpoint evidence.
A successful login proves authentication worked in that test.
It does not prove the user can access a departmental folder.
I did not test resource permissions today.
That distinction matters in SOC investigations.
Verify the evidence. Recognize what remains unknown.
@techspence
What if Active Directory shows a user in a security group, but the group's member list appears empty?
𝗗𝗔𝗬 𝟬𝟴/𝟵𝟬 | 𝗔𝗗 𝗨𝗦𝗘𝗥 𝗣𝗥𝗢𝗩𝗜𝗦𝗜𝗢𝗡𝗜𝗡𝗚
That was one discrepancy I encountered while testing three employee accounts.
The name was right. The Active Directory object type was WRONG.
𝗗𝗔𝗬 𝟬𝟳/𝟵𝟬 | 𝗢𝗨𝘀 & 𝗦𝗘𝗖𝗨𝗥𝗜𝗧𝗬 𝗚𝗥𝗢𝗨𝗣𝗦
I initially created GG_HR_Users as an OU instead of a security group.
I caught it, corrected it, and verified the actual group.
@techspence
Next came the real test.
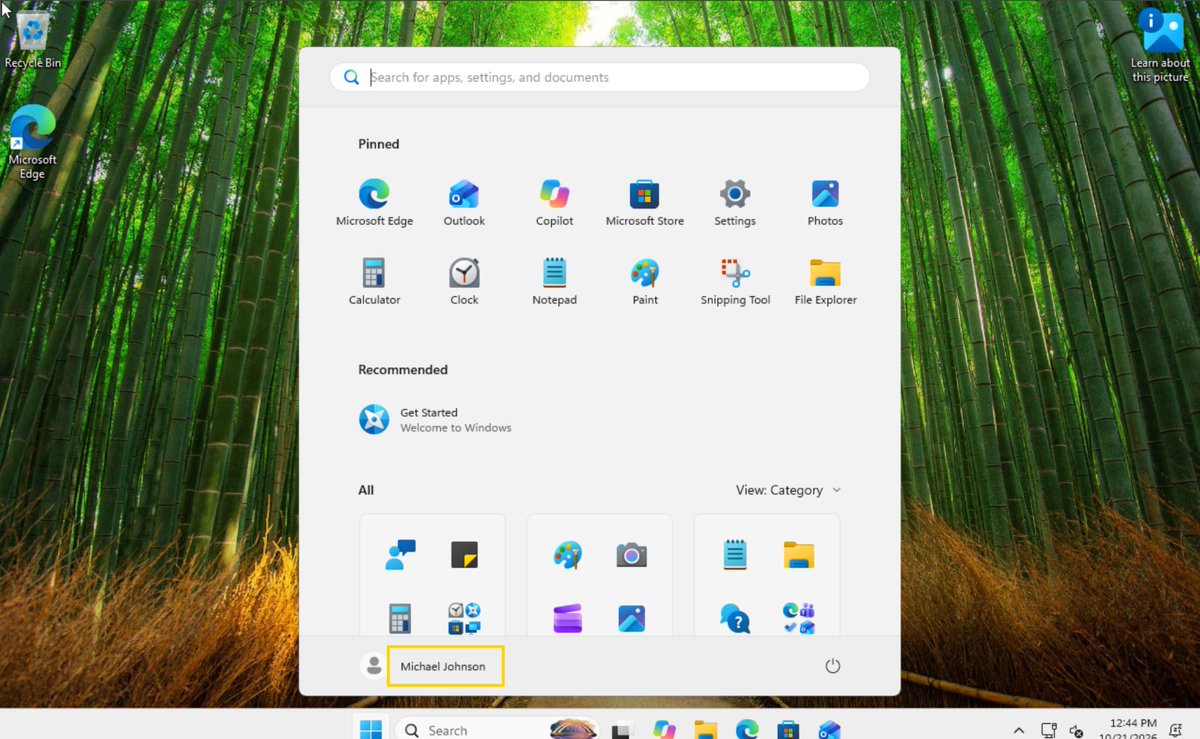
I signed in with all three accounts on my domain joined Windows 11 workstation.
Each user was required to change their initial password.
All three completed the password change and reached the desktop.
Configuration now had observable results.