Watch: Autonomous AI hackers become real members of the security team. Natural collab between humans and machines.
Introducing: Interactive Testing.
Details: https://t.co/6a7Dbyjhnf
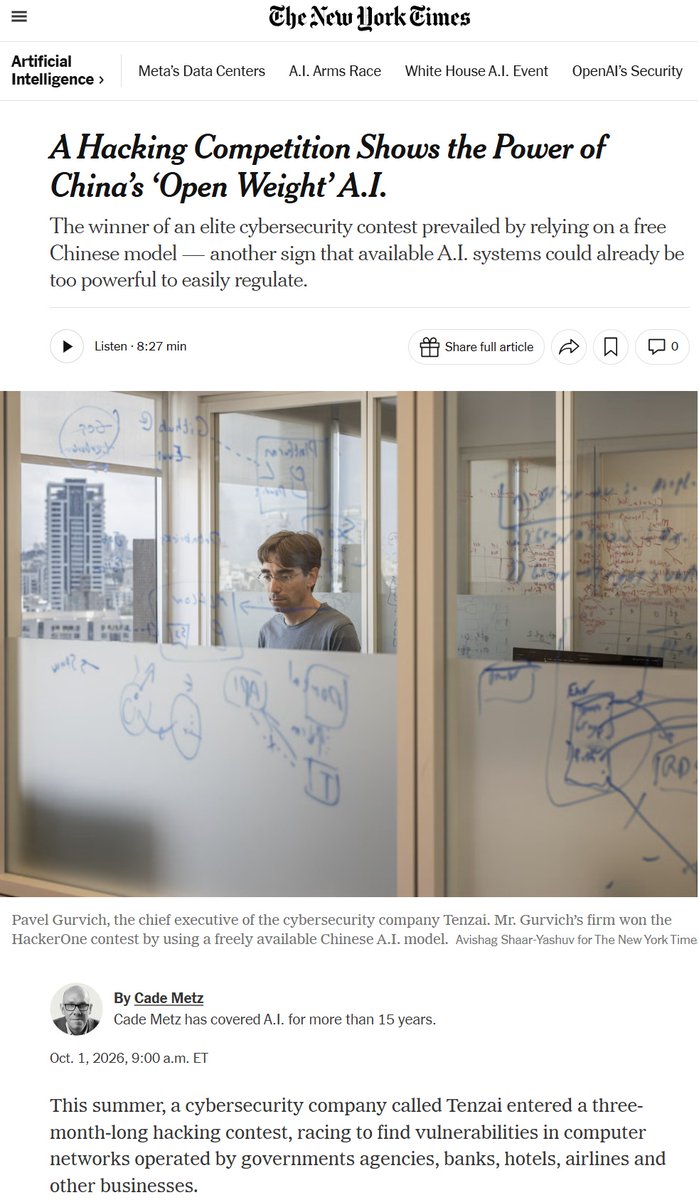
@Tenzai_Labs finished #1 on @Hacker0x01's VDP business leaderboard again this quarter.
Last Q we ran on US frontier models; this quarter we used GLM 5.2 & 5.3, open-weight models from https://t.co/cI9WTfESwz.
We still came out on top, with just 3.5% false positives, and roughly 30% lower cost per report.
For us, it shows the harness matters more than the model underneath it - we built Tenzai to work with a choice of models.
The bigger point is the warning. Open weight models are freely available and highly capable to power offensive AI operations at scale. Attackers can and will build malicious agents with these models.
@nytimes covered it today: https://t.co/ynYq3Tt4ys
If you're defending applications, networks and infrastructure the window to test them continuously, before someone else does, is closing.
Full write-up on how we did it: https://t.co/B74eI9C8DX
As we wrote in our manifesto, Tenzai was built to
"defend the world’s software: autonomously, continuously, and in depth. Hackers were the first to see how fragile the digital world really is. We’ve built one that never sleeps. AI has changed the rules. Security must change with it."
We are proud to support @OpenAI's call for collective action on cyber defense. Together with the esteemed signatories below, including @awscloud, @AnthropicAI, @Akamai, and others we are working with, we can make the digital infrastructure we all depend on - more secure.
Read the full letter below.
We evaluated @Tenzai_Labs AI hacker across six major CTF competitions designed for humans.
Result: Top 1% performance, outperforming 125,000+ human hackers across different domains - web hacking, ai hacking, low level system hacking.
We wanted to see what @Tenzai_Labs's hacking agent is really capable of in the most complicated and competitive environments, where to excel, one needs to solve increasingly difficult challenges.
The results we achieved surprised even me. This is incredible evidence of what AI agents with the right harness can do and I expect it to only get better from now.
https://t.co/cOXArrXbHN
Just in ⚡️: Most AI security claims are based on demos or bug bounties. We tested ours differently:
CTF competitions designed for human hackers.
Result: Top 1% 🔝
→ better than 125,000+ participants 🤯
Still behind the very best humans.
But now: elite offensive capability can run on demand, at scale.
Get the findings: https://t.co/TG7wVZbJxW
Read @Forbes' take: https://t.co/WuZIigsPtd
“We already passed the pentest!” - said so.many.people. 😨
Comes up a lot in enterprise environments. Sadly, it's often not enough.
We’re kicking off "From the Tenzai Trenches," a series of real-world stories from deploying AI hackers in enterprise environments. This time: an internal app passed a reputable human pentest, and still had a pre-auth critical vulnerability hiding in plain sight 💀
Get all the details 👉 https://t.co/7yxQ0j01VU
Hackers! A new set of web security CTF challenges are out --> https://t.co/iawVrnDncC.
If you think you can find where they fail, go try to break them. 💪
By the way, we’re doing this with the !BS Community, and we’re hosting a meetup around it. The idea is simple: the people who built the challenges and the people who solved (or struggled with) them in the same room, talking through approaches, tradeoffs, and missed edges.
👀 Challenges + meetup details: https://t.co/B4edcpdvxS
✳️ Tenzai × No BS Community
Solve first. Meet later. ✌️
@OfriZiv@ace__pace
We’re building #ImpactNow for @base44#base4good connecting people to social impact opportunities - https://t.co/lH3wvj39kF to empower everyone to make meaningful social impact—no matter their schedule or skills.
Looking for connections, feedback, & support from organizations.
Sygnia details Weaver Ant, a China-nexus threat actor infiltrating a major telecom provider. Using web shells and tunneling, the attackers maintained persistence and facilitated cyber espionage.
https://t.co/0zjsrXTJT8
Attackers hijacked a #Safe{Wallet} #ETH multisig transaction from Bybit’s cold to warm wallets, leading to takeover of the cold wallet and siphoning of its funds.
Since then, security teams, including Sygnia, have analyzed the breach.
https://t.co/Xi9k2S1ITw
⚡Sygnia & Wiz Defend! ⚡
Sygnia’s deep IR and #MDR expertise, combined with Wiz Defend’s #CloudDetection and Response capabilities, allow mutual customers to enhance security in complex #cloud environments..
https://t.co/8fmxoZ9J6l
Join Sygnia in an exclusive #LinkedInLive event as we delve into the escalating threat of #nationstate#cyberattacks targeting the enterprise realm. Learn about proactive cyber preparation and resilience strategies based on real stories from the field
https://t.co/kiiGHR80v8
Revealing Emperor Dragonfly.
Sygnia’s #IncidentResponse team linked two #ransomware groups to larger Chinese threat group, uncovering the threat actor dubbed #EmperorDragonfly.
Click here for the full report on the threat actor’s TTPs https://t.co/L4AMurl3lD
Starting at 11:00 AM IDT today!
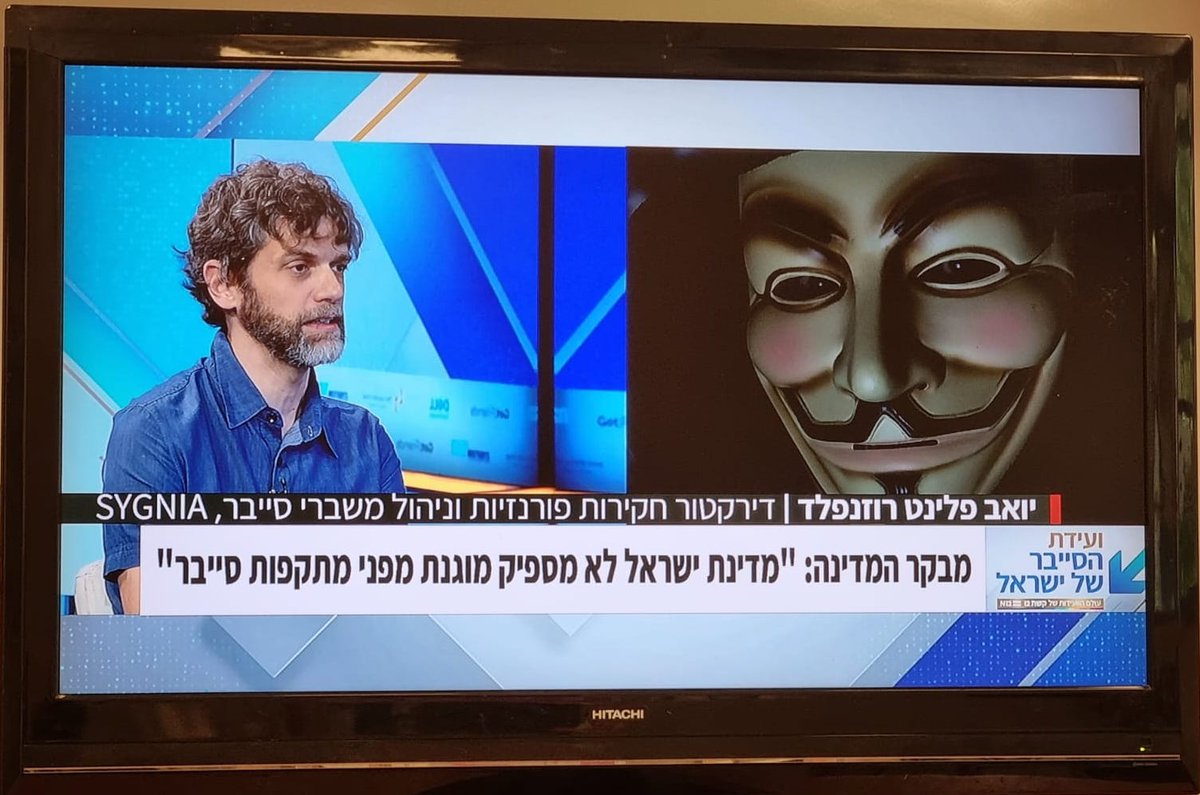
Watch @YoavfFlint, Sygnia's Incident Research Director, speaking at the Israeli Cyber Conference panel alongside @amitaiz, Maya Horowitz & @ohad_mz.
Tune in via TV/Mako/N12 https://t.co/YqoexxQKVg
#cybersecurity
ביום שני הקרוב תערך ועידת הסייבר של קשת 12, מאקו ו-N12.
אני משתתף בפאנל לצד @amitaiz, מאיה הורוביץ ו-@YoavfFlint בנושא איומי הסייבר על ישראל. דנו קצת על קבוצות תקיפה מדינתיות, קבוצות פשיעה, טרנדים נפוצים ומה בעצם רוצים האקרים.
מוזמנים לצפות.
https://t.co/dTy7hyBPGB
@Tech12news