We spent a year tracking CopperDragon’s Sparrow Framework - used by Chinese nexus APTs around the 🌍
🔎 Watering-hole attacks on government websites
🕵️ Passive backdoors and rootkit capabilities
📡 Espionage targeting major telecom operators
Read More ->
https://t.co/oWeio9fZVa
Agentic hacking frameworks are on the rise.
We tracked 2,000+ #ARTEX servers and obtained databases with full conversation logs that show exactly how the agents hacked.
It proves: Fully autonomous cybercrime is already here.
Read more 👇:
https://t.co/ZibylV402n
🖱️No clicks.
⚠️No warning.
🗣️Just a conversation.
CPR found a #ChatGPT Lockdown Mode bypass enabling silent data exfiltration from the chat.
Read more 👇:
https://t.co/umFmjE7JxP
When an AI jailbreak starts injecting ads: meet #Haiou, an example of Prompt Adware.
A glimpse into a new class of unwanted software.
Read more 👇
https://t.co/Gje90C8cYR
Tricks from the past via signed ChatGPT and Claude binaries.
🎣Fake ChatGPT and Claude projects on GitHub
📦Signed binaries sideload Yoba malware
🖼️Telegram channel image seeds a DGA
🔐DNS over HTTPS retrieves payload instructions
Full research 👇:
https://t.co/qeabCNSUzM
Infostealers are hijacking the AI train.
What’s Aokigahara after?
🎯AI sessions from Claude and ChatGPT Desktop
🔑IDE data and developer secrets
💰Browser credentials and crypto wallets
Your AI workspace is on the collection list.
Read more 👇
https://t.co/yOJYkm83UO
Our latest research exposes how AntiDetect browsers enable fraud, account takeovers, and coordinated influence operations at huge scale.
Knowledge bases, 24/7 support and MCP servers for LLM integration, the ecosystem is evolving fast.
Read more -->
https://t.co/g4vHtqwKx8
Can you detect adversarial prompts with just a quick LLM and an eye for Base64, Morse code, and similar artifacts? We show the answer is no: some plain English prompts mean one thing to a quick LLM and a completely different thing to a high-reasoning model.
https://t.co/rq4imGo9vU
What if isolated #ChatGPT sessions could secretly exchange data? 🤔
🔓A shared internal service became a covert channel between accounts, enabling attackers to execute hidden tasks and access the victim's data and connected apps.
Read more 👇
https://t.co/pagg9VOqDG
From local banking trojans to foreign 🇨🇳 operators targeting Brazil 🇧🇷.
CPR uncovered #GamblingGoblin, a Chinese-speaking actor abusing Brazilian government sites for large-scale #SEO fraud.
Read more 👇: https://t.co/uzfFajajyf
#JSCeal didn't give up its secrets willingly.
Following our #BlackHat2026 talk, we're releasing Breaking the Seal: our research on statically deobfuscating compiled, obfuscated #V8#malware.
Inside: the methodology, the open-source toolkit, and the malware capabilities recovered along the way.
https://t.co/cZpgKhzJBt
⚒️ BTR Reforged: Weaponizing Defender's Remediation Driver as a Kernel Operation Primitive
⚠ Trusted Remediation Primitives with Undocumented Internals.
🔓 15+ years. Unchanged. Unblockable.
🤔 What if an attacker learned its language? We did.
👇
https://t.co/AICs7JCI4d
#StopAndProtect blends ransomware, data theft and hands-on keyboard control.
🥷OPSEC failures reveals logs from over 6,000 victim IPs
📰Thousands of hacked WordPress websites used to lure victims and host operation infrastructure
📱 Custom stealer uses WhatsApp web and desktop to search & exfiltrate results
Read more 👇:
https://t.co/Q97dvgcg2F
0-Day Used by Lazarus in #DreamJob Campaign Against Defense Sector:
💥LPE vulnerability in Microsoft’s Afd.sys driver (CVE-2026-68820)
🧰New tools, including #Troy backdoor
🌍Compromised Roundcube servers (CVE-2025-49113) as infrastructure
Read More :
https://t.co/GDI2Ze7CRH
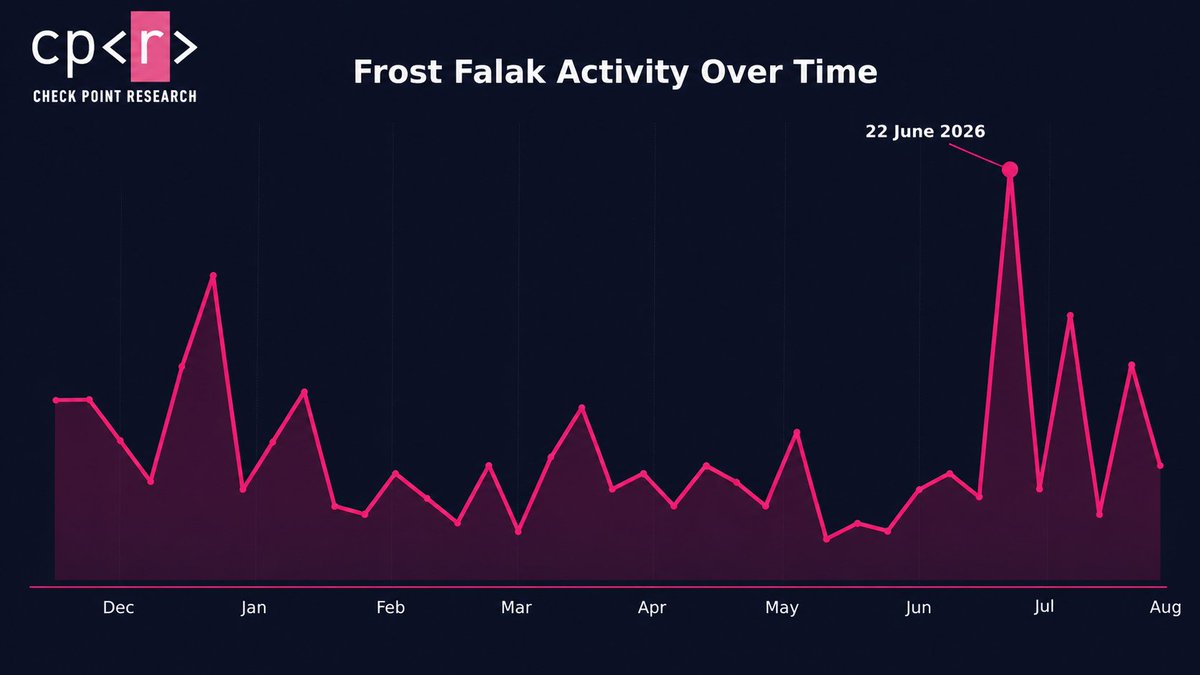
FrostFalak, a Yemen-based threat actor targeting Israeli OT networks, uses Israeli VPN exit nodes and compromised network appliances to conceal its activity while targeting construction, transportation and building management organizations.