Can you detect adversarial prompts with just a quick LLM and an eye for Base64, Morse code, and similar artifacts? We show the answer is no: some plain English prompts mean one thing to a quick LLM and a completely different thing to a high-reasoning model.
https://t.co/rq4imGo9vU
What if isolated #ChatGPT sessions could secretly exchange data? 🤔
🔓A shared internal service became a covert channel between accounts, enabling attackers to execute hidden tasks and access the victim's data and connected apps.
Read more 👇
https://t.co/pagg9VOqDG
From local banking trojans to foreign 🇨🇳 operators targeting Brazil 🇧🇷.
CPR uncovered #GamblingGoblin, a Chinese-speaking actor abusing Brazilian government sites for large-scale #SEO fraud.
Read more 👇: https://t.co/uzfFajajyf
#JSCeal didn't give up its secrets willingly.
Following our #BlackHat2026 talk, we're releasing Breaking the Seal: our research on statically deobfuscating compiled, obfuscated #V8#malware.
Inside: the methodology, the open-source toolkit, and the malware capabilities recovered along the way.
https://t.co/cZpgKhzJBt
⚒️ BTR Reforged: Weaponizing Defender's Remediation Driver as a Kernel Operation Primitive
⚠ Trusted Remediation Primitives with Undocumented Internals.
🔓 15+ years. Unchanged. Unblockable.
🤔 What if an attacker learned its language? We did.
👇
https://t.co/AICs7JCI4d
#StopAndProtect blends ransomware, data theft and hands-on keyboard control.
🥷OPSEC failures reveals logs from over 6,000 victim IPs
📰Thousands of hacked WordPress websites used to lure victims and host operation infrastructure
📱 Custom stealer uses WhatsApp web and desktop to search & exfiltrate results
Read more 👇:
https://t.co/Q97dvgcg2F
0-Day Used by Lazarus in #DreamJob Campaign Against Defense Sector:
💥LPE vulnerability in Microsoft’s Afd.sys driver (CVE-2026-68820)
🧰New tools, including #Troy backdoor
🌍Compromised Roundcube servers (CVE-2025-49113) as infrastructure
Read More :
https://t.co/GDI2Ze7CRH
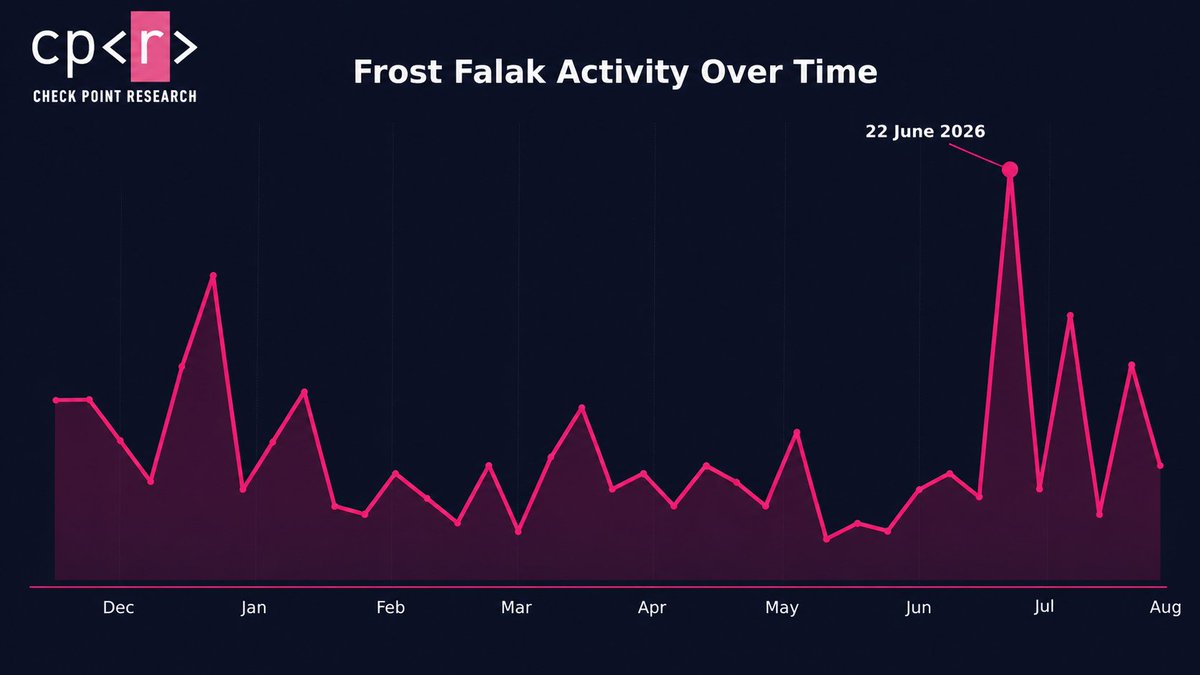
FrostFalak, a Yemen-based threat actor targeting Israeli OT networks, uses Israeli VPN exit nodes and compromised network appliances to conceal its activity while targeting construction, transportation and building management organizations.
I'm super excited to be speaking at Black Hat USA 2026, delivering my research "BTR Reforged: Weaponizing Defender's Remediation Driver as a Kernel Operation Primitive" 🤗💪
Big thanks @_CPResearch_ & @BlackHatEvents! 💯
Join me: https://t.co/nk3i07jWgj
#BHUSA#cybersecurity
🚪 Foothold via abused RMM tools already deployed
🧬 Dissection traces evolution "Cav3rn" (non-modular) ➡️ modular "Cavern"
🛠️ New IDA plugin & how-to for NativeAOT malware
🤬 Full code structure + cursing errors & typos: a human, not an AI bot
Can a website turn into ransomware on Android?
We found an AI-generated malware sample that suggests the answer is closer to "yes" than many would expect.
No exploit. No APK. No native malware.
👇
https://t.co/d4nvZ73Lyu
Fake trust is attacker infrastructure: GitHub starts, YouTube views, news websites and even "safe" VirusTotal comments to sell legitimacy.
https://t.co/fL5K6YHheR…
Lookalike Ghidra, dnSpy, and other download sites turned trusted clicks into TDS redirects. CPR found click hijacking, gated routing, and multiple malware families downstream — including an evasive, previously undocumented framework we call SessionGate.
https://t.co/HN10pG6zFN…
Iranian threat actor #NimbusManticore rapidly developed its tooling, introducing the AI-assisted MiniFast backdoor and new delivery methods including trojanized software and SEO-poisoned sites.
Read More -->
https://t.co/hPjlKBFMFt