Vice story on a service that -- incredibly -- allowed a reporter's texts to be intercepted and sent to another device. All you had to do is swear you're authorized to receive texts at the targeted number. This is nuts. https://t.co/RXXUo0ztow
A Medium piece from @lucky225 has a deep dive into how all SMS-based authentication just got owned. https://t.co/a4MD3GPHtO I agree: It's long past time to stop using SMS for anything.
‘More than just an email hack, Molson Coors continued that the incident "has caused and may continue to cause a delay or disruption to parts of the Company's business, including its brewery operations, production, and shipments."’ https://t.co/ecBQ62B8nK
On October 8 at 2 pm ET, we're participating in the Cybersecurity Awareness Month Twitter chat, co-hosted by @staysafeonline and @IDTheftCenter You should join in on the conversation. Do Your Part. #BeCyberSmart https://t.co/lJWRsV8hQy
Setting a path to #CMMC? Don’t miss this NERDIC/@PolarisMEP webinar on Current DFARS #Cybersecurity Requirements for Manufacturers & other businesses in the #DoDSupplyChain.
Tues, Sept 22, 11am.
RSVP: https://t.co/5A9W7SX4CE
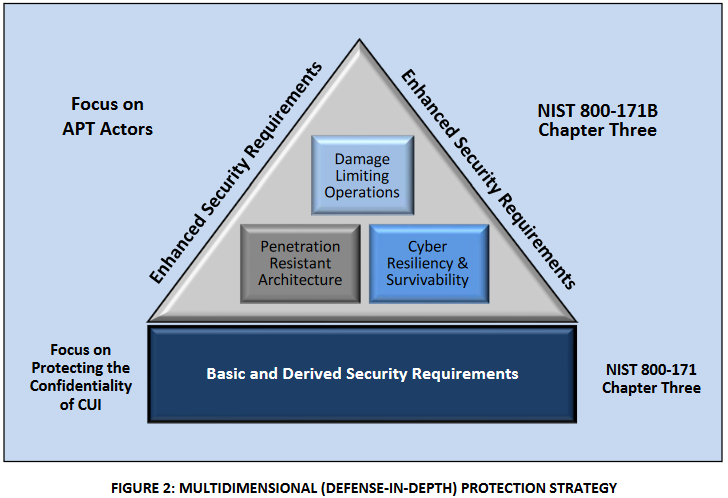
New! Draft NIST SP 800-171B: Comments due by July 19. Enhanced Security Requirements for Critical Programs and High Value Assets to protect the confidentiality of CUI from the advanced persistent threat. #Polaris_MEP#NISTCyber https://t.co/8W5HiZyDII
Breaking: NIST releases two critical cybersecurity publications. Enhanced security requirements to protect CUI in critical programs and high value assets from the Advanced Persistent Threat. https://t.co/ala7i205nV #StopTheAPT#ProtectCUI#CyberResiliency#DefenseInDepth
"The digitial infrastructure that serves the country is literally under attack"..."If you are a small business, a business that is somewhere in our defense supply chain, you are a target" -Vicki Michetti
Tune in now: NIST CUI Webcast Overview of DFARS #CUISecurity@Polaris_mep
‘You need to protect your assets’ snd that includes your information says @Polaris_mep’s Jean Lehman. #Cybersecurity is an important part of risk management for supply chain vendors.
NIST will release an update for SP 800-171 on 06-07-18, one week ahead of schedule. The update will include minor changes to selected CUI security requirements, additional references and definitions, and a new appendix that contains an expanded discussion about each requirement.