https://t.co/LM7lwBlxWe is a very fair and balanced article. They did proper research and talked to experts.
That's entirely unlike nearly all of the coverage by the media in Spain, France, Germany and the Netherlands. In the few cases we were asked for our perspective, nearly nothing we said was included. They acted as sycophants for the state and did not challenge or verify their claims.
Why is it that nearly all the western European news coverage is sycophantic?
There's a major state sponsored misinformation and smear campaign towards GrapheneOS in the Netherlands and Germany. The misinformation campaign includes unsubstantiated security claims not holding up to scrutiny to scare people away from it. They're also heavily misrepresenting who uses it overall.
These smear campaigns conflate GrapheneOS with forks and modifications of it sold by shady companies. Those usually include a device management app to remotely manage the devices of their customers as if they're employees. These are largely not GrapheneOS devices or have preinstalled malware apps.
A common tactic being used in these smear campaigns is to make unsubstantiated and outright false claims about the capabilities of forensic data extraction tools. They misrepresent how they get into devices. They want to scare people into using far less secure devices which are easier to exploit.
France, Germany, Spain and the Netherlands are becoming increasingly authoritarian surveillance states with an ongoing crackdown against privacy. It's happening throughout the whole EU and it's likely both secure devices and end-to-end encryption without backdoors are going to end up outlawed.
There are a bunch of companies based in the EU selling phones with drastically worse privacy and security than an iPhone including Jolla, Volla, Murena and iodé. These products are effectively backdoored by not providing standard privacy and security patches/protections while misleading users.
France and other EU countries are actively cracking down on legitimate privacy and security projects while supporting unsafe products within their control. These products make it far easier to remotely exploit devices and also to bypass encryption to extract data. They're phony privacy products.
Each of the companies we've listed have participated in the misinformation and smear campaigns against GrapheneOS. Jolla spent years working closely with Putin's regime. Volla, Murena and iodé are building an EU Play Integrity API. None provides the crucial standard privacy patches/protections.
Murena is directly assisting with state anti-privacy campaigns smearing highly private and secure devices as mainly benefiting criminals. They've repeatedly falsely claimed GrapheneOS is mainly used by criminals. Here are 2 of many examples:
https://t.co/tknnMLauok
https://t.co/QmrgmbRyVa
GrapheneOS, end-to-end encrypted messaging apps, Monero and other projects are being targeted with state and corporate propaganda and anti-privacy laws. Meanwhile, the same governments heavily fund and support phony privacy projects clearly downgrading privacy and security compared to an iPhone.
GrapheneOS is only an initial target for these state actors and their sycophants in corporate news organizations. Apple heavily works on protecting users against exploits too. It would be much harder to convince the public that an iPhone is for criminals so they're starting with open source.
@RobustProducts@GrapheneOS Yes. GrapheneOS App Store is for the mostly for updating OS app components out-of-band (meaning without the need to update the entire operating system). There are some app mirrors there too but not many.
@MarauderMag@GrapheneOS It did have a duplicate of the GrapheneOS web site, but the links for OS releases were 404'd or were hyperlinking straight to us. A more advanced threat actor could have filtered that for certain user demographics though. Don't think anything cool like that has came around though
@MarauderMag@GrapheneOS It wasn't distributing, to our current knowledge, a fake GrapheneOS, the link we shown was what appeared to be a strain of malware for MacOS devices.
I'm doing the thing until I can convince people that focusing on whether or not AI is being used in intrusions is a waste of time. What will be figured out is that virtually every cyber threat is using AI, because AI these days is as generally available as the internet. Imagine back when the requirement was "threats using the internet." AI isn't an emerging threat anymore. It's the norm.
@Gi7w0rm AI-generated PoC web sites are the worst. You have one page about a vulnerability and it's designed like it's trying to sell me a sketchy resold VPS, give me a break!
@CryptoChrisG Simple answer is a threat actor that isn't going to be held accountable will not need to give a shit about what privacy coins to use. If it's a North Korea op again then what could anyone do about it? They wouldn't arrest their own people.
All life is a limited span of time that once it is spent, you can NEVER get that time back. When you work for someone you are sacrificing a part of that sacred lifetime. You should only work where you are compensated and respected like they understand that.
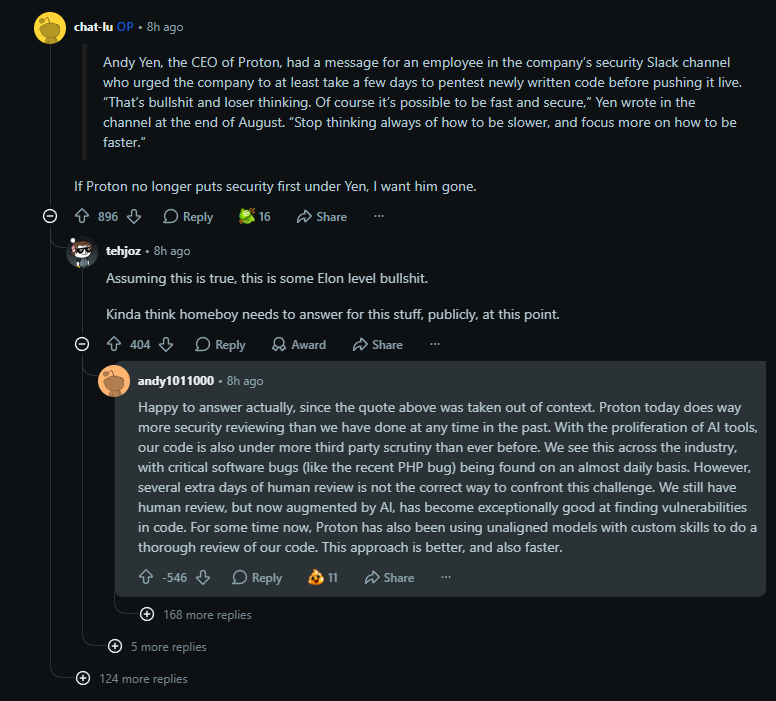
I seriously hate when corporates think it is okay to refer to anything about their teams and workers with insulting language like "stupid" and "losers". He didn't seem to address that afterward too. A product is nothing without the people who work on it, you must respect them.
New: you think you know Proton, but you really don't.
I spoke to 8 current employees, got Slack chats, meeting audio, and an AI manifesto written by its CTO.
“That’s bullshit and loser thinking,” Yen wrote. “Stop thinking always of how to be slower, and focus more on how to be faster.”
CEO Andy Yen critiques AI in public. But inside, he is pushing everyone to use AI, even those with security concerns https://t.co/4FG6haZ5Vd
You are not being a firebrand, outspoken, misunderstood or 'just being blunt' by having such an insulting tone to your own workers. You only make prospective employees not want to be supervised by you.
If there is a statement to come of this, that should be the first to address.