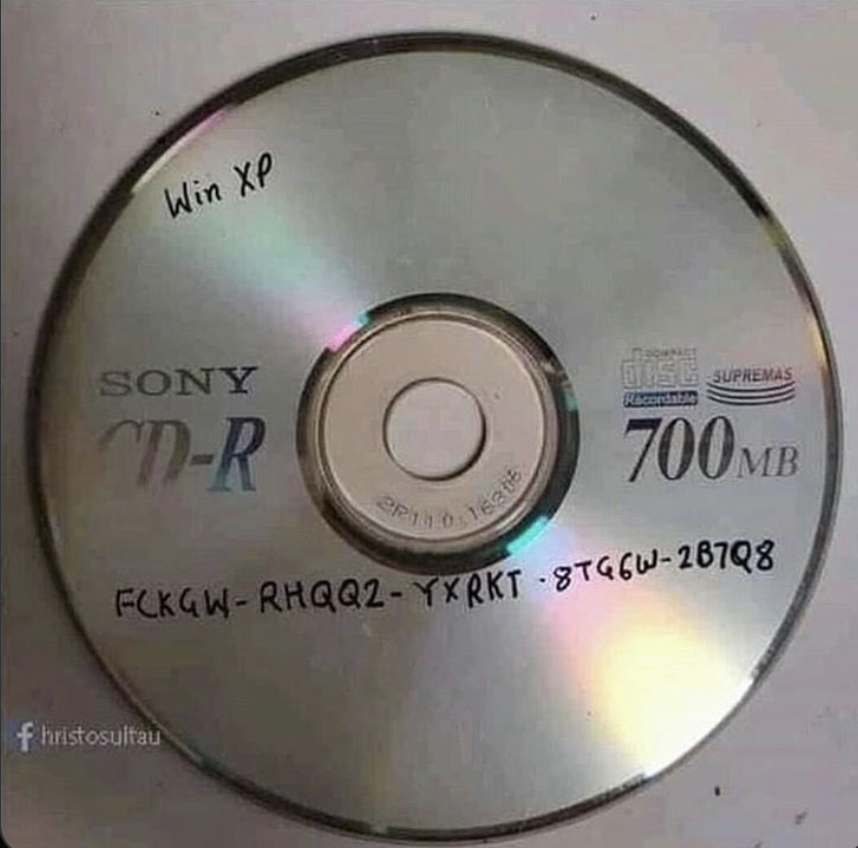
This is the story of FCKGW-RHQQ2-YXRKT-8TG6W-2B7Q8.
I was the primary author of Windows Product Activation on the operating systems side. Not the key math – those were the ACTUALLY smart guys with heads so big that they bumped the doorjamb on the way into your office. I just did the protection of and integration into the operating system.
As you likely recall, Product Activation required that you have a key, and you’d have to activate it online or over the phone.
But Microsoft had large corporate customers, think hundreds of thousands of PCs, and those customers did not want to have to activate every offline PC. So in that case, you would be given special “Volume Media” that could be unlocked with a Volume key.
That way, a volume key could never unlock your retail CD.
Now, to know what media you have, I inspect the disc image. And the Volume licensing media contained a special binary blob that I made. It was about 10MB of data, entropy stripped, hard to duplicate on Usenet at the time. And it was only present on the Volume media.
That secret data, which I hashed and checked to match to the key, was Microsoft Bob. I took their disc data and compressed and encrypted it several times. Rest assured it’s encrypted and even in the AI age no one has extracted it yet. I really just needed random data, so I started with a precompressed binary image because, secretly, I was young and didn’t know if I could trust CryptGenRand
And so, if you ever tried the FCKGW key on a regular XP CD, it wouldn’t work, because you didn’t have Bob buried in your bits.
But if you had the means in 1995 to download large ISO binaries or copy CDs, all it took was the key and a copy of the disc.
The key itself still had to pass the product-key validation math (the part I didn’t own). Once it did, WPA simply skipped the rest of the process. That combination—valid VLK + matching volume media—is what made the install look fully legitimate, including early Windows Update checks.
How it leaked
RTM went to manufacturing on 24 August 2001. Retail launch was 25 October. Roughly five weeks before launch the warez group Devils0wn (often written “Devil’s Own”) posted a complete, non-beta “Windows XP Pro Corporate” ISO together with the FCKGW key. That ISO was the volume media. Pirates then started baking the key into images or just writing it on the CD with a Sharpie. The famous photo of the marked-up disc is from that scene.
The most plausible source is an OEM or hardware partner that received final media early so they could ship PCs on launch day. Dell is the name that comes up most often; Intel has also been mentioned because of later source dumps. There were very few organizations that actually possessed a VLK that early, which is why the timing points at a partner rather than a random corporate customer. But I do not know. Presumably someone does.
Aftermath
We started blacklisting the Product IDs that belonged to the leaked keys (FCKGW decoded to one of the 640-range PIDs we later treated as toxic) in SP1. SP2 and Windows Genuine Advantage made the check more aggressive and also started blocking updates for those installs. Other, un-leaked VLKs continued to work on volume media for years; Microsoft did not kill the entire volume-licensing path, just the ones that had escaped.
So the design decision was “give trusted big customers a convenient offline path.” The operational failure was that the media and one of those keys left the building before the product even reached stores. Once both pieces were public, WPA’s hardware-binding never got a chance to run.
These Days
If you’re curious about what I’m doing today, check out Task Manager TMOG at https://t.co/OZcq1axGTb where you can download the Free version! It runs fully native on Windows, Mac, and Linux!
Puas banget bacanya.
Makasih Kak sudah mewakili.
Penutupnya GONG Banget!
"Jujurly Maudy Ayunda, yang kamu lakukan itu, jahat.
Minimal, stupid.
Warga gak ngarep kamu berjibaku ngadepin karhutla di lapangan kayak Andrew Kawaleit. Warga juga gak ngarep kamu bisa nulis kolom kritis di Kompas kayak Reza Rahadian. Warga cuma ngarep kamu balas hutang budi kamu ke para pembayar pajak. Dengan mengamplifikasi jeritan mereka di platform kamu.
Dan itulah serendah-rendahnya iman seorang influencer."
Tanggal 9 September lalu, saya mengajukan lagi permintaan informasi terkait sekolah Gibran di UTS Inserach, Sydney, Australia. Permintaan resmi saya daftarkan online, dan dikonfirmasi UTS melalui potongan email di atas.
Saya meminta seluruh data sekolah Gibran di sana. Kapan masuknya? Program apa? Apakah selesai? Kapan lulusnya? Bagaimana nilainya? Dst.
Apa jawaban UTS, kita tunggu saja.
Kalau tidak diberikan juga, saya mempertimbangkan menggugat Keterbukaan Informasi Publik melalui kantor hukum saya INTEGRITY Lawyers yang punya cabang di Sydney, Australia.
Karena saya sendiri punya izin praktik hukum (Solicitor) di Australia, selain advokat di Indonesia.
Keep on fighting for the better Indonesia.
Salam Integritas!
Maaf, teman2. Saya harus berkata kasar. Soalnya ini sudah keterlaluan.
Kepala SPPG menyalahkan guru akibat tidak mencicipi MBG? Bangsat ya anda! SOP kalian adalah mencicipi makanan itu sebelum dikirim ke sekolah!
Kalo kalian keracunan, ya itu SOP kalian untuk tidak mendistribusikan makan tersebut. Kenapa jadi guru? Tai!
https://t.co/C2gT0VrXqN
Kalo guru yang keracunan, terus gak apa-apa gitu? Kontol! Kalian dengan seenaknya menikmati uang rakyat, tapi tidak ada tanggung jawab sama sekali ketika kasus keracunan terjadi!
Alhamdulillah, akhirnya status Palestina resmi diakui sebagai anggota penuh PBB, bukan lagi non-state member seperti selama ini. Selamat untuk rakyat Palestina !!!
Semenjak denger Ustadz felix di podcast ini bener-bener terngiang-ngiang setiap aku kerja🥹
Beliau lagi menjelaskan konsep rezeki, pekerjaan, dan rasa syukur🥹
I resigned from Anthropic today. I spent the last three years doing pretraining research at both OpenAI and Anthropic. Neither company is acting responsibly. They are racing straight to self-improving superintelligence and gambling with our lives. More thoughts below.
magnet:?xt=urn:btih:13ffbf49431b19b85fdee41beb565ed5beb611aa&dn=d6993ad34309.tar.zst.age
sha256 40c686202840b8af0325fcac54e2eb43f4f5a736bd9818cbbea78ce1226a5d7f
encrypted archive, please help safeguard, decryption key to be published
Main2 pulpen saat rapat dengan kepala negara jelas akan ditafsirkan sbg kebosanan, ketidakpedulian, sikap menyepelekan, nggak respek.
Si karbitan ini apa nggak ngeh kalau dlm dunia diplomasi, setiap gerak-gerik delegasi dipantau dan dianggap membawa pesan dan makna.
Apalagi ini sama Putin..
Guys, ini bukan fiksi ilmiah lagi.
Juli kemarin, Taiwan kena serangan siber yang 100% dijalanin AI,tanpa manusia pencet tombol.
8 agen AI kerja bareng 4 hari nonstop, mutusin sendiri mau nyerang ke mana, nyoba metode baru kalau kena blokir.
Hasilnya: 21 sistem pemerintah dipetain, 85 akun jebol, 2.500 data personel raib.
Ini yang di security research disebut "agentic threat", ancaman yang nggak nunggu perintah, dia belajar sendiri di lapangan kayak makhluk hidup nyari celah. Deterrence lama (mendeteksi pola serangan manusia) jadi kurang mempan karena musuhnya beradaptasi real-time.
PR buat kita: institusi cyber security nasional wajib mulai stress-test sistem lawan AI otonom, bukan cuma hacker manusia.
Kalau nggak, kita bakal telat sadar pas datanya udah raib duluan.
#intinyadeh viral video yg nunjukin bbrp anggota TNI nyebrang lewat jalur Busway dan manjat utk masuk ke Halte Bundaran HI, tanpa lewat gate pembayaran.
Dipertanyakan knp harus lewat situ, melanggar & membahayakan, padahal gak jauh ada zebra cross, tempat nyebrang semestinya.