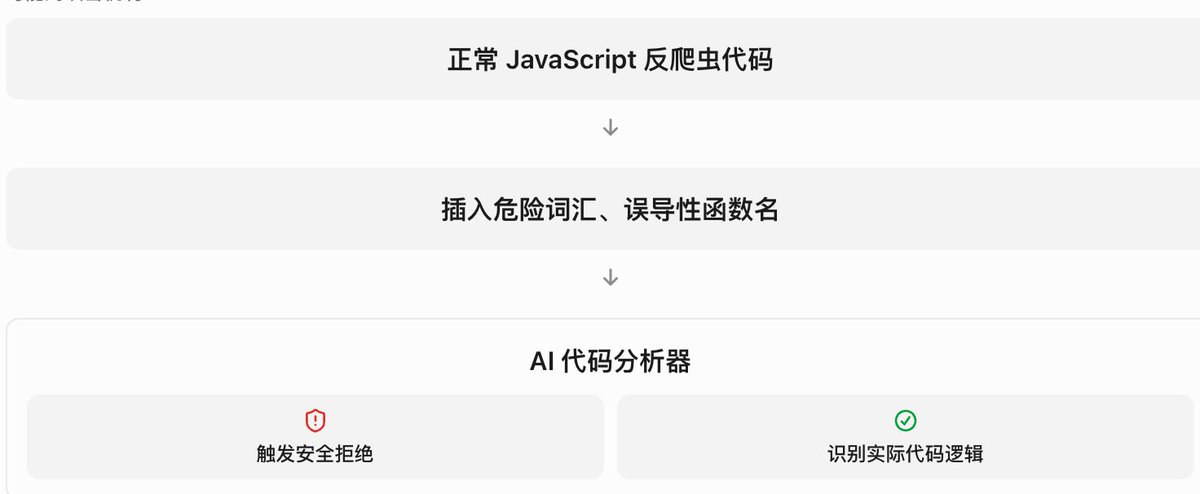
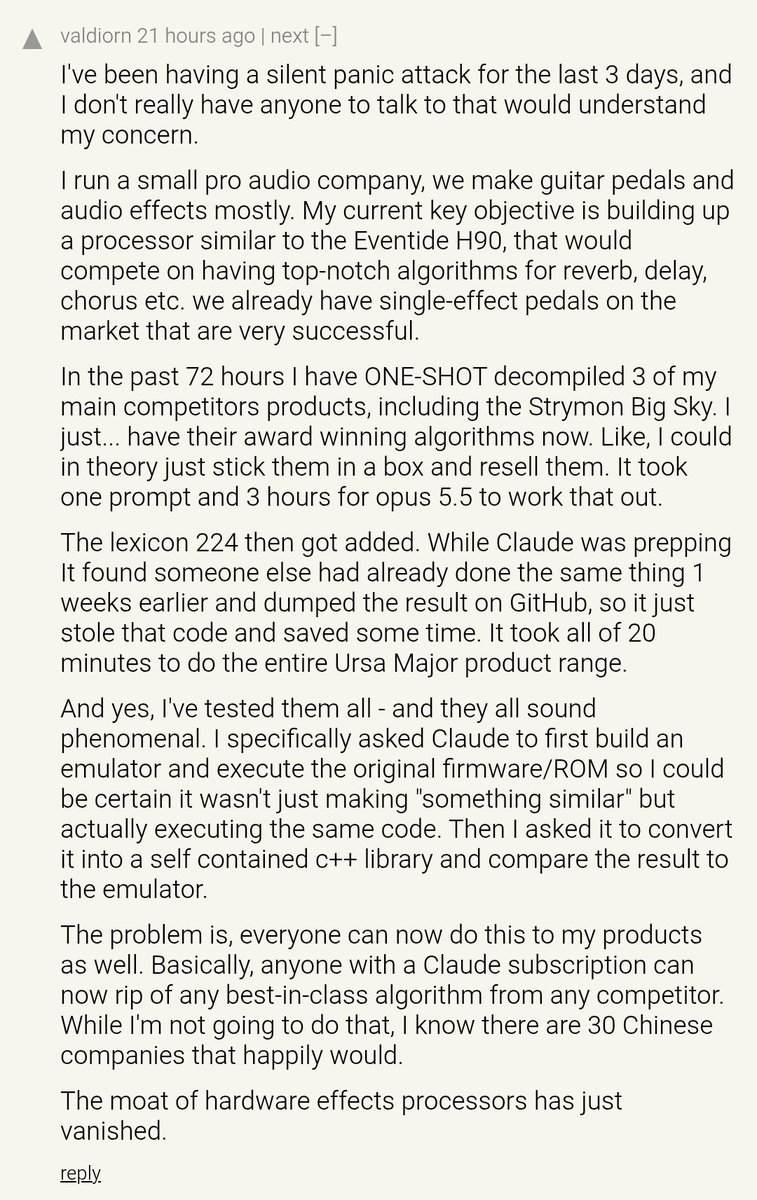
Reality of our days:
1. I am sitting on a set of vulns (4+) that allows me to remotely take over a consumer home automation device I have (3+ diff ways).
2. The vendor doesn't only serve consumers, but also critical infra (announced partnerships include pharma manufacturing plants, airport logistics, hospitals, etc) across various locations in Europe and the US (not the same product line, ofc, so maybe moot).
3. Claude and Astra refuse to help me explore even my own device, so now I'm using Chinese hosted models for investigating.
4. The vendor (with a revenue of $0.75B) does not maintain any security disclosure practice whatsoever, nor does respond to emails.
So, to recap, I need to outsource vulnerability hunting of (potentially, I don't know) critical western infrastructure to Chinese models, because the western models refuse; and the vendor doesn't give a shit. Fun timeline.
PS: The vendor is Swiss.
Was literally explaining the, "society falls when old men don't plant trees they will never sit under" to my neighbor (boomer)
He said he didn't get it and why would he plant trees if won't be around to see them
@petejkim Someone once explained to me that you aren’t supposed to use jira as it ships out of the box, your task is to tune it with configs and he tuned it perfectly and it worked great and I never complained about jira again. It just ships w everything default on.
We acknowledge that no one has the bandwidth for this, but if it helps:
-It’s ‘sleight of hand’
-It’s ‘bated breath’
-It’s ‘lo and behold’
-It's 'buck naked'
-It’s ‘brass tacks’
-It’s ‘free rein’
-It’s ‘toe the line'
Not just PHP. Node.js has also announced security releases for October 21, with HIGH-severity vulnerabilities affecting its 26.x, 24.x and 22.x release lines.
If you run either stack in production, keep an eye on official advisories and apply patches promptly.
Security maintenance doesn't stop at your application code. Your runtime matters too.
Node.js advisory: https://t.co/rmgw4sOnqU
In the last 24 hours:
1. iPhone 11 through 16 are apparently vulnerable to remote attacks.
2. SSL certificates are broken until browsers remove eMudhra CA.
3. PHP >9 vulnerability CVE published (tomorrow).
The world is about to witness things that have never been seen before.
Full details of a remotely exploitable vulnerability in the core engine of *all* PHP versions will be released tomorrow, October 21st. If your organization has internet facing PHP applications then you need to be ready to patch the minute the update is released or *strongly* consider taking the application offline until you can:
https://t.co/hpdTOdvSsQ
@ShaughnCasey@AlexBerenson Absolutely thank you for articulating this. It’s super stressful. I also binged MadMen during Covid and felt the same way re Don’s alcoholism. One hour is one thing but many hours is a diff beast.
"AI agent deleted entire upcoming season of Swedish reality competition show called “The Challenge Sverige,” just weeks before the premiere," per FUTURISM
@DoozerDiffuser I’ve also encountered this and what helps is negotiating who will edit what on each turn and be very communicative when you do, I think it has to do with the way it caches files to read/ write. I think the pissiness just comes from not managing expectations