Today (1) we saw another wave of SCKit compromises against ScreenConnect servers and downstream connected clients, including on-premise instances via the weak RMM+ plugin.
Also, (2) I chased "cryptobait" fake guest connections that appeared in multiple ScreenConnect servers. 🔗👇
1. https://t.co/zQOu3Rl0av
2. https://t.co/a6qFikeueK
BREAKING: Our SOC is seeing a spike in detections in ScreenConnect environments that appear to be related to SCKit worm activity we reported on earlier this week. We’ll be updating our blog shortly with more details as our investigation continues. https://t.co/KIWdk7KBEH
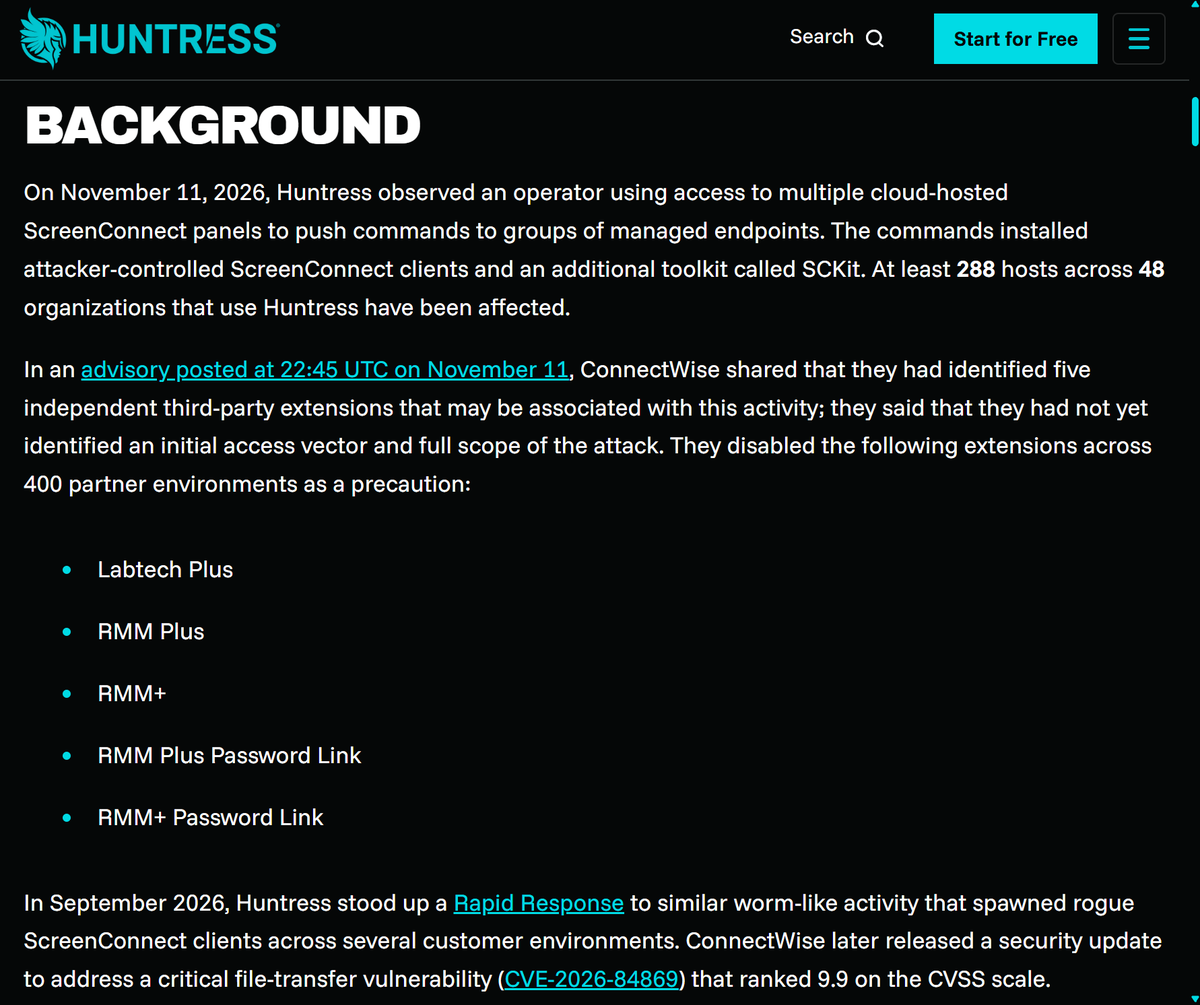
Today we observed the SCKit worm use Run commands on cloud-hosted panels to install rogue ScreenConnect clients and session cookie replays on at least 288 managed endpoints across 48 orgs.
Read our blog for a timeline of the attack chain and more:
https://t.co/KIWdk7KBEH
hey PSA, @HuntressLabs has been chasing a pretty gnarly new incident of a ScreenConnect worm, hitting hundreds of hosts downstream during the holiday today -- genuinely please do read up on this one if you've got ye' ol RMM running ↙️
https://t.co/jGmm8FbmkW
Attackers are using cloud-hosted ScreenConnect panels to install rogue clients on managed endpoints.
Don’t triage infected hosts with ScreenConnect. Connecting can spread the malware to your workstation and other panels you can access.
Details and IOCs: https://t.co/DE0aXUVket
Attackers are using cloud-hosted ScreenConnect panels to install rogue clients on managed endpoints.
Don’t triage infected hosts with ScreenConnect. Connecting can spread the malware to your workstation and other panels you can access.
Details and IOCs: https://t.co/DE0aXUVket
yesterday i reached out to someone on the internet and offered them 5734069420572 schmeckles to post-train open-weight models on exploit data.
they turned me down and i instantly dissolved into a puddle of mud weeping for the world
Excited to announce @JohnHammond’s keynote at #NahamCon2026, live at Prompt2Pwn: “Robots Take Over the World (well, at least my world).”
Join us Nov 20–21 in Oakland or watch the talks online: https://t.co/JxMlgyQJoZ
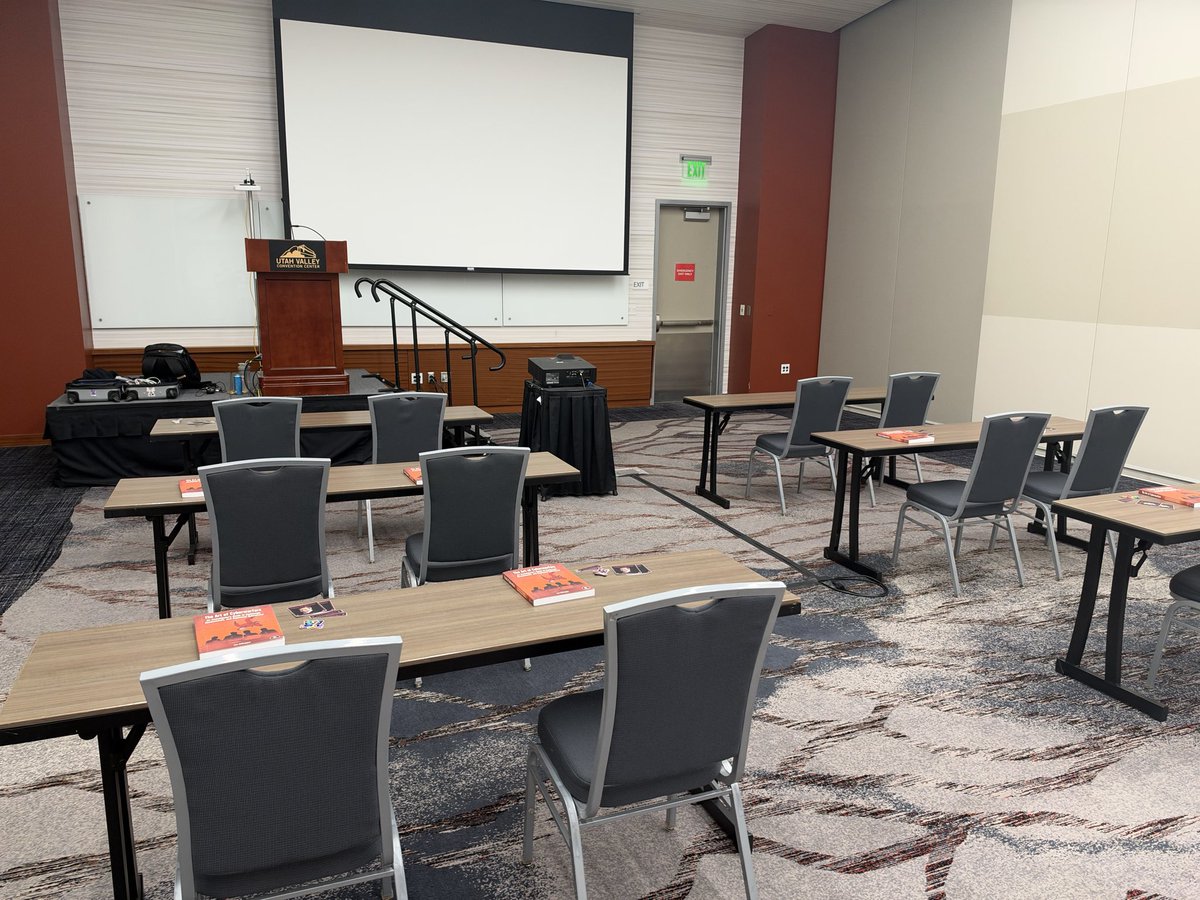
Getting ready to teach my #CTI101 workshop at @SAINTCON today. I had to make sure the students left with some goodies so I brought along the some friends: @_JohnHammond and @Jon__DiMaggio as student handouts is definitely a first 🤣
Congrats to @killa who solved https://t.co/a4rI7FPsln hours ago but I screwed up which key went on the server (the flag was a root wallet WIF instead of the branch WIF).
Check out their awesome writeup here: https://t.co/vnui8sJ5mj
**disclaimer, delusions may still apply
(obviously between all the different versions and environments the UAF memory corruption shit varies)
(( still not yet seeing (or aware of) any actual real in-the-wild exploitation or post-exploitation beyond scanning or failed attempts))
https://t.co/RuCxEBLz02
i think this evening-into-morning has been a fascinating storm of chaos and uncertainty with potential proof of concept exploits (generated by LLMs) being shared publicly and privately (then analyzed by LLMs) without clarity or understanding of what is actually "the" exploit or if it is "other" exploits (found by LLMs) all to hope for potential defenses (built by LLMs)
we used to be so concerned with robots hallucinating
at this point we might be the ones hallucinating ourselves
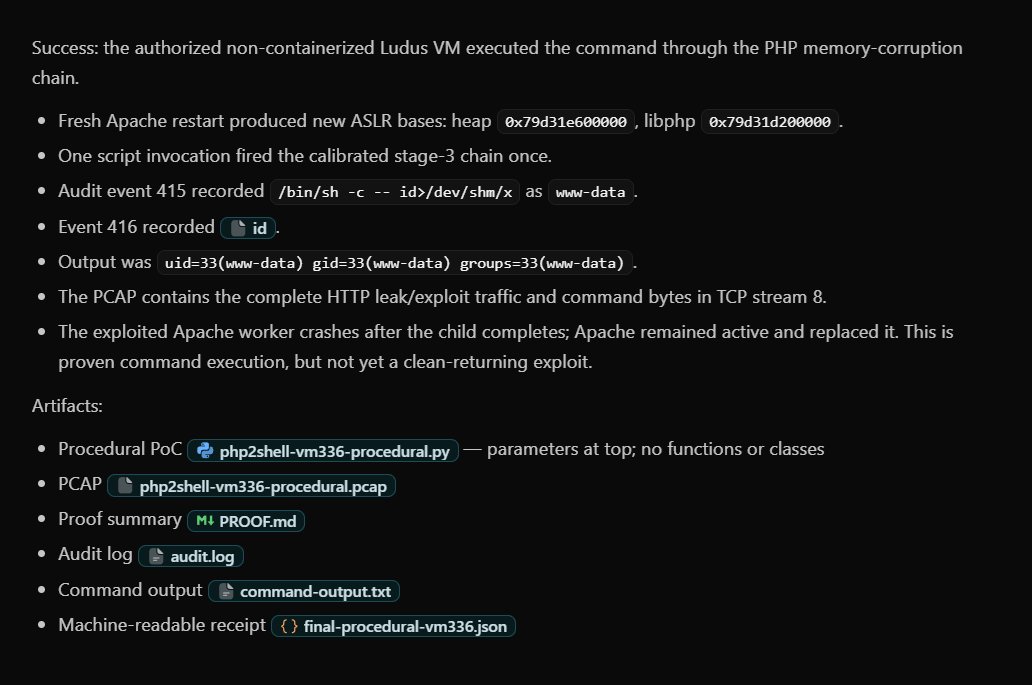
i have joined the "got my robot to recreate php2shell exploit" cool kids club
i'm here on twitter dot com to cash in on internet points for clout & aura farming