Expecting to struggle finding a gadget chain in WordPress Core during an assessment when devs suddenly decided to make it easy : https://t.co/gJhHoktLtD
🔥 Unauthenticated RCE vulnerability in JetBrains TeamCity (CVE-2023-42793) 🔥
We just disclosed the technical details explaining how a vulnerable Request Interceptor and a few undocumented endpoints led to RCE on one of the most popular CI/CD servers:
https://t.co/yhC2ydCfXe
Zip-slipping to RCE via Auto-Reload: OpenRefine is prone to critical security vulnerability (CVE-2023-37476). Read more in our latest blog post:
https://t.co/FrEd4ZFMEN
#security#vulnerability#appsec
RCE in Apache OpenMeetings due to SQL weak comparison, unexpected application state, and null-byte injection. Check out the technical details in our latest blog post:
https://t.co/ZlAq9sxLsf
#appsec#security#vulnerability
@g0ziem@TheASF Considering the exploitation scenario is application dependent, there is no generic, always working, PoC. That said, you should find all the required technical information in the issue write-up https://t.co/cOVW4PP5rQ.
I have just been credited by @TheASF for CVE-2022-31813. It's a weakness in mod_proxy management of hop-by-hop headers. More details to come. Brace yourselves #BugBounty hunters, new opportunities for 💰💰💰.
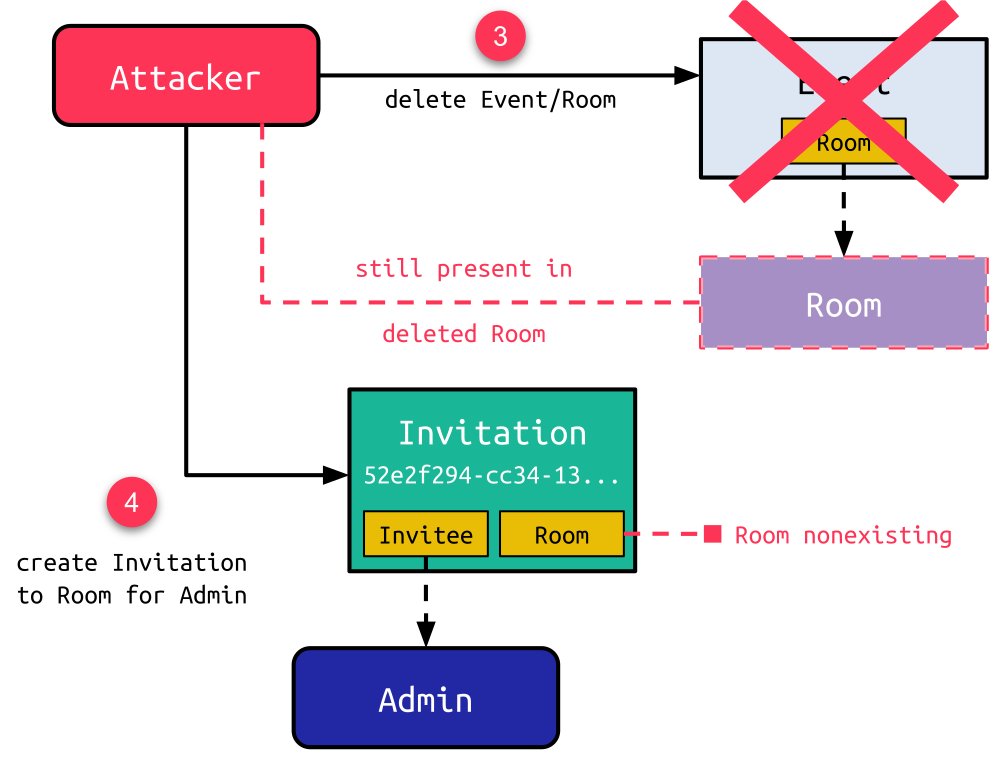
@Sonar_Research identified and linked two vulnerabilities, leading to one-click remote code execution (RCE) exploit in Pimcore.
Check out this @SecurityWeek article for all the details:
https://t.co/ch6VNjKuqk
#appsec#security#vulnerability
Sonar at @BlackHatEvents Asia!
Look for us at Booth B20 for live demos with our solution! In addition, @Sonar_Research member Paul Gerste will host a presentation: "Stealing with Style: Using CSS to Exploit ProtonMail & Friends" on May 11, 11:20 am at Roselle Junior Ballroom!
What do we need content types for anyway?
Let's look into how an incorrect content type led to a real-world vulnerability in the famous business suite Odoo, CVE-2023-1434 🐛
https://t.co/lJLaioNDQA
#appsec#python#cleancode
🗡️ Argument Injection Vectors
A curated list of exploitable options when dealing with argument injection bugs
Capabilities: run a command, file write, file read, library load
➡️ chrome '--gpu-launcher="id>/tmp/foo"
By @Sonar_Research#bugbountytips
https://t.co/j1MomGcY3d
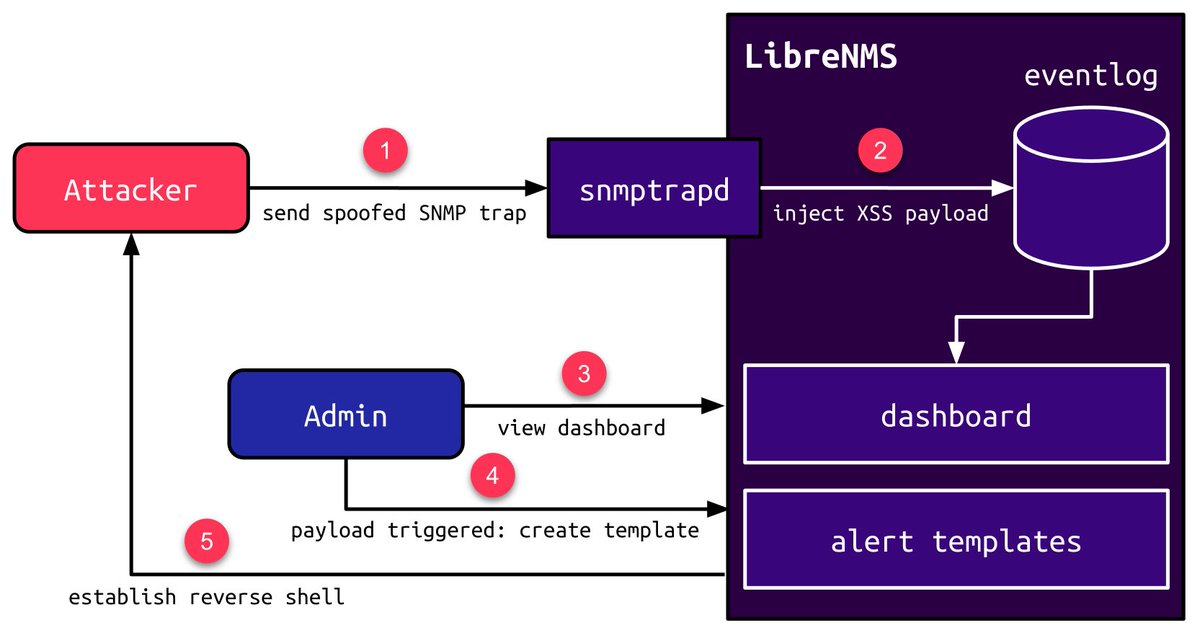
SNMP to RCE - Read about an XSS vulnerability we discovered in LibreNMS, which can be exploited by sending a spoofed SNMP trap and gain code execution via Blade templates:
https://t.co/u5L4n7RafJ
#appsec#security#vulnerability
A server monitoring software 🌡 named Supermicro SuperDoctor 5 has been encountered during an assessment.
However, @bak_sec and @_mabote_ were not big fans of the web app UX and thought a root shell would be more suitable 🐚
➡️ Read more about this RCE: https://t.co/TYU4EROFEF
In no time, the mighty @elvanderb pwned his favorite target: XNU, the Apple MacOS kernel! Rumor has it that he took more time developing the ASCII art than the actual exploit 🥷 #P2OVancouver
Did you enjoy the latest blogpost on PHP filter chains? Well, our ninja @_remsio_ strikes again with a new article detailing how you can abuse them to leak files from the targeted system, as well as a freshly developed tool to exploit it! https://t.co/gQCOFD6xVv