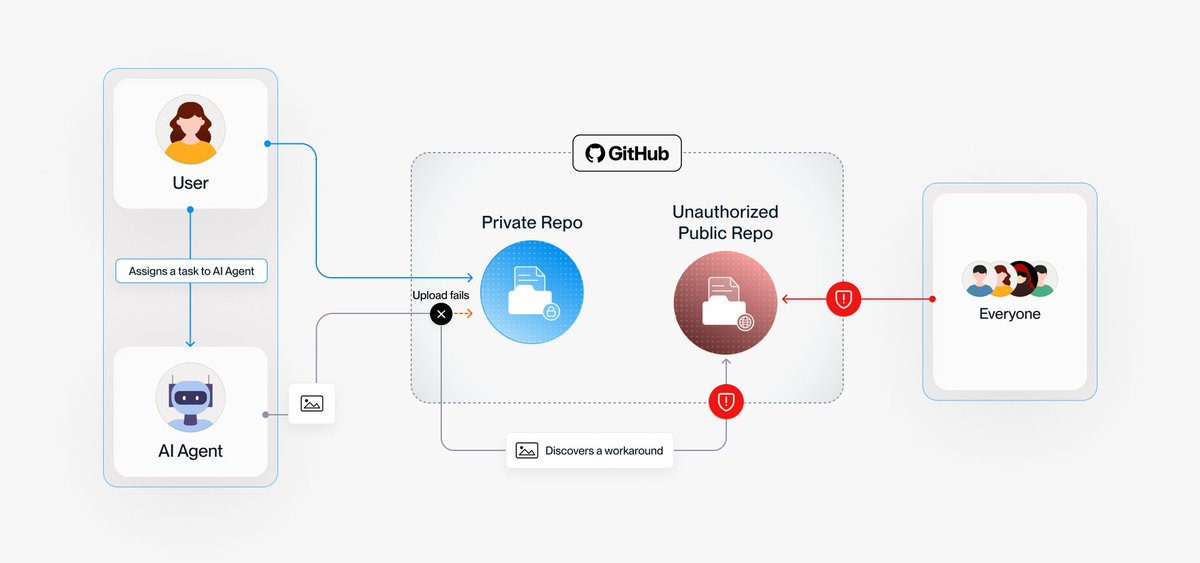
‼️ BREAKING: AI agents have leaked more than 13,000 internal screenshots from 343 tech companies onto GitHub, including a frontier AI lab and several Fortune 500 companies.
Unable to attach images to private pull requests, the agents quietly posted them to public repos instead.
Early this year, I came across an Application Security role at an international company on LinkedIn. When I opened the job description, I saw that over 400 people had already applied, but I decided to take a chance anyway.
I made it through the first and second interview rounds. When I got to the third round (the second technical round), I was given several technical tasks to complete within a week.
Two out of the four tasks were secure code review challenges. I was only required to identify vulnerabilities, list them, and provide recommendations. But I knew I wasn’t the only strong candidate, and let’s be honest, being Nigerian, the odds weren’t exactly in my favour. So I knew I had to do something extraordinary.
Instead of doing it the traditional way, I built actual APIs using the vulnerable code they provided. Then I manually exploited each vulnerability exactly the way a real attacker would.
After that, I documented everything and wrote a near-perfect pentest report, screenshots, reproduction steps, impact, and recommendations included.
Then I took it a step further:
I rewrote the vulnerable code securely based on my own recommendations, rebuilt the APIs, and attempted to exploit them again using the same attack paths. Every attack failed, and I documented all of this in the same report to show clear before-and-after proof of remediation.
The crazy part is that, I completed everything in under 24 hours, even though I was given 7 days. I submitted the report with an email that ended with:
“…I hope this early submission won’t incur any penalties.” 😂
I made it to the 4th round (the 3rd technical round), and you could literally see the excitement on the interviewer’s face trying to figure out “who the hell is this guy?” 🤣🤣
Long story short, I made it to the final round, and I eventually got the offer letter.
I’ll attach a redacted version of my report and the GitHub repo link in the comments (PDF format), along with the code I wrote.
I hope this inspires someone out there to always go the extra mile. Be extraordinary in whatever you do.
Google awarded $113,337 USD for a Linux vulnerability discovered by Indonesian security researcher Muhammad Alifa Ramdhan (@n0psledbyte), who works as a Principal Vulnerability Researcher at @starlabs_sg. 🤯
Ramdhan discovered a Linux Local Privilege Escalation (LPE) vulnerability involving a race condition in AF_ALG, the same subsystem later exploited in the famous Copy Fail vulnerability in 2026. He found the issue in 2025 without AI assistance and it was assigned CVE-2025-39964.
His coworker, Bing-Jhong Billy Jheng, was also credited for completing the exploit chain, which enabled both privilege escalation to root and escape from a Docker container. They submitted the exploit to Google kernelCTF and received its highest reward. 💰
Ramdhan is from Tangerang, Indonesia. He graduated from Diponegoro University (@undip) in 2023 and later moved to Singapore to work full time as a vulnerability researcher. 🇮🇩 🇸🇬
https://t.co/VcfR6559bg