Persistent Remote DoS via Integer Underflow in Wire iOS
CVE-2026-35049: One message from a chat participant could crash Wire persistently without interaction. Recovery required reinstalling, erasing local message history. Fixed in 4.16.0.
Advisory: https://t.co/JjeicXQMUm
Our own Jesse D’Aguanno (@0x30n) delivered his talk “Can’t Touch This: Attacking Fingerprint Systems from Sensor to OS” at Black Hat USA this week!
Jesse detailed his journey researching and attacking fingerprint authentication across Linux, Windows, and Apple platforms.
I’ll be speaking @BlackHatEvents on Thursday: Can’t Touch This: Attacking Fingerprint Systems from Sensor to OS
Come hear about the current state of biometric security across Linux, Windows, and Apple platforms and my journey reverse engineering hardware, firmware, Windows drivers, protocols, Apple userland, kernel, and SEP
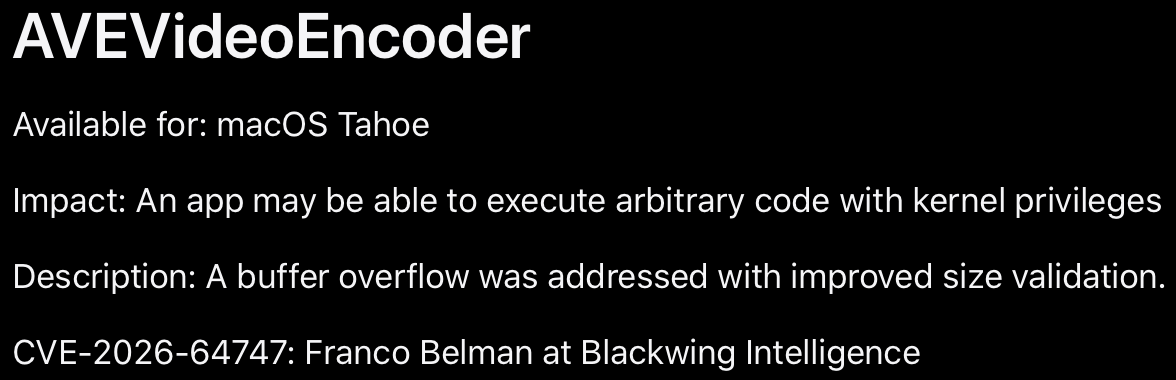
Apple credited me today for CVE-2026-64747, a vulnerability in AVEVideoEncoder affecting macOS/iOS. It earned a $60K accelerated bounty after I captured an Apple Target Flag.
Write-up coming soon.
Last year for @blackwinghq's 20th anniversary party in Vegas during Black Hat and DEF CON, the invites came with a little puzzle I put together: a floppy with a custom bootloader and a USB stick with extras.
Play along at home: https://t.co/Nxe1VQkAW3
Going to @REverseConf? Looking forward to seeing you if we know each other and meeting you if we don’t!
I’m hiring too, so hit me up if you want to chat.
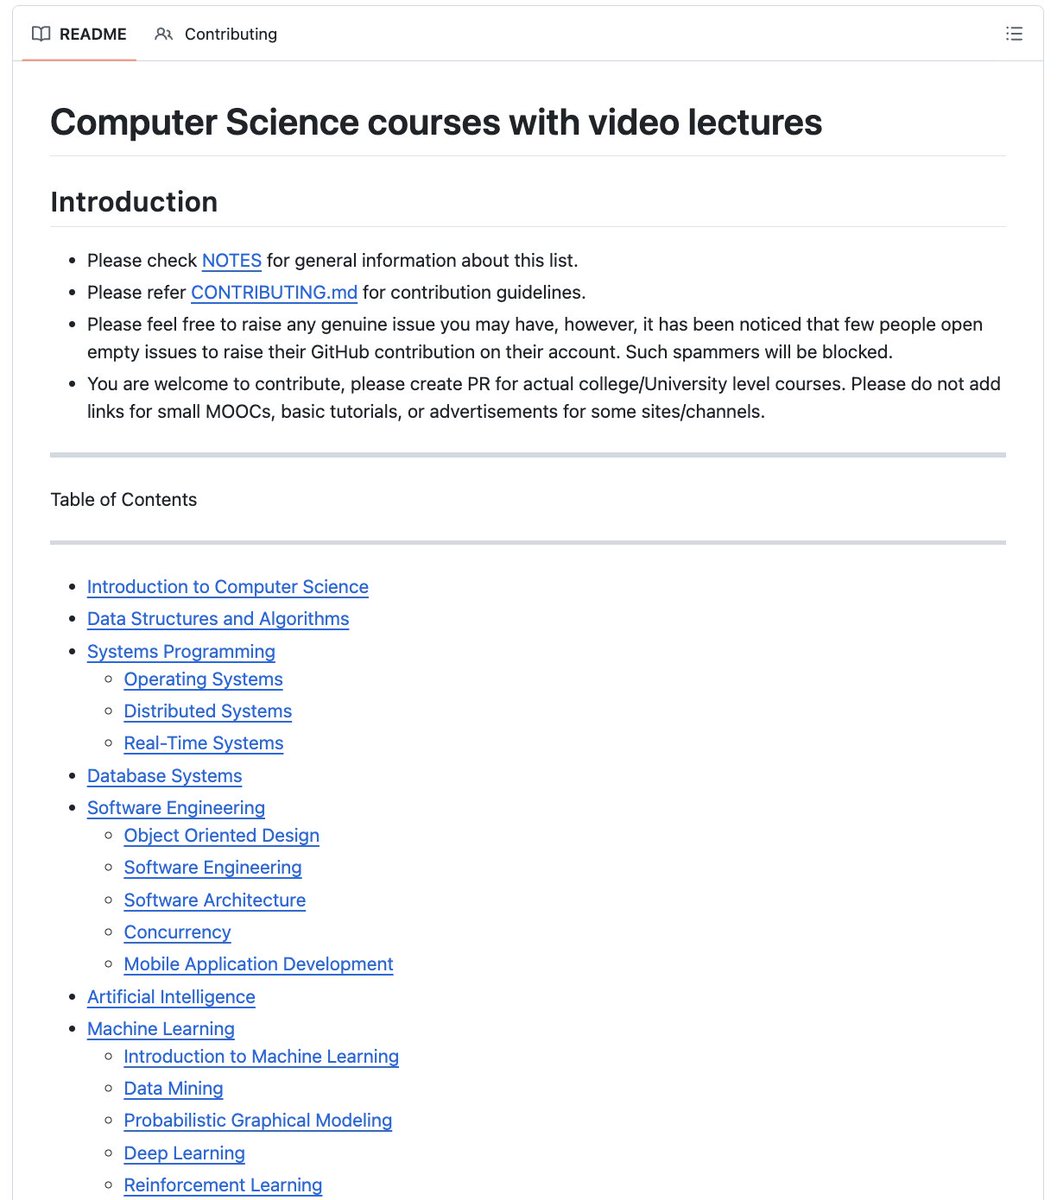
🚨BREAKING: Someone compiled every CS course from MIT, Stanford, Harvard, CMU and Berkeley in one place.
You can learn:
- Algorithms, OS, Distributed Systems, ML, AI
- Deep Learning, Computer Vision, NLP, LLMs
- Security, Databases, Quantum Computing
- 500+ courses with full video lectures
70.3K stars. 100% Opensource.
New in Wirebrowser: Breakpoint-Driven Heap Search (BDHS) — step-out debugging + temporal heap snapshots to identify the user-land function where a JavaScript value is created, even across async boundaries.
Writeup: https://t.co/1pQAUX5zlj
Everyone who attended our @blackwinghq anniversary party received a bootable 3.5” floppy 💾 with a fun little puzzle in a custom bootloader I made.
I’ll post the floppy image if anyone’s interested.
1/11: Another day, another #backdoor! Our team started digging deep into the #macOS#malware sample (yet undetected on VirusTotal) shared by @bruce_k3tta, and surprisingly found out that it has the ability to execute arbitrary commands sent from C2 and capture screenshots.
We’ve been thinking about putting on some training around Apple vuln research and exploitation (stay tuned @blackwinghq). In that spirit, @ausernamedjosh created a tool to play with libmalloc interactively to better understand its internals. Check out his new blog here: https://t.co/39iowiujKO