My latest Chrome bug just got derestricted.
Did you know that floats have a minus zero? Turns out if you forget about it, that can mean RCE :).
https://t.co/ysgtEM3Vum
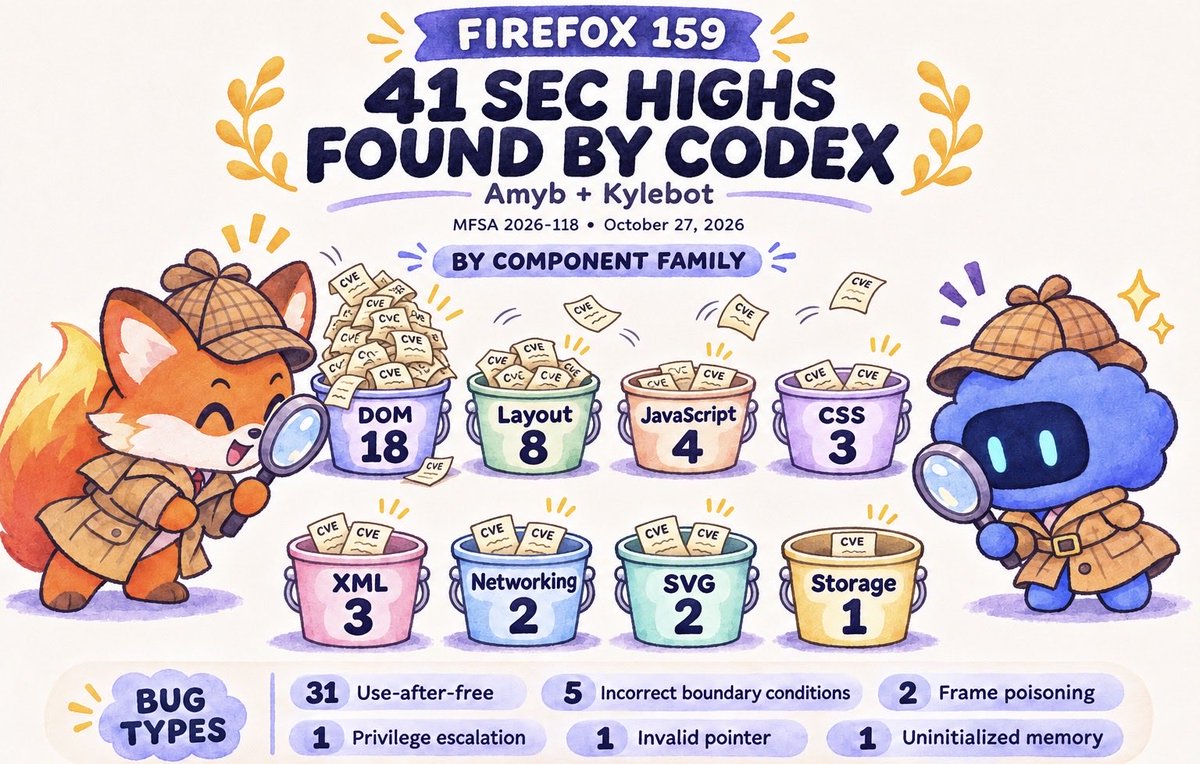
Firefox 159.0 just fixed 41 sechigh vulnerabilities found by me and @ky1ebot
Most of these leads to code exec in the renderer!
Along side a heroic effort from the Mozilla security team to secure Firefox with agents!
One of many projects we are working to harden, more to come
I was disappointed that nearly nobody at #OffensiveCon remembered Holey Beep from 8 years ago.
A bug in the setuid beep binary beep. You had to win multiple races to write 4 bytes of uninitialized memory to an arbitrary file.
And ofc, the man page boasted that it's unhackable.
After a few years in beta, the V8 Sandbox is now considered a real security boundary! (Just announced at OffensiveCon Tokyo together with @mlippautz). This is less about reaching a particular software milestone than about two things:
Glad to announce IERAE CTF is back!
AI killed CTF? We believe we're not done yet!
Bring your insight or an agent that proves us wrong 😄
IERAE CTF FINAL for Humans Round 1
- Oct 10, 00:00 UTC
- 1 chal, 8 hours
- $1,000 in prizes
Today I'm joining Anthropic to lead the cybersecurity mission of the Frontier Red Team.
In my career I've never seen a clearer opportunity to build a more secure world for everyone. For 40 years we've lived with fundamentally insecure technology. What will it take to make the past 40 years of hacking a historical oddity? That's what I'm here to find out.
Super excited to work with @logangraham and the rest of the FRT crew.
During my time at @QED_Audit I circled back and took another quick look at browser/JSE vulnerability research. AI agents flying high, seemingly finding & exploiting bugs everywhere, and there's this: a **constant integer overflow** in V8, alive for over 3.5 years. (1/5)
I found a Linux 0day vuln with @rqda_A, and $80,000+ rewarded for it by Google kernelCTF!
The vuln has been surprisingly hidden for about 19 years.
We've published an English version of the blog post!
https://t.co/Xsx1GyEtT4
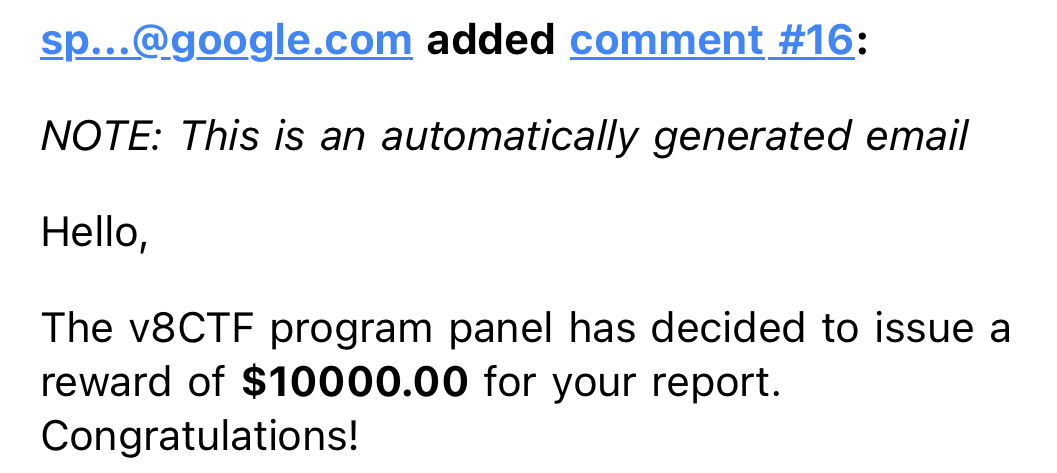
We won v8CTF, with Codex!
This is the first confirmed 0day entry in v8CTF since Oct 2025. Our entry was submitted on June 19, at the bottom:
https://t.co/Yb883U2BZK
Full technical writeup and PoCs will be released after the bugs are fixed.
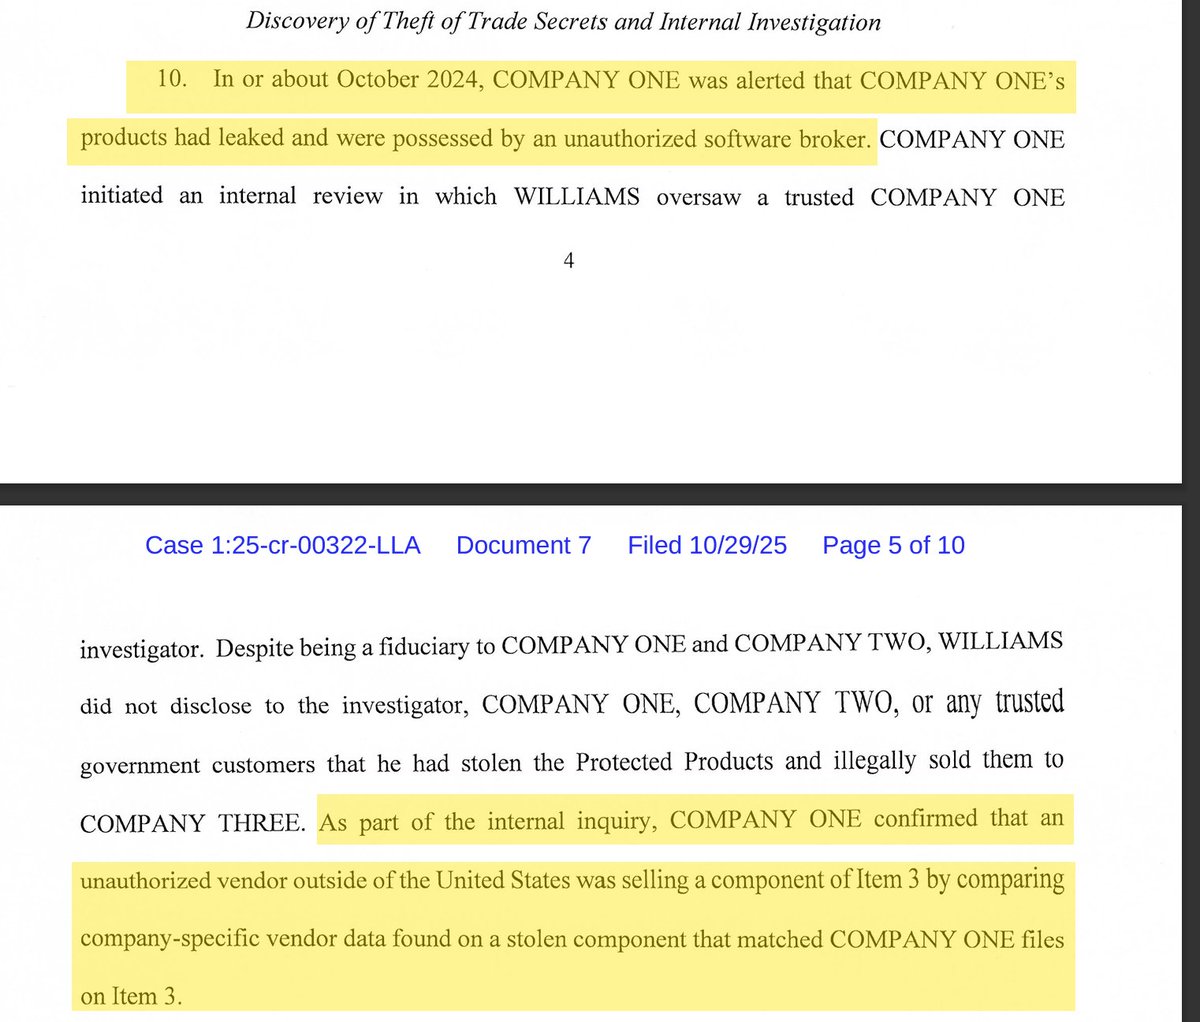
This Williams story is crazy. The documents only leave more questions. How did L3Harris (company 1) learn about the sales to Operation Zero (company 3)?
Were they able to attribute their own exploit (item 3) by looking at the rop chain or did he legit leave the headers in?
We derestricted https://t.co/DvAkrs21i4 today which might just be my favorite bug of the last few years: bad interaction between WebAudio changing the CPU's handling of floats and V8 not expecting that. See https://t.co/ovkSmnegNP for a PoC exploit. Also affected other browsers
"they did not feel their research was ready to publicly demonstrate"
And this kids is what happens when you can't come up with a catchy name for your vuln on time.
If anyone else wants to disclose whatsapp 0click, our team is always available to help: [email protected]