Thread of English language podcasts I find interesting and enjoy listening to, unordered. My links go through antennapod dot org to make it easy to view and subscribe on modern podcast apps. I'm not a premium X user, only limited chars per post. Suggestions and comments welcome.
@En0tuK_ set up dns that redirects all yandex[.]net and yandex[.]ru to ur pc (i used dnsmasq), then you use the leaked certs (mastodon link in the replies to OP) to issue certificates for these domains, then you mitm the traffic and search for /get_sync_info, intercept it and enable adbd
So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and https://t.co/QlOXb3COq3 went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
A Florida man was found dead in his home during a welfare check in July 2022. Weeks later, one of the officers who discovered his body moved into the home and spent years impersonating him, according to investigators. https://t.co/p66rB0yE7y
Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
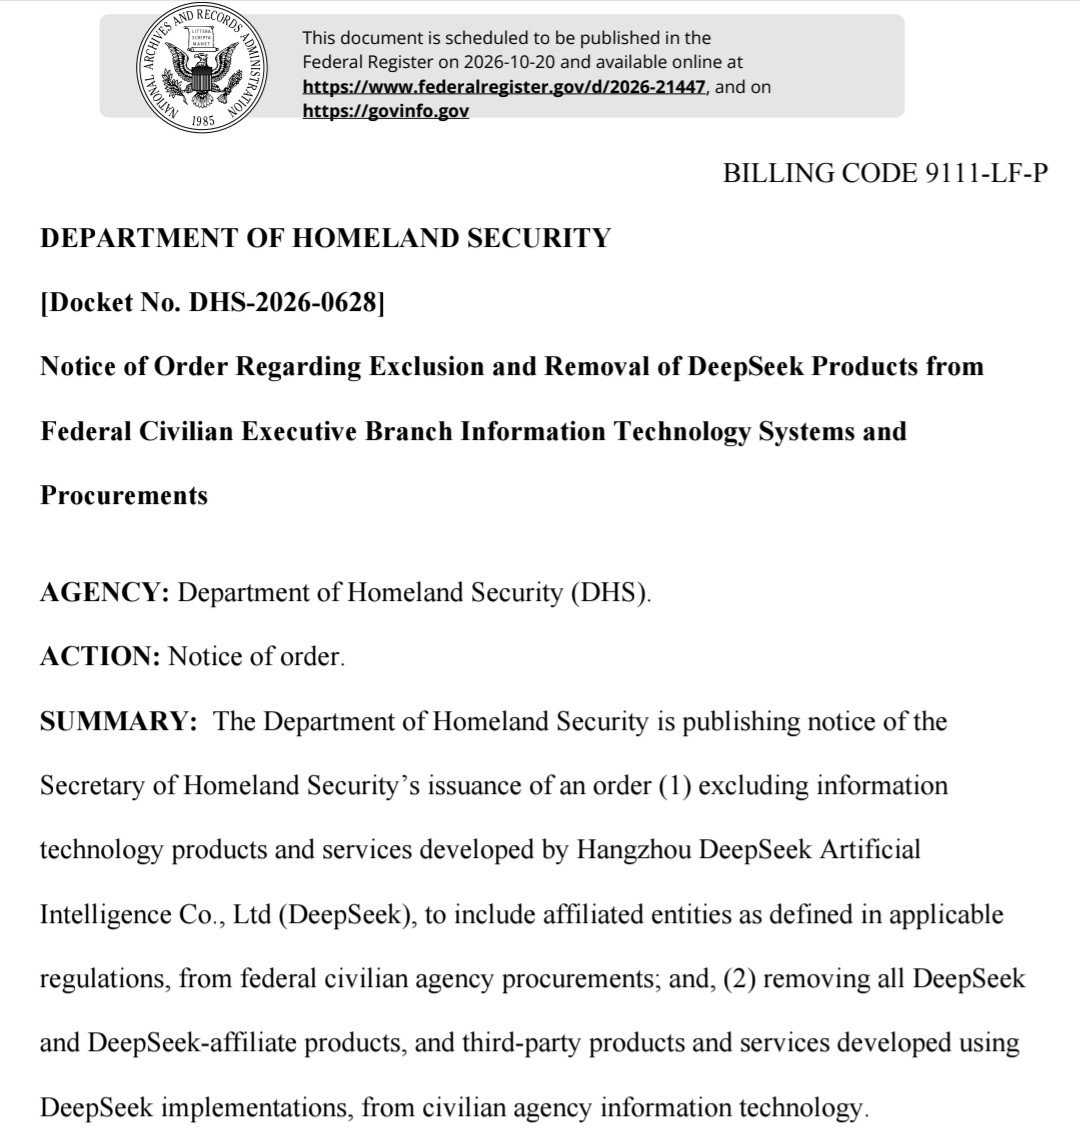
The Department of Homeland Security is requiring all civilian federal agencies to remove DeepSeek products and 'any third-party services developed using DeepSeek implementations,' and to stop buying them.
Si vous avez téléchargé aujourd'hui la dernière version de CLI d'OVHcloud, merci de la mettre à jour à nouveau très rapidement. Sinon effacer. Il s'agit de repo:
https://t.co/mSILpJyTEq
La version CLI de 14h47 a été compromise par un hacker. Nous l'avons détecté et bloqué à 16h21. Merci au client qui nous a remonté le souci. La version compromise est v0.11.0 v0.12.0 v0.13.0 v0.14.0 v0.15.0.
La version v0.10.0 et la future 0.16.0 est clean.
On vient de finit les premières vérifications et aucun autre repo n'est affecté. Nous avons aussi retracé l'incident. Le hacker a utilisé le compte github d'un des développeurs et a ajouté un binaire dont le job est récupérer les secrets sur le disque. La qualité du binaire est médiocre mais il peut aller jusqu'au bout. Si vous êtes concernés, merci de changer tous les secrets sur votre disque.
On continue les recherches sur le binaire et on va publier les détails additionnels sous peu.
🇳🇱 🚨 NETHERLANDS: PHILIPS ALLEGEDLY BREACHED, 13.5GB OF DATA LEAKED ON HACKER FORUM
A threat actor calling itself "Z-Union" has published a 13.5GB dataset it claims was taken from Koninklijke Philips N.V., the Dutch health technology giant, and is offering it for free download.
What we know so far:
* Claimed size: 13.5GB
* Shared openly as a downloadable dump, not offered for sale
* The actor has not described the contents, so it is unclear whether the files include corporate documents, customer records or product data
The claim has not been independently verified, and Philips has not publicly confirmed a breach.
⚠️ Analyst Note:
Philips makes medical devices and health systems used by hospitals worldwide, so any real exposure of internal files could matter well beyond the company, from GDPR scrutiny to product and supply-chain risk. Until the dataset is examined, treat it as an unverified claim; recycled or third-party data is often relabeled with a big brand name.
#DDW #DarkWeb #Netherlands #Philips #DataBreach #ThreatIntelligence
Even serieuzer is het toch opvallend dat ze daar onder de advertentie de .nl van @Rijkswaterstaat kunnen krijgen, die vervolgens doorverwijst naar een fake @ADNL website. Dit probleem is al weken lang aan de gang. @PolitieTHTC zit niet meer op X. Alleen hierom al onverstandig.