@P0ystick start w file-related parameters L file path download ir export then test traversal with ../../ and encoding variations this realy helps in understanding how the app handles this in
Its sometimes linked to other vuln or a linked param like a file name in a file upload for example
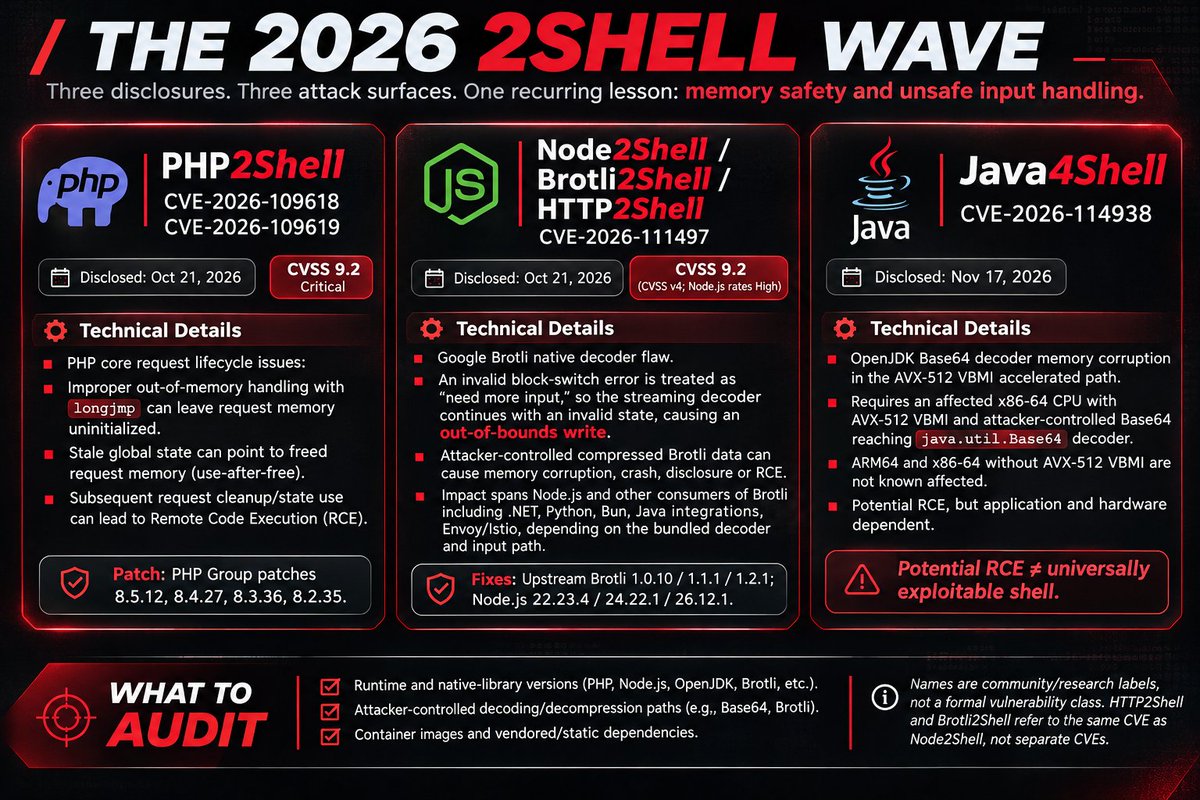
Memory corruption vulnerabilities are making headlines in 2026.
PHP2Shell, Node2Shell, Java4Shell — different runtimes, one common theme: memory safety.
More vulnerability research and technical breakdowns coming. Follow for more! 🔴
#CyberSecurity#RCE#MemoryCorruption
If you want Opus 5.5 to work with almost no safeguards, use Opus 4.6 and have it delegate tasks to Opus 5.5 through subagents. It'll get things done with almost no refusals.
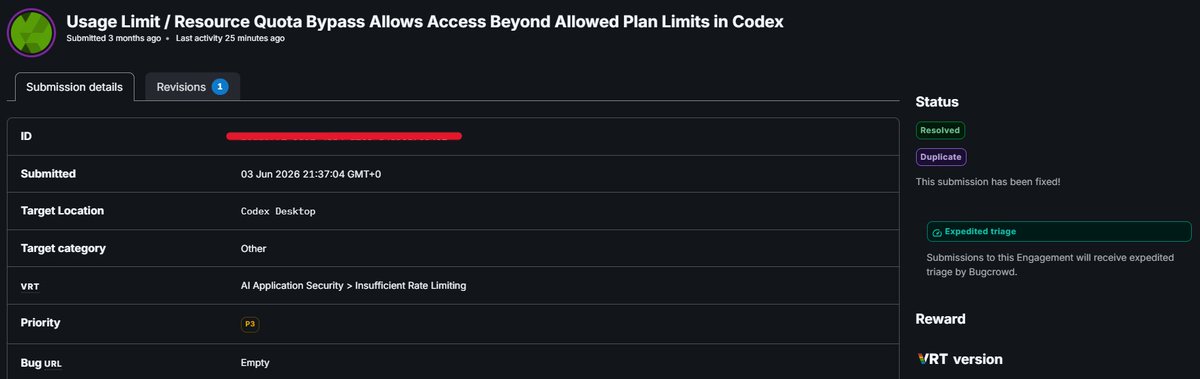
🔐 AI Security Finding — OpenAI Codex
بفضل الله وتوفيقه
I identified a usage-limit bypass in Codex involving concurrent sessions.
P3 | AI Application Security
Status: Resolved
Another step in my journey exploring AI Security & Offensive Security. 🚀
https://t.co/K97KYIJIki
By the grace of God, I completed my NTI Ethical Hacking Final Practical Exam (CEH v13). 🚀
I also shared my Pentest Report for anyone interested in the full attack chain.
👇
https://t.co/LxKksf8H4t
#CyberSecurity#EthicalHacking#Pentesting#CEH