I created a Private Second Brain 🧠 for you. It’s called Dump.
I used Slack, Twitter bookmarks, and Apple Notes to store things, but finding old info was painful. Slack’s 90-day limit made it worse. Many founders faced the same issue, so I built Dump.
Dump is your private second brain. It stores everything on your device or iCloud and helps you retrieve information with context, exactly when you need it. 100% privacy.
Would love to hear your thoughts.
🚨 CVE-2026-21636 in Node.js (@nodejs)
Node.js permission model bypass via unchecked Unix Domain Socket connections (UDS)
This vulnerability was autonomously discovered by https://t.co/Ym7gcZXFen, an AI agent that can find, exploit, and patch security vulnerabilities in codebases.
Thanks to @_rafaelgss for triaging and fixing the issue.
Introducing Chibi - Your AI User Researcher
Mixpanel tells you what happened.
Chibi tells you why.
✨ Features
- Direct insights into user pains & behavior
- No more session replay fatigue
- Clear answers to “why aren’t users converting?
- A dashboard built for PMs & founders, not analysts
Fix friction, stop churn, boost revenue.
Turn drop-offs into revenue at chibi[dot]sh
Claudia Update: First of many.
The users asked. We delivered.
✨ WHAT'S NEW IN CLAUDIA?
- You can now drag and drop images and screenshots on Claudia and preview them with a similar and familiar UX to Cursor.
- HIGHLIGHT: Interactive Web Previews, just like the ones in v0, Lovable, and Bolt. And Claude can see what you're seeing just by clicking "Send to Claude"! 🔥
🔜 WHAT'S COMING
- Shareable Agents: Create and share CC Agents. Releasing tomorrow!
- Remote Claude: Interact with your Claude Code instance from anywhere.
Reply with your feature requests and we'll ship the ones people want! Follow along! ❤️
Introducing Asterisk MCP - An MCP server that fixes security vulnerabilities while you vibe code.
Supports Cursor, Windsurf, Cline, Claude, and any IDE that supports the model context protocol.
It can perform codebase-wide scans, analyze snippets in your conversation history, and verify changes/fixes for security issues.
mcp dot asterisk dot so
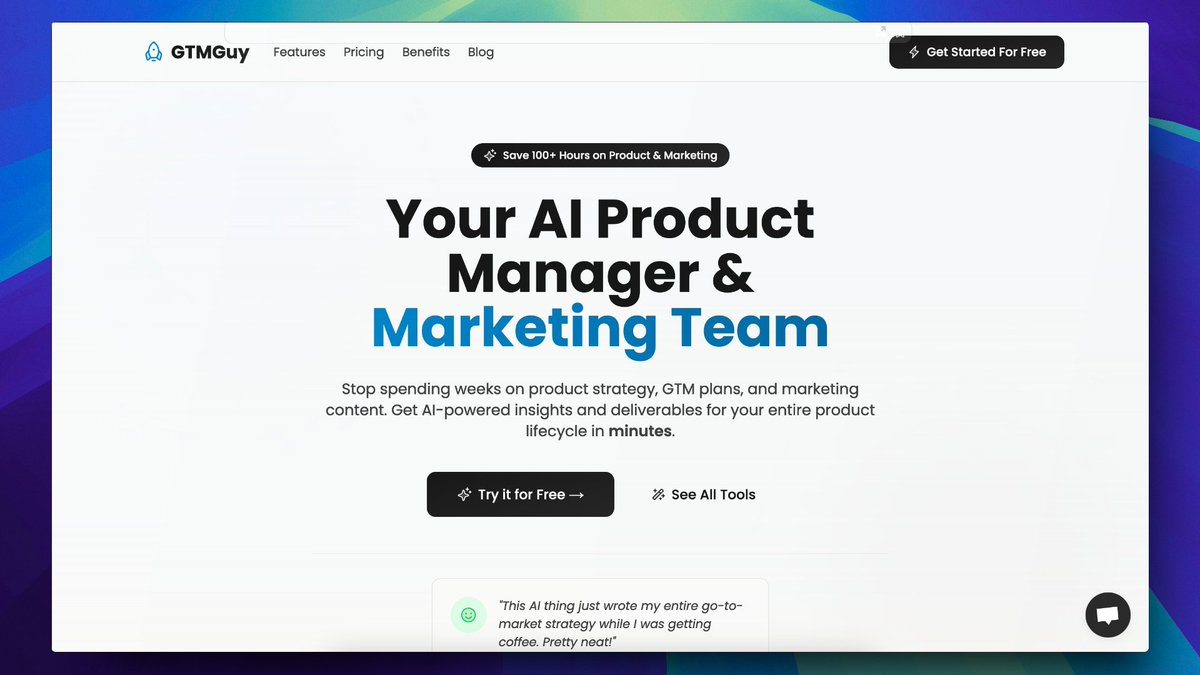
I’ve spent countless hours stuck in busywork—writing PRDs, planning MVPs, optimizing landing pages.
The more time I spend on this, the less time I have to execute.
So, I built GTMGuy, an AI tool to take care of the grind
https://t.co/pciwCiOOxL
#indiehackers#buildinpublic
Our security research team discovered a full-read SSRF vulnerability in Jamf Pro. We have published an advisory on this issue here: https://t.co/e1KEASxV3o and you can read about the discovery process here: https://t.co/rzhrqbyrv3
I'm excited to announce Tactical Adversary Podcast!
I have been procrastinating over this for some time and finally here comes the intro episode!
https://t.co/abXhP3XtQ3
Please do share your valuable feedback!
#TacticalAdversary#Podcast@TacticAdversary#CyberSecurity
Hello! I created a small repository related to Android Security. Repository contains notes, writeups, reports, good reads and lot more things. Gradually, I will update more resources and notes there. Checkout : https://t.co/fqxULjSBl9
#AndroidSecurity#BugBounty#Hacking
1/2 Who wants to learn AD hacking for free? I'll select 4 random people. How to participate:
1- You can fully commit to the schedule below
2- Like/RT then follow @0xTib3rius@theXSSrat@rana__khalil
3- Have basic pentesting skills
4- Do NOT DM me asking to be included 🙂
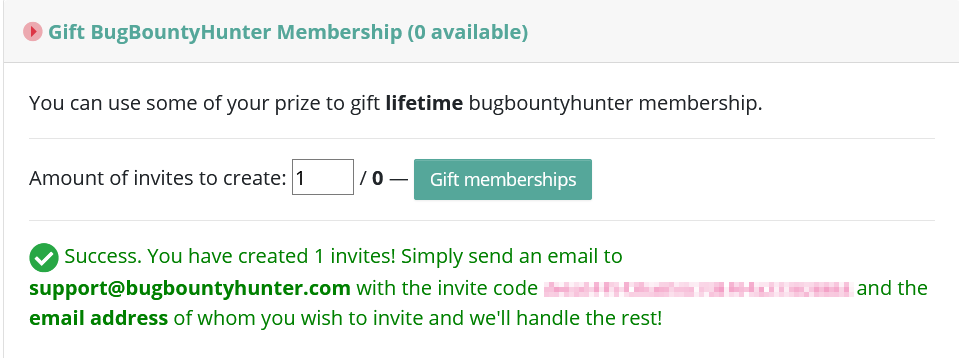
Hello hackers! After FirstBlood I'm giving away a lifetime subscription to @BugBountyHunt3r. All you have to do is retweet this and I'll be picking someone randomly on Saturday.
Happy Hacking! #bugbounty
While moving to Signal, I found that the amount of mallu stickers were quite low and I couldn't find any.
So made 2 sticker packs for my fellow mallus.
https://t.co/p5ajHsZ76J
https://t.co/wqKdJSUd5z
Enjoy my friends🥳