📢 To our incredible community of contributors: thank you for everything you do to keep the internet safe! 🛡️
To help protect our platforms and maintain the high-quality data you rely on, here is a quick refresher on our submission guidelines across MalwareBazaar, URLhaus, and ThreatFox: 👇
❓ Why do these guidelines matter so much? ❓
1️⃣ Impact at scale: Our datasets power security tools worldwide 🌍. Inaccurate submissions cause false positives on a massive scale - with great power comes great responsibility! 🕸️💪
2️⃣ Actionable intelligence: We want the data to stay razor-sharp and immediately useful, not a graveyard of noise 🪦
If an contributor's account is ever restricted, our goal is always to send an explanation right away ✉️.
On rare occasions, immediate action is required to prevent harm before we can send a heads-up. If this happens, please reach out to us so we can review it together: 🔗 https://t.co/5nTMc6j16n
Since 2009, https://t.co/x0TWKNn9PP has been built by the community, for the community. None of this works without you. 🙌
If a policy ever feels unclear or counterproductive, talk to us! We would much rather refine our wording (or the policy itself) than lose good data or a great contributor. 💛
Quick links to the submission policies for each platform:
🦠 MalwareBazaar: https://t.co/4ySdaW3IPX
🌐 URLhaus:
https://t.co/ZJ67EcyE4o
🦊 ThreatFox:
https://t.co/0sSgQTFrOQ
Thank you for standing with us to make the web safer for everyone! 🚀👏
🏆 Community spotlight: meet 'wristhulk'! 🏆
They joined the community in September and have already made a big impact. 👊
In the last 30 days:
🔗 96K+ malicious URLs submitted to URLhaus, with a 100% abuse report rate 🎯
🦠 5th on the MalwareBazaar leaderboard
🦊 14th on ThreatFox
🛡️ Earned the 50K+ Takedown badge on 1 November
A lot of their hunting goes after malware hiding in plain sight on GitHub, often disguised as fake versions of “zapret”, a popular tool people use to get around internet censorship.🕵️
And they are part of something even bigger: Over the last 30 days the community together has shared 170,942 contributions, up 117%. That’s a record month! 🚀🎉
Thank you, wristhulk, and thank you to everyone who contributes. Every submission makes the internet a little safer. 💙
#SharingIsCaring #ThreatIntel #URLhaus
Have you ever heard about São Tomé and Príncipe 🇸🇹? If not and if you care about cyber security, you should read on ⤵️
🔎 What is São Tomé and Príncipe?
São Tomé and Príncipe 🇸🇹 is an island nation located in the Gulf of Guinea off the western coast of Africa 🌍. Its country-code Top-Level Domain (ccTLD) is .st, which has recently attracted a surge of threat actors registering malicious domains to conduct cybercrime 🕵️.
📏 How big is the threat posed by ccTLD .st?
Public statistics from @spamhaus show roughly 11,600 active .st domains. Nearly 5,000 of them are flagged for malicious activities 🛑. That’s an astonishing abuse rate of over 40% of all active domain names within this ccTLD! 📈
➡️ https://t.co/0lKGJcZey5
While threat actors often register domains across various ccTLDs, the big issue with .st is how its registry is dealing with, or better said, not dealing with, abuse reports 📩.
Over the past few months we’ve sent nic .st several abuse reports about domains registered purely to run botnet command-and-control (C2) infrastructure.
Here's two recent examples of malicious domains within ccTLD .st:
1️⃣ thisisafalsepositive .st - An active botnet C2 domain for SilentNet, a Java-based Remote Access Trojan (RAT) and infostealer sold under a Malware-as-a-Service model. Over the past two months, more than 400 malicious GitHub repositories spreading SilentNet have been reported to URLhaus 🏠🔥.
2️⃣ imarapi .st - An active botnet C2 server for the infamous JackSkid DDoS botnet that was disrupted earlier this year by the US DOJ 🇺🇸. It infects IoT devices and Android TV 📺 boxes worldwide 🌍.
🗣️ How did nic .st respond?
The registry routinely pushes back, stating that:
"To be able to investigate we need official document that confirm illegal activity hosted under mentioned domain, this can be decision of courtroom or any other official authorities which will be authorization for us to perform investigation."
🛡️ What should you do?
If you don't do businesses in São Tomé and Príncipe, we strongly recommend you to entirely block .st at your network security perimeter 🛑
In an international law enforcement operation 👮, the US Department of Justice 🇺🇸, in cooperation with private sector partners, have taken down notorious bulletproof hosting provider Virtualine 💥
➡️ https://t.co/ls6AxDHv3H
Operating as AS202412 (Omegatech LTD), Virtualine received upstream connectivity from German 🇩🇪 providers aurologic GmbH (AS30823) and Pfcloud UG (AS51396), as well as French 🇫🇷 PEERXY NETWORKS SAS (AS213382), as bgp .tools shows. This network connectivity is now gone, currently making it impossible for Omegatech to operate 🛑
Omegatech announced 24x /24 IPv4 CIDRs, totaling 6,144 IPs. Out of these, hundreds were seen daily participating in spamming, internet-wide scanning, and botnet C2 hosting ⤵️
🌐 URLhaus tracked over 10,000 malware distribution sites at Omegatech: https://t.co/TuHmy8rx1K
📡 ThreatFox logged 2,000+ community-shared IOCs tied directly to Omegatech: https://t.co/rcQvqOziQQ
The hoster primarily served malicious infrastructure associated with RATs 🖥️ (e.g., PureRAT and OverlordRAT), rogue ScreenConnect servers 🔌, and social engineering malware campaigns like ClickFix and ErrTraffic 🖱️. While internet abuse for sure can happen, Virtualine was not reacting on abuse reports at all and advertised their "bulletproof hosting services" on the darkweb, as investigation shows 🕵️♀️
The takedown of Omegatech is welcome news. However, its long-term impact remains uncertain. Bulletproof hosters commonly re-brand and resume operations under new ASNs quickly 🔃
Furthermore, Omegatech is just the tip of the iceberg. Other active bulletproof hosters include:
➡️ AS219502 (STORMCLOUD)
➡️ AS207043 (DEDIK-IO)
➡️ AS214351 (FEMOIT)
What do they all have in common? According to bgp .tools, they all receive upstream connectivity from German provider aurologic GmbH (AS30823) as well 🔍👀
If you don't want to worry about the threats posed by bulletproof hosters, just block any CIDRs and ASNs listed on @spamhaus 's Don't Router Or Peer List (DROP):
🛑 https://t.co/7mNWn3R85C
From TODAY, non-authenticated users can no longer export files from our platforms. If you haven’t already #Authenticate 👉 https://t.co/eazWk4bYUP
Once authenticated, you will need to:
➡️ Use the new domain: {{platform}}-api.abuse.ch (where the platform can be urlhaus, threatfox or mb for MalwareBazaar)
➡️ Insert your unique Auth Key before the file name (obtained via https://t.co/bKBle6tNU5)
#SteadyPlatform #SteadySignal #SharingIsCaring
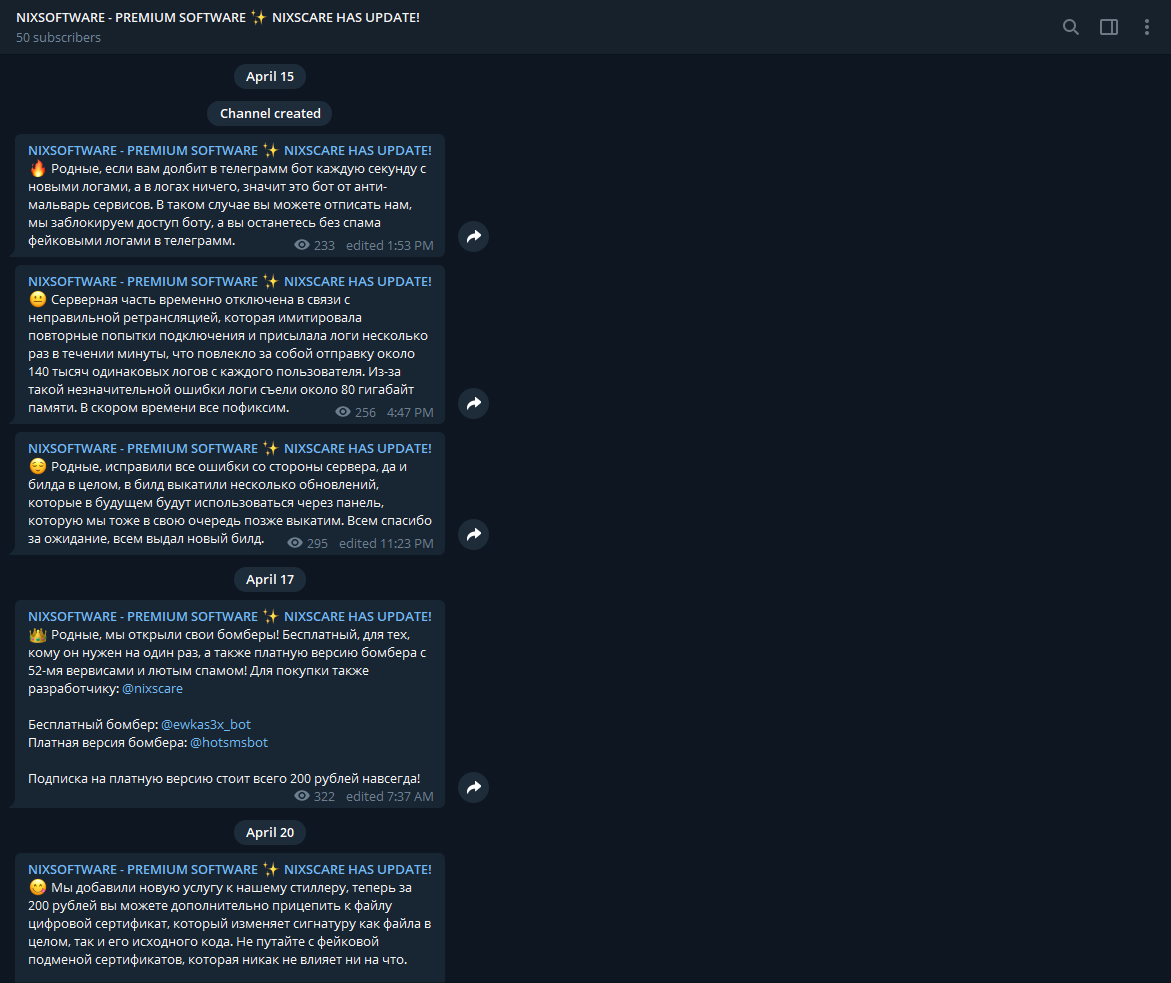
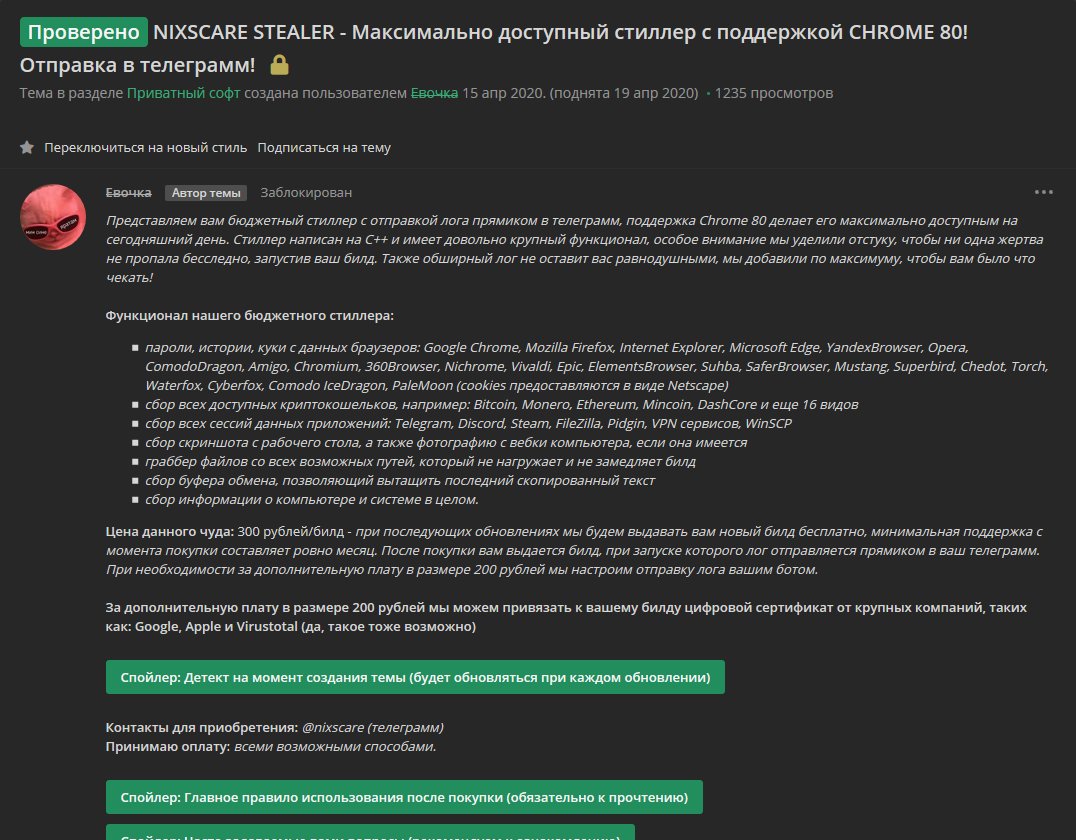
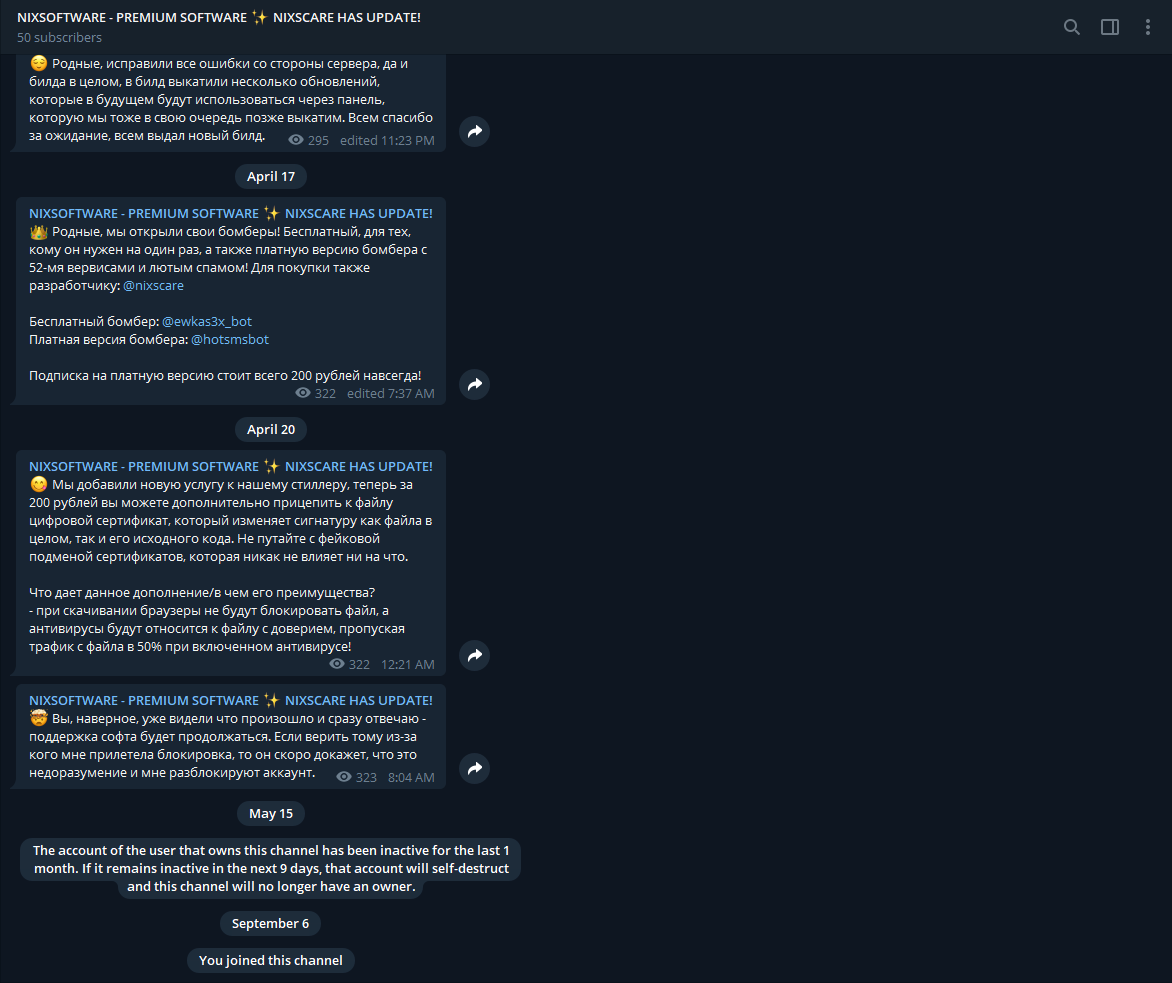
#Malware#Stealer#Teelegram#NixScareStealer
StalkCraft.exe:
https://t.co/4eKbZkYNUH
https://t.co/5CIqc4ekKm
GitHub: https://t.co/NOt5JjeC41
Special thanks to @ViriBack.
https://t.co/85tSxLFgQ0
Still information in the comments 👇
Why are we making this change? 🤔
Some users have been pulling down file exports too often, which puts extra pressure on the platforms. We know this feature is important to the community. That’s exactly why we’re making this change, to keep things running smoothly for everyone.
👉 Authenticate now so you’re ready: https://t.co/eazWk4bYUP
#SteadyPlatform #SteadySignal #SharingIsCaring
📢 Important update | Changes to file exports
From October 21st, file exports will require authentication. Non-authenticated users will no longer be able to export files. Authenticated users can continue exporting, with a small update to how export URLs are accessed.
If you’re an authenticated user, you’ll now need to:
➡️ Use the new domain: {{platform}}-api.abuse.ch (where the platform can be urlhaus, threatfox or mb for MalwareBazaar)
➡️ Insert your unique Auth Key before the file name (obtained via https://t.co/bKBle6tNU5)
📄 Example URL:
https://mb-api[.]abuse[.]ch/v2/files/exports/{YOUR_AUTH_KEY_HERE}/filename.ext
@devmihaylov@SquiblydooBlog@malwrhunterteam We ran a dist-upgrade on the MalwareBazaar backend yesterday, causing that some uploads did not went through. We have fixed that issue about an hour ago. Sorry for any inconvenience caused 🙏
Did you know that if you run Cowrie high interaction SSH and Telnet honeypot 🍯🐝, you can automatically submit malicious URLs caught by it to URLhaus 💡? If you aren't running a Cowrie honeypot yet, you may want to check it out:
Project website:
🖥️ https://t.co/EMAaT4mUt9
GitHub repository:
🖱️ https://t.co/ad5epUMtXW
Malicious URLs caught by Cowrie honeypots:
🌐 https://t.co/GQxQuduK9V
A couple of months in and the Community Hub is thriving 🤩 ... 36,441 contributions across all https://t.co/x0TWKNn9PP platforms in the last 30 days (up +30.8%) 🔥🔥🔥
@geenensp 🥇 on URLhaus (78-month streak!!)
TheRavenFile 🥇 on ThreatFox
whack_sh 🥇 on MalwareBazaar
Go see the full Top10 leaderboards
👉 https://t.co/klxLeWz8jY
#SharingisCaring #Leaderboards #Community 💛
We recently sinkholed a DDoS #botnet of 200,000 compromised Android TV boxes infected with #CECbot malware 🕵️♀️. Shortly after, the threat actor responded by registering a rather specific botnet C2 domain 👇
📡 spamhaushackers .at
Nice try, but their new C2 domain is already flagged🛑. Its authoritative DNS runs on DNSPod (*.dnspod.com), which has carried a poor reputation for years! 💡
⤵️⤵️⤵️⤵️
https://t.co/rQHYkDSUsJ
🚨 ANNOUNCEMENT FOR TOP CONTRIBUTORS! 🚨
We’ve been working on something huge and the cat 🐈 is finally out of the bag 👀 ... https://t.co/x0TWKNn9PP and Spamhaus have officially partnered with Modat (@modat_magnify) to give FREE Magnify licenses to our top contributors! 🎉🔥
You give your time, brainpower, and expertise to this community 👏. You hunt down the bad guys every single day - we want to make sure you have the best tools 🛠️ to do what you do for the good of the internet every single day!
Consider this our way of saying THANK YOU 🙏 🙏
Top contributors - keep an eye out, we'll be reaching out in the coming weeks to get your access sorted.
More details in comments 👇