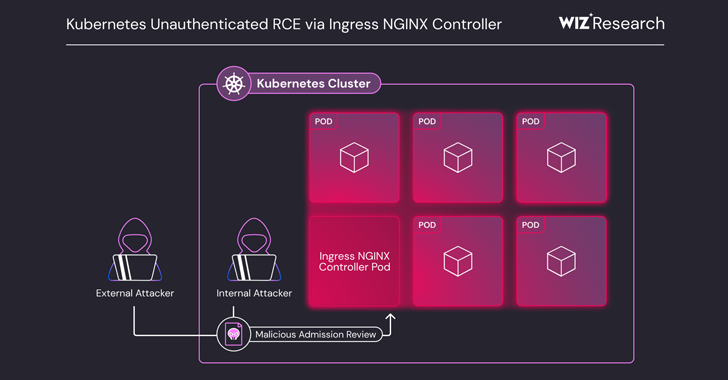
🚨 WARNING: 43% of cloud setups at risk from new "IngressNightmare" flaws.
Unauth RCE in Ingress NGINX Controller for Kubernetes could let attackers take over entire clusters—no creds needed. Over 6,500 exposed.
🔥 CVSS 9.8 | 5 CVEs | 1 attack chain | Total cluster compromise.
Patch now → Versions 1.12.1, 1.11.5, 1.10.7 Disable admission controller if not needed Lock down external access to webhooks
This isn’t the NGINX Ingress Controller you think it is.
👉 Full details + fixes → https://t.co/fxMzmvsi5R