We gave an autonomous pentest AI one target. Then we watched its entire attack — live, from the kernel.
It logged 46 commands. The kernel saw 141 processes and 141 packets.
60 seconds below. Zero code inside the agent.
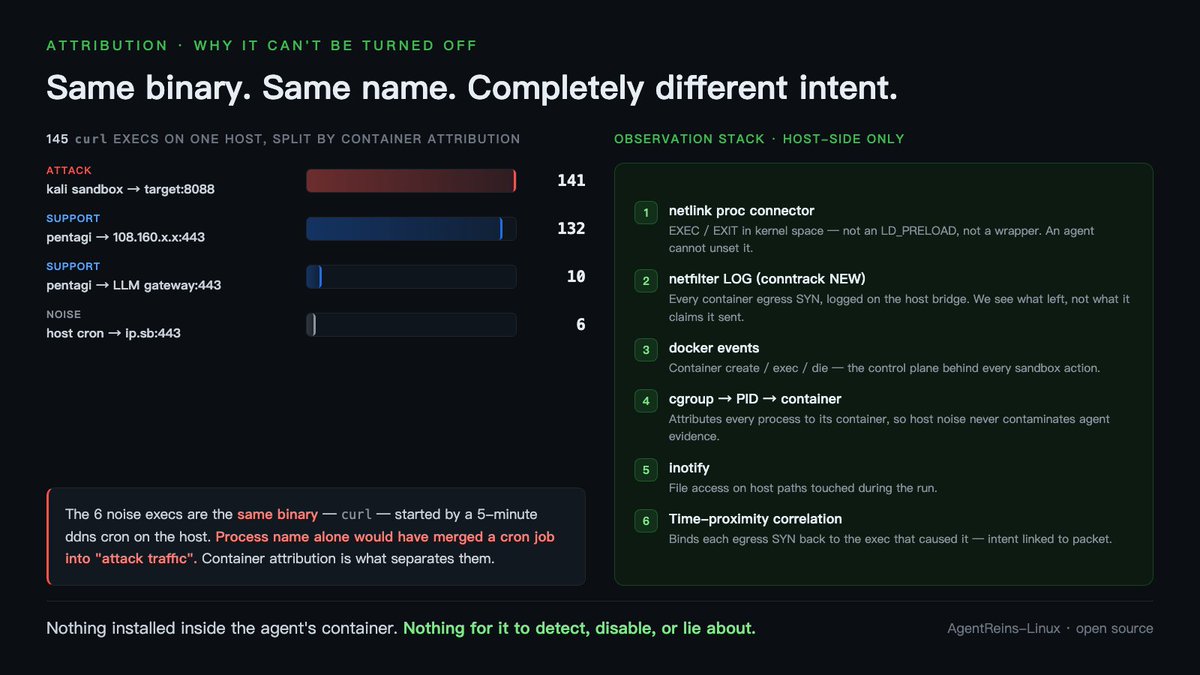
145 curl executions on one host.
141 were the attack. 6 were a cron job.
Same binary name. Same process name. Different cgroup.
Process names lie. Cgroups don't.
46 commands the agent said it ran.
141 processes the kernel saw it start.
141 packets that actually left the host.
Same attack. Three resolutions.
We watched an autonomous pentest AI from the kernel — zero code inside its container.
At this moment, I am considering how to deliver agent security products. I am currently writing the Linux version of agentreins for monitoring PentAGI.
网络死循环与重试风暴(Loop Detection):Agent 在调用某个第三方 API 失败后(例如遇到了 429 Too Many Requests),由于大模型在非确定性环境下的逻辑缺陷,可能会在 1 秒内疯狂重试上千次,直接造成“网络账单刺客”。你的产品如果在网络层第一秒发现这种异常的高频重复网络模式,直接发出断路器(Circuit Breaker)拦截,这就是核心价值。
I'm a solo developer, and I know my strengths. But to build a truly exceptional product alone, ruthless prioritization is non-negotiable.
I used to think Agent Observability was niche enough. But to achieve a true single-point breakthrough, I need to go even deeper.
My laser focus now: Agent Network Observability. I am narrowing down exclusively to the network communication layer of AI Agents. Time to master this single domain. 🎯