CVE-2023-43326 mooSocial v3.1.8 was discovered to contain a cross-site scripting (XSS) vulnerability via the change email function. https://t.co/Yw7AAonUKw
CVE-2023-43325
A reflected cross-site scripting (XSS) vulnerability in the data[...
https://t.co/y5Q1JhQRaH
Vulnerability Alert Subscriptions: https://t.co/hrQhy5uz4x
#Datasecurity concerns of Tesla's Sentry Mode have manifested in sporadic bans from various areas, mostly those associated with the military or government offices. But this has recently expanded to certain sporting events and airport parking. https://t.co/VrYFFzs5To
Hi, @openbugbounty
I have created an account using the username “ahrixia” and outlook email. But every time I try to login I don’t get any OTP on my email. Could you please suggest?
My advice: Please don’t listen to every Cybersecurity Professional on LinkedIn. Half of the things they talk are not even backed up with any experience. I see people with 5-50K “LinkedIn family” sharing their blogs/knowledge on things which they haven’t even done yet!
@airvistara 3: compensation on hotel took 3hr+ in total and that too was away from airport. When asked if you can checkin the luggage for us as we don’t wanna get back early again. You denied. I really am disappointed from you @airvistara. Shame on you to make my family suffer like this.
@airvistara 2: you said we can and also told us you contacted the team in Delhi. But seems like it was a lie. Once we reached there, you said we missed our flight. You said it will wait for us for few minutes as it was all on you. But you took it for granted and left us like it. Even…
@airvistara 1: @airvistara I swear to god I am very disappointed. After such a long time I tried to bring my family to Singapore:. But because the flight got moved to Jaipur. It’s fine I do understand the weather. It’s just when my family and I asked if we can still catch our flight…
@ECCOUNCIL please recheck my CPENT exam as I’m sure I’ve score more than 86%. Also few questions in exams had all wrong answers! Tell me what am I supposed to do.
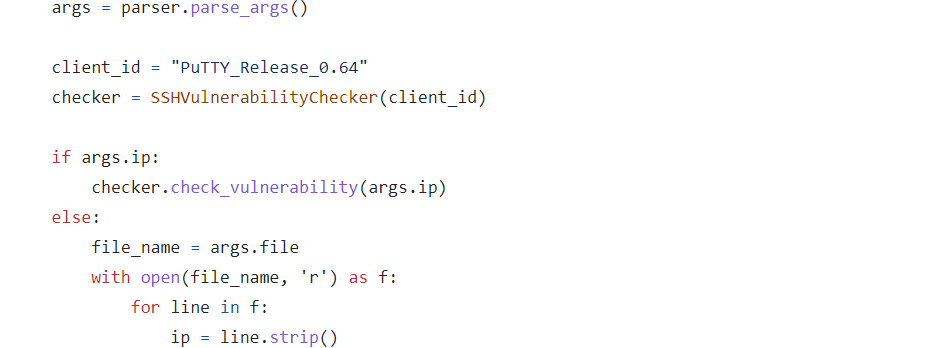
CVE-2023-25136: OpenSSH server (sshd) 9.1 introduced a double-free vulnerability during options.kex_algorithms handling. This is fixed in OpenSSH 9.2
PoC
https://t.co/DHxVaTJXh2
My tool for exploiting race conditions vulnerabilities is available here: https://t.co/J8tXVWeYyy It includes a distributed architecture for improved exploitation, a vulnerable web application for testing, a browser add-on, and an OWASP ZAP extension to simplify exploitation.
I am inspired by curiosity.
That is what drives me.
So let us expand the scope & scale of consciousness so that we may aspire to understand the Universe.