يالربع مس��كم الله بالخير اليوم جايب لكم موقع يقدم محتوى مسار الشهادة الاحترافية cwes من htb بشكل مجانى كل المديولات الموجودة في مسار cwes تحصلها فيه بشكل مجانى عكس htb بفلوس الموقع: https://t.co/WfFpj95i4S
نفس المحتوى انت اللي عليك تنسخ الكلام وترسله ل gpt يترجم ويشرح وبالتوفيق
irraz/vulnerator-ai: Autonomous OODA-loop pentesting agent. Hermes brain, Kali + Playwright tools over MCP, ATT&CK as the Orient language. https://t.co/D0MeZTz9eb
Ola Bug bounty hunters 😀
DarkEntry’s free Associated Domains feature maps every domain tied to a target — including exposed admin panels.
Type in your in-scope domain, one click, Export All its associated domains as .txt!
https://t.co/ADJNvpSCj6
Happy hunting 🙏
The Ultimate SSRF Guide is here!
From discovery to Exploitation and filter Bypasses, everything you need to hunt SSRF vulnerabilities, from zero to hero.
https://t.co/6wcC7oBfZa
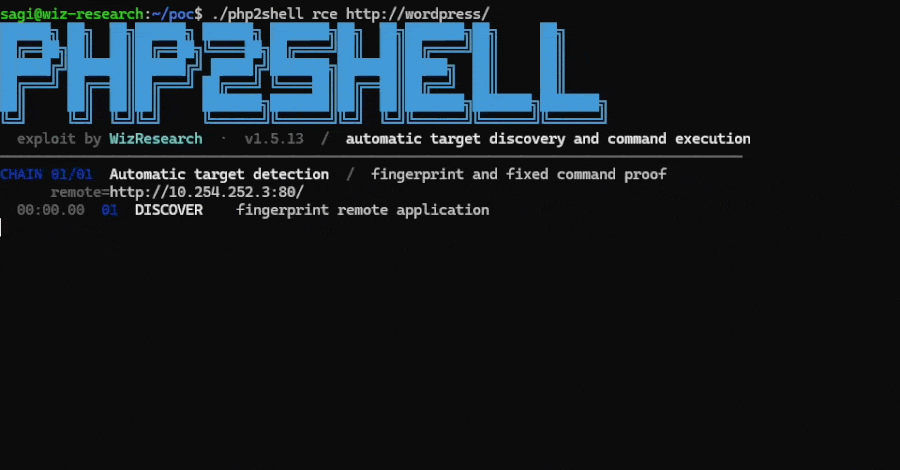
Public PoC claims ASLR-bypass RCE on unpatched PHP
A public proof-of-concept exploit has been released on GitHub targeting the PHP session flaws behind "PHP2Shell". The author says it achieves one-shot, fully remote code execution on an unpatched PHP 8.4.26 + Apache stack (mod_php, prefork), bypassing ASLR over plain HTTP with no code added to the target page.
* The PoC runs against the official php:8.4.26-apache image; the author reports a 3/3 success rate yielding www-data command execution.
* It leaks heap and PHP library addresses to defeat ASLR; the current version needs display_errors=on.
* This targets unpatched 8.4.26 - fixed builds already exist.
Patch now: update to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35, or your vendor's fixed package.
https://t.co/bQ4DYTbi5N
#PHP #CyberSecurity
🚨 Critical pre-authentication RCE research published for two PHP core vulnerabilities; CVE-2026-109618 + CVE-2026-109619
PoC: https://t.co/UMqqumv8e1
The flaws affect PHP's session.upload_progress handling and can be chained through session-file injection, memory corruption, or deserialization behavior to achieve remote code execution under specific application conditions.
CVSS: 9.2 Critical
Affected: PHP 5.4.0 through 8.5.11
Fixed: PHP 8.2.35, 8.3.36, 8.4.27, and 8.5.12
The repository includes verification PoCs for session injection, a heap use-after-free, and handler-mismatch deserialization, along with a vulnerable Docker lab and detailed technical analysis.
مشروع Reverse Engineer Anything
وصل ل300 ألف نجمة في قيتهب ورقم 1 حالياً في المنصة 💀
وغالباً المشروع هذا من جد بيخلي أشياء كثيرة مفتوحة المصدر , مثل ماشفنا مع آرت كرافت اللي نافست برامج أدوبي
وممكن نشوف منافسين لمايكروسوفت أوفيس وأكثر من سلسلة برمجيات مدفوعة
@badr_halabi قبل طلب الحماية، لازم حضرموت ترتب بيتها من الداخل: إبعاد كل من ارتبط بالأحزاب والمشاريع الخارجية عن المناصب وفتح المجال للكفاءات والشباب الحضارم المستقلين وتعزيز الهوية الحضرمية والاعتزاز بتاريخها العريق بعيدًا عن صراعات الشمال والجنوب
حضرموت أولًا، وقرارها لأهلها
@hadhramot1967 بس اللي أعرفه إن القوات الموجودة على حدود حضرموت هي الفرقتين الأولى والثالثة وعددها اكثر من 20 الف والمفروض هي اللي تساند في الجوف ومأرب ، مش اللواء السادس من درع الوطن